# Getting Started

Get started with We360.ai — quick onboarding guide for employee monitoring, productivity tracking, and workforce analytics setup.

Welcome to <code class="expression">space.vars.company\_name</code>! This quick-start guide will help you set up your account and get your team up and running in minutes.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-bolt">:bolt:</i></td><td><strong>The 5-Minute Launch Guide</strong></td><td>High-level checklist for account setup, creating your first department, and agent download.</td><td><a href="/quick-start/5-minute-launch-guide">The 5-Minute Launch Guide</a></td></tr><tr><td><i class="fa-compass">:compass:</i></td><td><strong>Navigating the Dashboard</strong></td><td>A guided tour of the Admin Portal, Manager View, and Employee Self-Service screens.</td><td><a href="/quick-start/navigating-the-dashboard">Navigating the Dashboard</a></td></tr><tr><td><i class="fa-sitemap">:sitemap:</i></td><td><strong>Setting Up Your Hierarchy</strong></td><td>Mapping your company: Defining Departments, Teams, and Designations.</td><td><a href="/quick-start/setting-up-your-hierarchy">Setting Up Your Hierarchy</a></td></tr><tr><td><i class="fa-check-circle">:check-circle:</i></td><td><strong>Essential Pre-Flight Check</strong></td><td>Verifying hardware requirements and testing agent-to-server connectivity.</td><td><a href="/quick-start/essential-pre-flight-check">Essential Pre-Flight Check</a></td></tr></tbody></table>


# The 5-Minute Launch Guide

5-minute setup guide for We360.ai — account creation, team onboarding, and agent deployment for employee monitoring.

Get your entire team tracked and monitored in under five minutes. This checklist covers the essential actions for a new account administrator.

{% stepper %}
{% step %}

#### Create Your Account

Register on [portal.we360.ai](https://portal.we360.ai) and verify your email address. Log in as the **Super Admin** -- the account owner who has access to billing and all platform settings.
{% endstep %}

{% step %}

#### Set Up Your Organization

Navigate to **Settings > Organization & Billing** and configure:

* Your company name, logo, and timezone.
* Your subscription plan and seat count.
  {% endstep %}

{% step %}

#### Create Your Hierarchy

Go to **Settings > User Management** and build your org structure:

* **Departments / Teams** -- Group employees (e.g., "Engineering", "Sales").
* **Designations** -- Define job roles (e.g., "Senior Developer", "Account Manager").
  {% endstep %}

{% step %}

#### Invite Your Employees

From **Settings > User Management > User Directory**, invite employees by email or upload a bulk CSV. Assign each user a team, designation, and role.
{% endstep %}

{% step %}

#### Deploy the Agent

Navigate to the **Agent Deployment Hub** and download the installer for your platform. Share the installer link with your employees, or follow the [Mass Deployment](https://docs.we360.ai/deployment-and-it-ops/agent-deployment-hub/mass-deployment) guide for IT-managed rollouts.

{% hint style="success" %}
Once the agent is installed and the user logs in, data will automatically begin flowing into your dashboard.
{% endhint %}
{% endstep %}
{% endstepper %}

## Post-Launch Configuration

After the initial setup, configure these areas to get the most out of We360.ai:

<details>

<summary>Customize Workplace Settings</summary>

Define your standard working hours, set parameters for half-day/full-day recognition, and adjust the wellness scale to reflect your company's work-life balance targets. See [Workplace Settings](https://docs.we360.ai/reference/work-and-time-management/user-interfaces/portal/settings-center/workplace) for details.

</details>

<details>

<summary>Set Up Productivity Mapping</summary>

Categorize applications and URLs as productive, unproductive, or neutral. Create application policies tailored to each team's responsibilities. See [Productivity Settings](https://docs.we360.ai/reference/work-and-time-management/user-interfaces/portal/settings-center/productivity) for details.

</details>

<details>

<summary>Configure Alerts and Notifications</summary>

Set up alert rules to receive email notifications when specific conditions are met (e.g., excessive break time, use of a flagged application). See [Emails & Alerts](https://docs.we360.ai/reference/work-and-time-management/user-interfaces/portal/settings-center/emails-alerts) for details.

</details>

<details>

<summary>Explore Modules and Reports</summary>

We360.ai provides modules for productivity tracking, attendance, wellness, project management, and field operations. Explore the sidebar modules to familiarize yourself with the analytics available, and schedule automated email reports for recurring insights.

</details>

<details>

<summary>Introducing We360.ai to Your Team</summary>

A transparent rollout builds trust. Consider these strategies:

* **Brief management first** -- Managers will be integral in utilizing analytics and addressing team questions.
* **Hold a company-wide meeting** -- Explain what data is collected, how it is used, and the goals of the deployment.
* **Share employee dashboards** -- Encourage employees to review their personal analytics to foster ownership and self-improvement.
* **Establish feedback channels** -- Create open channels for employees to share input on the analytics and tools being used.

</details>


# Navigating the Dashboard

Navigate the We360.ai dashboard — admin portal, manager view, and employee self-service for productivity tracking and analytics.

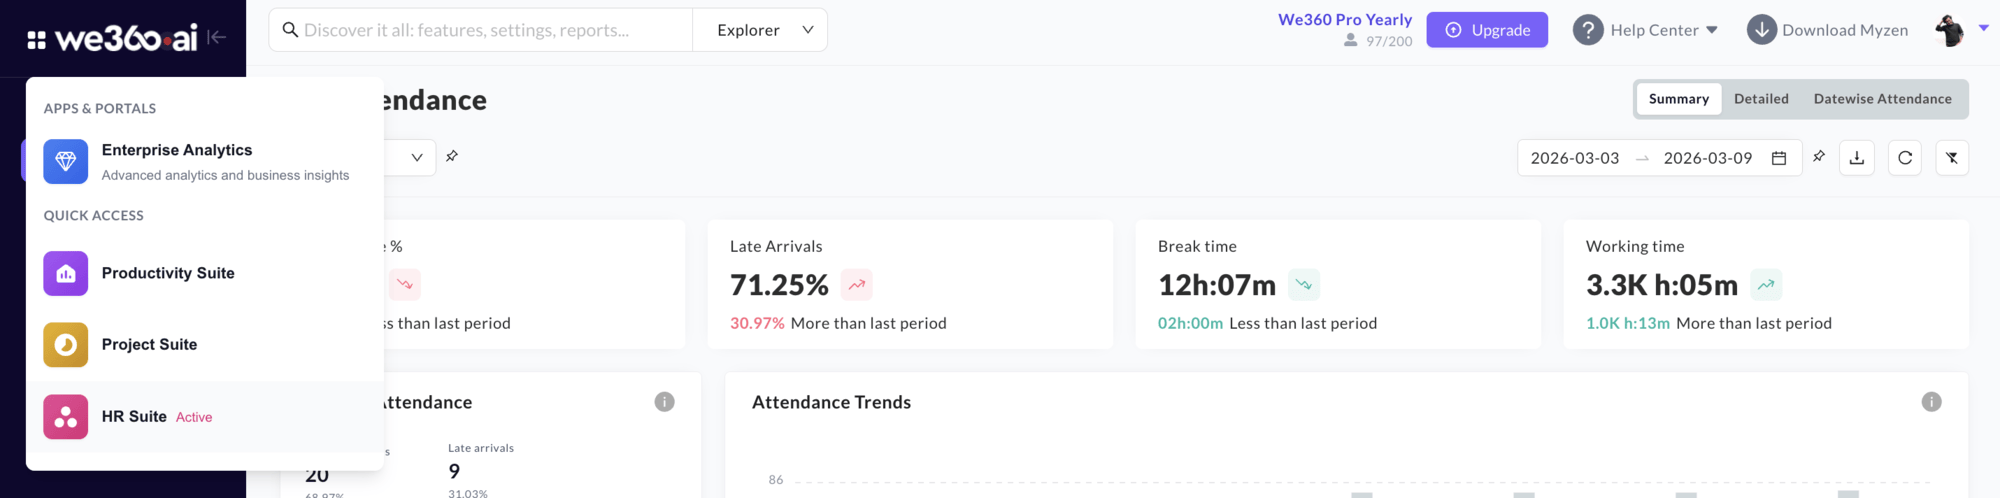
The We360.ai portal is organized around three role-based perspectives. Your sidebar navigation is automatically tailored to what your role can access.

{% tabs %}
{% tab title="Super Admin / Admin" %}
As an admin you have access to the full platform. Your sidebar includes:

* **Productivity Suite** -- Organization-wide activity dashboards, real-time view, analytics, and supplemental tracking.
* **Project Suite** -- Projects, timesheets, and notebooks.
* **HR Suite** -- Attendance and leave management for all employees.
* **Universal Tools** -- Bulk reports, alerts, integrations, and user detail drill-down.
* **Settings Center** -- Full platform configuration including user management, compliance, billing, and integrations.
  {% endtab %}

{% tab title="Manager" %}
Managers see the same sections as admins but scoped exclusively to their **assigned teams**. They cannot access billing or global settings.

Recommendations for managers:

* **Regular check-ins** -- Use analytics to inform one-on-one meetings, setting goals and addressing challenges.
* **Customize alerts** -- Set up alert rules for specific activities or milestones to stay informed proactively.
* **Leverage historical data** -- Use trend data for performance reviews, resource allocation, and identifying training needs.
* **Encourage feedback** -- Create open channels for team input on the analytics and tools in use.
  {% endtab %}

{% tab title="Employee" %}
If self-service access is enabled by the organization, employees can view their own activity timelines, attendance records, and leave balances.

The **Employee Dashboard** provides personalized analytics across five areas:

1. **Attendance** -- Daily and monthly attendance patterns, punch-in/out times, and working duration.
2. **Wellness** -- Work-life balance insights showing healthy, overburdened, and underutilized days with monthly breakdowns.
3. **Productivity** -- Top applications used, top URLs visited, and a breakdown of productive, unproductive, and neutral time.
4. **Activity** -- Online and break time breakdowns alongside active and idle time metrics.
5. **Apps & URLs** -- Detailed view of most-used applications and websites.

Use these insights to set personal goals, track progress, and maintain a healthy balance between work and rest.
{% endtab %}
{% endtabs %}

{% hint style="info" %}
The exact items visible in your sidebar depend on which features your organization has enabled. Contact your admin if a section you expect is missing.
{% endhint %}


# Setting Up Your Hierarchy

Set up departments, teams, and designations in We360.ai to organize employee monitoring and workforce analytics by role.

The We360.ai hierarchy mirrors your company's org chart. A correct structure ensures that managers see the right data and reports are meaningful.

## Hierarchy Concepts

{% columns %}
{% column %}

#### Departments

The top-level grouping. Typically maps to business units (e.g., "Engineering", "Operations", "Sales").
{% endcolumn %}

{% column %}

#### Teams

Sub-groups within a department, managed by a specific manager (e.g., "Frontend Team" under "Engineering").
{% endcolumn %}
{% endcolumns %}

{% columns %}
{% column %}

#### Designations

Job titles or roles used for filtering and reporting (e.g., "Senior Developer", "QA Engineer", "Account Manager").
{% endcolumn %}

{% column %}

#### Roles

Access-level permissions within the platform: **Super Admin**, **Admin**, **Manager**, or **Employee**.
{% endcolumn %}
{% endcolumns %}

## Understanding Roles and Permissions

We360.ai provides two primary user roles that control portal access:

<details>

<summary>Admin Role</summary>

Designed for administrators or managers overseeing team analytics. This role grants full access to various features and modules, subject to purchased licences.

* Access to complete team analytics for assigned teams.
* Ability to invite and manage users within their teams.
* Full control over group management and setting configurations.
* Unrestricted access to all purchased features and modules in the web portal.

Access is restricted to analytics of assigned teams only.

</details>

<details>

<summary>Standard Role</summary>

Tailored for individual employees, offering limited access focused on personal analytics and task management.

* Access to personal analytics on the employee dashboard.
* Ability to manage personal tasks and projects.
* Cannot access broader team or company analytics.

</details>

Admin users can invite new users, assign roles, customize access permissions, and update role assignments as organizational needs change. Settings that control both roles are only visible and adjustable by Admin users.

## Setup Steps

{% stepper %}
{% step %}

#### Create Departments

Go to **Settings > User Management** and navigate to the Teams & Designations section. Add your top-level departments first.
{% endstep %}

{% step %}

#### Create Teams

Under each department, add teams and assign a manager. A manager can only see data for users in their assigned team(s).
{% endstep %}

{% step %}

#### Create Designations

Add job titles that will be used to categorize employees. These can be used for role-based productivity rule targeting later.
{% endstep %}

{% step %}

#### Assign Users

When inviting users, assign them a department, team, and designation. This can also be done in bulk via CSV upload.
{% endstep %}
{% endstepper %}

{% hint style="warning" %}
An employee **must** be assigned to a team to appear in a manager's view. Unassigned employees are only visible to admins.
{% endhint %}


# Essential Pre-Flight Check

Pre-deployment checklist for We360.ai — system requirements, firewall rules, and agent connectivity for employee monitoring setup.

Before deploying the agent across your organization, complete these checks to ensure a smooth rollout.

## System Requirements

| Requirement           | Minimum Spec                                    |
| --------------------- | ----------------------------------------------- |
| **Operating Systems** | Windows 10+, macOS 13+, Ubuntu 20.04+           |
| **RAM**               | 4 GB                                            |
| **Disk Space**        | 500 MB free (for agent + local data cache)      |
| **Network**           | HTTPS (TCP 443) outbound access to `*.we360.ai` |

## Connectivity Checklist

{% stepper %}
{% step %}

#### Verify Firewall Rules

Ensure that the target machine can reach We360.ai endpoints. All traffic uses **HTTPS/WSS on TCP port 443**.

Recommended wildcard rules:

* `*.we360.ai`
* `*.in.we360.ai` *(India region)*

Refer to the [Allowlist Guide](https://docs.we360.ai/deployment-and-it-ops/network-and-security-hardening/allowlist-guide) for the full URL list if wildcards are not supported.
{% endstep %}

{% step %}

#### Grant macOS Permissions

If deploying on macOS, ensure the following permissions are granted via **System Settings → Privacy & Security**:

* **Screen Recording** — required for screenshot capture.
* **Input Monitoring** — required for idle detection.
* **Accessibility** — required for reading application window titles.

{% hint style="warning" %}
Without these permissions, the agent will report zero productivity on macOS.
{% endhint %}
{% endstep %}

{% step %}

#### Disable AV/EDR Conflicts

If your organization uses antivirus or endpoint detection software (e.g., CrowdStrike, Defender, SentinelOne), add We360.ai process exclusions before installation. See the [AV & EDR Exclusions](https://docs.we360.ai/deployment-and-it-ops/network-and-security-hardening/av-and-edr-exclusions) guide.
{% endstep %}

{% step %}

#### Test the Agent

Install the agent on a single pilot machine first. Log in, let it run for 5–10 minutes, then verify that activity appears on the dashboard. Only then proceed with mass deployment.
{% endstep %}
{% endstepper %}


# Reference

We360.ai reference docs — employee monitoring architecture, workforce analytics, productivity tracking, and compliance standards.

Not actionable. This is a detailed 'know us' section covering our framework, products, and interfaces.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-abacus">:abacus:</i></td><td><strong>Glossary</strong></td><td></td><td><a href="/reference/work-and-time-management/glossary">Glossary</a></td></tr><tr><td><i class="fa-cube">:cube:</i></td><td><strong>Framework</strong></td><td>Platform vision, system architecture, data privacy, compliance standards, and company processes.</td><td><a href="/reference/work-and-time-management/framework">Framework</a></td></tr><tr><td><i class="fa-box">:box:</i></td><td><strong>Product</strong></td><td>Complete product reference for Work &#x26; Time Management and Workforce Productivity features.</td><td><a href="/reference/work-and-time-management/product">Product</a></td></tr><tr><td><i class="fa-desktop">:desktop:</i></td><td><strong>User Interfaces</strong></td><td>Documentation for Desktop App, Mobile App, and Portal interfaces.</td><td><a href="/reference/work-and-time-management/user-interfaces">User Interfaces</a></td></tr></tbody></table>


# Glossary

List of terms encountered while using the portal and their meanings. Made to help users understand product features, reporting metrics, and how they compare to industry standards

{% hint style="info" %}
This glossary is alphabetized for convenience
{% endhint %}

## Abbreviations

* **DLP**—Data Loss Prevention
* **HRMS**—Human Resource Management System
* **RBAC**—Role-Based Access Control
* **RDP**—Remote Desktop Protocol
* **VDI**—Virtual Desktop Infrastructure

## A

### Active Time

**The total time tracked by the software based on keyboard/mouse input from the user.**

**See also:** Idle Time, Online Time

### Activity Report

See **Report**.

### Activity Trend

See **Input Activity**.

### Alert Rule

**A set of conditions that trigger automated notifications or log entries when specific user behaviors or system events occur.**

### API Free Tier

**The base level of API access provided at no additional cost, subject to specific rate limits.**

### API Pro Tier

**A high-performance API access level with increased rate limits for enterprise-scale integrations.**

### App & URL Usage

**A detailed record of the software applications and websites accessed by a user, including the duration of focus on each. These applications and URLs can be categorized as Productive, Neutral, or Unproductive per organization or team requirements.**

### Application Logging

See **App & URL Usage** or **Livestream**.

### Application Policy

**The classification of specific applications and URLs as productive, unproductive, or neutral based on an organization's requirements.**

### Approval Workflow

**A formalized process for reviewing and validating timesheet entries or manual time requests before they're finalized.**

### Attendance

**The record of an employee's presence during scheduled shifts, determined by punch-in and punch-out events.**

### Audit Log

**A chronological record of administrative actions taken within the system to ensure security and accountability.**

### Average Daily Hours

**The rolling average of hours tracked per employee over a specific period.**

## B

### Billing Plan

**The specific subscription tier and license count assigned to an organization's account.**

### Break

**A period of allowable downtime during a working session, tracked separately from active and idle time.**

**See also:** Break Policy

### Break Policy

**The rules defining allowable downtime, including duration, paid status, and permitted applications during breaks.**

### Break Report

See **Report**.

### Built-in Permission Role

**A predefined set of system access rights assigned to users, such as Standard or Admin.**

### Business Intelligence

**A module for creating custom KPI charts and visualizations across productivity, activity, and attendance metrics.**

## C

### Capacity Planning

**An analytics framework for measuring workforce utilization by comparing actual hours worked against ideal capacity.**

### Category Mapping

See **App & URL Usage**.

### Company Profile

**The central repository for an organization's legal information, contact details, and billing address.**

### Compliance Configuration

**Settings that govern the strictness of monitoring, including privacy levels, stealth mode, and capture frequencies.**

### Configurable Captures

See **Compliance Configuration**.

### Cross-Day Attendance

See **Shift Configuration**.

### Custom Project Field

**A user-defined data attribute, such as a billing code or client ID, attached to a project for specialized reporting.**

**See also:** Custom User Field

### Custom User Field

**A user-defined data attribute, such as an employee ID or job level, attached to a user profile.**

## D

### Data Loss Prevention (DLP)

**Security features designed to detect and prevent unauthorized data exfiltration and ensure client confidentiality.**

**See also:** USB Detection, Security Alert

### Default Report Columns

**Parameters displayed by default in system-generated reports.**

### Default View

**The standard visual layout shown to users upon their first login to the dashboard.**

### Department

**A top-level group in the organizational hierarchy, containing one or more Teams.**

**See also:** Team, Organizational Hierarchy

### Designation

**A user's job title within a team or the organization's hierarchy.**

### Desktop Agent

**The tracking application installed on a Windows, macOS, or Linux computer that records application and URL usage, input activity, and screenshots. Supported in Citrix, RDP, and VDI environments.**

**See also:** Device, Stealth Mode

### Device

**A computer or smartphone that runs the tracking agent.**

### Device360

**A detailed view providing hardware and software metadata for a specific monitored endpoint, such as a user's computer or smartphone. Provides details such as IP address, location, and more.**

## E

### Employee Performance Metric

**A composite measure of a user's output, based on attendance, activity levels, goal achievement, and other relevant parameters.**

### Epic

**A large body of work in the project hierarchy that groups related tasks.**

**See also:** Task, Project

## F

### Field Workforce

**Employees who perform their duties outside of a traditional office environment, tracked via mobile GPS.**

## G

### Geofence

**A virtual geographic boundary that triggers an alert or log entry when a field employee enters or exits the area.**

### Goal Achievement Tracking

See **Productivity Goal**.

### Goals

See **Productivity Goal**.

## H

### Half-Day Rule

**The configuration that determines when a working day is counted as a half-day based on total hours or punch times.**

## I

### Ideal Capacity

**The expected number of working hours for an employee or team within a specific period, used as a benchmark for utilization.**

### Identity

**A unique record representing an individual user's account and related data. Also referred to as ID.**

### Idle Time

**Time during which no keyboard or mouse activity is detected for a specific threshold. The threshold can be edited by Admins.**

**See also:** Active Time, Online Time

### Input Activity

**Physical interaction with a device via keyboard and mouse inputs, used to gauge engagement.**

**See also:** Live Activity Status, Active Time

### Integration

**A connection between We360 and an external platform, such as an HRMS, project tool, or identity provider, that synchronizes data via OAuth, API, or webhooks.**

**See also:** OAuth & API Configuration, Webhook, Sync Priorities

### Invoice

**A billing document recording an amount paid or due for the organization's subscription, downloadable as a PDF for accounting. Also referred to as invoicing.**

**See also:** Billing Plan

## L

### Live Activity Status

**A real-time indicator showing whether a user is currently active, idle, or offline based on recent activity.**

**See also:** Input Activity, Livestream

### Livestream

**A real-time broadcast of one or more active employee screens for live tracking.**

**See also:** On-Demand Screenshot

## M

### Manual Time

**Working hours logged by an employee for activities performed away from a monitored device.**

### Mobile App

**The application installed on iOS or Android devices for location tracking and mobile workforce management.**

## O

### OAuth & API Configuration

**The settings for connecting the platform to external systems using secure authentication protocols.**

### On-Demand Screenshot

**A high-resolution screenshot of a user's current screen in real time.**

**See also:** Livestream, Screenshot

### Online Time

**The total duration for which the user was logged in, regardless of user activity.**

**See also:** Active Time, Idle Time

### Organizational Hierarchy

**The structured mapping of an organization into Departments, Teams, and Designations to drive reporting and access control.**

**See also:** Designation

## P

### Performance Metrics

See **Employee Performance Metric**.

### Productive Active Time

**Duration spent in applications deemed "Productive" during which the user was actively engaged with their computer based on keyboard strokes or mouse input.**

**See also:** Productive Passive Time, Productivity Classification

### Productive Passive Time

**Duration spent in applications deemed "Productive" during which no keyboard or mouse input was detected, for example when watching a video or attending an online meeting.**

**See also:** Productive Active Time, Idle Time

### Productivity Classification

**The categorization of time into Productive, Unproductive, or Neutral based on which applications are being used.**

**See also:** Productive Active Time, Unproductive Time

### Productivity Goal

**A target set for individuals or teams, typically defining a minimum number of productive hours required per shift.**

**See also:** Employee Performance Metric

### Project

**A unit of trackable or billable work that tasks and time entries are logged against, with configurable visibility and team assignment.**

**See also:** Task, Timesheet, Custom Project Field

### Punch In/Out

**The action of an employee signaling the start or end of their working session, either manually or automatically.**

**See also:** Attendance, Shift Configuration

### Punch Marker

**A visual indicator on the user's timeline showing the exact time of their first and last punch of the day.**

**See also:** Punch In/Out, Timeline

## R

### Report

**A structured export of system data, available in formats like PDF or CSV, covering metrics such as attendance and productivity.**

**See also:** Business Intelligence

### Role-Based Overrides

See **Application Policy**.

## S

### Screenshot

**A periodic image capture of a user's display, used to provide visual context for tracked activities.**

**See also:** On-Demand Screenshot

### Security Alert

**A notification triggered by high-risk events, such as accessing a blacklisted URL or connecting an unauthorized USB device.**

**See also:** Alert Rule, Data Loss Prevention (DLP)

### Shift Configuration

**The definition of standard working hours, grace periods, and rules for half-day or full-day attendance marking.**

**See also:** Attendance, Punch In/Out

### SSO

**Single Sign-On; a mechanism that allows users to authenticate once and access multiple systems using federated credentials.**

**See also:** OAuth & API Configuration

### Stealth Mode

**A mode of the tracking software that operates continuously in the background without any visible UI or user interaction. It begins logging data the moment the device is turned on, until the user logs off, unlike regular mode where a Punch In is required to begin tracking.**

**See also:** Compliance Configuration

### Sync Priorities

**The rules establishing which system acts as the source of truth when synchronizing data between We360 and an external platform.**

**See also:** OAuth & API Configuration

## T

### Task

**A discrete unit of work within a project, categorized as an Epic, Task, or Bug, that time can be logged against.**

**See also:** Project, Epic

### Team

**A group of users within a Department, used for bulk reporting and group-based access filtering.**

**See also:** Department, Designation, Organizational Hierarchy

### Tenant

**A customer organization representing the top-level boundary for data isolation, users, and settings in the platform.**

### Tenant Manager

**A user role with permissions to manage specific teams or departments, typically including access to reports and approvals.**

### Tenant Owner

**The primary administrative user for a tenant, possessing full access to all settings, billing, and organizational data. The role assigned to a Tenant Owner is usually "Super Admin."**

### Tenant User

**A standard employee account within a tenant, typically restricted to viewing their own data and performance metrics.**

### Timeline

**A chronological visualization of an employee's working day, mapping activities, idle spans, and screenshots over a 24-hour axis.**

**See also:** Punch Marker

### Timesheet

**A record of the hours a user has logged against projects and tasks over a period, subject to optional managerial approval before finalization.**

**See also:** Approval Workflow, Manual Time, Project

## U

### Unclassified Time

**Time spent in applications or on websites that haven't yet been assigned a productivity classification, tagged "Neutral" by default.**

**See also:** Productivity Classification

### Unproductive Time

**Time spent in applications or on websites that have been explicitly classified as non-work-related.**

**See also:** Productivity Classification, Alert Rule

### USB Detection

**A security feature that logs and alerts when external mass storage devices are connected to or disconnected from a monitored machine.**

**See also:** Data Loss Prevention (DLP)

### User Directory

**The centralized list of all employees within a tenant, used for managing profiles, team assignments, and reporting lines.**

**See also:** Identity

## W

### Webhook

**An automated message sent from the platform to an external URL whenever a specific event, such as a punch-in or alert, occurs.**

**See also:** OAuth & API Configuration

### Wellness Threshold

**Limits set on continuous working hours or minimum break duration to identify and prevent potential employee burnout.**

**See also:** Break Policy

### Working Time

See **Average Daily Hours**.

## Z

### ZenAI

**The integrated AI assistant that provides natural language insights and automated visualizations for productivity and workforce data.**

**See also:** Business Intelligence


# Framework

We360.ai framework — platform architecture, data privacy, compliance standards, and employee monitoring philosophy.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><h4><i class="fa-lightbulb">:lightbulb:</i></h4></td><td><strong>Platform Vision &#x26; Core Pillars</strong></td><td>The intersection of Wellness, Productivity, and Business Intelligence.</td><td><a href="/reference/work-and-time-management/framework/platform-vision-and-core-pillars">Platform Vision &amp; Core Pillars</a></td></tr><tr><td><h4><i class="fa-cog">:cog:</i></h4></td><td><strong>The Anatomy of the We360.ai Agent</strong></td><td>Technical overview of data capture, URL/App monitoring, and Offline sync.</td><td><a href="/reference/work-and-time-management/framework/anatomy-of-the-we360.ai-agents">The Anatomy of the We360.ai Agent</a></td></tr><tr><td><h4><i class="fa-lock">:lock:</i></h4></td><td><strong>Data Privacy &#x26; Ethics</strong></td><td>Privacy by Design: The Blur engine, stealth vs. visible modes, and data ownership.</td><td><a href="/reference/work-and-time-management/framework/data-privacy-and-ethics">Data Privacy &amp; Ethics</a></td></tr><tr><td><h4><i class="fa-project-diagram">:project-diagram:</i></h4></td><td><strong>System Architecture</strong></td><td>Cloud vs. On-Premise data flow and API layer communication.</td><td><a href="/reference/work-and-time-management/framework/system-architecture">System Architecture</a></td></tr><tr><td><h4><i class="fa-certificate">:certificate:</i></h4></td><td><strong>Compliance &#x26; Security Standards</strong></td><td>GDPR, HIPAA, SOC2 readiness, SLA/SLO, RPO, RTO and encryption.</td><td><a href="/reference/work-and-time-management/framework/compliance-and-security-standards">Compliance &amp; Security Standards</a></td></tr><tr><td><h4><i class="fa-briefcase">:briefcase:</i></h4></td><td><strong>Company Processes</strong></td><td>SDLC, Device Policies, Personnel policies, Incident Management.</td><td><a href="/reference/work-and-time-management/framework/company-processes">Company Processes</a></td></tr></tbody></table>


# Platform Vision & Core Pillars

We360.ai vision — workforce analytics platform combining employee wellness, productivity tracking, and business intelligence.

**1. Platform Vision**

We360.ai envisions enhancing global productivity through technology by transforming scattered workplace data into meaningful, actionable intelligence. At the intersection of Wellness, Productivity and Business Intelligence, the platform reflects the evolving nature of modern work and decision-making. Born in the era of flexible and hybrid work, the platform enables organizations to ensure that teams, leaders and business outcomes stay aligned regardless of where work happens.

By converting work behaviour and operational data into realtime insights and business intelligence — captured at per-second granularity across all major platforms (Windows, macOS, Linux, iOS, and Android) — We360.ai helps organizations improve the way work is processed, strengthen communication and drive efficiency, proving that productivity, wellness and flexibility can coexist.

At its core, the platform aims to create a transparent, data driven, efficient and performance focused work culture where both organizations and employees move forward together, supported by insights that balance organizational productivity with employee wellness and business intelligence.

**2. Core Pillars**

**Integrity & Intent**\
We take responsibility for our actions by aligning what we do with what we say, building trust through clarity, ownership and authenticity.

**Set Standard**\
We continuously raise the bar for quality, challenge the status quo and strive to create the next benchmark in everything we deliver.

**Push the Boundaries**\
We move forward with urgency and determination, doing what it takes to innovate, evolve and drive the company and our customers, toward the future.


# The Anatomy of the We360.ai Agent

We360.ai desktop agent internals — stealth mode, silent monitoring, screen recording, app tracking, and offline data sync.

We360.ai provides comprehensive productivity and activity tracking designed to operate seamlessly across **all major platforms — Windows, macOS, Linux, iOS, and Android** — whether a user is online or offline. This tracking is delivered through two distinct desktop applications tailored for different operational needs: the **Standard App** and the **Stealth App**. Both modes offer the same full-featured tracking capabilities, with the Stealth App operating silently as a fully functional background service.

## 1. Operating Modes

{% tabs %}
{% tab title="Standard Mode" %}
Provides employees with a visible Desktop Agent, allowing them to manually punch in/out, pause tracking, or view their own stats. Designed for environments requiring transparent, user-driven time tracking.
{% endtab %}

{% tab title="Stealth Mode" %}
Installs the tracker silently in the background, operating entirely without UI interaction. It runs as a fully functional system service, delivering the same per-second tracking capabilities as Standard Mode — including app & URL tracking, input monitoring, screenshots, and screen recording — while automatically tracking work during configured shifts.
{% endtab %}
{% endtabs %}

## 2. Data Capture Mechanisms

The core engine of the agent is responsible for continuously but efficiently capturing the following data points at **per-second granularity**, ensuring no work activity is missed:

* **App & URL Tracking:** The desktop app passively watches the active window title and records the application or domain URL in focus. It records the exact duration — down to the second — the app or URL remains active. A dedicated **Chrome Extension** is also available for enhanced browser-level tracking.
* **Input Tracking:** Fully functional keyboard and mouse activity tracking with **sub-second precision** — logging interaction frequency by counting keystrokes and mouse clicks (without recording actual keys pressed or characters typed). We360.ai does **not** perform keylogging; only aggregate counts are captured to ensure privacy while calculating active versus idle time.
* **Visual Data:** Captures periodic screenshots mapping to specific tracked time intervals, if permitted by policy.
* **Location Tracking:** The Standard App includes built-in location tracking, complementing the mobile app's GPS-based field tracking to provide comprehensive whereabouts visibility across both desktop and mobile endpoints.

## 3. Offline-First Architecture

To ensure uninterrupted tracking regardless of internet stability, both We360.ai applications utilize a robust offline-first architecture:

{% stepper %}
{% step %}
**Local Storage**

All captured data (text metrics, screenshots, and recordings) is immediately written to a local database on the user's machine.
{% endstep %}

{% step %}
**Periodic Sync**

When network connectivity is detected, the agent initiates a background sync, securely transmitting the local data to the backend API over encrypted HTTPS.
{% endstep %}

{% step %}
**Data Integrity**

Once the server confirms receipt of the data, the local database marks the data as synced and clears the database to optimize space.
{% endstep %}
{% endstepper %}

## 4. Privacy and Security Compliance

Protecting user data and maintaining organizational compliance is built into the architecture of both applications.

* **Data in Transit:** All synced data is securely transmitted and encrypted using standard HTTPS protocols. Real-time livestreams are secured via WSS (WebSocket Secure).
* **Compliance Standards:** Built to strictly align with major global compliance and security frameworks, including SOC 2, GDPR, DPDP, and HIPAA. The platform also includes **Data Loss Prevention (DLP)** capabilities to help organizations detect and prevent unauthorized data exfiltration.
* **Virtual Desktop Support:** Fully supports **Citrix, RDP, and VDI environments**, enabling organizations to monitor virtual desktop sessions with the same fidelity as physical endpoints.
* **Privacy Controls:**
  * *Screenshot Blurring:* Protects sensitive on-screen data. Administrators can adjust the blur level to ensure privacy without compromising activity monitoring.
  * *URL Blocking:* Enforce internet usage policies directly through the portal by creating blacklists of domains that the local agent should actively block access to.


# Data Privacy & Ethics

We360.ai data privacy — blur engine, stealth vs. visible monitoring modes, GDPR compliance, and employee data ownership.

**Data Privacy & Ethics**

At We360.ai, data protection and ethical processing of workforce analytics are governed by strict legal, regulatory and information security standards. Our platform is designed to ensure that organizational visibility is achieved without compromising individual privacy, data ownership or lawful processing principles.

## Lawful, Fair & Purpose Limited Processing

We360.ai processes data solely for legitimate and explicitly defined business purposes, including productivity insights, operational analytics, insights, system security and regulatory compliance.

Data collection is limited to what is relevant, necessary and proportionate to these purposes, in alignment with globally accepted privacy principles and the requirements of the Digital Personal Data Protection Act (DPDP Act 2023), India.

## Transparency & Informed Use

{% hint style="info" %}
We enable organizations to implement clear and auditable monitoring policies by providing:

* Configurable tracking controls aligned to business requirements
* Visibility into what data is collected and how it is used
* Access for users to view their own work analytics

This ensures transparency, supports informed deployment and promotes accountable data governance.
{% endhint %}

## Data Subject Rights & Control

We360.ai supports the exercise of user rights, including the ability to:

* Access and review personal data
* Request rectification or erasure, where applicable
* Withdraw consent in consent based environments
* Raise grievances through defined redressal mechanisms

Data ownership remains with the customer organization and We360.ai acts as a data processor in accordance with contractual obligations.

## Security & Technical Safeguards

We maintain enterprise grade information security controls to ensure the confidentiality, integrity and availability of data, including:

* Encryption of data in transit and at rest
* Role based access control and least privilege enforcement
* Secure hosting infrastructure
* Continuous monitoring and vulnerability management

Our security framework aligns with internationally recognized standards such as ISO 27001, VAPT and SOC 2 Type II.

## Data Collection Specifics

All data collected by the We360.ai agent is encrypted both in transit and at rest using Google Cloud Platform (GCP) for secure storage.

<details>

<summary>Computer and User Information</summary>

The agent collects essential device and session metadata (not tied to individual user activities):

* **Computer Name** -- The machine's hostname.
* **Computer Timezone** -- The local timezone configured on the device.
* **Logon Domain** -- The Active Directory domain name, or the computer name if not domain-joined.
* **Network ID** -- A hashed representation used for uniqueness.
* **Private IP** -- Local network IP address.
* **Public IP** -- Internet-facing IP address.
* **Session ID** -- Identifies different user sessions, particularly on terminal servers.
* **User Information** -- Login names from the operating system (friendly name and simple login name).

</details>

<details>

<summary>User Activity Information</summary>

User activity is defined as the currently active window with mouse movement, mouse clicks, and keypresses — all captured with **sub-second precision**. We360.ai provides fully functional keyboard and mouse activity tracking but does **not** perform keylogging; individual characters typed are never recorded. The information collected includes:

* **Date and Time** -- When a specific activity was first accessed.
* **Description** -- Brief description of each activity.
* **Duration** -- Time spent on an activity.
* **Executable** -- The executable file associated with each activity.
* **Screenshots** -- Periodic screenshots of the active window (frequency is configurable).
* **Title** -- Content of the title bar of the activity window.
* **URL** -- Full URL accessed in a browser for web-based activities.

</details>

<details>

<summary>Data We Never Collect</summary>

We360.ai strictly does not collect:

* **Keystroke logging** -- Individual keystrokes are never recorded.
* **Video camera monitoring** -- Webcam feeds are never accessed or recorded.

</details>

## The Blur Engine

To further strengthen privacy protection, We360.ai incorporates a built-in **Blur Engine** designed to prevent the exposure of sensitive or confidential information during screen monitoring or analytics processes.

The Blur Engine automatically obscures or masks sensitive visual data that may appear on user screens, ensuring that productivity insights can be generated without revealing confidential content.

{% hint style="success" %}
The Blur Engine reinforces We360.ai’s commitment to **privacy by design**, ensuring that productivity analytics and workforce intelligence can be delivered while minimizing unnecessary exposure of sensitive data.
{% endhint %}

<details>

<summary>Key Capabilities of the Blur Engine</summary>

* Automatic blurring of sensitive on-screen content where required
* Configurable privacy settings aligned with organizational policies
* Protection of confidential information such as personal communications, financial details, authentication fields, or other sensitive data elements
* Support for privacy-conscious monitoring practices in hybrid and remote work environments

</details>

## Data Lifecycle

{% columns %}
{% column %}
**Data Retention & Minimization**

Data is retained only for the duration necessary to fulfill the specified purpose or to meet contractual and legal requirements. Upon expiry of the retention period, data is securely deleted or irreversibly anonymized.
{% endcolumn %}

{% column %}
**Third-Party Processing**

If required, any engagement with subprocessors is governed by strict confidentiality, data processing agreements and equivalent security obligations. Cross border data transfers, where applicable, are conducted in compliance with relevant legal frameworks.
{% endcolumn %}
{% endcolumns %}

## Compliance Commitment

Our privacy and security program are structured to support compliance with major global data protection and industry regulations:

{% tabs %}
{% tab title="DPDP" %}
**Digital Personal Data Protection Act 2023 (India)** Aligns with requirements governing the processing of digital personal data in India.
{% endtab %}

{% tab title="GDPR" %}
**General Data Protection Regulation** Governs the protection of personal data for individuals within the European Union.
{% endtab %}

{% tab title="CCPA" %}
**California Consumer Privacy Act** Provides California residents with enhanced rights regarding the use of their personal data.
{% endtab %}

{% tab title="HIPAA" %}
**Health Insurance Portability and Accountability Act** Protects sensitive patient health information from being disclosed without the patient's consent or knowledge.
{% endtab %}

{% tab title="SOC 2 Type II" %}
**Service Organization Control 2 Type II** Validates that internal controls meet the Trust Service Criteria.
{% endtab %}
{% endtabs %}

## Governance & Accountability

We maintain internal policies, audit mechanisms and contractual controls to ensure responsible data handling and continuous compliance with evolving regulatory standards.

<details>

<summary>Data Governance Policies</summary>

**Data Residency**

Customer data is hosted in secure cloud infrastructure environments designed to meet enterprise security and compliance requirements. Where applicable, We360.ai supports hosting customer data within specific geographic regions to comply with regulatory or organizational data residency requirements. For customers operating in India, data may be hosted within infrastructure located in India to support compliance with the Digital Personal Data Protection Act and other applicable regulations.

**Data Ownership**

Customers retain full ownership of the data they provide or generate within We360.ai. The organization does not sell, rent, or commercially exploit customer data. Customer data is processed solely for the purpose of delivering platform services and supporting system functionality.

**Data Usage Limitations**

Customer data is processed only for legitimate operational purposes related to the delivery of platform services including:

* Platform functionality and analytics
* System monitoring and troubleshooting
* Service improvement and reliability

Unauthorized access, sharing, or use of customer data is strictly prohibited. Data usage is governed by strict access control policies and internal security procedures.

</details>

<details>

<summary>Customer Access &#x26; Portability</summary>

**Customer Data Access Rights**

Customers maintain control over access to their data within We360.ai. Authorized customer administrators can:

* Manage user access permissions
* Configure system integrations
* View and analyze operational data
* Export data where functionality permits

**Data Portability**

Customers may request access to their data in order to export or transfer it for operational or compliance purposes through APIs, system reports, or explicit export mechanisms.

</details>

## Ethical Use of Workforce Analytics

We360.ai is built on the principle that workforce analytics must enable better work outcomes while preserving individual dignity, trust and organizational transparency. The platform is designed to generate objective, work pattern based insights that support process optimization, capacity planning and data driven decision making, rather than employee surveillance.

Workplace data is contextualized to reflect productivity trends, application usage patterns and workflow efficiency, ensuring that insights are business relevant and not behaviorally intrusive.

{% hint style="info" %}
We360.ai does not position analytics as a tool for micromanagement or punitive evaluation. Instead, it enables organizations to adopt a balanced, proportionate and policy driven approach that is consistent with applicable data protection laws, internal governance frameworks and globally accepted workplace ethics standards.
{% endhint %}

We360.ai promotes ethical deployment by enabling organizations to:

* Define role-based and policy driven tracking configurations aligned with business needs.
* Restrict monitoring to designated work hours and authorized environments.
* Provide employees visibility into their own productivity analytics to encourage self improvement and accountability.
* Use aggregated and trend based insights for performance conversations, workforce planning and process enhancement.
* Avoid disproportionate or covert monitoring practices.

### Stealth and Visible Modes

We360.ai provides configurable deployment options through Stealth Mode and Visible Mode, allowing organizations to align monitoring practices with their internal policies and regulatory requirements.

{% tabs %}
{% tab title="Visible Mode" %}
Ensures transparency by displaying the application interface to users, allowing them to view their work analytics and system status. Users are required to punch in & out in Visible Mode.
{% endtab %}

{% tab title="Stealth Mode" %}
Where permitted by applicable laws and organizational policies, allows the monitoring agent to operate silently in the background without a visible interface. Stealth Mode is fully functional — all tracking features (per-second activity monitoring, screenshots, input tracking, and screen recording) work identically to Visible Mode.
{% endtab %}
{% endtabs %}


# System Architecture

We360.ai system architecture — cloud vs. on-premise deployment, API communication, and employee monitoring data flow.

Our platform is designed to provide you with real-time endpoint visibility without compromising your network performance or data security.

***

### How We Process and Protect Your Data

1\. Secure Access & Identity Management (Zero-Trust Foundation): We integrate with your existing security postures rather than forcing you to build new ones.

* Authentication and Authorization Service: All connections—from endpoint agents to portal users—must pass through strict authentication. We support enterprise SSO and OAuth2, ensuring your team accesses the platform using your established corporate credentials.
* Licensing & Entitlements Service: A dedicated service validates licenses and enforces Role-Based Access Control (RBAC), guaranteeing that your users only see the data and features they're explicitly authorized to access.

2\. High-Performance, Low-Impact Ingestion: Your endpoint performance and network stability are our top priorities.

* Asynchronous Processing: Endpoints push encrypted telemetry and media to our Ingestion API, which immediately offloads it to a Raw Data Store. This decoupled design ensures that sudden spikes in your endpoint activity will never bottleneck the system or slow down the devices.
* Intelligent Routing (Workers): A fleet of background workers silently parses, enriches, and normalizes your data before securely routing it to the appropriate storage systems.
* Real-Time Livestreaming: When your admins need instant visibility, our Livestream Server establishes a low-latency, secure WebSocket (WSS) connection directly to the endpoint, bypassing the main database to deliver real-time screen feeds.

3\. Segregated Storage for Speed and Compliance: To guarantee lightning-fast dashboard performance and simplify your data retention policies, we strictly segregate how we store your data:

* Analytics DB: Highly optimized for structured telemetry and event logs, powering your rapid analytics and trend reporting.
* Metadata DB: Securely stores your system configurations, user profiles, and security policies.
* Object Store: A highly scalable vault for your media, such as session recordings and screenshots.

4\. Ecosystem Integration & Actionable Insights: The platform is designed to break down data silos and feed your existing workflows.

* Targeted APIs: Your Web Portal accesses data through specialized APIs. The Management API handles policy updates securely, while the Analytics API crunches complex queries instantly.
* Automated Reporting: The system handles scheduled jobs, alert digests, and secure CSV/email delivery, pushing vital information to your stakeholders automatically.
* Extensibility: Built-in push (Webhooks/Streaming) and pull (API) capabilities mean our platform easily feeds your existing SIEM, BI, or ITSM tools.

```mermaid
 sequenceDiagram
    actor EP as Endpoint Device
    participant AUTH as Auth Server
    participant LIC as Licensing Server
    participant IG as Ingestion API
    participant RAW as Raw Data Store
    participant OBJ as Object Store
    participant WK as Workers
    participant MDB as Metadata DB
    participant ADB as Analytics DB
    participant LS as Livestream Server
    participant MAPI as Mgmt and Metadata API
    participant AAPI as Analytics API
    participant RPT as Reporting
    participant EXT as External Integrations
    actor PO as Web Portal

    %% Auth flow — Endpoint
    EP->>AUTH: HTTPS — authenticate and request token
    AUTH-->>EP: Token issued

    %% Auth flow — Portal
    PO->>AUTH: HTTPS — authenticate and request token
    AUTH-->>PO: Token issued

    %% Licensing flow — Endpoint
    EP->>LIC: HTTPS — validate license and check entitlements
    LIC-->>EP: License confirmed

    %% Licensing flow — Portal
    PO->>LIC: HTTPS — validate license and seat count
    LIC-->>PO: License confirmed

    %% Licensing flow — Mgmt API
    MAPI->>LIC: HTTPS — verify feature entitlements
    LIC-->>MAPI: Entitlements confirmed

    %% Ingest flow
    EP->>IG: HTTPS POST — activity events and media
    IG->>IG: Validate and authenticate
    IG-->>EP: 200 OK
    IG->>RAW: Write raw payload
    IG->>OBJ: Store screenshots and recordings

    %% Worker processing
    RAW->>WK: Consume raw payload
    WK->>MDB: Write user and policy metadata
    WK->>ADB: Write events and activity
    WK->>RPT: Trigger scheduled jobs and alert digests
    WK->>EXT: Push — webhooks and streaming
    EXT->>WK: Pull — third-party API requests

    %% Livestream flow
    EP-)LS: WSS — live screen feed
    LS-)PO: WSS — Live Monitor Dashboard

    %% Management Dashboard flow
    PO->>MAPI: HTTPS — fetch config, policies, user data
    MAPI->>MDB: Read metadata
    MDB-->>MAPI: Results
    MAPI-->>PO: Response — Management Dashboard
    PO->>MAPI: HTTPS — update config or policy
    MAPI->>MDB: Write metadata
    MDB-->>MAPI: Acknowledged
    MAPI-->>PO: Confirmed

    %% Analytics Dashboard flow
    PO->>AAPI: HTTPS — query filters and aggregates
    AAPI->>ADB: Fetch events and activity
    ADB-->>AAPI: Results
    AAPI-->>PO: Response — Analytics Dashboard

    %% Reporting output
    RPT-->>PO: CSV export and email delivery

```

```mermaid
flowchart TD
    DEVICE["Endpoint Device"]

    subgraph CORE["Core Services"]
        INGEST["Ingestion API"]
        RAW[("Raw Data Store")]
        WORKERS["Workers<br/>• Parse<br/>• Enrich<br/>• Normalize<br/>• Route"]
        LS["Livestream Server<br/>• WSS"]
    end

    AUTH["Auth Server<br/>• Token Issuance<br/>• Session Validation<br/>• SSO / OAuth2"]

    LIC["Licensing Server<br/>• License Validation<br/>• Seat Management<br/>• Feature Entitlements"]

    subgraph STORES["Data Stores"]
        MDB[("Metadata DB<br/>• Users<br/>• Policies<br/>• Config")]
        ADB[("Analytics DB<br/>• Events<br/>• Activity")]
        OBJ[("Object Store<br/>• Screenshots<br/>• Recordings")]
    end

    subgraph APIS["APIs"]
        MAPI["Mgmt &amp; Metadata API<br/>• Auth / RBAC<br/>• Settings<br/>• Policies"]
        AAPI["Analytics API<br/>• Queries<br/>• Aggregates<br/>• Filters"]
    end

    RPT["Reporting<br/>• Scheduled Jobs<br/>• Alert Digests<br/>• CSV Export<br/>• Email Delivery"]

    EXT["External Integrations<br/>• Push — Webhooks / Streaming<br/>• Pull — Third-party API Access"]

    subgraph PORTAL["Web Portal"]
        LIVE["Live Monitor Dashboard"]
        ADASH["Analytics Dashboard"]
        MDASH["Management Dashboard"]
    end

    DEVICE <-->|HTTPS| AUTH
    DEVICE <-->|HTTPS| LIC
    DEVICE -->|HTTPS| INGEST
    DEVICE <-->|WSS| LS
    LS <--> LIVE

    PORTAL <-->|HTTPS| AUTH
    PORTAL <-->|HTTPS| LIC
    MAPI <-->|HTTPS| LIC

    INGEST --> RAW
    INGEST --> OBJ
    RAW --> WORKERS

    WORKERS --> MDB
    WORKERS --> ADB
    WORKERS --> RPT
    WORKERS <--> EXT

    MDB <--> MAPI
    ADB --> AAPI

    AAPI --> ADASH
    MAPI --> MDASH

```


# Screenshot & Recording Upload

How the We360.ai desktop agent uploads screenshots and screen recordings — out-of-band signed-URL / data-relay pipeline, server-side encryption, and segregated object storage.

The desktop agent never blocks tracking on media transfer. Screenshots and screen recordings are captured to disk, referenced from the activity event by a small **identifier**, and uploaded **out-of-band** on the regular sync ticks. The telemetry event itself carries no image bytes — only the identifier the backend later resolves to the stored object.

This decoupling means a slow or unreachable object store never delays activity data, and a media upload can retry independently without ever losing an event.

***

## The image identifier

Every screenshot is addressed by an opaque **imageId** — e.g. a date-scoped token, optionally prefixed with `enc/` when the tenant has encryption enabled. The agent computes it at capture time and writes it into the activity event's `image_path`.

The backend is the **single source of truth** for turning an imageId into a storage key:

```
<tenant>/screens/<identity>/<imageId>.png
```

The tenant and identity segments always come from the **authenticated token**, never from the client — so a compromised or crafted identifier can never write into another tenant's or user's space. The agent only ever supplies the opaque imageId; it never constructs a full storage path.

Because the same derivation is used when signing the **upload** URL and when signing the **read** URL, an object written out-of-band lands exactly where the viewer later looks for it.

***

## Upload routes

Which route the agent uses depends on whether the tenant has **screenshot encryption** enabled.

{% tabs %}
{% tab title="Encryption disabled" %}
The full image is uploaded **directly to the object store** via a short-lived pre-signed `PUT` URL requested from the backend. A matching pre-signed URL is used for the thumbnail.

If the direct `PUT` is blocked (e.g. a corporate firewall that allows only the We360.ai API host), the agent transparently falls back to the **data relay** — same bytes, same verb, an allow-listed host.
{% endtab %}

{% tab title="Encryption enabled" %}
Screenshot bytes are encrypted with a **per-tenant key that lives only on the backend** and is never distributed to endpoints. The agent therefore cannot encrypt locally, so the full image is sent through the **data relay**, which is the encryption boundary: it encrypts the bytes server-side and stores the ciphertext at the derived key.

Thumbnails are generated by the relay from the received bytes and stored unencrypted (they contain only a low-resolution preview).
{% endtab %}
{% endtabs %}

### The data relay

The data relay is a media-upload endpoint used both as the encrypted-upload path and as the firewall fallback for direct uploads. It has two wire-compatible implementations — one embedded in the core service, one a standalone service — that the agent cannot tell apart. Authentication is performed at the mesh, which forwards the validated tenant and identity; the relay derives the storage path from those authenticated principals plus the agent-supplied imageId.

For encrypted tenants the standalone relay fetches the tenant's encryption configuration from an internal, service-only API and caches it. If that configuration cannot be retrieved, the upload **fails closed** — the relay never stores plaintext when the encryption state is unknown.

***

## Segregated storage

Screenshots and screen recordings are stored in **separate** backends and are never crossed:

* **Screenshots** → image object store (full image + thumbnail).
* **Screen recordings** → video object store.

The relay routes each upload by media kind to the correct backend. Screen recordings now upload through the relay endpoints as well; the earlier signed-URL recording endpoints remain available but are deprecated.

***

## Resilience & local cleanup

Uploads are asynchronous and self-healing:

* On a transient failure the local file is **kept on disk** and retried on the next sync tick; a blocked direct upload falls back to the relay automatically.
* A local file is deleted **only** on a strictly-validated success response — a genuine relay acknowledgement or a confirmed object-store `PUT`, not merely any `2xx`. A misconfigured or wrong endpoint can never trigger premature deletion.
* As a disk-safety backstop, a file that has still not uploaded **30 days** after capture is pruned.

Because the activity event is synced independently of the bytes, a stuck upload only means a temporarily missing preview in the portal — never a lost event or a lost work record.

***

## Data flow

```mermaid
sequenceDiagram
    participant Agent as Desktop Agent
    participant API as Ingestion / Sign API
    participant Relay as Data Relay
    participant Store as Object Store

    Agent->>Agent: Capture to disk, compute imageId
    Agent->>API: Activity event (image_path = imageId, no bytes)

    alt Encryption disabled
        Agent->>API: Request pre-signed PUT URL (imageId)
        API-->>Agent: Signed URL (derived key)
        Agent->>Store: PUT image + thumbnail
        Note over Agent,Store: On firewall block → fall back to Relay
    else Encryption enabled
        Agent->>Relay: PUT bytes (imageId)
        Relay->>Relay: Fetch tenant key (cached), encrypt
        Relay->>Store: Store ciphertext + thumbnail
    end

    Store-->>Agent: Validated OK → delete local file
```


# Compliance & Security Standards

We360.ai compliance — GDPR, HIPAA, SOC2 standards, encryption, SLA/SLO, and employee monitoring data security.

Detailed documentation on the compliance certifications, security architecture, and operational standards that govern the We360.ai platform.

## SOC 2 Compliance

We360.ai has achieved full SOC 2 Type 1 and Type 2 compliance, reinforcing our dedication to maintaining the highest standards of security and operational excellence.

<details>

<summary>What is SOC 2 Compliance?</summary>

SOC 2 compliance, established by the American Institute of Certified Public Accountants (AICPA), involves a thorough audit that evaluates an organization's systems and controls for processing customer data. It focuses on security, availability, processing integrity, confidentiality, and privacy of the system.

**SOC 2 Type 1 vs. Type 2:**

* **Type 1** -- Assesses the design of security processes at a specific point in time.
* **Type 2** -- Examines the operational effectiveness of these processes over a period, typically six months to a year.

We360.ai has been awarded both SOC 2 Type 1 and Type 2 compliance.

</details>

### Trust Service Principles

SOC 2 compliance is based on five Trust Service Principles:

| Principle                | Description                                                                                                                           |
| ------------------------ | ------------------------------------------------------------------------------------------------------------------------------------- |
| **Security**             | Protecting system resources against unauthorized access.                                                                              |
| **Availability**         | Ensuring system availability as committed or agreed.                                                                                  |
| **Processing Integrity** | System processing is complete, valid, accurate, timely, and authorized.                                                               |
| **Confidentiality**      | Information designated as confidential is protected as such.                                                                          |
| **Privacy**              | Personal information is collected, used, retained, disclosed, and destroyed in conformity with the commitments in the privacy notice. |

### Maintaining Compliance

To maintain SOC 2 compliance, We360.ai:

* Regularly reviews and updates security policies and procedures.
* Conducts ongoing training for staff to ensure compliance with these policies.
* Engages in continuous monitoring and auditing of security systems and processes.
* Undergoes annual audits to renew SOC 2 compliance.

Clients interested in reviewing the SOC 2 report can contact the We360.ai team for detailed information and access.

## Additional Standards

<details>

<summary>GDPR Readiness</summary>

We360.ai's data handling practices align with the General Data Protection Regulation (GDPR), ensuring lawful processing, data minimization, and support for data subject rights for individuals within the European Union.

</details>

<details>

<summary>HIPAA Considerations</summary>

For organizations handling protected health information, We360.ai's encryption, access controls, and audit logging capabilities support HIPAA compliance requirements.

</details>

<details>

<summary>Data Encryption</summary>

* **In Transit** -- All data transmitted between the agent and We360.ai servers is encrypted using TLS.
* **At Rest** -- All stored data is encrypted using industry-standard encryption on Google Cloud Platform (GCP) infrastructure.

</details>

<details>

<summary>Infrastructure and Hosting</summary>

We360.ai leverages the security protocols of Google Cloud Platform (GCP) for data infrastructure, providing robust protection and high availability.

</details>


# Company Processes

We360.ai governance — security processes, workforce analytics policies, and organizational compliance documentation.

<details>

<summary>1. Introduction</summary>

This document outlines the operational, governance, security and support processes followed for We360.ai. The purpose of this document is to provide enterprise customers with transparency into the systems, processes and controls that ensure reliable and secure service delivery.

This document is intended to address common requirements raised during:

* Vendor Due Diligence
* Security Questionnaires
* Enterprise RFP processes
* IT and Risk Assessments

**The document covers:**

* Product Release Management
* Change Management
* Incident Management
* Infrastructure Governance
* Data Security Practices
* Business Continuity & Disaster Recovery
* Customer Onboarding
* Customer Support & Escalation
* Vendor & Third-Party Governance
* Compliance and Operational Governance
* Continuous Improvement
* Security Certifications, Compliance & Regulatory Alignment
* Data Protection & Data Flow Architecture
* Security Controls & Technical Safeguards
* Risk Management & Security Governance Framework
* Secure Software Development Lifecycle (SSDLC)
* Service Level Agreements (SLA) & Operational Commitments

· Data Residency, Data Ownership & Customer Rights

· Audit, Reporting & Compliance Assurance

</details>

<details>

<summary>2. Product Release Management</summary>

We360.ai follows a structured release management process to ensure that all product updates are delivered in a controlled, reliable and secure manner.

Release Lifecycle

2.1 Product Planning

Product features and enhancements are identified through:

* Product roadmap planning
* Customer feedback
* Security improvements
* Performance enhancements

Features are prioritized based on customer impact and business value.

2.2 Development

Engineering teams develop product features in controlled development environments. Secure development practices are followed, including:

* Version control
* Code reviews
* Branch management
* Development environment segregation

2.3 Code Review

All code changes undergo peer review to ensure:

* Code quality
* Security best practices
* Performance standards
* Compliance with architecture guidelines

2.4 Testing

Multiple testing layers are performed before release:

* Functional testing
* Regression testing
* Performance testing
* Integration testing

Where applicable, security checks and vulnerability scans are also conducted.

2.5 Staging Validation

Approved builds are deployed to staging environments that replicate production configurations. This allows teams to validate:

* System stability
* Integration compatibility
* Feature behaviour

2.6 Production Release

Once validation is complete, releases are deployed to production environments through controlled deployment pipelines.

Deployment typically occurs during planned release windows to minimize service impact.

2.7 Post-Release Monitoring

After deployment, system monitoring tools track:

* Performance metrics
* Error logs
* System availability

Any anomalies are investigated immediately.

2.8 Release Types

| Release Type      | Description                             |
| ----------------- | --------------------------------------- |
| Minor Release     | Bug fixes and small improvements        |
| Feature Release   | New features or enhancements            |
| Emergency Release | Critical fixes such as security patches |

Release notes and change logs are maintained for traceability.

</details>

<details>

<summary>3. Change Management</summary>

A structured change management process ensures that modifications to the system are implemented in a controlled and auditable manner.

3.1 Change Categories

Standard Changes

Routine operational updates with minimal risk.

Examples:

* Minor configuration updates
* System optimizations

Normal Changes

Planned system updates requiring internal review and approval.

Examples:

* Feature updates
* Infrastructure modifications

Emergency Changes

Urgent changes implemented to resolve critical issues such as system outages or security vulnerabilities.

3.2 Change Management Process

1\. Change Request Initiation

o Internal change request logged

2\. Impact Assessment

o Risk analysis conducted

o Technical impact reviewed

3\. Approval

o Relevant technical stakeholders approve the change

4\. Deployment Planning

o Release window defined

o Rollback plan prepared

5\. Implementation

o Change deployed in production environment

6\. Validation

o System performance verified

o Functionality confirmed

7\. Documentation

o Change logs updated

o Records maintained for audit purposes

</details>

<details>

<summary>4. Incident Management</summary>

We360.ai follows a structured incident management framework to ensure that service disruptions are addressed quickly and effectively.

4.1 Incident Sources

Incidents may be identified through:

* System monitoring alerts
* Customer support reports
* Internal engineering detection
* Infrastructure monitoring tools

4.2 Incident Response Workflow

1\. Incident detection

2\. Incident logging

3\. Severity classification

4\. Investigation by engineering team

5\. Issue resolution or mitigation

6\. Root cause analysis

7\. Preventive actions

4.3 Incident Severity Levels

| Severity | Description                        |
| -------- | ---------------------------------- |
| Critical | Complete system outage             |
| High     | Major feature disruption           |
| Medium   | Partial functionality issue        |
| Low      | Minor issue or enhancement request |

Critical incidents receive immediate attention from engineering teams.

5\. Infrastructure & Cloud Hosting

We360.ai is hosted on secure cloud infrastructure designed for scalability, availability and reliability.

5.1 Infrastructure Characteristics

* Cloud-native architecture
* Scalable infrastructure resources
* High availability configuration
* Continuous system monitoring

5.2 Hosting Environment

We360.ai is hosted on secure cloud infrastructure with primary hosting located in India to support enterprise data residency expectations.

Infrastructure includes:

* Secure networking layers
* Firewall configurations
* Access restrictions
* Monitoring systems

5.3 Infrastructure Monitoring

Infrastructure monitoring tools track:

* Server health
* System availability
* Resource usage
* Error logs

Alerts are triggered if abnormal behaviour is detected.

</details>

<details>

<summary>6. Data Security &#x26; Privacy</summary>

Data security is a core operational priority.

6.1 Security Controls

Key security practices include:

* Encryption of data in transit using secure protocols
* Controlled access to infrastructure and administrative systems
* Continuous monitoring of system activity
* Logging and auditing mechanisms

6.2 Access Management

Access to We360.ai is governed through:

· Role-Based Access Control (RBAC): Users are assigned permissions based on their roles within the organization.

· Least Privilege Model: Users and administrators receive only the minimum access required to perform their responsibilities.

· Administrative Access: Administrative system access is restricted to authorized personnel and monitored through logging systems.

</details>

<details>

<summary>7. Business Continuity &#x26; Disaster Recovery</summary>

Business continuity processes ensure that We360.ai can continue operating even during unexpected disruptions.

7.1 Key Measures

* Automated data backup procedures
* Infrastructure redundancy
* Disaster recovery planning
* Operational monitoring

7.2 Backup Policy

System configurations and essential operational data are backed up regularly to ensure recoverability.

7.3 Disaster Recovery

In the event of infrastructure disruption:

1\. Engineering teams investigate the failure

2\. Recovery procedures are initiated

3\. Services are restored using backup infrastructure

Periodic reviews ensure disaster recovery readiness.

</details>

<details>

<summary>8. Customer Onboarding</summary>

Customer onboarding is designed to allow new organizations to start using We360.ai quickly and efficiently.

8.1 Onboarding Steps

Step 1: Account Creation

Users register on We360.ai and verify their accounts.

Step 2: Organization Setup

Customers configure their organization profile and workspace.

Step 3: Onboarding Wizard

A guided onboarding wizard assists users with:

* Initial configuration
* Team member setup
* System settings

Step 4: User Management

Administrators add team members and assign roles.

Step 5: System Setup

Customers configure productivity & team mapping role setting required for data collection.

Step 6: Data Synchronization

Once setup is complete, operational data begins appearing in We360.ai dashboard.

Documentation such as the 5-Minute Launch Guide helps users quickly understand We360.ai functionality.

</details>

<details>

<summary>9. Customer Support &#x26; Escalation</summary>

Customer support ensures that users receive assistance when needed.

9.1 Support Channels

Customers can reach support through:

* Email support
* Support ticket system
* Customer success engagement

9.2 Support Escalation Model

| Level   | Responsibility              |
| ------- | --------------------------- |
| Level 1 | Customer Support Team       |
| Level 2 | Product Support Specialists |
| Level 3 | Engineering Team            |

Critical issues are escalated immediately to engineering teams for investigation.

</details>

<details>

<summary>10. Vendor &#x26; Third-Party Management</summary>

We360.ai may utilize third-party service providers to support infrastructure and operations.

10.1 Vendor Categories

Typical vendors include:

* Cloud infrastructure providers
* External Auditors
* Security tools

10.2 Vendor Evaluation

Before engaging with any vendor, the following factors are reviewed:

* Security posture
* Infrastructure reliability
* Compliance standards
* Operational stability

Vendor relationships are periodically reviewed to ensure ongoing compliance.

</details>

<details>

<summary>11. Compliance &#x26; Security Governance</summary>

Governance processes ensure alignment with enterprise operational and security expectations.

11.1 Governance Controls

The organization maintains documentation related to:

* Product architecture
* Security practices
* Release history
* Change logs
* Operational procedures

These documents support enterprise:

* Vendor risk assessments
* Security reviews
* Compliance audits
* RFP evaluations

</details>

<details>

<summary>12. Continuous Improvement</summary>

We360.ai follows a continuous improvement approach to enhance reliability, security and customer experience.

12.1 Improvement Initiatives

* Monitoring system performance
* Reviewing incident trends
* Implementing security improvements
* Incorporating customer feedback
* Enhancing operational processes

Regular internal reviews ensure We360.ai evolves to meet enterprise operational standards.

</details>

<details>

<summary>13. Security Certifications, Compliance &#x26; Regulatory Alignment</summary>

We360.ai follows industry-recognized security and privacy standards to ensure the protection of customer data and operational integrity. The organization aligns with globally accepted frameworks, regulatory requirements and security best practices.

These certifications and compliance programs demonstrate our commitment to maintaining enterprise-grade security, privacy protection and regulatory adherence.

13.1 Security Certifications

SOC 2 Type II

We360.ai maintains compliance with SOC 2 Type II, which validates that the organization's internal controls meeting the Trust Service Criteria.

SOC 2 Type II focuses on the following trust principles:

* Security
* Availability
* Processing Integrity
* Confidentiality
* Privacy

The certification involves an independent audit that evaluates the effectiveness of security controls over a defined monitoring period. This ensures that security practices are not only designed appropriately but also operate effectively over time.

Key SOC 2 control areas include:

* Access control management
* Infrastructure monitoring
* Change management
* Incident response
* Data protection controls
* Vendor management

ISO/IEC 27001

We360.ai aligns with the ISO/IEC 27001 framework, which defines best practices for establishing and maintaining an Information Security Management System (ISMS).

ISO 27001 focuses on:

* Risk management
* Information security policies
* Asset management
* Access control
* Cryptography
* Incident management
* Business continuity

This framework ensures a systematic approach to managing sensitive information and maintaining strong security governance practices.

ISO/IEC 27017

We360.ai aligns with ISO/IEC 27017, which provides additional security guidance specifically for cloud service providers and cloud-based systems.

Key areas covered include:

* Cloud infrastructure security
* Shared responsibility model
* Virtual machine security
* Cloud service configuration controls
* Administrative access governance

This standard ensures that cloud deployments follow recognized best practices for protecting data and workloads in cloud environments.

ISO/IEC 27018

We360.ai follows privacy protection guidelines defined in ISO/IEC 27018, which focuses on protecting personally identifiable information (PII) in public cloud environments.

Key protections include:

* Restrictions on data processing
* Transparency in data handling
* Customer data ownership protections
* Secure deletion of data
* Privacy-focused operational controls

13.2 Security Assessments

Vulnerability Assessment & Penetration Testing (VAPT)

We360.ai undergoes periodic Vulnerability Assessment and Penetration Testing conducted by qualified security professionals.

The objective of VAPT is to identify potential security weaknesses and proactively address them before they can be exploited.

The assessment typically includes:

* Network vulnerability assessment
* Application security testing
* Infrastructure security review
* Penetration testing simulations

Findings from these assessments are prioritized based on severity and remediated according to internal security policies.

Regular VAPT exercises help ensure We360.ai remains resilient against emerging security threats.

13.3 Privacy & Data Protection Regulations

We360.ai is designed to support compliance with major global privacy regulations governing the protection of personal data.

Digital Personal Data Protection Act 2023 (DPDP)

We360.ai aligns with the requirements of the Digital Personal Data Protection Act 2023, which governs the processing of digital personal data in India.

Key principles supported include:

* Lawful data processing
* User consent management
* Data minimization
* Secure storage and processing
* Protection against unauthorized access

These measures help ensure compliance with India's evolving data protection landscape.

General Data Protection Regulation (GDPR)

We360.ai supports compliance with the General Data Protection Regulation, which governs the protection of personal data for individuals within the European Union.

GDPR compliance principles include:

* Lawful processing of personal data
* Transparency in data collection
* Data minimization
* Data subject rights
* Security safeguards
* Breach notification mechanisms

We360.ai incorporates controls that enable organizations to meet GDPR requirements when handling personal data.

California Consumer Privacy Act (CCPA)

We360.ai supports compliance with the California Consumer Privacy Act, which provides California residents with enhanced rights regarding the use of their personal data.

We360.ai enables organizations to support CCPA requirements including:

* Data transparency
* Consumer access rights
* Data deletion requests
* Data usage disclosures

Health Insurance Portability and Accountability Act (HIPAA)

For customers operating within healthcare ecosystems, We360.ai aligns with the principles of Health Insurance Portability and Accountability Act.

HIPAA focuses on protecting Protected Health Information (PHI) through:

* Administrative safeguards
* Physical safeguards
* Technical safeguards

These protections help ensure the confidentiality, integrity and availability of sensitive healthcare data.

13.4 Ongoing Security Governance

Security and compliance controls are continuously monitored and improved through:

* Periodic security assessments
* Internal security reviews
* Infrastructure monitoring
* Access control audits
* Incident response testing
* Security training and awareness

The organization is committed to maintaining high standards of security and privacy to meet enterprise and regulatory expectations.

</details>

<details>

<summary>14. Data Protection &#x26; Data Flow Architecture</summary>

We360.ai follows a secure data architecture designed to protect customer information throughout its lifecycle. The architecture incorporates security controls at every stage of data handling, including collection, transmission, processing, storage and deletion.

The system architecture is designed following security frameworks such as SOC 2 Type II and ISO/IEC 27001.

14.1 Data Flow Overview

We360.ai processes data through the following controlled stages:

1\. Data Collection

2\. Data Transmission

3\. Data Processing

4\. Data Storage

5\. Data Access & Usage

6\. Data Retention & Deletion

Each stage incorporates encryption, authentication and monitoring mechanisms to protect data integrity and confidentiality.

14.2 Data Collection

Data is collected from customer systems using secure integration methods configured during onboarding.

Collection mechanisms may include:

* Secure API integrations
* Platform connectors or agents
* System integrations configured by the customer
* User inputs through the application interface

Data collection follows the principle of data minimization, meaning only the data required for platform functionality is collected.

Customer administrators retain control over integration configurations and permissions.

14.3 Data Transmission

All communication between customer environments and We360.ai is secured using encrypted protocols.

Transmission protections include:

* HTTPS/TLS encrypted communication
* Secure API authentication
* Token-based authorization mechanisms
* Network traffic monitoring

Encryption prevents interception, tampering, or unauthorized access during data transmission.

14.4 Data Processing

After transmission, data is processed within secured application environments.

Processing operations may include:

* Data analysis
* Monitoring operations
* Event correlation
* System analytics

Application services operate in isolated environments to ensure secure processing and prevent unauthorized cross-access.

Strict access control policies ensure internal systems only access required datasets.

14.5 Data Storage

Customer data is stored within secure cloud infrastructure environments.

Security controls for storage include:

* Encryption of stored data
* Access-controlled databases
* Network segmentation
* Infrastructure monitoring

Data is logically separated by tenant to ensure that one organization's data cannot be accessed by another.

14.6 Data Access Controls

Access to platform data is governed through Role-Based Access Control (RBAC).

User roles may include:

* Organization Administrators
* Operational Users
* Read-Only Users

Permissions are granted according to job responsibilities following the least privilege principle.

Administrative system access is restricted to authorized personnel.

.7 Data Retention

Data retention policies define how long data is stored within We360.ai.

Retention periods depend on:

* Operational requirements and Agreements
* Customer configuration
* Security monitoring needs
* Regulatory requirements

Logs and operational data may be retained for monitoring, auditing and compliance purposes.

14.8 Data Deletion

Data deletion procedures are implemented when:

* Data reaches the end of its retention period
* Customers request deletion
* Customer contracts terminate

Deletion processes may include:

* Secure database deletion
* Storage cleanup
* Backup lifecycle expiration

These processes help ensure that customer data is not retained beyond required periods.

14.9 Monitoring & Data Protection Controls

Continuous monitoring is implemented to detect unauthorized activity or system anomalies.

Monitoring mechanisms include:

* Infrastructure monitoring
* Application log monitoring
* Security alerts
* Access activity tracking

Security events are handled through the incident management process.

14.10 Privacy Protection

We360.ai supports compliance with major privacy regulations including:

* Digital Personal Data Protection Act
* General Data Protection Regulation
* California Consumer Privacy Act
* Health Insurance Portability and Accountability Act

Privacy protections focus on secure data processing, transparency and protection of personal data.

</details>

<details>

<summary>15. Security Controls &#x26; Technical Safeguards</summary>

We360.ai implements a layered security model designed to protect systems and customer data from unauthorized access, misuse and security threats.

Security controls align with frameworks such as ISO/IEC 27001 and SOC 2 Type II.

15.1 Access Control

Access to systems and data is governed by strict identity and access management policies.

Controls include:

* Role-Based Access Control (RBAC)
* Least privilege access model
* User authentication mechanisms
* Administrative access restrictions

Access rights are reviewed periodically to ensure that users retain only necessary permissions.

Administrative access to production systems is limited to authorized personnel.

15.2 Authentication & Identity Management

User identity verification is implemented through secure authentication mechanisms.

These include:

* Secure login authentication
* Password policy enforcement
* Session management controls
* Access revocation procedures for inactive users

Identity verification helps ensure that only authorized users access We360.ai.

15.3 Encryption Controls

Encryption protects sensitive data during transmission and storage.

Encryption measures include:

Encryption in Transit

* TLS-based encrypted communication
* Secure API connections

Encryption at Rest

* Encrypted database storage
* Secure storage configurations
* Infrastructure-level encryption controls

These encryption practices prevent unauthorized access to stored or transmitted data.

15.4 Logging & Audit Trails

Logging systems capture activity across We360.ai to support monitoring, troubleshooting and security investigations.

Logged events may include:

* User authentication events
* Administrative activities
* System configuration changes
* Access attempts
* Security alerts

Logs are retained for operational monitoring and compliance purposes.

Audit trails help maintain accountability and transparency within We360.ai.

15.5 Security Monitoring

Security monitoring systems continuously observe platform activity to identify potential threats.

Monitoring capabilities include:

* Infrastructure health monitoring
* Application monitoring
* Security alerting
* Log analysis

Alerts are generated for suspicious activities and investigated by engineering teams.

15.6 Vulnerability Management

We360.ai maintains a proactive vulnerability management process.

Security activities include:

* Regular vulnerability scanning
* Periodic Vulnerability Assessment and Penetration Testing
* Security patching
* Risk prioritization and remediation

Security findings are reviewed and remediated based on severity levels.

5.7 Incident Response

Security incidents are managed through a defined incident response process.

The process includes:

1\. Detection of security events

2\. Incident classification

3\. Investigation and containment

4\. Resolution and recovery

5\. Root cause analysis

Security incidents are handled in accordance with internal incident management procedures.

15.8 Security Governance & Continuous Improvement

Security controls are continuously reviewed and improved through:

* Security audits
* Compliance assessments
* Infrastructure monitoring
* Incident trend analysis
* Security awareness initiatives

These measures ensure that We360.ai maintains a strong and evolving security posture.

</details>

<details>

<summary>16. Risk Management &#x26; Security Governance Framework</summary>

The organization follows a structured risk management and security governance framework to ensure that information security risks are identified, assessed and mitigated in a systematic manner.

The framework aligns with industry standards such as ISO/IEC 27001 and incorporates security best practices to protect systems, infrastructure and customer data.

Security governance ensures that policies, procedures and controls are continuously reviewed and improved to maintain a strong security posture.

16.1 Information Security Governance

Information security governance establishes the policies and responsibilities required to manage and protect organizational information assets.

Key governance principles include:

* Defined security policies and procedures
* Role-based responsibilities for security management
* Security oversight and accountability
* Periodic review of security controls
* Alignment with regulatory and compliance requirements

Security governance helps ensure that security controls remain effective and aligned with business and regulatory expectations.

16.2 Risk Management Process

A formal risk management process is followed to identify and mitigate risks associated with information systems and infrastructure.

The risk management lifecycle includes the following stages:

Risk Identification

Potential risks are identified through:

· Security assessments

· Infrastructure reviews

· Vulnerability scans

· Incident analysis

· Vendor assessments

Risk Assessment

Identified risks are evaluated based on:

· Likelihood of occurrence

· Potential impact on systems or data

· Exposure to operational disruption

Risk Mitigation

Appropriate mitigation strategies are implemented, including:

· Security controls

· Process improvements

· Infrastructure safeguards

· Monitoring mechanisms

Risk Monitoring

Risks are continuously monitored to ensure controls remain effective.

Periodic reviews are conducted to reassess risks and update mitigation strategies.

16.3 Security Policies & Standards

The organization maintains documented security policies that guide operational and security practices.

Key policy areas include:

* Information security policy
* Access control policy
* Data protection policy
* Incident response policy
* Change management policy
* Vendor management policy
* Acceptable use policy

These policies establish the security framework for managing and protecting organizational assets.

16.4 Security Risk Assessments

Regular security assessments are conducted to identify vulnerabilities and evaluate the effectiveness of existing controls.

Security assessments may include:

* Internal security reviews
* Infrastructure security assessments
* Application security testing
* Threat analysis

Periodic Vulnerability Assessment and Penetration Testing is performed to detect potential vulnerabilities and strengthen We360.ai’s security posture.

Findings are prioritized based on severity and remediated through defined security processes.

16.5 Security Awareness & Training

Security awareness programs help ensure that employees understand their responsibilities in protecting organizational systems and data.

Training initiatives may include:

* Security awareness training
* Data protection best practices
* Secure system usage guidelines
* Phishing and social engineering awareness

These programs help reduce risks caused by human error and strengthen the overall security culture.

16.6 Vendor Risk Management

Third-party vendors that support infrastructure or operational services are evaluated to ensure they meet security and reliability standards.

Vendor risk assessments may include evaluation of:

* Security posture
* Compliance certifications
* Infrastructure reliability
* Data protection practices

Vendor relationships are periodically reviewed to ensure continued compliance with security expectations.

16.7 Compliance Monitoring

Security and compliance controls are regularly reviewed to ensure adherence to industry standards and regulatory requirements.

We360.ai supports compliance with frameworks such as:

* SOC 2 Type II
* ISO/IEC 27001
* ISO/IEC 27017
* ISO/IEC 27018

Compliance activities include:

* Security audits
* Policy reviews
* Control testing
* Continuous monitoring

16.8 Continuous Security Improvement

The organization follows a continuous improvement approach to maintain and enhance its security posture.

Security improvements are driven by:

* Incident reviews
* Security audit findings
* Vulnerability assessments
* Emerging threat intelligence
* Customer feedback and enterprise security reviews

These practices ensure that the security program evolves to address new risks and maintain alignment with global security standards.

</details>

<details>

<summary>17. Secure Software Development Lifecycle (SSDLC)</summary>

The organization follows a Secure Software Development Lifecycle (SSDLC) to ensure that security is integrated throughout the entire software development process. Security practices are incorporated from the initial design stage through development, testing, deployment and ongoing maintenance.

The SSDLC framework ensures that security risks are identified early, vulnerabilities are minimized and secure coding practices are consistently followed.

17.1 Security by Design

Security considerations are incorporated during the initial stages of product design and architecture planning.

Key design practices include:

* Threat modeling and risk identification during design stages
* Secure architecture planning
* Data protection and privacy considerations in system design
* Implementation of least-privilege access principles
* Secure API design and authentication mechanisms

By addressing security at the design stage, potential vulnerabilities can be prevented before development begins.

17.2 Secure Development Practices

Developers follow established secure coding guidelines to minimize vulnerabilities within application code.

Secure development practices include:

* Use of secure coding standards
* Input validation and output encoding
* Protection against common web vulnerabilities
* Proper error handling and logging
* Secure configuration management

Development environments are controlled and separated from testing and production environments to prevent unauthorized access.

17.3 Code Review & Version Control

All application code is maintained in version-controlled repositories and undergoes peer review before being merged into the main codebase.

Code review processes help ensure:

* Adherence to coding standards
* Security best practices
* Code quality and maintainability
* Identification of potential vulnerabilities

Version control systems maintain a history of changes, ensuring traceability and accountability for all modifications.

17.4 Security Testing

Security testing is integrated into the development and testing lifecycle to identify vulnerabilities before software is released.

Testing activities may include:

* Application security testing
* Static code analysis
* Dynamic testing of application behavior
* Dependency vulnerability checks

In addition, periodic Vulnerability Assessment and Penetration Testing may be conducted to evaluate the security posture of We360.ai.

Security issues discovered during testing are documented and remediated according to defined severity levels.

17.5 Environment Segregation

To maintain system integrity and security, the organization maintains separate environments for:

* Development
* Testing
* Staging
* Production

This separation ensures that development activities do not affect production systems and helps prevent unauthorized code from reaching live environments.

Access to production environments is restricted to authorized personnel.

17.6 Secure Deployment

Deployment processes follow controlled procedures to ensure that only approved and tested code is released into production environments.

Deployment controls include:

* Automated deployment pipelines where applicable
* Controlled release management processes
* Approval mechanisms for production releases
* Rollback procedures in case of deployment issues

Deployment logs are maintained to track system changes and maintain auditability.

17.7 Dependency & Vulnerability Management

Software dependencies and third-party libraries are monitored to ensure they remain secure.

Dependency management practices include:

* Tracking third-party libraries and components
* Monitoring known vulnerability databases
* Applying security updates and patches when required

Regular updates help reduce exposure to vulnerabilities present in external libraries.

17.8 Security Incident Handling

If vulnerabilities or security issues are identified within the application, they are addressed through the organization’s incident management and vulnerability management processes.

The process includes:

1\. Identification of the security issue

2\. Risk and severity assessment

3\. Remediation planning

4\. Deployment of security fixes

5\. Post-resolution review

Security incidents are documented and analyzed to prevent recurrence.

17.9 Continuous Security Improvement

The SSDLC framework is continuously improved through:

* Security reviews of development practices
* Feedback from security testing activities
* Monitoring emerging threat landscapes
* Improvements to development tools and processes

These efforts ensure that the software development process evolves alongside evolving security threats and industry best practices.

</details>

<details>

<summary>18. Service Level Agreements (SLA) &#x26; Operational Commitments</summary>

The organization is committed to maintaining reliable and consistent service delivery through clearly defined Service Level Agreements (SLAs) and operational processes. These commitments help ensure that enterprise customers receive dependable system availability, responsive support and timely resolution of operational issues.

Operational commitments are designed in alignment with enterprise best practices and security frameworks such as SOC 2 Type II and ISO/IEC 27001.

18.1 Service Availability

We360.ai is designed to provide high levels of service availability through resilient infrastructure and proactive monitoring.

Key availability practices include:

* Cloud-based infrastructure with scalable resources
* Infrastructure monitoring and alerting systems
* Redundant system components where applicable
* Incident response procedures for service disruptions

These measures help maintain continuous service availability and minimize downtime.

18.2 System Uptime Commitment

We360.ai targets a high level of service availability for production environments.

Typical uptime targets may include:

| Service Component         | Target Availability             |
| ------------------------- | ------------------------------- |
| Application Platform      | 99.9% uptime                    |
| Core Services             | 99.9% uptime                    |
| Infrastructure Components | High availability configuration |

Availability calculations typically exclude scheduled maintenance windows or extraordinary events beyond operational control.

18.3 Incident Response & Resolution Targets

Incidents are prioritized based on severity and business impact.

| Severity Level | Description                                     | Response Target               | Resolution Target               |
| -------------- | ----------------------------------------------- | ----------------------------- | ------------------------------- |
| Critical       | Complete service outage or major system failure | Immediate response            | Highest priority resolution     |
| High           | Major feature unavailable or major degradation  | Within defined support window | Prompt resolution               |
| Medium         | Partial functionality issue                     | Standard support response     | Scheduled resolution            |
| Low            | Minor issue or enhancement request              | Best effort response          | Future release or scheduled fix |

Critical incidents receive immediate attention and escalation to engineering teams.

18.4 Support Availability

Customer support services are available to assist customers with operational issues and platform usage questions.

Support channels may include:

* Email-based support
* Customer success engagement
* Technical support ticket system

Support requests are tracked through internal ticketing systems to ensure accountability and timely resolution.

18.5 Escalation Process

An escalation framework ensures that issues are addressed by the appropriate technical teams.

| Escalation Level | Responsibility                          |
| ---------------- | --------------------------------------- |
| Level 1          | Customer Support Team                   |
| Level 2          | Product Support / Technical Specialists |
| Level 3          | Engineering Team                        |

Critical or complex issues are escalated to engineering teams for investigation and resolution.

18.6 Scheduled Maintenance

To maintain system reliability and performance, periodic maintenance activities may be performed.

Maintenance activities may include:

* Infrastructure updates
* Security patching
* Performance improvements
* Platform upgrades

Where possible, scheduled maintenance is conducted during predefined maintenance windows to minimize service disruption.

Customers may be notified in advance of planned maintenance activities when they are expected to impact service availability.

18.7 Monitoring & Operational Oversight

Continuous monitoring systems are implemented to detect and respond to operational issues.

Monitoring capabilities include:

* Infrastructure health monitoring
* Application performance monitoring
* System error tracking
* Security alerting

Alerts generated by monitoring systems are investigated promptly to maintain system stability.

18.8 Communication During Incidents

When significant incidents occur, communication may be provided to affected customers through appropriate channels.

Communication may include:

* Notification of service disruption
* Status updates during incident resolution
* Confirmation when services are restored

These communications help maintain transparency and provide customers with visibility into operational events.

18.9 Continuous Service Improvement

Operational performance is regularly reviewed to identify opportunities for improvement.

Service improvement initiatives may include:

* Monitoring service performance metrics
* Reviewing incident trends
* Enhancing infrastructure reliability
* Improving response and resolution procedures

Continuous improvement ensures that operational processes evolve alongside customer needs and industry best practices.

</details>

<details>

<summary>19. Data Residency, Data Ownership &#x26; Customer Rights</summary>

The organization is committed to ensuring transparency and accountability in how customer data is stored, processed and managed. This section outlines policies related to data residency, data ownership and customer rights concerning data hosted within We360.ai.

These policies are designed to align with global data protection regulations and enterprise data governance expectations.

19.1 Data Residency

Customer data is hosted in secure cloud infrastructure environments designed to meet enterprise security and compliance requirements.

Where applicable, We360.ai supports hosting customer data within specific geographic regions to comply with regulatory or organizational data residency requirements.

For customers operating in India, data may be hosted within infrastructure located in India to support compliance with the Digital Personal Data Protection Act and other applicable regulations.

Data residency ensures that organizations maintain appropriate jurisdictional control over their data and comply with regional data protection laws.

19.2 Data Ownership

Customers retain full ownership of the data they provide or generate within We360.ai.

The organization does not claim ownership over customer data. Data collected and processed by We360.ai remains the property of the respective customer organization.

Customer data is processed solely for the purpose of delivering platform services and supporting system functionality.

The organization does not sell, rent, or commercially exploit customer data.

19.3 Data Usage Limitations

Customer data is processed only for legitimate operational purposes related to the delivery of platform services.

Permitted uses of data include:

* Platform functionality and analytics
* System monitoring and troubleshooting
* Service improvement and reliability

Data usage is governed by strict access control policies and internal security procedures.

Unauthorized access, sharing, or use of customer data is strictly prohibited.

19.4 Customer Data Access Rights

Customers maintain control over access to their data within We360.ai.

Authorized customer administrators can:

* Manage user access permissions
* Configure system integrations
* View and analyze operational data
* Export data where functionality permits

These controls allow organizations to manage data access in accordance with their internal governance policies.

19.5 Data Portability

Customers may request access to their data in order to export or transfer it for operational or compliance purposes.

Where technically feasible, data export capabilities may be provided through:

* Application interfaces
* System reports
* Data export mechanisms

Data portability supports customer flexibility and helps organizations maintain operational continuity.

19.6 Data Retention & Deletion Rights

Customers may request deletion of their data in accordance with contractual agreements and operational requirements.

Data deletion procedures may be initiated in the following circumstances:

* Customer request
* Contract termination
* Expiration of defined retention periods

Deletion processes ensure that customer data is securely removed from active systems and storage environments when no longer required.

19.7 Data Protection & Privacy Rights

We360.ai supports organizations in meeting their obligations under global privacy regulations such as:

* Digital Personal Data Protection Act
* General Data Protection Regulation
* California Consumer Privacy Act
* Health Insurance Portability and Accountability Act

Privacy protections include:

* Secure handling of personal data
* Controlled data access
* Data protection safeguards
* Transparent data processing practices

These controls help ensure that organizations using We360.ai can meet their regulatory and privacy obligations.

19.8 Customer Transparency

The organization is committed to transparency in data processing and privacy practices.

Customers may request information regarding:

* Data handling practices
* Security controls
* Compliance certifications
* Operational policies

This transparency supports enterprise due diligence and helps customers evaluate We360.ai’s security and compliance posture.

</details>

<details>

<summary>20. Audit, Reporting &#x26; Compliance Assurance</summary>

The organization maintains structured processes to ensure transparency, accountability and compliance with recognized security and privacy standards. These processes support internal governance, external audits and enterprise vendor due-diligence requirements.

Regular assessments, documentation and reporting mechanisms are maintained to ensure that operational, security and compliance controls are functioning effectively.

20.1 Internal Audits

Periodic internal audits are conducted to evaluate the effectiveness of security and operational controls across We360.ai.

Internal audits may review areas including:

* Access control management
* Infrastructure security
* Application security practices
* Incident management procedures
* Change management controls
* Data protection policies

Findings from internal audits are reviewed by relevant stakeholders and corrective actions are implemented where necessary.

20.2 External Audits & Independent Assessments

The organization may undergo independent third-party audits and security assessments to validate its compliance with industry standards.

External assessments may include:

* Security compliance audits
* Infrastructure security reviews
* Application security assessments
* Penetration testing exercises

Periodic Vulnerability Assessment and Penetration Testing helps identify potential vulnerabilities and ensures that We360.ai remains resilient against evolving threats.

20.3 Compliance Certifications

We360.ai aligns with globally recognized security and privacy standards.

Key certifications and frameworks include:

* SOC 2 Type II
* ISO/IEC 27001
* ISO/IEC 27017
* ISO/IEC 27018

These frameworks ensure that the organization maintains strong security governance, operational controls and privacy safeguards.

20.4 Regulatory Compliance Alignment

We360.ai is designed to support compliance with major global privacy and data protection regulations, including:

* Digital Personal Data Protection Act
* General Data Protection Regulation
* California Consumer Privacy Act
* Health Insurance Portability and Accountability Act

Operational policies and security controls help ensure that customer data is processed responsibly and in accordance with regulatory expectations.

0.5 Compliance Monitoring

Compliance monitoring mechanisms help ensure that controls remain effective and aligned with security standards.

Monitoring activities include:

* Periodic security reviews
* Policy compliance checks
* Infrastructure monitoring
* Security incident tracking
* Change management reviews

These processes ensure that security and compliance controls remain operational and up to date.

20.6 Audit Logging & Evidence Management

We360.ai maintains logs and documentation that support audit requirements and operational transparency.

Audit evidence may include:

* Access logs
* System activity logs
* Change management records
* Incident management reports
* Security assessment reports

These records support both internal governance and external compliance verification.

20.7 Customer Assurance & Transparency

Enterprise customers may require assurance regarding We360.ai’s security posture and compliance status.

Where applicable, customers may request information related to:

* Security policies and procedures
* Compliance certifications
* Security assessment reports
* Operational documentation

This transparency helps organizations conduct vendor risk assessments and verify security practices.

20.8 Continuous Compliance Improvement

Security and compliance programs are continuously improved through:

* Feedback from internal and external audits
* Security assessments and vulnerability testing
* Updates to regulatory requirements
* Improvements to operational controls

Continuous improvement ensures that We360.ai maintains a strong compliance posture as regulatory expectations and security threats evolve.

</details>


# Trust & Compliance

At We360.ai, we believe that world-class workforce analytics must be built on a foundation of absolute trust, security, and transparency. As the leading platform for employee productivity and workforce optimization, we have engineered our infrastructure from the ground up to protect your organization’s most sensitive data.

We balance powerful operational insights with uncompromising data protection, ensuring peace of mind for both leadership and employees. Here is an overview of the rigorous security measures, compliance standards, and architectural safeguards that make We360.ai a trusted partner for over 7,000 global companies.

***

### 1. Global Compliance & Certifications

We adhere to the most stringent international compliance standards to ensure your data is handled with the highest level of legal and regulatory integrity.

* SOC 2 Type II: We have successfully undergone rigorous auditing to demonstrate our ongoing commitment to the five trust service principles: security, availability, processing integrity, confidentiality, and privacy.
* HIPAA Compliant: For our partners in the healthcare sector, we maintain strict adherence to the Health Insurance Portability and Accountability Act, ensuring all health data privacy and security requirements are fully met.
* ISO 27001 Certified: Our information security management systems are certified against the premier international standard for data security, minimizing risk and maximizing proactive defense.
* GDPR Compliant: We ensure full compliance with European Union data protection regulations, protecting Personally Identifiable Information (PII) and guaranteeing your users' right to privacy.

### 2. Unbreakable Data Protection & Encryption

We utilize robust, industry-standard cryptographic protocols to ensure your information is indecipherable to unauthorized entities.

* Data at Rest: All stored data is secured using industry-standard AES-256 or equivalent encryption.
* Data in Transit: All communication between your devices and our servers is heavily protected using industry-standard TLS/SSL encryption.
* Strict Access Controls: Customer data is encrypted at rest with KMS-managed keys, and operational access to customer content is restricted to authorized personnel, protected by MFA, logged, and audited. For organizations requiring full custody of their data and keys, on-premise and Bring-Your-Own-Cloud deployments keep all monitoring data entirely within your own infrastructure.

### 3. Secure Software Development Life Cycle (SDLC)

Security is not an afterthought; it is woven directly into how we write, test, and deploy our code.

* End-to-End Secure SDLC: We maintain a strictly controlled and secure SDLC flow from initial design to final deployment.
* Continuous Scanning: Automated, regular code scanning is a mandatory part of our SDLC, preventing vulnerabilities from ever reaching production.
* Thorough Review Process: Every release undergoes rigorous peer and security reviews to guarantee structural integrity.
* Vulnerability Assessment and Penetration Testing (VAPT): We conduct multiple, aggressive rounds of penetration testing throughout the year, supplemented by comprehensive annual third-party pen testing to fortify our defenses against emerging threats.

### 4. Advanced Infrastructure & Network Security

Our platform operates on a multi-cloud fortress designed for maximum uptime, scalability, and threat prevention.

* Cloud-Native Scanning: Hosted on top-tier infrastructure, we leverage advanced Cloud-Native scanning (AWS) to automatically detect, assess, and mitigate infrastructure vulnerabilities in real-time.
* Cloudflare WAF: We route our traffic through a powerful Web Application Firewall (WAF) powered by Cloudflare, ensuring immediate protection against DDoS attacks, SQL injections, malicious bot traffic, and other zero-day exploits.
* Continuous Monitoring: Our enterprise data centers feature 24/7 continuous system auditing and monitoring to detect anomalies and respond to potential threats instantly.


# Compliance FAQs

This document addresses frequently asked questions about We360.ai's compliance posture, security controls, data handling practices, and regulatory alignment.

***

### 1. General Security & Compliance Posture

#### Q: What certifications and compliance standards does We360.ai hold?

We360.ai maintains the following certifications and compliance attestations:

| Certification / Standard | Status               | Details                                                                                                                                                                   |
| ------------------------ | -------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **ISO/IEC 27001:2022**   | Certified            | Information Security Management System (ISMS). Independently certified.                                                                                                   |
| **SOC 2 Type II**        | Attested             | Covers Security, Confidentiality, and Availability trust service criteria. Audit period: April–October 2024. Clean opinion issued. Recertification is conducted annually. |
| **SOC 2 Type I**         | Attested             | Precursor to Type II. Completed 2023.                                                                                                                                     |
| **GDPR**                 | Audited & Compliant  | Independent audit confirmed adequately designed controls across all GDPR requirements.                                                                                    |
| **HIPAA**                | Assessed & Compliant | Assessed against NIST SP 800-66 Rev 2. All Administrative, Physical, Technical, and Organizational safeguards found compliant.                                            |
| **VAPT**                 | Certified            | Annual Vulnerability Assessment & Penetration Testing. Application certified free from OWASP Top 10 and other known vulnerabilities.                                      |

#### Q: Does We360.ai undergo regular security testing?

Yes. We360.ai conducts:

* **Annual VAPT** — Web application penetration testing against OWASP Top 10 and other known vulnerability classes. Retesting is performed to confirm remediation of any findings.
* **Static Application Security Testing (SAST)** — Automated scanning of the codebase for known vulnerabilities in dependencies and libraries.
* **Periodic security audits** — Independent third-party assessments across ISO 27001, SOC 2, GDPR, and HIPAA frameworks.

#### Q: Does We360.ai have a formal Information Security Management System (ISMS)?

Yes. We360.ai operates a formal ISMS aligned with ISO/IEC 27001:2022. The ISMS encompasses:

* Documented security policies and procedures (32+ active policies)
* Defined information security roles and responsibilities (CISO, Privacy Officer, Information Security Group)
* Risk management procedures with regular risk assessments
* Internal audit and continual improvement processes
* Management review meetings for ISMS oversight

#### Q: Can We360.ai provide compliance documentation for our vendor assessment?

Yes. We360.ai can furnish the following upon request (subject to NDA where applicable):

* ISO 27001:2022 certificate and Statement of Applicability
* SOC 2 Type II report
* GDPR compliance audit report
* HIPAA assessment report
* VAPT certificate and web application security report
* Individual security policies (e.g., Access Control, Encryption, Incident Management)
* Architecture and data flow diagrams
* Completed security questionnaires (We360.ai has experience completing assessments for financial services, insurance, and enterprise clients)

#### Q: Can customers conduct their own penetration testing or security assessments?

Yes. We360.ai supports customer-initiated security assessments against their We360.ai environment, subject to the following process and rules of engagement.

**Requesting a Test:**

1. **Notification** — Customers must submit a formal testing request to **<security@we360.ai>** at least **14 business days** prior to the anticipated start date.
2. **Required details** — The request must include:
   * Proposed testing dates and duration
   * Originating IP addresses of all testers
   * List of automated tools that will be used
   * Contact information for the lead tester (name, email, phone)
3. **Approval** — Testing may only commence after receiving **written authorization** and a finalized scoping agreement from the We360.ai Information Security team. Unauthorized testing will be treated as a security incident.

**Rules of Engagement — Prohibited Activities:**

| Prohibited Activity                 | Description                                                                                                                                                                                                                                                       |
| ----------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **No Denial of Service (DoS/DDoS)** | Volumetric attacks, network stress testing, or any attempt to exhaust system resources (e.g., brute-forcing login portals at high velocity) are strictly prohibited.                                                                                              |
| **No Infrastructure Scanning**      | Network-level vulnerability scanning or exploitation targeting the underlying cloud infrastructure (e.g., Kubernetes nodes, AWS/GCP/Azure resources, managed databases) is not permitted. Testing must be limited to the **We360.ai application layer**.          |
| **No Cross-Tenant Attacks**         | Any active attempt to access, view, or modify data belonging to other We360.ai customers is prohibited. Testing for horizontal privilege escalation is permitted, but testers **must immediately halt and report** if they successfully access cross-tenant data. |

**Reporting:** Upon completion, testers are expected to share a summary of findings with the We360.ai Information Security team at <security@we360.ai>. We360.ai commits to acknowledging findings within 48 hours and providing a remediation timeline based on severity.

#### Q: Does We360.ai have a vulnerability disclosure or bug bounty program?

We360.ai maintains a responsible vulnerability disclosure policy. Security researchers and customers who discover potential vulnerabilities are encouraged to report them to <security@we360.ai>. Reports are triaged promptly, and We360.ai commits to acknowledging receipt within 48 hours and providing a remediation timeline based on severity.

***

### 2. Data Privacy — GDPR, DPDP Act & CCPA

#### Q: Is We360.ai GDPR compliant?

Yes. We360.ai has undergone an independent GDPR compliance audit and has been found to have adequately designed controls to meet GDPR requirements in all material respects. Key GDPR measures include:

* **Lawful basis for processing** — Processing is carried out under a valid legal basis (contract performance, legitimate interest, or consent as applicable).
* **Data Processing Addendum (DPA)** — Available for all customers subject to GDPR, incorporating Standard Contractual Clauses (Commission Decision 2021/914) for international data transfers.
* **EU Representative** — A GDPR Representative has been formally appointed in the EU to serve as a point of contact for data protection authorities and data subjects.
* **Data subject rights** — Full support for access, rectification, erasure, portability, restriction of processing, objection, and withdrawal of consent. Requests are addressed within one month under GDPR, and as soon as reasonably practicable under other applicable regulations.
* **Data Protection Officer (DPO)** — Reachable at <dpo@we360.ai>.
* **Data minimization** — Only data necessary for the specified purpose is collected and retained.
* **Privacy by design** — Built-in privacy controls including screenshot blurring, configurable tracking scope, and shift-based monitoring.
* **Processor breach notification SLA** — As a Data Processor, We360.ai commits to notifying the customer (the Data Controller) of any confirmed personal data breach **within 24 hours** of becoming aware of the breach. This gives the Controller sufficient time to assess the incident and fulfill its own regulatory obligation to notify the supervisory authority within 72 hours under GDPR Article 33. The notification includes the nature of the breach, categories and approximate number of data subjects affected, likely consequences, and measures taken or proposed to address the breach. See Section 8 for full incident management details.

#### Q: How does We360.ai comply with India's Digital Personal Data Protection (DPDP) Act 2023?

We360.ai aligns with the DPDP Act 2023, including:

* Clear purpose limitation and consent mechanisms for personal data processing
* Provision for data principal rights (access, correction, erasure)
* Designated Grievance Officer for data protection queries
* Data stored in India, supporting data localization requirements
* Documented retention and deletion policies to ensure data is not retained beyond its lawful purpose

#### Q: Does We360.ai support CCPA requirements?

Yes. We360.ai supports CCPA requirements through:

* Transparency about data collection and usage practices via the Privacy Policy
* Mechanisms for consumers to request access to, deletion of, and information about their personal data
* We360.ai does not sell personal data to third parties

#### Q: What is We360.ai's data retention policy?

Data retention is governed by the Data and Record Retention and Deletion Policy. Key retention periods:

| Data Category             | Retention Period                       |
| ------------------------- | -------------------------------------- |
| Client/customer data      | Duration of contract + 3 months        |
| End-user monitoring data  | 1 year post-termination of services    |
| Database backups          | 1 month (rolling)                      |
| Trial account data        | Deleted within 1 month of trial expiry |
| Financial/billing records | 7+ years (statutory requirement)       |

Upon expiry of the retention period, data is securely deleted or irreversibly anonymized. Customers may also request data deletion at any time, subject to contractual and legal obligations.

#### Q: Does We360.ai sell or share personal data with third parties?

No. We360.ai does not sell, rent, or commercially exploit customer or end-user data. Data is shared with third-party subprocessors only as necessary for service delivery (e.g., cloud hosting, payment processing), under strict confidentiality obligations and data processing agreements.

***

### 3. HIPAA

#### Q: Is We360.ai HIPAA compliant?

Yes. We360.ai has been assessed against NIST SP 800-66 Rev 2 and found compliant across all HIPAA safeguard categories:

* **Administrative Safeguards** — Security management process, workforce security, information access management, security awareness and training, security incident procedures, contingency planning, evaluation
* **Physical Safeguards** — Facility access controls, workstation use and security, device and media controls
* **Technical Safeguards** — Access controls, audit controls, integrity controls, person or entity authentication, transmission security
* **Organizational Requirements** — Business associate contracts, policies and procedures
* **Documentation Requirements** — Required documentation and record retention

#### Q: Does We360.ai offer a Business Associate Agreement (BAA)?

Yes. We360.ai offers a Business Associate Agreement for customers whose use of the platform may result in incidental exposure to Protected Health Information (PHI).

> **Important clarification:** We360.ai is a workforce analytics platform — it is **not** designed to purposefully collect, store, or process PHI. However, in certain environments (e.g., monitoring a telehealth worker's screen, or employees who handle electronic health records), screenshots or screen recordings may incidentally capture PHI visible on-screen. The BAA exists to provide contractual coverage for this **incidental exposure**, not to authorize We360.ai as a system for purposeful PHI processing.

#### Q: How does We360.ai minimize incidental PHI capture?

We360.ai is designed to minimize the risk of incidental PHI exposure through the following controls:

* **Screenshot Blur Engine** — Automatically masks and blurs sensitive on-screen content in captured screenshots, including text fields, personal communications, financial data, and authentication fields. For healthcare environments, the Blur Engine significantly reduces the risk of readable PHI appearing in screenshots.
* **Screenshot frequency control** — Administrators can reduce screenshot frequency or disable screenshots entirely for users who regularly handle PHI.
* **Screen recording toggle** — Screen recording is off by default and must be explicitly enabled. Organizations monitoring healthcare workers should carefully evaluate whether screen recording is necessary and proportionate.
* **Shift-based tracking** — Limits monitoring to designated work hours, reducing the window of potential PHI exposure.
* **Do Not Track list** — Employees who routinely handle high volumes of PHI (e.g., clinical staff) can be excluded from screenshot and screen recording capture entirely while still being tracked for time and attendance.
* **Data retention controls** — Screenshots that may contain incidental PHI are subject to the organization's configured retention period and are automatically deleted upon expiry.

> **Recommendation:** Organizations in healthcare or telehealth should enable the Blur Engine, minimize screenshot frequency for clinical staff, and conduct a risk assessment to determine the appropriate monitoring scope for employees who handle PHI. The BAA should be executed before deployment in any environment where incidental PHI exposure is possible.

#### Q: How does We360.ai protect Protected Health Information (PHI)?

We360.ai implements multiple layers of protection for any PHI that may be incidentally captured:

* **HIPAA Internal Privacy Policy** — Governs the use, disclosure, and protection of PHI, enforcing minimum necessary standards.
* **PHI De-identification Policy** — Documented procedures for anonymizing health data when de-identified data is sufficient for the intended purpose.
* **Guidelines on Use and Disclosure of PHI** — Operational guidelines covering permissible uses and disclosures, individual rights (access, amendment, accounting of disclosures), and administrative/physical/technical safeguards.
* **Encryption** — PHI is encrypted both in transit (TLS) and at rest (industry-standard encryption algorithms).
* **Access controls** — Role-based access with least-privilege principles; MFA for privileged access.
* **Breach notification** — Documented HIPAA Breach Notification Policy aligned with regulatory timelines.

***

### 4. Data Collection & What Is NOT Collected

#### Q: What data does the We360.ai agent collect?

The We360.ai agent captures workforce productivity data at per-second granularity. The data collected includes:

**Device Metadata:**

* Computer name and timezone
* Operating system and domain information
* Network identifier (hashed), private and public IP addresses

**User Activity Data:**

* Active application names and window titles
* URLs visited in browsers
* Duration of activity per application/URL
* Mouse click and keystroke frequency counts (aggregate counts only)
* Screenshots of the active window (at a configurable frequency)
* Screen recordings (if enabled by the organization)

**Attendance & Location Data:**

* Login/logout timestamps, break patterns
* GPS coordinates from the mobile app (for field workforce tracking, if enabled)

All data collection is configurable by the organization's administrators, allowing fine-grained control over what is captured.

#### Q: What does We360.ai NOT collect?

> **⚠️ IMPORTANT — Definitive Data Collection Boundaries**
>
> The following restrictions are absolute, apply to all deployment modes (Standard and Stealth), all platforms (Windows, macOS, Linux, mobile), and all hosting models (cloud, on-premise, BYOC). They are enforced by design and cannot be overridden by configuration. All other sections of this document that reference these boundaries defer to this section as the authoritative source.

We360.ai explicitly does **NOT** collect — and is **architecturally incapable** of collecting — the following:

* **❌ Individual keystrokes (No Keylogging)** — Only aggregate keystroke frequency counts are captured (e.g., keystrokes per minute as an activity indicator). **Actual key presses, typed text, passwords, form inputs, chat messages, or any content entered by the user are never recorded, transmitted, or stored.** The We360.ai agent does not contain a keylogger and has no mechanism to capture individual keystrokes.
* **❌ Webcam or camera feeds** — The platform **never** accesses device cameras or captures any video of the user. No webcam permissions are requested or used.
* **❌ Audio or microphone data** — **No audio recording is performed**, ever. The platform does not access or request microphone permissions.
* **❌ Personal file contents** — File contents on the user's device are not accessed, read, or transmitted. The agent tracks application and window metadata only.

#### Q: Can organizations control what data is collected?

Yes. We360.ai provides extensive configurability:

* **Screenshot frequency** — Adjustable from 2 per hour to 60 per hour, or disabled entirely.
* **Screenshot blurring (Blur Engine)** — Automatic blurring/masking of sensitive on-screen content to prevent exposure of personal communications, financial details, or authentication fields.
* **URL and app tracking** — Can be scoped or restricted via productivity rules and URL blocklists.
* **Shift-based tracking** — Monitoring can be restricted to designated work hours and authorized environments only.
* **Screen recording** — Optional; must be explicitly enabled.
* **Field/GPS tracking** — Optional; applies only to the mobile app and must be enabled.

#### Q: Can employees see their own data?

Yes. In Standard mode, employees have access to their own productivity analytics, enabling self-assessment and improvement. This supports transparency and aligns with data protection principles around data subject access.

***

### 5. Encryption & Data Protection

#### Q: How is data encrypted in transit?

All data transmitted between the We360.ai agent and backend infrastructure is encrypted using:

* **HTTPS/TLS** — All REST API communication uses TLS encryption over TCP port 443.
* **WSS (WebSocket Secure)** — Real-time data streaming uses encrypted WebSocket connections.
* **No unencrypted channels** — The platform does not transmit data over HTTP or any unencrypted protocol.

#### Q: How is data encrypted at rest?

Data at rest is protected using industry-standard encryption:

* **Database encryption** — All databases (PostgreSQL, ClickHouse) use encryption at rest with platform-managed keys.
* **Object storage encryption** — Screenshots, recordings, and backups stored in cloud object storage are encrypted.
* **Encryption standards** — AES-256 encryption for data at rest, with symmetric keys of at least 128 bits and asymmetric keys of at least 2048 bits.
* **Key management** — Encryption keys are managed through the cloud provider's key management services, with access restricted to authorized personnel.

#### Q: How is data handled when the agent is offline?

We360.ai uses an offline-first architecture:

* Activity data is stored locally on the user's device in an encrypted local database when connectivity is unavailable.
* Data is automatically synced to the server over encrypted HTTPS once connectivity is restored.
* Local data is cleared after the server confirms receipt.
* This ensures continuous, uninterrupted tracking regardless of internet stability.

***

### 6. Infrastructure, Hosting & Data Residency

#### Q: Where is We360.ai data hosted?

We360.ai uses an isolated cell-based architecture. Each cell is a fully independent deployment — with its own compute, database, and storage layers — ensuring complete data isolation between regions. Currently available cells:

| Cell              | Region                                                                                                                         |
| ----------------- | ------------------------------------------------------------------------------------------------------------------------------ |
| **India**         | Default cell for all customers. Data is stored and processed entirely within India, supporting data localization requirements. |
| **United States** | Isolated US cell for customers requiring data residency within the United States.                                              |

Additional cells can be provisioned in other regions based on customer requirements.

#### Q: Does We360.ai support data residency requirements?

Yes. For cloud-hosted deployments, data is stored in India by default. For organizations with specific data residency or sovereignty requirements (e.g., EU, Middle East, or other jurisdictions), We360.ai offers:

* **We360.ai Managed Cloud** — We360.ai hosts and manages the platform in a region of the customer's choice, removing the operational burden while meeting data residency requirements.
* **On-premise deployment** — The entire platform can be deployed within the customer's own infrastructure, ensuring complete control over data location.
* **Bring-Your-Own-Cloud (BYOC)** — Customers can host the platform on their own cloud tenancy in any region of their choice.

#### Q: What cloud infrastructure does We360.ai use?

We360.ai is deployed on enterprise-grade cloud infrastructure leveraging services including:

* Managed Kubernetes clusters distributed across multiple availability zones for high availability
* Managed relational databases (PostgreSQL) with encryption at rest
* Columnar databases for analytics workloads
* Encrypted object storage for screenshots and backups
* Cloud-native identity and access management
* Network segmentation with private subnets and firewall rules

The underlying cloud providers maintain their own extensive compliance certifications, including ISO 27001, ISO 27017, ISO 27018, SOC 1/2/3, PCI DSS, and CSA STAR.

#### Q: Is the infrastructure multi-tenant or single-tenant?

The We360.ai managed cloud is multi-tenant at the infrastructure layer, with tenant boundaries enforced independently across every persistence and access layer:

* **Filesystem** — Tenant-scoped folders isolate files on shared filesystems.
* **S3 object storage** — Each tenant uses a distinct object-key prefix ("virtual folder") for screenshots, screen recordings, and other objects. Prefix-level authorization prevents cross-tenant object access.
* **Databases** — Tenant data is partitioned into dedicated schemas or logical databases, selected by datastore and workload.
* **Encryption** — Each tenant uses a tenant-specific data encryption key (DEK), providing cryptographic separation between tenants' ciphertext.
* **Access control** — Role-based access control (RBAC) and tenant-aware authorization enforce the same boundary across APIs and services.

We also support Bring Your Own Bucket (BYOB) for screenshot and screen-recording data, allowing those objects to reside in a customer-controlled bucket. Customers requiring end-to-end physical isolation can use on-premise or Bring-Your-Own-Cloud (BYOC) deployment options, which provide dedicated single-tenant environments.

***

### 7. Access Controls & Authentication

#### Q: How does We360.ai control access to customer data?

We360.ai implements a comprehensive access control framework based on the principle of least privilege:

* **Role-Based Access Control (RBAC)** — Users are assigned permissions based on their organizational role. Administrators can define granular access levels.
* **Least privilege** — Users and system accounts are granted only the minimum access necessary to perform their responsibilities.
* **Multi-Factor Authentication (MFA)** — Enforced for all privileged and administrative access, including cloud infrastructure management.
* **Single Sign-On (SSO)** — Supported for enterprise customers, integrating with existing identity providers.
* **SCIM Provisioning** — Custom SCIM (System for Cross-domain Identity Management) integration is available for enterprise customers. SCIM enables automated user provisioning and deprovisioning synchronized with the customer's identity provider (e.g., Azure AD, Okta, OneLogin), ensuring that user accounts in We360.ai are created, updated, and removed in lockstep with the organization's directory. This reduces manual administration overhead and eliminates the risk of orphaned accounts retaining access after employee offboarding. Contact We360.ai to scope a SCIM integration for your environment.
* **Inactive account deactivation** — Accounts with no login activity for 30 days are automatically deactivated (can be reactivated upon request).
* **Dormant account removal** — Accounts that remain deactivated and unused for 90 days are reviewed and permanently removed.
* **Quarterly access reviews** — Periodic reviews ensure access permissions remain appropriate.
* **Immediate revocation on termination** — Access is revoked immediately upon employee separation.

#### Q: What password policies does We360.ai enforce?

We360.ai enforces strong password management practices as documented in the Password Management Policy, including minimum complexity requirements, prohibition of password reuse, and event-driven password changes (e.g., upon suspected compromise) aligned with current NIST SP 800-63B guidance. MFA is required for privileged access as an additional layer of protection.

#### Q: How is administrative access to infrastructure managed?

Administrative access to cloud infrastructure and production systems is:

* Restricted to authorized personnel only
* Protected by MFA
* Logged and auditable (all access activity is tracked)
* Subject to periodic access reviews
* Segregated by environment (development, staging, production)

#### Q: Are customer administrator actions logged and auditable?

Yes. All administrative actions performed within the We360.ai platform — including configuration changes, user management, access to employee data, modifications to Do Not Track lists, and policy changes — are logged in an immutable audit trail. These logs include the administrator identity, timestamp, action performed, and affected resources. Audit logs are available to customer administrators and can be exported for compliance and internal review purposes.

***

### 8. Incident Management & Breach Notification

#### Q: Does We360.ai have a formal incident management process?

Yes. We360.ai maintains a documented Incident Management Policy that defines:

* **Incident classification** — Incidents are categorized by severity (Low, Moderate, High) and type (intrusion, malicious code, denial of service, unauthorized use, data breach, web defacement).
* **Incident Response Team (IRT)** — A structured team with an executive sponsor responsible for coordinating response efforts.
* **Response procedures** — Defined processes for detection, containment, eradication, recovery, and lessons learned.
* **Root Cause & Corrective Action (RCCA)** — Post-incident analysis to identify root causes and implement corrective actions.
* **Security awareness training** — Annual training for all personnel on security incident identification and reporting.

#### Q: How does We360.ai handle data breaches?

In the event of a data breach:

* **Immediate containment** — The Incident Response Team takes prompt corrective action to contain the breach.
* **Assessment** — The nature, scope, and impact of the breach are assessed.
* **Notification to the customer (Controller)** — As a Data Processor, We360.ai commits to notifying the affected customer (the Data Controller) **within 24 hours** of becoming aware of a confirmed personal data breach. This notification includes:

  * Nature and scope of the breach
  * Categories and approximate number of data subjects and records affected
  * Likely consequences of the breach
  * Measures taken or proposed by We360.ai to contain and remediate the breach
  * Contact details of We360.ai's Data Protection Officer for ongoing coordination

  This 24-hour processor-to-controller SLA is designed to give the Controller sufficient time to fulfill its own downstream regulatory obligations:

  * **GDPR (Article 33)** — The Controller must notify the relevant supervisory authority within 72 hours of becoming aware of a breach. By notifying within 24 hours, We360.ai ensures the Controller retains at least 48 hours to assess the incident, determine reportability, and file its notification. Where the breach is likely to result in a high risk to the rights and freedoms of individuals, the Controller must also notify affected data subjects without undue delay (Article 34).
  * **HIPAA** — Notification in accordance with the HIPAA Breach Notification Rule timelines.
  * **DPDP Act** — Notification to the Data Protection Board and affected data principals as required under the Act.
* **Remediation** — Corrective actions are implemented and documented.
* **Post-incident review** — Lessons learned are incorporated into policies and controls.

#### Q: Does We360.ai maintain an incident register?

Yes. All security incidents are logged in an incident register with relevant details including classification, timeline, response actions, and resolution. This register supports audit requirements and continual improvement of the incident management process.

***

### 9. Vendor & Subprocessor Management

#### Q: How does We360.ai manage third-party vendors and subprocessors?

We360.ai maintains a formal Vendor Management Policy that governs the selection, assessment, and ongoing oversight of all third-party vendors and subprocessors:

* **Due diligence** — All vendors undergo a security and compliance assessment before engagement, including evaluation of their own certifications, security controls, and data handling practices.
* **Contractual safeguards** — Non-Disclosure Agreements (NDAs), Data Processing Agreements, and SLAs are required for all vendors handling customer data.
* **Critical vendor classification** — Vendors are classified by criticality, with enhanced oversight for those processing sensitive data or providing critical services.
* **Periodic reviews** — Vendor access and compliance status are reviewed periodically.
* **Vendor auditing** — We360.ai reserves the right to audit vendor compliance with contractual and security obligations.
* **Cloud-specific controls** — For cloud service providers, additional controls are enforced including data localization verification, encryption validation, and multi-tenant segregation assurance.

#### Q: Does We360.ai share data with subprocessors?

Data is shared with subprocessors only as necessary for service delivery (e.g., cloud hosting, payment processing, email delivery). All subprocessors are bound by confidentiality obligations and data processing agreements. A list of subprocessors can be provided upon request as part of the Data Processing Addendum.

We360.ai does not sell, rent, or commercially exploit customer data.

***

### 10. Business Continuity & Disaster Recovery

#### Q: Does We360.ai have a Business Continuity Plan (BCP)?

Yes. We360.ai maintains a comprehensive Business Continuity and Disaster Recovery (BC/DR) Policy based on Business Impact Analysis (BIA). The plan defines:

* **Maximum Acceptable Outage (MAO)** — The maximum tolerable period of disruption.
* **Recovery Time Objective (RTO)** — Target time to restore services after a disruption. Standard baseline RTO is 4 hours, though custom SLAs are available for enterprise customers. Detailed RTO targets per service tier are available upon request under NDA.
* **Recovery Point Objective (RPO)** — Maximum acceptable data loss measured in time. Standard baseline RPO is 24 hours, though custom SLAs are available for enterprise customers. Detailed RPO targets per data category are available upon request under NDA.
* **Work-from-home provisions** — Security guidelines for maintaining operations during office disruptions.

#### Q: How often is the BC/DR plan tested?

The BC/DR plan is tested regularly through multiple exercise types:

* **Tabletop exercises** — Walkthrough of disaster scenarios with the response team.
* **Simulated exercises** — Live simulation of failure scenarios.
* **Partial and complete recovery tests** — Actual failover and recovery exercises.

Testing covers scenarios including single-node failure (automatic self-healing via Kubernetes), availability zone failure (multi-AZ failover), full database/cluster failure (backup restoration), and regional failure (infrastructure recreation from code plus backup restoration).

#### Q: How are backups managed?

* **Frequency** — Daily automated database backups.
* **Retention** — Backups retained for 1 month on a rolling basis.
* **Encryption** — Backups are encrypted at rest.
* **Testing** — Backup restoration is tested as part of DR exercises.
* **Infrastructure as Code** — Infrastructure is defined in code, enabling rapid recreation of the entire environment from scratch if needed.

***

### 11. Stealth vs Standard Mode — Ethical Monitoring

#### Q: What is the difference between Stealth and Standard mode?

We360.ai offers two deployment modes, both delivering identical tracking capabilities:

| Aspect                    | Standard Mode                                                                            | Stealth Mode                                                             |
| ------------------------- | ---------------------------------------------------------------------------------------- | ------------------------------------------------------------------------ |
| **Visibility**            | Visible to the employee — system tray icon and desktop application                       | Runs silently in the background — no visible UI                          |
| **User interaction**      | Employees can punch in/out, pause tracking, view their own analytics                     | No user interaction; tracking is automatic based on configured shifts    |
| **Use case**              | Transparent monitoring environments where employee awareness and self-service are valued | Discreet monitoring where automated, policy-driven tracking is preferred |
| **Admin rights**          | Not required for installation                                                            | Required for installation                                                |
| **Tracking capabilities** | Full feature set                                                                         | Identical full feature set                                               |
| **Security & encryption** | Same standards                                                                           | Same standards                                                           |

**Both modes provide:**

* Per-second activity granularity
* App and URL tracking
* Aggregate input activity (mouse/keyboard counts only — see Section 4 for definitive data collection boundaries)
* Screenshots and screen recording (if configured)
* Offline-first data sync
* Encrypted data transmission and storage

#### Q: Is stealth monitoring ethical and legal?

We360.ai recommends that organizations deploying in Stealth mode:

* Comply with all applicable local, regional, and national laws governing employee monitoring and workplace privacy.
* Inform employees through workplace policies, employment agreements, or privacy notices as required by applicable law.
* Use monitoring data for legitimate business purposes (productivity optimization, security, compliance) — not for punitive surveillance.

We360.ai's platform is designed to support ethical, proportionate, and policy-driven monitoring regardless of the deployment mode selected.

#### Q: Does We360.ai support monitoring only during work hours?

Yes. Shift-based tracking allows organizations to restrict monitoring to designated work hours and authorized environments. Outside of configured shifts, the agent does not capture activity data. This aligns with privacy principles of data minimization and purpose limitation.

***

### 12. On-Premise & BYOC Deployment

#### Q: Can We360.ai be deployed on our own infrastructure?

Yes. We360.ai offers two self-hosted deployment models:

**VM-Based Deployment (recommended for up to 2,000 users):**

* Single Linux VM running containerized services
* Customer-managed database and object storage
* Suitable for organizations seeking simplicity with full data control

**Kubernetes Deployment (recommended for 1,000+ users):**

* Kubernetes cluster with multiple worker nodes
* Horizontally scalable for large enterprises
* High-availability configuration with multi-node redundancy

Both options ensure that all data — including activity logs, screenshots, recordings, and backups — remains entirely within the customer's own infrastructure or cloud tenancy.

#### Q: What are the infrastructure requirements for on-premise deployment?

**VM-Based:**

* Linux (Ubuntu Server LTS)
* 16 CPU cores, 64 GB RAM, 512 GB SSD (resizable)
* External S3-compatible object storage for screenshots and backups
* PostgreSQL and ClickHouse databases (managed or self-hosted)

**Kubernetes-Based:**

* Kubernetes v1.30+ cluster with 3–6 worker nodes
* 8 cores / 32 GB RAM per worker node
* CSI storage provisioner with 100+ GB SSD
* Separate PostgreSQL and ClickHouse instances

**Additional requirements:**

* SMTP server access for email functionality (TLS/STARTTLS/SSL supported)
* Outbound internet access for license validation only (no customer data is transmitted)

#### Q: Does the on-premise deployment send any data back to We360.ai?

The on-premise deployment requires outbound connectivity to We360.ai's licensing server for tenant configuration and license validation only. **No customer data, employee activity data, screenshots, or any monitoring data is transmitted to We360.ai's infrastructure.** All collected data remains entirely within the customer's environment.

#### Q: Does the same data isolation apply to Bring-Your-Own-Cloud (BYOC) deployments?

Yes. **The BYOC deployment model has the exact same data isolation guarantees as on-premise.** In a BYOC deployment, the entire We360.ai platform runs within the customer's own cloud tenancy (e.g., their own AWS, Azure, or GCP account). Specifically:

* **All customer data stays in the customer's cloud tenancy** — Activity logs, screenshots, screen recordings, database contents, backups, and all other monitoring data are stored and processed entirely within the customer's cloud account. No customer data is transmitted to We360.ai's infrastructure.
* **Outbound connectivity is limited to license validation only** — Identical to on-premise, the only outbound connection to We360.ai is for tenant configuration and license validation. This connection transmits no customer data, employee activity data, or monitoring data of any kind.
* **Customer controls the infrastructure** — The customer owns and manages the cloud account, network configuration, encryption keys, and access policies. We360.ai does not have standing access to the customer's cloud tenancy unless explicitly granted for support purposes.
* **Region and jurisdiction control** — The customer selects the cloud region, ensuring full control over data residency and sovereignty.

> **In summary:** Whether deployed on-premise or via BYOC, We360.ai operates under the same strict principle: **all monitoring data remains within the customer's environment; only license validation traffic is exchanged with We360.ai.**

#### Q: What platforms does the We360.ai agent support?

| Platform             | Support                                                                                                                      |
| -------------------- | ---------------------------------------------------------------------------------------------------------------------------- |
| **Windows**          | Windows 10 and later (x86-64)                                                                                                |
| **macOS**            | macOS 13 (Ventura) and later — Intel and Apple Silicon                                                                       |
| **Linux**            | Ubuntu and Ubuntu-based distributions (e.g., Linux Mint, Pop!\_OS). On-premise server deployment requires Ubuntu Server LTS. |
| **iOS**              | Available on the Apple App Store                                                                                             |
| **Android**          | Available on the Google Play Store                                                                                           |
| **Chrome**           | Browser extension for enhanced web activity tracking                                                                         |
| **Virtual Desktops** | Full support for Citrix, RDP, and VDI environments                                                                           |

***

### 13. Is Employee Monitoring Legal?

> **Disclaimer:** This section is for informational purposes only and does not constitute legal advice. Organizations should consult qualified legal counsel for jurisdiction-specific guidance on employee monitoring requirements.

#### Q: Is employee monitoring legal?

Yes. Employee monitoring is legal in most jurisdictions worldwide, provided it is conducted in compliance with applicable laws regarding notice, consent, proportionality, and data protection. The legality depends on the jurisdiction, the type of monitoring, and the safeguards in place.

We360.ai is designed to help organizations monitor workforce activity lawfully by providing configurable controls, transparency features, and compliance-aligned defaults.

#### Q: What are the legal requirements for employee monitoring in India?

India does not have a single unified employee monitoring statute, but several laws and frameworks govern the practice:

* **Information Technology Act, 2000 (IT Act)** — Section 43A requires bodies corporate that possess, deal with, or handle sensitive personal data to implement reasonable security practices. The IT (Reasonable Security Practices and Procedures and Sensitive Personal Data or Information) Rules, 2011 require that organizations collecting personal information provide a privacy policy, obtain consent, and use data only for the stated purpose.
* **Digital Personal Data Protection (DPDP) Act, 2023** — Establishes consent-based processing, purpose limitation, data minimization, and data principal rights (access, correction, erasure). Employers must have a valid legal basis for processing employee data and must provide clear notice about what data is collected and why.
* **State-specific Shops & Establishments Acts** — Various Indian states have legislation governing working conditions, record-keeping, and employee rights that may impact monitoring practices.
* **Employment agreements and standing orders** — Organizations should include monitoring disclosures in employment contracts, offer letters, or company policies to ensure employees are informed.

**We360.ai's approach**: The platform supports configurable consent mechanisms, purpose limitation through shift-based tracking, data minimization controls, and full data subject rights — aligning with the DPDP Act and IT Act requirements.

#### Q: What are the key employee monitoring laws in the United States?

Employee monitoring in the US is governed by a combination of federal and state laws:

**Federal Laws:**

| Law                                              | Relevance                                                                                                                                           |
| ------------------------------------------------ | --------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Electronic Communications Privacy Act (ECPA)** | Permits employer monitoring of electronic communications on company-owned systems, particularly when employees are notified or consent is provided. |
| **Computer Fraud and Abuse Act (CFAA)**          | Prohibits unauthorized access to computer systems; relevant when monitoring extends to non-company devices.                                         |
| **National Labor Relations Act (NLRA)**          | Section 7 protects employees' rights to organize; monitoring must not be used to surveil or suppress protected concerted activity.                  |
| **Americans with Disabilities Act (ADA)**        | Monitoring data related to disability or medical conditions must be kept confidential and handled appropriately.                                    |
| **Fair Labor Standards Act (FLSA)**              | Employers must maintain accurate records of hours worked; time-tracking tools support FLSA compliance.                                              |

**State-Specific Requirements:**

Several US states have enacted specific employee monitoring notification or consent requirements:

| State           | Key Requirement                                                                                                                                  |
| --------------- | ------------------------------------------------------------------------------------------------------------------------------------------------ |
| **Connecticut** | Written notice to employees prior to electronic monitoring (Public Act 98-142).                                                                  |
| **Delaware**    | Written notice required before monitoring email, internet access, or telephone use (Delaware Code Title 19, §705).                               |
| **New York**    | Written notice and conspicuous posting required when monitoring telephone, email, or internet usage (Civil Rights Law §52-c).                    |
| **California**  | CCPA/CPRA grants employees data access, correction, deletion, and opt-out rights. General privacy protections under the California Constitution. |
| **Texas**       | CUBI Act regulates collection of biometric identifiers.                                                                                          |
| **Illinois**    | Biometric Information Privacy Act (BIPA) requires informed written consent before collecting biometric data.                                     |

#### Q: What are the key employee monitoring requirements under EU/UK law?

Under the **General Data Protection Regulation (GDPR)** and **UK GDPR**, employee monitoring must comply with the following principles:

* **Lawfulness, fairness, and transparency** — A valid legal basis is required (typically legitimate interest or contractual necessity; consent is generally not considered freely given in an employment context due to the power imbalance).
* **Purpose limitation** — Monitoring must be conducted for specified, explicit, and legitimate purposes.
* **Data minimization** — Only data that is adequate, relevant, and limited to the stated purpose should be collected.
* **Storage limitation** — Data must not be retained longer than necessary.
* **Data Protection Impact Assessment (DPIA)** — Required when monitoring is likely to result in a high risk to employee rights and freedoms (see Section 17).
* **Employee notification** — Employees must be informed about the monitoring, its purpose, and their rights before monitoring begins.
* **Data subject rights** — Right to access, rectification, erasure, portability, restriction, and objection must be supported.

National laws within EU member states may impose additional requirements (e.g., works council consultation in Germany, CNIL guidelines in France).

#### Q: How does We360.ai help organizations comply with monitoring laws?

We360.ai provides built-in features that support legal compliance across jurisdictions:

* **Configurable tracking scope** — Administrators can enable or disable specific data collection features to match local legal requirements.
* **Shift-based tracking** — Restricts monitoring to designated work hours, preventing off-duty surveillance.
* **Do Not Track list** — Excludes specific users from monitoring entirely (see Section 14).
* **Screenshot blurring (Blur Engine)** — Masks sensitive on-screen content to prevent inadvertent capture of personal data.
* **Standard mode with employee visibility** — Provides full transparency to employees about what is being tracked.
* **Data subject rights support** — Built-in mechanisms for data access, export, correction, and deletion requests.
* **Data Processing Addendum (DPA)** — Available with Standard Contractual Clauses for international data transfers.
* **Retention controls** — Configurable data retention aligned with applicable legal requirements.

> **Note:** We360.ai provides technology and tools to support compliance. It is the deploying organization's responsibility to ensure that its use of the platform complies with all applicable laws, including obtaining any required notice, consent, or works council approval.

***

### 14. Privacy Controls & Do Not Track

#### Q: Does We360.ai support a Do Not Track (DNT) list?

Yes. We360.ai provides a Do Not Track (DNT) feature that allows administrators to exclude specific employees or user accounts from all monitoring and data collection. Users placed on the DNT list:

* Are not tracked by the We360.ai agent
* Have no activity data, screenshots, or recordings collected
* Do not appear in productivity reports or analytics dashboards

This is useful for exempting executives, HR personnel, legal teams, works council members, or any employees who should not be monitored due to legal, contractual, or policy reasons.

#### Q: What privacy controls does We360.ai provide?

We360.ai offers a layered set of privacy controls to help organizations implement proportionate and ethical monitoring:

| Privacy Control                           | Description                                                                                                                                   |
| ----------------------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------- |
| **Do Not Track (DNT) list**               | Completely exclude specific users from all monitoring.                                                                                        |
| **Shift-based tracking**                  | Restrict monitoring to designated work hours only. No data is captured outside configured shifts.                                             |
| **Screenshot blurring (Blur Engine)**     | Automatically mask/blur sensitive on-screen content (personal communications, financial data, authentication fields) in captured screenshots. |
| **Screenshot frequency control**          | Adjustable from 2 to 60 per hour, or disabled entirely.                                                                                       |
| **Screen recording toggle**               | Screen recording is off by default and must be explicitly enabled.                                                                            |
| **URL/app scope control**                 | Configure which applications and websites are tracked via productivity rules and blocklists.                                                  |
| **GPS tracking opt-in**                   | Field/GPS tracking applies only to the mobile app and must be explicitly enabled.                                                             |
| **Employee self-service (Standard mode)** | Employees can view their own data, providing transparency into what is tracked.                                                               |

#### Q: Can employees request to be excluded from monitoring?

Depending on the organization's policies and applicable local laws, employees may have the right to request exclusion from monitoring. We360.ai's Do Not Track list provides the technical mechanism to implement such exclusions. The decision to honor exclusion requests is made by the deploying organization in accordance with its HR policies, legal obligations, and collective agreements.

Under GDPR, employees have the right to object to processing based on legitimate interest; the organization must then assess whether its grounds override the employee's objection.

#### Q: Are privacy controls enabled by default?

We360.ai is designed with privacy-conscious defaults:

* Screenshot blurring (Blur Engine) is available and configurable from the outset.
* Screen recording is **off by default** — it must be explicitly enabled by an administrator.
* GPS/location tracking is **off by default** — it applies only to the mobile app and requires explicit activation.
* No keylogging, webcam, camera, microphone, or audio data collection — ever. See Section 4 for the definitive list of data collection boundaries.

***

### 15. Workforce Analytics vs. Surveillance

#### Q: How is We360.ai different from employee surveillance software?

We360.ai is a workforce analytics and productivity optimization platform — not a surveillance tool. The distinction is important:

| Aspect                   | Surveillance Tools                                                       | We360.ai (Workforce Analytics)                                                                                 |
| ------------------------ | ------------------------------------------------------------------------ | -------------------------------------------------------------------------------------------------------------- |
| **Purpose**              | Monitor and record individual behavior for punitive oversight            | Provide actionable productivity insights for teams and organizations                                           |
| **Data approach**        | Capture everything possible (keystrokes, camera feeds, personal content) | Collect only business-relevant activity data with configurable scope. See Section 4 for definitive boundaries. |
| **Employee visibility**  | Typically hidden from employees                                          | Standard mode provides full transparency; employees can view their own data                                    |
| **Privacy controls**     | Minimal or none                                                          | Blur Engine, DNT list, shift-based tracking, screenshot controls                                               |
| **Output**               | Raw surveillance logs for individual scrutiny                            | Aggregated analytics, trends, and productivity metrics                                                         |
| **Keylogging**           | Often included                                                           | **Never** — see Section 4                                                                                      |
| **Camera/audio capture** | Common                                                                   | **Never** — see Section 4                                                                                      |

#### Q: What is We360.ai designed to be used for?

We360.ai is designed for legitimate business purposes, including:

* **Productivity optimization** — Understanding how teams spend their time across applications and tasks.
* **Workforce planning** — Data-driven decisions about workload distribution and capacity.
* **Time and attendance** — Automated time tracking and attendance management.
* **Compliance and security** — Monitoring for policy violations, data exfiltration risks, and insider threats.
* **Operational efficiency** — Identifying workflow bottlenecks and optimizing tool usage.
* **Remote workforce management** — Maintaining visibility and accountability for distributed teams.

We360.ai recommends that deploying organizations use monitoring data constructively — for coaching, process improvement, and organizational decision-making — rather than punitive individual surveillance.

#### Q: Does We360.ai perform keylogging?

**No. We360.ai does not and cannot perform keylogging.** For the complete, definitive statement on all data that We360.ai does not collect — including keylogging, webcam, audio, and personal file access — see **Section 4: Data Collection & What Is NOT Collected**. The platform captures only aggregate keystroke and mouse-click frequency counts as an activity indicator.

***

### 16. Employee Transparency & Data Access Rights

#### Q: What information can employees see about their own monitoring?

In Standard mode, employees have access to a personal dashboard showing their own productivity analytics, including:

* Time tracked and attendance records
* Application and website usage summaries
* Productivity scores and trends
* Activity timelines

This transparency allows employees to self-assess, understand how their time is spent, and improve their workflows. It also supports data protection principles by ensuring data subjects can verify what data is held about them.

#### Q: How can employees exercise their data protection rights?

We360.ai supports data subject rights as required by GDPR, DPDP Act, CCPA, and other applicable regulations:

| Right                            | How It Is Supported                                                                                                                                                               |
| -------------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Right to be informed**         | Organizations are expected to notify employees about monitoring practices via policies, employment agreements, or privacy notices. Standard mode provides real-time transparency. |
| **Right of access**              | Employees can access their own data via the Standard mode dashboard. Organizations can also export and provide data upon request.                                                 |
| **Right to rectification**       | Data inaccuracies can be corrected through administrative controls.                                                                                                               |
| **Right to erasure**             | Administrators can delete individual user data upon request. Data is also deleted automatically per the retention policy.                                                         |
| **Right to data portability**    | Data can be exported in standard formats for portability purposes.                                                                                                                |
| **Right to restrict processing** | The Do Not Track list allows organizations to cease processing for specific individuals. Shift-based tracking restricts the scope of processing.                                  |
| **Right to object**              | Organizations can evaluate objections and use the DNT list or other controls to implement the outcome.                                                                            |

Requests are processed in accordance with the applicable regulatory timeline (e.g., one month under GDPR, as soon as reasonably practicable under DPDP Act).

#### Q: Does We360.ai notify employees that they are being monitored?

The notification mechanism depends on the deployment mode:

* **Standard mode** — The We360.ai application is visible on the employee's system (system tray icon and desktop application). The employee is inherently aware of the monitoring.
* **Stealth mode** — The application runs silently. It is the deploying organization's responsibility to inform employees through workplace policies, employment contracts, or privacy notices as required by applicable law.

We360.ai recommends that all organizations, regardless of deployment mode, maintain transparent communication with employees about monitoring practices to build trust and meet legal requirements.

***

### 17. Data Protection Impact Assessment (DPIA)

#### Q: When is a DPIA required for employee monitoring?

Under GDPR (Article 35) and equivalent regulations, a Data Protection Impact Assessment is required when processing is likely to result in a **high risk to the rights and freedoms** of individuals. Employee monitoring commonly triggers a DPIA requirement when it involves:

* **Systematic monitoring** — Regular, ongoing tracking of employee activity across applications, websites, and systems.
* **Large-scale processing** — Monitoring across a significant number of employees or an entire organization.
* **Sensitive data** — Processing that may incidentally capture health information, union membership, or other special category data.
* **New or intrusive technologies** — Deploying monitoring tools that use automated decision-making, biometric data, or novel data collection methods.
* **Evaluation or scoring** — Using monitoring data for performance evaluation, profiling, or productivity scoring.

Most deployments of workforce analytics software, including We360.ai, are likely to require a DPIA under GDPR.

#### Q: How does We360.ai support DPIA completion?

We360.ai provides the information and controls needed to conduct a thorough DPIA:

* **Data inventory** — Clear documentation of all data types collected, processing purposes, and retention periods (see Section 4).
* **Configurable data collection** — Ability to minimize data collection to only what is necessary for the stated purpose, supporting the proportionality assessment.
* **Privacy controls documentation** — Blur Engine, DNT list, shift-based tracking, and other safeguards that serve as risk mitigation measures in the DPIA.
* **Security controls** — Encryption, access controls, and incident management processes documented in this FAQ serve as technical and organizational measures.
* **Data flow information** — Architecture and data flow diagrams available upon request to map how data moves through the system.
* **Subprocessor information** — List of subprocessors and their roles available as part of the DPA, supporting the third-party risk assessment.
* **Deployment flexibility** — On-premise and BYOC options allow organizations to reduce risk by keeping data within their own infrastructure.

> **Tip:** Organizations should complete a DPIA before deploying We360.ai and review it periodically or when making significant changes to the monitoring configuration. We360.ai's team can provide supporting documentation upon request.

#### Q: Is a DPIA required under India's DPDP Act?

The DPDP Act 2023 does not explicitly mandate a DPIA in the same manner as GDPR. However, it requires Data Fiduciaries to implement appropriate technical and organizational measures to protect personal data and to demonstrate compliance. Conducting a privacy impact assessment is considered a best practice for organizations deploying employee monitoring tools in India and may be required for Significant Data Fiduciaries as designated by the government.

***

### 18. Remote, Hybrid & BYOD Workforce Monitoring

#### Q: How does We360.ai support monitoring for remote and hybrid workforces?

We360.ai is built for distributed workforce environments. The agent operates identically whether the employee is in the office, working from home, or at a remote location:

* **No VPN dependency** — The agent communicates with We360.ai's backend over standard HTTPS (port 443). No VPN, corporate network, or special network configuration is required.
* **Offline-first architecture** — If the employee's internet connection is intermittent, activity data is stored locally in an encrypted database and synced automatically when connectivity is restored.
* **Shift-based tracking** — Ensures monitoring is limited to work hours regardless of the employee's physical location, respecting work-life boundaries.
* **Multi-platform support** — Agents available for Windows, macOS, Linux, iOS, Android, and Chrome, covering all common remote work environments.
* **Location-agnostic analytics** — Productivity metrics are calculated consistently regardless of whether the employee is onsite or remote.

#### Q: Does We360.ai support BYOD (Bring Your Own Device) environments?

Yes, We360.ai can be deployed on both company-owned and employee-owned devices. However, organizations deploying on personal devices should consider:

* **Legal requirements** — Many jurisdictions require explicit, informed consent before monitoring personal devices. Organizations should ensure appropriate consent mechanisms are in place.
* **Scope limitation** — Use shift-based tracking to restrict monitoring strictly to work hours, preventing capture of personal activity.
* **Privacy controls** — Enable the Blur Engine and configure URL/app blocklists to minimize incidental capture of personal data.
* **Employee communication** — Clearly communicate the scope and limitations of monitoring on personal devices via policies or agreements.
* **Standard mode recommended** — Standard mode provides full transparency to the employee, which is particularly important on personal devices where the expectation of privacy is higher.

We360.ai does **not** access personal files, camera feeds, microphone, or audio on any device — company-owned or personal. For the definitive list of data collection boundaries, see **Section 4**.

#### Q: How does We360.ai ensure work-life balance boundaries?

We360.ai provides several mechanisms to ensure monitoring respects work-life boundaries:

* **Shift-based tracking** — Monitoring activates only during configured work shifts and deactivates automatically outside those hours. No activity data is captured during off-hours.
* **Do Not Track list** — Employees can be exempted entirely during specific periods or permanently.
* **No always-on monitoring** — Unlike some surveillance tools, We360.ai does not continuously monitor 24/7 unless explicitly configured by the organization to do so.
* **Standard mode controls** — In Standard mode, employees can see when tracking is active, providing clarity on monitoring boundaries.
* **GPS tracking only when enabled** — Field location tracking applies only to the mobile app and only when explicitly activated by the organization.

***

### Contact

For compliance inquiries, documentation requests, or to schedule a security review:

* **Data Protection Officer**: <dpo@we360.ai>
* **Security & Vulnerability Reporting**: <security@we360.ai>
* **General Support**: <support@we360.ai>

We360.ai is committed to transparency and will work with your security and compliance teams to address any additional questions during the vendor evaluation process.


# Product

We360.ai product reference — employee monitoring, time tracking, attendance management, and workforce productivity features.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-calendar">:calendar:</i></td><td><strong>Work &#x26; Time Management</strong></td><td>Attendance, Leave Management, Invoicing, Notes, Projects &#x26; Tasks, Timesheets.</td><td><a href="/reference/work-and-time-management/product/work-and-time-management">Work &amp; Time Management</a></td></tr><tr><td><i class="fa-chart-area">:chart-area:</i></td><td><strong>Workforce Productivity</strong></td><td>App &#x26; URL Tracking, Field Tracking, Insights, IT Tracking, Productivity Rules, Screen Tracking, GeoFencing.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity">Workforce Productivity</a></td></tr><tr><td><i class="fa-chart-mixed">:chart-mixed:</i></td><td><strong>Advanced Analytics</strong></td><td>Business Intelligence, Capacity Planning, Technology Usage, Workforce Risk Intelligence. (Premium)</td><td><a href="/reference/work-and-time-management/product/advanced-analytics">Advanced Analytics</a></td></tr></tbody></table>


# Work & Time Management

We360.ai work and time management — attendance tracking, timesheet logging, leave management, and project task tracking.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-user-check">:user-check:</i></td><td><strong>Attendance</strong></td><td>Employee attendance tracking and management.</td><td><a href="/reference/work-and-time-management/product/work-and-time-management/attendance">Attendance</a></td></tr><tr><td><i class="fa-umbrella-beach">:umbrella-beach:</i></td><td><strong>Leave Management</strong></td><td>Employee leave request and approval system.</td><td><a href="/reference/work-and-time-management/product/work-and-time-management/leave-management">Leave Management</a></td></tr><tr><td><i class="fa-file-invoice-dollar">:file-invoice-dollar:</i></td><td><strong>Invoicing</strong></td><td>Invoice generation and management.</td><td><a href="/reference/work-and-time-management/product/work-and-time-management/invoicing">Invoicing</a></td></tr><tr><td><i class="fa-sticky-note">:sticky-note:</i></td><td><strong>Notes</strong></td><td>Note-taking and documentation features.</td><td><a href="/reference/work-and-time-management/product/work-and-time-management/notes">Notebook</a></td></tr><tr><td><i class="fa-tasks">:tasks:</i></td><td><strong>Projects &#x26; Tasks</strong></td><td>Project and task management capabilities.</td><td><a href="/reference/work-and-time-management/product/work-and-time-management/projects-and-tasks">Projects &amp; Tasks</a></td></tr><tr><td><i class="fa-table">:table:</i></td><td><strong>Timesheets</strong></td><td>Timesheet tracking and reporting.</td><td><a href="/reference/work-and-time-management/product/work-and-time-management/timesheets">Timesheets</a></td></tr><tr><td><i class="fa-clock-rotate-left">:clock-rotate-left:</i></td><td><strong>Manual Time</strong></td><td>Log untracked work with manager approval.</td><td><a href="/reference/work-and-time-management/product/work-and-time-management/manual-time">Manual Time</a></td></tr></tbody></table>


# Attendance

We360.ai attendance management — track employee presence, punctuality, working hours, and break patterns automatically.

> Feature Path: HR Suite → Attendance

The Attendance module in we360.ai provides a clear overview of employee presence, punctuality, working hours, and break patterns. It helps organizations monitor attendance trends, understand team discipline, and evaluate working time distribution across teams and individuals.

The Attendance section is divided into three tabs, each designed to provide a different level of insight:

1. Summary
2. Detailed
3. Datewise Attendance

***

## Access Control

Visibility of attendance data depends on the role of the logged-in user.

* **Admin:**

  Can view attendance data for all teams and all users in the organization.
* **Manager:**

  Can view attendance data only for their assigned teams.
* **Standard User:**\
  Cannot access the Attendance module.\
  Can only view their own information through the User Detail page.

***

## Filters

Filters allow users to refine attendance data for accurate analysis.

#### Summary Tab Filters

* Team Selection: Multi-team hierarchical selection
* Date Range: Select a custom date range

#### Detailed Tab Filters

* Team Selection: Multi-team hierarchical selection
* User Selection: Multi-user filter
* Advanced User Search: Quickly locate specific employees
* Date Range: Select a custom time period

#### Datewise Attendance Filters

* Team Selection: Multi-team hierarchical selection
* User Selection: Multi-user filter
* Advanced User Search: Search specific employees
* Date Selection: Single date selection

***

## 1. Summary Tab

The Summary tab provides a high-level overview of attendance patterns within the selected date range.

It highlights overall attendance behavior across teams and helps administrators quickly understand trends.

#### Key Metrics

1. **Attendance %**\
   Shows the percentage of employees present during the selected period compared to total employees.
2. **Late Arrivals**\
   Displays the percentage of employees who checked in after their shift start time.
3. **Break Time**\
   Shows the cumulative break duration taken by employees during the selected period.
4. **Working Time**\
   Represents the total working hours recorded across employees.

Each metric also shows a comparison against the previous period, helping identify increases or decreases.

***

#### Today’s Attendance

This widget displays attendance distribution for the current day.

It includes:

* On-time arrivals
* Late arrivals
* Total employees
* Present vs Absent distribution

The visual representation helps managers quickly assess daily attendance health.

***

#### Attendance Trends

The Attendance Trends chart displays daily attendance activity within the selected date range.

The chart includes:

* Present employees
* Absent employees
* Attendance percentage
* Average working hours

This helps identify:

* Consistent attendance patterns
* Sudden spikes in absenteeism
* Changes in working hours across days

***

#### Break Trends

This graph displays how employee break durations change across days.

It helps organizations monitor:

* Excessive break patterns
* Consistency in break duration
* Team discipline during working hours

***

#### Late Arrival Tendency

This graph tracks how often employees arrive late across the selected time period.

It compares:

* Late arrivals
* On-time arrivals

Managers can quickly detect patterns such as repeated lateness on specific days.

***

## 2. Detailed Tab

The Detailed tab provides employee-level attendance insights.

It allows administrators and managers to analyze attendance metrics for each individual employee within the selected time range.

***

#### Attendance Trends

The top section displays attendance trends similar to the Summary tab but focuses on deeper analysis of attendance behavior.

It visualizes:

* Present vs Absent counts
* Attendance percentage
* Average working hours

***

#### Employee List

The Employee List table shows detailed attendance information for each employee.

Columns include:

Employee\
Displays employee name and avatar.

Attendance\
Number of days the employee was present during the selected period.

Working Time\
Total time the employee spent working.

Online Time\
Total time the employee remained active or connected to the system.

Break Time\
Total break duration taken by the employee.

View (Calendar Icon)\
Opens a calendar view showing attendance history for that employee.

***

#### Employee Calendar View

Clicking the calendar icon opens a side panel showing the employee’s attendance across the selected month.

The calendar uses color indicators to represent attendance status.

Common statuses include:

* Full Day
* Half Day
* Absent
* Minimum Presence
* Weekly Off

Selecting a specific date displays:

* Punch In time
* Punch Out time
* Total duration worked

This view helps managers analyze attendance behavior at an individual level.

***

## 3. Datewise Attendance Tab

The Datewise Attendance tab provides a daily snapshot of attendance.

It answers a simple question:

“Who is present and who is absent today?”

***

#### Present Employees

The left section lists employees who are currently present.

For each employee, the system shows:

* Punch-in time
* Punch-out time (if available)

This allows managers to quickly track who has started working and who has finished their shift.

***

#### Absent Employees

The right section lists employees who have not marked attendance for the selected date.

This helps administrators identify:

* Missing attendance entries
* Employees who have not logged in
* Potential attendance issues

<br>

> **Location:** HR Suite → Attendance
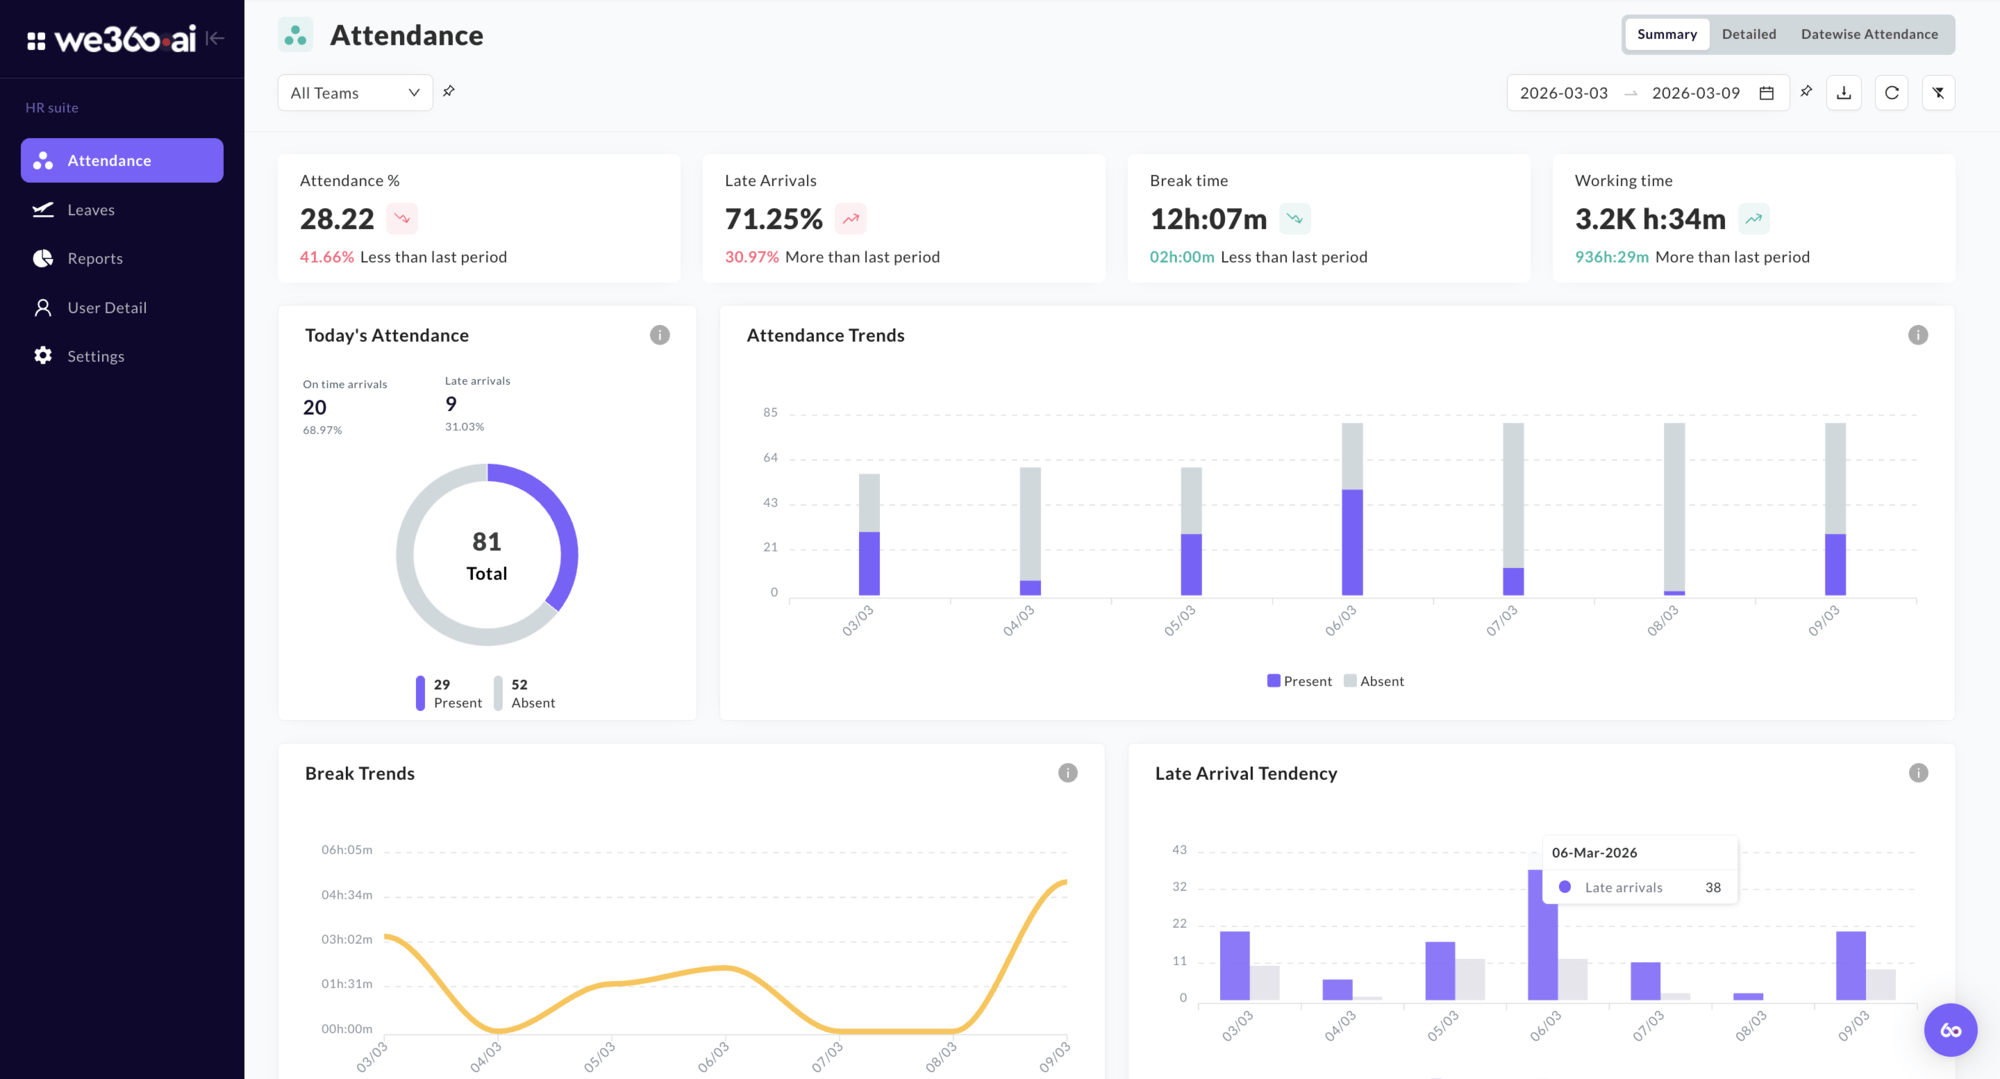
<div data-with-frame="true"><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e0a5bd9d1412701ac29b2336464fe01b545ec7ff%2Fattendance-hr-suite-app-switcher-menu.png?alt=media" alt="Apps and portals menu opened over the Attendance page, with HR Suite marked active alongside Productivity and Project Suite"><figcaption></figcaption></figure></div>

The **Attendance feature** in we360.ai provides a clear overview of employee presence, punctuality, working hours, and break patterns. It helps organizations monitor attendance trends, understand team discipline, and evaluate working time distribution across teams and individuals.

The Attendance section is divided into **three tabs**, each designed to provide a different level of insight:

1. [**Summary**](#id-1.-summary-tab)
2. [**Detailed**](#id-2.-detailed-tab)
3. [**Datewise Attendance**](#id-3.-datewise-attendance-tab)

***

## Access Control

Visibility of attendance data depends on the role of the logged-in user.

* **Admin**\
  Can view attendance data for **all teams and all users** in the organization.
* **Manager**\
  Can view attendance data only for **their assigned teams**.
* **Standard User**\
  Cannot access the Attendance module.\
  Can only view their **own information through the User Detail page**.

***

## Filters

Filters allow users to refine attendance data for accurate analysis.

#### Summary Tab Filters

* **Team Selection:** Multi-team hierarchical selection
* **Date Range:** Select a custom date range

#### Detailed Tab Filters

* **Team Selection:** Multi-team hierarchical selection
* **User Selection:** Multi-user filter
* **Advanced User Search:** Quickly locate specific employees
* **Date Range:** Select a custom time period

#### Datewise Attendance Filters

* **Team Selection:** Multi-team hierarchical selection
* **User Selection:** Multi-user filter
* **Advanced User Search:** Search specific employees
* **Date Selection:** Single date selection

***

## 1. Summary Tab

The **Summary tab** provides a high-level overview of attendance patterns within the selected date range.

It highlights overall attendance behavior across teams and helps administrators quickly understand trends.

<div data-with-frame="true"><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-bbdf23647fb24b37d2f14c4ea26cd41360252319%2Fattendance-summary-tab-dashboard-overview.png?alt=media" alt="Attendance Summary tab showing attendance percentage, late arrivals, break time, working time cards and trend charts"><figcaption></figcaption></figure></div>

#### Key Metrics

* **Attendance %**\
  Shows the percentage of employees present during the selected period compared to total employees.
* **Late Arrivals**\
  Displays the percentage of employees who checked in after their shift start time.
* **Break Time**\
  Shows the cumulative break duration taken by employees during the selected period.
* **Working Time**\
  Represents the total working hours recorded across employees.

Each metric also shows a comparison against the **previous period**, helping identify increases or decreases.

#### Today’s Attendance

This widget displays attendance distribution for the current day.

It includes:

* **On-time arrivals**
* **Late arrivals**
* **Total employees**
* **Present vs Absent distribution**

The visual representation helps managers quickly assess daily attendance health.

#### Attendance Trends

The **Attendance Trends chart** displays daily attendance activity within the selected date range.

The chart includes:

* **Present employees**
* **Absent employees**
* **Attendance percentage**
* **Average working hours**

This helps identify:

* Consistent attendance patterns
* Sudden spikes in absenteeism
* Changes in working hours across days

#### Break Trends

This graph displays how employee **break durations change across days**.

It helps organizations monitor:

* Excessive break patterns
* Consistency in break duration
* Team discipline during working hours

#### Late Arrival Tendency

This graph tracks how often employees arrive late across the selected time period.

It compares:

* **Late arrivals**
* **On-time arrivals**

Managers can quickly detect patterns such as repeated lateness on specific days.

***

## 2. Detailed Tab

The **Detailed tab** provides employee-level attendance insights.

It allows administrators and managers to analyze attendance metrics for each individual employee within the selected time range.

#### Attendance Trends

The top section displays attendance trends similar to the Summary tab but focuses on deeper analysis of attendance behavior.

It visualizes:

* Present vs Absent counts
* Attendance percentage
* Average working hours

#### Employee List

The Employee List table shows detailed attendance information for each employee.

Columns include:

**Employee**\
Displays employee name and avatar.

**Attendance**\
Number of days the employee was present during the selected period.

**Working Time**\
Total time the employee spent working.

**Online Time**\
Total time the employee remained active or connected to the system.

**Break Time**\
Total break duration taken by the employee.

**View (Calendar Icon)**\
Opens a **calendar view** showing attendance history for that employee.

***

#### Employee Calendar View

Clicking the **calendar icon** opens a side panel showing the employee’s attendance across the selected month.

The calendar uses color indicators to represent attendance status.

Common statuses include:

* **Full Day**
* **Half Day**
* **Absent**
* **Minimum Presence**
* **Weekly Off**

Selecting a specific date displays:

* **Punch In time**
* **Punch Out time**
* **Total duration worked**

This view helps managers analyze attendance behavior at an individual level.

***

## 3. Datewise Attendance Tab

The **Datewise Attendance tab** provides a daily snapshot of attendance.

It answers a simple question:

**“Who is present and who is absent today?”**

***

#### Present Employees

The left section lists employees who are currently present.

For each employee, the system shows:

* **Punch-in time**
* **Punch-out time (if available)**

This allows managers to quickly track who has started working and who has finished their shift.

***

#### Absent Employees

The right section lists employees who have **not marked attendance** for the selected date.

This helps administrators identify:

* Missing attendance entries
* Employees who have not logged in
* Potential attendance issues


# Leave Management

We360.ai leave management — employee time-off requests, approval workflows, and absence tracking for remote teams.

The Leave Management feature in we360.ai allows organizations to manage employee leave requests in a structured and transparent way. Employees can apply for leave, while managers and administrators can review, approve, reject, or edit leave requests based on their role and hierarchy.

This ensures that leave requests are tracked properly and approvals follow the organization’s reporting structure.

Feature Path: HR Suite → Leaves

***

## User Roles and Permissions

Leave management functionality varies depending on the user’s role within the organization.

### Employee (Standard User)

Employees can manage only their own leave requests.

Employees can:

* Apply for leave
* View their own leave applications
* Track the status of their leave requests

Employees cannot view or take actions on other employees' leave requests.

***

### Manager

Managers can manage leave requests for employees within their team hierarchy.

Managers can:

* Apply for leave
* View leave requests submitted within their reporting hierarchy
* View their own leave requests
* Approve leave requests
* Reject leave requests
* Edit leave requests within their hierarchy

Managers cannot take action on their own leave requests.

Once a manager approves or rejects a leave request, the decision becomes final and cannot be changed.

***

### Admin

Admins have the highest level of control within the Leave Management module.

Admins can:

* Apply for leave
* View leave requests across the organization
* View their own leave requests
* Approve leave requests
* Reject leave requests
* Edit leave requests

Admins can take action on leave requests submitted by:

* Admins
* Managers
* Standard users

Just like managers, once an Admin approves or rejects a leave request, the decision cannot be changed.

***

## Role Hierarchy

Leave approvals follow the organization’s reporting hierarchy.

Admin

* Can take action on leave requests from Admins, Managers, and Standard Users

Manager

* Can take action on leave requests from members of their assigned team

Standard User

* Can only view their own leave applications

This hierarchy ensures that leave approvals follow proper organizational reporting structures.

***

## Applying for Leave

Users can apply for leave directly from the Leave module.

Users who can apply for leave include:

* Employees
* Managers
* Admins

In some cases, Admins can also apply leave on behalf of users if required.

***

## Leave Application Fields

When submitting a leave request, users must provide the following details:

#### Leave Type

Select the type of leave from the available options in the dropdown.

Examples may include:

* Casual Leave
* Sick Leave
* Annual Leave
* Other leave types defined by the organization.

***

#### From Date

Select the start date of the leave using the calendar picker.

***

#### To Date

Select the end date of the leave using the calendar picker.

***

#### Reason

Provide a brief explanation for the leave request.

* Text input field
* Maximum limit: 100 words

Providing a clear reason helps managers review and process leave requests more effectively.

***

## Overlapping Leave Restriction

Users cannot apply for overlapping leave requests.

If a user has already applied for leave covering a particular date, they cannot submit another leave request that includes the same date.

Example:

Existing leave request\
10 June – 12 June

User cannot submit another leave request that includes:

* 11 June
* 12 June
* 10–13 June

This rule ensures that duplicate or conflicting leave requests do not occur.

***

## Leave Application Workflow

The leave process follows a simple approval workflow.

#### Step 1 — Submit Leave Request

The user selects:

* leave type
* start date
* end date
* reason

and submits the request.

***

#### Step 2 — Manager/Admin Review

The leave request becomes visible to the appropriate Manager or Admin based on the reporting hierarchy.

They can review the request and take action.

***

#### Step 3 — Approval or Rejection

Managers or Admins can choose one of the following actions:

* Approve
* Reject
* Edit

Once the leave request is approved or rejected, the decision becomes final and cannot be changed.

***

## Leave Module Tabs

The Leave module contains different tabs depending on the user’s role.

***

## Manager and Admin Tabs

Managers and Admins have access to three tabs that help them manage leave requests.

***

### Pending Approvals

This tab shows leave requests waiting for approval within the user’s hierarchy.

Managers and Admins can review these requests and take appropriate action.

Possible actions include:

* Approve
* Reject
* Edit

***

### My Pending Leaves

This tab shows leave requests submitted by the logged-in user that are still awaiting approval.

Users can track the status of their submitted requests here.

***

### All Leaves

The All Leaves tab displays all leave requests within the organization, regardless of their status.

This provides a complete view of leave activity.

#### Available Filters

Users can filter leave data using:

* User Search
* Leave Type
* Request Status
* Date Range

These filters help managers and admins quickly find specific leave requests.

***

## Employee Tabs

Standard users (employees) see a simplified version of the leave module.

***

### Pending Approvals

This tab shows leave requests submitted by the employee that are still awaiting approval.

Employees can track their pending requests here.

***

### All Leaves

This tab shows all leave requests submitted by the employee, regardless of status.

Employees can view whether their requests are:

* Pending
* Approved
* Rejected

#### Available Filters

Employees can filter their leave records using:

* Leave Type
* Request Status
* Date Range

***

## Best Practices for Leave Management

To ensure smooth leave management across the organization:

Submit leave requests in advance\
This allows managers enough time to review and plan team availability.

Provide clear reasons for leave\
This helps approvers make informed decisions.

Avoid duplicate requests\
Make sure your leave dates do not overlap with existing requests.

Check leave status regularly\
Employees can track approval progress from the leave dashboard.

<br>

The **Leave Management** feature in We360.ai allows organizations to manage employee leave requests in a structured and transparent way. Employees can apply for leave, while managers and administrators can review, approve, reject, or edit leave requests based on their role and hierarchy.

This ensures that leave requests are tracked properly and approvals follow the organization’s reporting structure.

> **Feature Path: HR Suite → Leaves**

***

## User Roles and Permissions

Leave management functionality varies depending on the user’s role within the organization.

### Employee (Standard User)

Employees can manage only their own leave requests.

Employees can:

* Apply for leave
* View their own leave applications
* Track the status of their leave requests

Employees **cannot view or take actions on other employees' leave requests**.

### Manager

Managers can manage leave requests for employees within their team hierarchy.

Managers can:

* Apply for leave
* View leave requests submitted within their reporting hierarchy
* View their own leave requests
* Approve leave requests
* Reject leave requests
* Edit leave requests within their hierarchy

Managers **cannot take action on their own leave requests**.

Once a manager **approves or rejects a leave request**, the decision becomes final and cannot be changed.

### Admin

Admins have the highest level of control within the Leave Management module.

Admins can:

* Apply for leave
* View leave requests across the organization
* View their own leave requests
* Approve leave requests
* Reject leave requests
* Edit leave requests

Admins can take action on leave requests submitted by:

* Admins
* Managers
* Standard users

Just like managers, once an **Admin approves or rejects a leave request, the decision cannot be changed.**

***

## Role Hierarchy

Leave approvals follow the organization’s reporting hierarchy.

**Admin**

* Can take action on leave requests from **Admins, Managers, and Standard Users**

**Manager**

* Can take action on leave requests from **members of their assigned team**

**Standard User**

* Can only view their own leave applications

This hierarchy ensures that leave approvals follow proper organizational reporting structures.

***

## Applying for Leave

Users can apply for leave directly from the **Leave module**.

Users who can apply for leave include:

* Employees
* Managers
* Admins

In some cases, **Admins can also apply leave on behalf of users** if required.

***

## Leave Application Fields

When submitting a leave request, users must provide the following details:

#### Leave Type

Select the type of leave from the available options in the dropdown.

Examples may include:

* Casual Leave
* Sick Leave
* Annual Leave
* Other leave types defined by the organization.

#### From Date

Select the **start date** of the leave using the calendar picker.

#### To Date

Select the **end date** of the leave using the calendar picker.

#### Reason

Provide a brief explanation for the leave request.

* Text input field
* Maximum limit: **100 words**

Providing a clear reason helps managers review and process leave requests more effectively.

***

## Overlapping Leave Restriction

Users **cannot apply for overlapping leave requests**.

If a user has already applied for leave covering a particular date, they cannot submit another leave request that includes the same date.

Example:

Existing leave request\
**10 June – 12 June**

User **cannot submit another leave request that includes:**

* 11 June
* 12 June
* 10–13 June

This rule ensures that duplicate or conflicting leave requests do not occur.

***

## Leave Module Tabs

The Leave module contains different tabs depending on the user’s role.

## Manager and Admin Tabs

Managers and Admins have access to three tabs that help them manage leave requests.

### Pending Approvals

This tab shows **leave requests waiting for approval** within the user’s hierarchy.

Managers and Admins can review these requests and take appropriate action.

Possible actions include:

* Approve
* Reject
* Edit

### My Pending Leaves

This tab shows **leave requests submitted by the logged-in user** that are still awaiting approval.

Users can track the status of their submitted requests here.

### All Leaves

The **All Leaves** tab displays all leave requests within the organization, regardless of their status.

This provides a complete view of leave activity.

#### Available Filters

Users can filter leave data using:

* **User Search**
* **Leave Type**
* **Request Status**
* **Date Range**

These filters help managers and admins quickly find specific leave requests.

***

## Employee Tabs

Standard users (employees) see a simplified version of the leave module.

### Pending Approvals

This tab shows leave requests submitted by the employee that are **still awaiting approval**.

Employees can track their pending requests here.

### All Leaves

This tab shows all leave requests submitted by the employee, regardless of status.

Employees can view whether their requests are:

* Pending
* Approved
* Rejected

#### Available Filters

Employees can filter their leave records using:

* Leave Type
* Request Status
* Date Range

***

## Best Practices for Leave Management

To ensure smooth leave management across the organization:

**Submit leave requests in advance**\
This allows managers enough time to review and plan team availability.

**Provide clear reasons for leave**\
This helps approvers make informed decisions.

**Avoid duplicate requests**\
Make sure your leave dates do not overlap with existing requests.

**Check leave status regularly**\
Employees can track approval progress from the leave dashboard.


# Invoicing

We360.ai billing and invoicing — manage subscriptions, view payment history, and configure invoice delivery.

The **Billing & Invoices** tab shows your active subscription details and your full invoice history in one place.

{% hint style="info" %}
Only Tenant Owners can access **Organization & Billing**.
{% endhint %}

## Open the billing page

1. Go to **Settings**.
2. Open **Organization & Billing**.
3. Select the **Billing & Invoices** tab.

## What you can see here

### Current subscription

At the top of the page, you can review your current plan details, including:

* **Plan name**
* **Subscription status**
* **Total usage**
* **Next billing date**

If plan upgrades are available for your workspace, you can also use the **Upgrade Plan** action from this page.

### Invoice history

The **Invoices** section lists all generated invoices with:

* **Invoice date**
* **Due date**
* **Total amount**
* **Status**

This helps you track whether an invoice is active, paid, due, or void.

## Email an invoice

Each invoice row includes an option to send the invoice by email.

Invoices are sent to the **contact person email** set in **Company Details**.

{% hint style="warning" %}
The contact email must belong to an active user in your We360.ai company.
{% endhint %}

## Change the invoice email

To change where invoices are sent:

1. Go to **Settings**.
2. Open **Organization & Billing**.
3. Select the **Company Details** tab.
4. Update the **contact person email**.
5. Save your changes.

After that, future invoice emails will be sent to the updated contact email.


# Notebook

We360.ai notebook — private note-taking and documentation built into the employee productivity platform.

The **Notebook** page is a private note space inside We360.ai.

Each note is personal. Only the user who created the note can view and manage it.

## Create a note

1. Open the **Notebook** page.
2. Click **Take a Note**.
3. Enter your note using the available fields.
4. Save or submit the note from the note editor.

## What you can do here

* Create personal notes for reminders, quick thoughts, or work references.
* View your notes in a card-based layout.
* Open and manage only the notes you created.
* Delete a note when it is no longer needed.

{% hint style="info" %}
Notes are private by default. Other users cannot access notes created in your Notebook.
{% endhint %}

The Notebook feature in we360.ai is a lightweight documentation space designed to help users capture ideas, notes, and task-related information while working. It allows users to quickly jot down thoughts, meeting notes, reminders, or any work-related details without leaving the platform.

Notebook is available within the Project Suite and can be accessed by Admins, Managers, and Standard Users.

Each user maintains a personal notebook, ensuring privacy and focus. Notes created in the notebook are visible only to the user who created them.
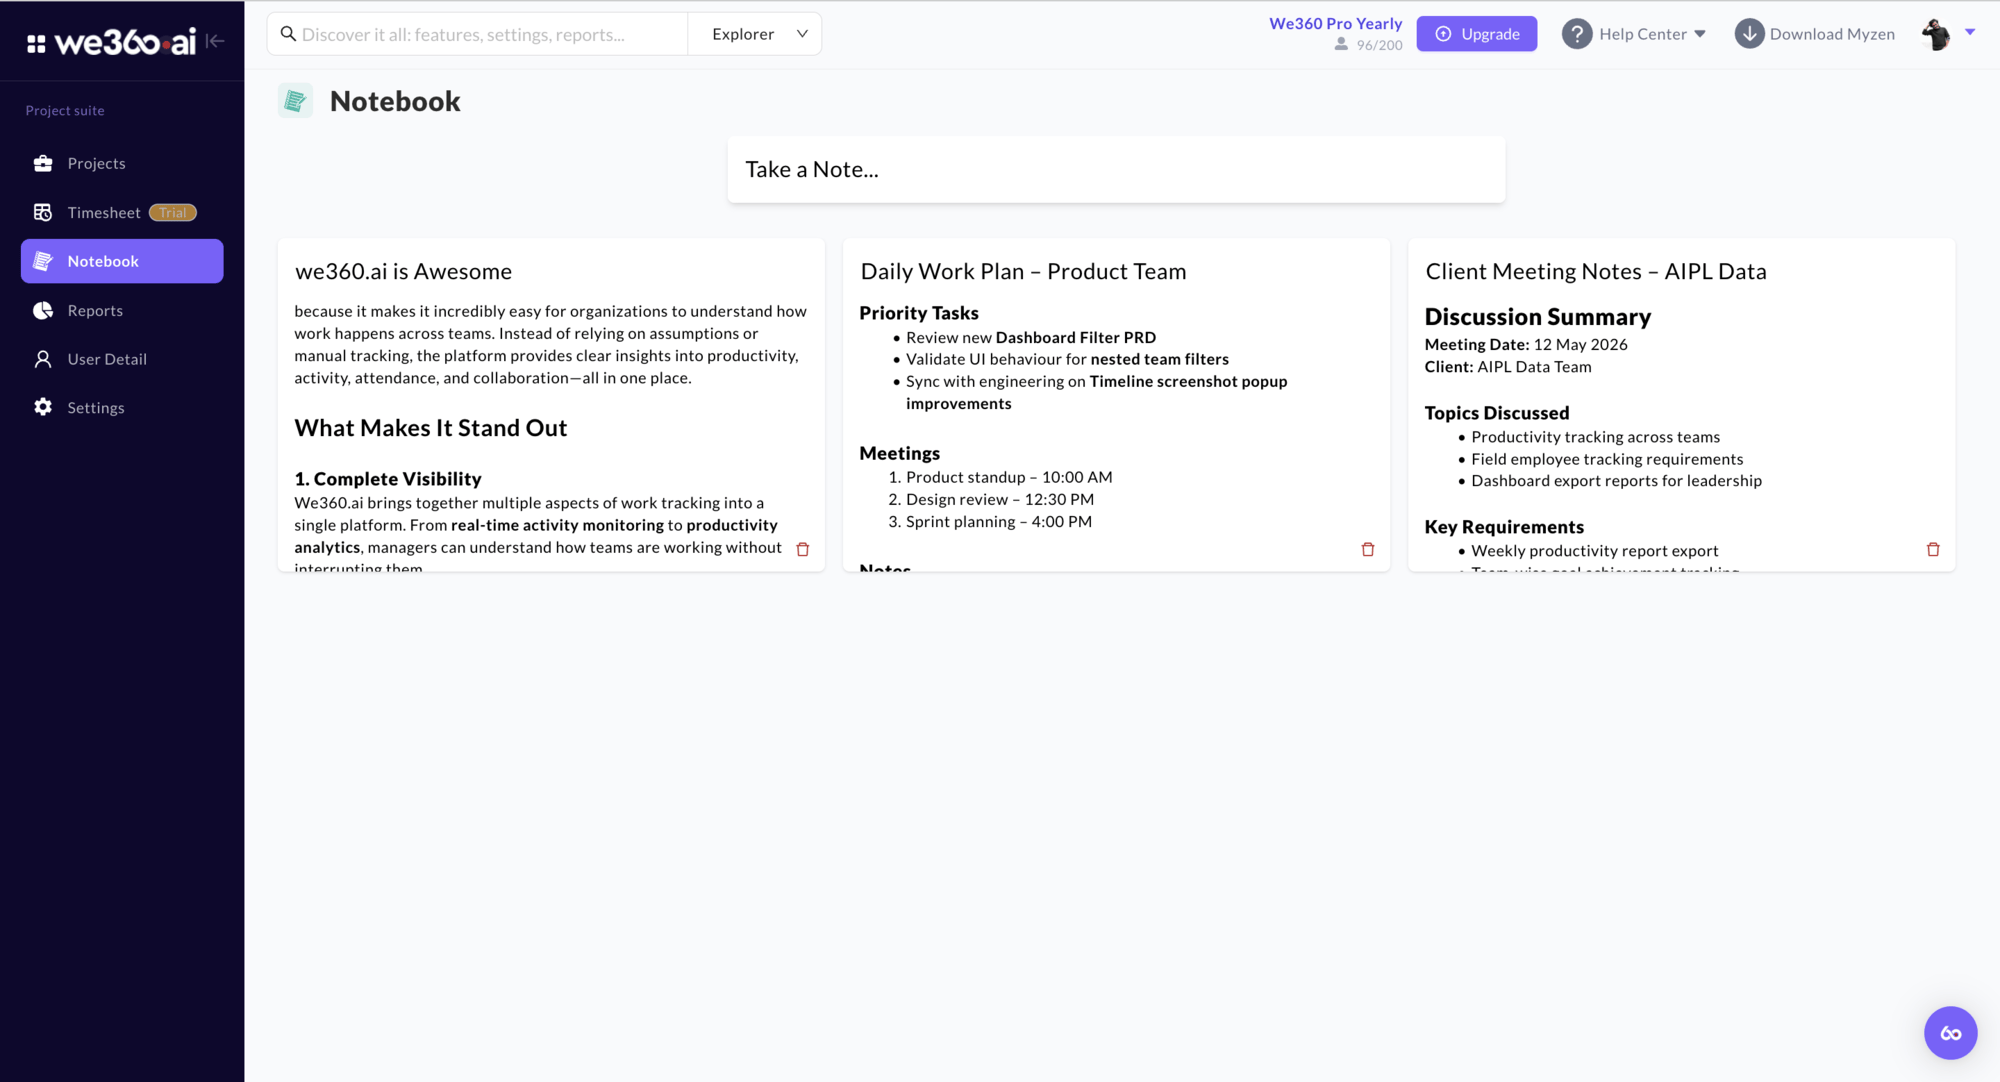
***

## Accessing the Notebook

To access the Notebook:

1. Navigate to the Project Suite from the main application switcher.
2. Select Notebook from the left navigation menu.

Once opened, the Notebook workspace displays:

* A quick input area to create a new note
* Previously saved notes displayed as cards
* Options to view, edit, or delete notes

The interface is designed for quick access so users can capture information instantly during their workflow.

***

## Creating a Note

Adding a note in the Notebook is simple and quick.

To create a new note:

1. Click on “Take a Note…” at the top of the Notebook page.
2. A note editor will open.
3. Enter a Title for your note.
4. Write your content in the note editor.
5. Click Save to store the note.

Once saved, the note will appear in the notebook as a card for easy access.

***

## Editing a Note

Users can modify their notes anytime.

To edit a note:

1. Click on the note card you want to modify.
2. The note will open in the editor view.
3. Make the required changes.
4. Click Save to update the note.

This allows users to continuously refine their notes as tasks evolve.

***

## Deleting a Note

If a note is no longer required, it can be removed.

To delete a note:

1. Locate the note card in the notebook.
2. Click the Delete icon on the note card.

The note will be permanently removed from your notebook.

***

## Note Formatting Options

The Notebook editor supports rich text formatting to help structure your notes clearly.

You can format your notes using the following options:

#### Headings

* Heading 1
* Heading 2
* Heading 3
* Normal text

These help organize notes into readable sections.

***

#### Text Formatting

You can format text using:

* Bold
* Italic
* Underline
* Remove formatting

These options allow you to emphasize important information.

***

#### Lists

Create structured lists using:

* Numbered lists
* Bullet lists

This is useful for action items, task lists, or meeting summaries.

***

#### Links

You can insert clickable links within your notes to reference external resources or documentation.

***

## Copy-Paste Formatting Support

Notebook supports preserving formatting when pasting content from other sources.

If you copy text from documents, emails, or web pages and paste it into the notebook, the existing formatting (such as headings, bold text, or lists) will remain intact wherever supported.

This makes it easier to transfer structured content into the notebook without having to reformat it.

***

## Data Retention

Notes created in the Notebook are not automatically deleted.

They remain saved in the user's account and can be accessed anytime in the future. This makes the Notebook useful for long-term documentation, reference material, and work records.

***

## Privacy of Notes

Notebook is designed as a personal workspace.

* Each logged-in user can only see their own notes.
* Notes are not visible to other users in the organization.

This ensures users can freely record ideas, drafts, and personal task notes without affecting team data.

***

## Limitations

While the Notebook supports rich text editing, certain content types are currently not supported.

The following cannot be added to notes:

* Images
* Videos
* PDF files
* File attachments

Notebook is intended for text-based documentation and quick note-taking.

***

## Common Use Cases

Users typically use the Notebook to:

* Capture quick ideas during work
* Maintain meeting notes
* Track daily work summaries
* Store reference links
* Write task reminders
* Draft documentation

Because it is built directly into the platform, users can document information without switching between tools.

<br>

The **Notebook** feature in We360.ai is a lightweight documentation space designed to help users capture ideas, notes, and task-related information while working. It allows users to quickly jot down thoughts, meeting notes, reminders, or any work-related details without leaving the platform.

Notebook is available within the **Project Suite** and can be accessed by **Admins, Managers, and Standard Users**.

Each user maintains a **personal notebook**, ensuring privacy and focus. Notes created in the notebook are visible only to the user who created them.
<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-cbc0f0e7c90d5465dd3f96025b2fabacbd7c8b7f%2Fnotebook-personal-notes-card-view.png?alt=media" alt="Notebook page in the Project Suite listing saved personal notes as cards below the Take a Note field"><figcaption></figcaption></figure>

***

## Accessing the Notebook

To access the Notebook:

1. Navigate to the **Project Suite** from the main application switcher.
2. Select **Notebook** from the left navigation menu.

Once opened, the Notebook workspace displays:

* A quick input area to create a new note
* Previously saved notes displayed as cards
* Options to view, edit, or delete notes

The interface is designed for quick access so users can capture information instantly during their workflow.

***

## Creating a Note

Adding a note in the Notebook is simple and quick.

To create a new note:

1. Click on **“Take a Note…”** at the top of the Notebook page.
2. A note editor will open.
3. Enter a **Title** for your note.
4. Write your content in the note editor.
5. Click **Save** to store the note.

Once saved, the note will appear in the notebook as a card for easy access.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-5155d596dc707dfedb61afe19b763621beaf2fe9%2Fnotebook-create-note-editor-dialog.png?alt=media" alt="Blank note editor dialog in Notebook with title field, formatting toolbar and Save and Discard buttons"><figcaption></figcaption></figure>

***

## Editing a Note

Users can modify their notes anytime.

To edit a note:

1. Click on the note card you want to modify.
2. The note will open in the editor view.
3. Make the required changes.
4. Click **Save** to update the note.

This allows users to continuously refine their notes as tasks evolve.

***

## Deleting a Note

If a note is no longer required, it can be removed.

To delete a note:

1. Locate the note card in the notebook.
2. Click the **Delete icon** on the note card.

The note will be permanently removed from your notebook.

***

## Note Formatting Options

The Notebook editor supports rich text formatting to help structure your notes clearly.

You can format your notes using the following options:

#### Headings

{% hint style="info" icon="chevron-right" %}

* ## Heading 1
* ### Heading 2
* #### Heading 3
* Normal text
  {% endhint %}

These help organize notes into readable sections.

***

#### Text Formatting

You can format text using:

{% hint style="info" icon="chevron-right" %}

* **Bold**
* *Italic*
* Underline
* Remove formatting
  {% endhint %}

These options allow you to emphasize important information.

***

#### Lists

Create structured lists using:

{% hint style="info" icon="chevron-right" %}

1. **Numbered Lists**

* **Bullet Lists**
  {% endhint %}

This is useful for action items, task lists, or meeting summaries.

***

#### Links

You can insert clickable links within your notes to reference external resources or documentation.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-399ccb620c7523f42dab7b4882412757c8d22f69%2Fnotebook-insert-link-in-note.png?alt=media" alt="Enter link popup inside an open note in Notebook, used to add a clickable hyperlink to selected text"><figcaption></figcaption></figure>

***

## Copy-Paste Formatting Support

Notebook supports **preserving formatting when pasting content** from other sources.

If you copy text from documents, emails, or web pages and paste it into the notebook, the existing formatting (such as headings, bold text, or lists) will remain intact wherever supported.

This makes it easier to transfer structured content into the notebook without having to reformat it.

***

## Data Retention

Notes created in the Notebook are **not automatically deleted**.

They remain saved in the user's account and can be accessed anytime in the future. This makes the Notebook useful for long-term documentation, reference material, and work records.

***

## Privacy of Notes

Notebook is designed as a **personal workspace**.

* Each logged-in user can only see **their own notes**.
* Notes are **not visible to other users** in the organization.

This ensures users can freely record ideas, drafts, and personal task notes without affecting team data.

***

## Limitations

While the Notebook supports rich text editing, certain content types are currently not supported.

The following cannot be added to notes:

* Images
* Videos
* PDF files
* File attachments

Notebook is intended for **text-based documentation and quick note-taking**.

***

## Common Use Cases

Users typically use the Notebook to:

* Capture quick ideas during work
* Maintain meeting notes
* Track daily work summaries
* Store reference links
* Write task reminders
* Draft documentation

Because it is built directly into the platform, users can document information without switching between tools.

***

The **Notebook feature helps keep your thoughts, ideas, and work notes organized in one place**, allowing you to focus on your tasks while keeping important information easily accessible.


# Projects & Tasks

We360.ai project management — organize tasks, track team work, and manage projects with built-in time tracking.

The **Projects & Tasks module** in We360.ai is designed to bring structure and visibility to how work is planned and executed across teams. It transforms scattered tasks and conversations into a **centralized system of record**, where every piece of work is clearly defined, assigned, and trackable.

At its foundation, the module organizes work into a simple hierarchy:

> **Projects → Tasks → Child Tasks**

A **Project** represents a larger initiative, a **Task** represents an actionable unit of work, and **Child Tasks** allow further breakdown of complex work into smaller, manageable steps. This structure ensures clarity at both the planning level and execution level.

{% hint style="info" %}
This page describes what the module is and how it behaves. To see where each control lives on screen, see the [Project Suite screens](https://docs.we360.ai/reference/work-and-time-management/user-interfaces/portal/project-suite/projects). For step-by-step goals such as billable time, sprints, and Jira sync, see [Managing Projects & Time](https://docs.we360.ai/how-to-and-best-practices/managing-projects-and-time).
{% endhint %}

***

### Core Capabilities

<details>

<summary><strong>Project Management</strong></summary>

The **Project** serves as a high-level overview of all projects within the workspace.

It provides:

* A consolidated list of all projects
* Visibility into project ownership and structure
* Financial indicators such as billing type (non-billable, time-based, fixed, mixed, or inherited from the organization default)
* Quick insight into project distribution and status

Each project is identified with a unique key, name, and ownership, and exists in a defined lifecycle:

* **Active** → Work is ongoing
* **Archived** → Work is paused; the project is hidden from operational views but can be reactivated
* **To Be Deleted** → The project is queued for permanent removal

Projects remain active until explicitly archived or marked for deletion, ensuring continuity and visibility.

Projects can be **Public** (visible to everyone in the organization) or **Private** (accessible only to assigned members). This lets teams keep sensitive work restricted while keeping general work transparent and searchable.

This enables teams to monitor multiple projects simultaneously without diving into individual task details.

</details>

<details>

<summary><strong>Task Management</strong></summary>

Tasks are the core execution units within a project.

Each task captures all essential information required to complete work, including:

* Task summary and description
* Task type (Epic, Task, or Bug)
* Assignee, Reporter, Reviewer or QA
* Status, priority, and tags
* Start date and due date
* Time estimate and story points

Tasks move through a defined lifecycle. Each project defines its own set of statuses through workflow settings; a new project is seeded with defaults such as:

* **To Do**
* **In Progress**
* **Done**

Teams can add or rename statuses (for example, a **Review** or **Blocked** stage) to match how they work. This provides a consistent way to track progress and understand the current state of work.

***

**Task Views**

Tasks can be visualized in multiple formats to suit different workflows:

<table data-view="cards"><thead><tr><th></th><th></th></tr></thead><tbody><tr><td><strong>List View</strong> →</td><td>Structured, data-heavy view for detailed tracking</td></tr><tr><td><strong>Kanban View</strong> →</td><td>Status-based visualization for workflow tracking</td></tr></tbody></table>

This flexibility allows teams to choose between a **structured view or a flow-based view** of work.

***

**Inline & Structured Task Creation**

The module supports two modes of task creation:

<table data-view="cards"><thead><tr><th></th><th></th></tr></thead><tbody><tr><td><strong>Structured Task Creation</strong> →</td><td>For detailed tasks with full context</td></tr><tr><td><strong>Inline Task Creation</strong> →</td><td>For quickly adding tasks during planning</td></tr></tbody></table>

This ensures both speed and depth, depending on how work is being captured.

***

**Attachments & Context Management**

Each task supports **attachments**, allowing teams to store relevant files directly within the task.

This includes:

* Documents
* Screenshots
* Design assets
* Requirement files

By attaching context directly to tasks, the module eliminates dependency on scattered communication tools.

***

**Search & Advanced Task Filtering**

As projects scale, discoverability becomes critical.

The module includes:

**Search**

* Keyword-based lookup across tasks

**Advanced Task Filtering**

* Logic-based filtering system using conditions such as:
  * is
  * contains
  * does not contain
  * exactly contains

Filters follow a structured format:\
**Where → Field → Condition → Value**

This allows users to construct precise queries and quickly locate relevant tasks.

***

**Customizable Task Views**

Users can customize how task data is displayed by selecting relevant columns such as:

* Status
* Assignee
* Estimate
* Reporter
* Start Date
* Due Date

This ensures that the task view aligns with different team workflows and priorities.

</details>

<details>

<summary><strong>Child Tasks (Granular Execution)</strong></summary>

Child Tasks allow teams to break down complex tasks into smaller, actionable components.

This enables:

* Better distribution of work
* Clearer ownership
* More accurate tracking of progress

Child tasks remain linked to their parent task, ensuring that detailed execution stays connected to the broader objective.

</details>

***

### Project Cost Management

The module includes built-in awareness of project-level financial structures, enabling organizations to track the true cost of work delivery.

Projects can operate under different billing models:

* **Non-billable**—no cost is accrued
* **Time-based**—an hourly rate applied to logged time
* **Fixed**—a flat project amount
* **Mixed**—a fixed amount plus an hourly rate
* **Inherited**—the organization-wide default billing configuration

Rates can also be overridden per member, so a specific person's time on a project can be priced differently from the project default.

{% hint style="info" %}
Billing and cost configuration is enabled per organization. When enabled, rates can be set at the organization, project, and member levels, and costs are calculated from approved timesheet time. Generating and sending invoices directly from the project interface isn't yet available.
{% endhint %}

This ensures that execution and financial tracking remain aligned.

***

### Timesheet Synchronization

The system links time logs with task activity, so time logged against a task and time recorded on a timesheet stay reconciled.

This ensures that:

* Work tracked in timesheets reflects actual task execution
* Task-level effort is accurately captured

This linkage improves both **productivity tracking and financial accuracy**.

***

### Workflow Control

Tasks operate within structured workflows that define how they move between statuses.

These workflow rules ensure:

* Consistency in execution
* Controlled progress transitions
* Standardization across teams

Because statuses and transitions are configured per project, each team can enforce a workflow that matches its own process.

***

### Role & Access Context

Project access is governed by ownership and membership. Even within a project, **execution control is structured** through roles and assignment.

* Tasks define responsibility through assignees
* Projects define ownership
* Role-based access governs who can view, modify, or manage work

Project roles include **Project Owner** and **Project Member**, plus **Guests**, who have view-only access and can't make changes. In Public projects, any organization user can participate according to their permissions; in Private projects, only assigned members can.

This ensures a balance between **transparency and control**.

***

### Jira Sync

Projects can be synchronized with Jira so that tasks, worklogs, and fields stay aligned between We360.ai and Jira. The integration supports two-way, inbound-only, or outbound-only sync, project and user mapping, and field mapping (including story points).

{% hint style="info" %}
The Jira integration is in **Alpha** and under active development. See [Integrations](https://docs.we360.ai/administration/settings-center/integrations) for setup and sync options.
{% endhint %}

***

### What This Module Enables

Projects & Tasks in We360.ai isn't just a task tracker—it's a **work execution system** that brings together planning, tracking, and accountability.

It enables organizations to:

* Convert ideas into structured work
* Break down complex initiatives into manageable tasks
* Maintain visibility across teams
* Track progress in real time
* Connect execution with time and financial data

The Projects & Tasks feature in We360.ai allows teams to organize work into projects and manage individual tasks efficiently. It provides a centralized workspace where teams can create projects, break down work into tasks and child tasks, assign responsibilities, and track progress.

With Projects & Tasks, all work-related activities remain structured, searchable, and visible to the members who have access.

***

## Who Can Create Projects

Projects can be created by **any user in the organization**, including:

* **Admins**
* **Managers**
* **Standard Users**

This ensures that teams can start organizing work without relying on administrative permissions.

When a project is created, its creator can set it as Public or Private, which determines who else can see and work on it.

***

## Project Visibility

Every project has a **visibility** setting that controls who can access it:

* **Public**—visible to everyone in the organization. Any user can view its tasks and search across them.
* **Private**—visible only to assigned members. Users who aren't members can't see the project or its tasks.

Public projects improve transparency and collaboration; private projects keep sensitive work restricted to the people involved.

***

## Project Status

Every project has a **status** that indicates its current state:

* **Active**—work is ongoing
* **Archived**—the project is paused and hidden from operational views, but can be reactivated
* **To Be Deleted**—the project is queued for permanent removal

When a project is created, its status is **Active by default**. A project remains active until a user archives it or marks it for deletion.

Changing the project status helps teams indicate whether a project is still ongoing, paused, or being retired.

***

## Deleting a Project

To permanently remove a project, mark it as **To Be Deleted**.

Archiving is the reversible option: an archived project is hidden from active views but retains its tasks and history and can be reactivated at any time. Marking for deletion is the path to permanent removal.

This two-step approach prevents accidental loss of work or task history.

***

## Understanding the Structure

Work inside the Projects module follows this structure:

**Project → Tasks → Child Tasks**

***

## Projects

A **project** represents a larger initiative or group of related work.

Examples include:

* Product feature development
* Website redesign
* Marketing campaigns
* Client implementation projects
* Internal audits

Opening a project displays the **task list view**, where all tasks belonging to the project are visible.

***

## Tasks

Tasks represent individual work items that need to be completed within a project.

Examples:

* Create dashboard UI
* Fix login issue
* Prepare monthly report
* Design campaign creatives

Each task includes important information such as:

* Task summary
* Task type (Epic, Task, or Bug)
* Description
* Assignee
* Status
* Priority
* Start date
* Due date
* Time estimate
* Story points
* Reporter

Tasks help teams clearly understand what work needs to be completed and who is responsible.

***

## Child Tasks

Some tasks require multiple smaller steps to complete. In such cases, you can create **child tasks**.

Child tasks allow you to break down larger tasks into smaller actionable steps.

Example:

**Parent Task:**\
Build Analytics Dashboard

**Child Tasks:**

* Design dashboard layout
* Develop data APIs
* Implement chart components
* Perform testing

Child tasks remain linked to the parent task, helping teams track progress more effectively.

***

## Task List View

When you open a project, tasks appear in a **list view**.

The task list displays important task information in columns such as:

* Task summary
* Status
* Assignee
* Estimate
* Reporter
* Start date
* Due date

This view provides a quick overview of all work happening within the project.

***

## Creating Tasks

Tasks can be created in two ways:

#### Create Task Button

You can create a task using the **Create Task button** inside the project.

Steps:

1. Open the project
2. Click **Create Task**
3. Enter task details
4. Save the task

This method is useful when creating detailed tasks that require descriptions, dates, or assignments.

***

#### Inline Task Creation

Tasks can also be created directly within the task list using **inline task creation**.

Steps:

1. Click the **Create Task field inside the task list**
2. Enter the task summary
3. Press **Enter** to create the task instantly

Inline task creation is designed for **quick task entry**, allowing teams to rapidly add multiple tasks during planning sessions.

***

## Task Attachments

Each task supports **file attachments**.

Attachments help teams keep relevant resources connected directly to the task.

You can attach files such as:

* documents
* screenshots
* reference files
* design assets
* requirement documents

Attachments allow team members to access all necessary resources without searching through emails or chat threads.

***

## Task Status

Each task moves through the statuses defined for its project. A new project starts with a default set, which teams can customize.

Typical default statuses include:

#### To Do

The task has been created but work has not started yet.

#### In Progress

The task is currently being worked on.

#### Done

The task has been completed.

Updating task status ensures the project reflects the current progress of work.

***

## Searching Tasks

Projects may contain many tasks, so searching quickly becomes important.

The task list includes a **search function** that allows users to find tasks by keywords.

You can search using:

* task name
* assignee
* task details

This makes it easier to locate specific work items.

***

## Advanced Task Filtering

The Projects module also includes **advanced task filtering**.

This filtering system allows users to build complex search conditions similar to tools like **Jira** or **ClickUp**.

Filters use a structured query approach based on conditions such as:

**Where → Field → Condition → Value**

Example filters:

* **Assignee is John**
* **Status contains "In Progress"**
* **Summary contains "Dashboard"**
* **Reporter exactly contains "Admin"**
* **Task type does not contain Bug**

Supported filter logic includes:

* **is**
* **contains**
* **does not contain**
* **exactly contains**

These filters allow teams to create precise queries to quickly find the tasks they need.

***

## Customizing Task List Columns

The task list allows users to customize which columns are visible.

Columns that can be displayed include:

* Status
* Assignee
* Estimate
* Reporter
* Start Date
* Due Date

This flexibility allows users to tailor the task list view according to their workflow.

***

## Best Practices for Managing Projects and Tasks

To get the most value from Projects & Tasks:

**Break complex work into child tasks**\
Smaller tasks improve clarity and progress tracking.

**Assign tasks clearly**\
Every task should have a responsible owner.

**Attach relevant resources**\
Use attachments to keep important files linked to tasks.

**Use advanced filters**\
Filters help teams quickly locate the tasks they need.

**Update statuses regularly**\
Keeping task statuses updated ensures accurate project visibility.

***

## Why Use Projects & Tasks

The Projects & Tasks feature helps teams:

* organize work in a structured way
* track responsibilities clearly
* collaborate more effectively
* search and filter work easily
* maintain transparency across teams

By structuring work into **projects, tasks, and child tasks**, teams can manage projects more efficiently and keep all work in one centralized workspace.


# Timesheets

We360.ai timesheets — weekly time tracking, employee timesheet logging, and team timesheet review for managers.

The **My Timesheet** page in **Weekly view** is where employees log work for each day of the week.

All employees can fill their own weekly timesheet from this view.

## Weekly view

Weekly view shows one week at a time, broken down by day.

You can add one or more rows for each day, depending on how many work items you need to log.

## Fill a timesheet row

Each row supports these fields:

* **Summary**
* **Task**
* **Tags**
* **Billable or non-billable**
* **Start time**
* **End time**
* **Duration**

Only these fields are required:

* **Summary**
* **Duration**

You can also link the entry to a task from **Projects & Tasks**.

You can add new tags or select from existing tags.

You can mark the work as **billable** or **non-billable**.

If needed, you can also enter the exact start and end time.

## Time entry formats

The timesheet accepts flexible time input.

### Start and end time

You can enter time in formats like:

* `2000`
* `2200`
* `22:00`
* `11:00 pm`
* `8:00 AM`

When start and end time are entered, **Duration** is filled automatically.

### Duration

If you skip exact time, you can enter duration directly.

Simple numbers are treated as hours.

Examples:

* `2` = 2 hours
* `2h` = 2 hours
* `120m` = 2 hours
* `45 mins` = 45 minutes
* `2h 40m` = 2 hours 40 minutes
* `1h 10m 30s` = 1 hour 10 minutes 30 seconds

You can use hours, minutes, and seconds in the same value.

## Keyboard shortcuts

Keyboard entry is supported in Weekly view.

* **Tab** moves across the current row.
* **Enter** on the **Duration** field saves the row and opens a new row for the **same day**.
* **Tab** from the **Duration** field moves to a new row for the **next day**.

This makes it faster to fill a full week without using the mouse.

## Submit the week

After all rows are filled for the week, click **Submit Timesheet**.

Once submitted, the timesheet is locked and cannot be edited by the employee.

{% hint style="warning" %}
A submitted timesheet can only be edited again if the team manager reopens it.
{% endhint %}

## History

The **History** tab shows all timesheets submitted by the employee.

Users can only see their own timesheets in this section.

Each row usually shows:

* **Period**
* **Total hours**
* **Status**
* **Approver**
* **Remark**

This helps employees track what was submitted, who reviewed it, and whether any action is needed.

The **Remark** field helps explain why a timesheet was approved, rejected, or reopened.

Click the arrow on any row to open that week's timesheet in a drawer view and review the full entry details.

### Status meanings

#### Pending

**Pending** means the timesheet was submitted by the employee but has not been reviewed by the manager yet.

#### Approved

**Approved** means the timesheet was reviewed and approved.

#### Rejected

**Rejected** means the timesheet was reviewed and sent back as rejected.

#### Reopened

**Reopened** means the manager asked the employee to update the timesheet because of a mismatch, correction, or missing detail.

When a timesheet is reopened, the employee can edit it again and resubmit it.

## Team's Timesheet

The **Team's Timesheet** tab is available only to team managers.

It gives managers the ability to review submitted timesheets for their team and take action on them.

### Sections

Team's Timesheet has three sections:

* **Pending**
* **Approved**
* **Rejected**

#### Pending

The **Pending** section shows all submitted timesheets that have not been reviewed yet.

#### Approved

The **Approved** section shows timesheets that were reviewed and approved.

#### Rejected

The **Rejected** section shows timesheets that were reviewed and rejected.

### Row layout

Each row shows the employee and the week summary at a glance.

This includes:

* **User**
* **Day-wise logged time**
* **Total logged hours for the week**

The day columns show the total time logged for each day.

The final total shows the full number of hours logged for the week.

### Open timesheet details

Click the info icon at the start of the row to open the weekly timesheet in a drawer view.

This drawer is similar to the detail drawer in **My Timesheet**.

For managers, the drawer also includes these actions:

* **Approve Timesheet**
* **Reject Timesheet**
* **Reopen Timesheet**

### More actions

The three-dot menu on a row opens additional actions:

* **View Detail**
* **Approve**
* **Reject**
* **Reopen**
* **View All Timesheet**

**View All Timesheet** opens the full timesheet history for that user.

The other actions follow the same approval flow already used for timesheet review.

### Approve, reject, and reopen

When a manager approves, rejects, or reopens a timesheet, the action opens a confirmation modal.

These modals follow the same structure, with only the action button label changing based on the selected action.


# Manual Time

We360.ai manual time — let employees log work done while untracked, with a manager approval workflow and supporting evidence.

**Manual Time** lets employees record work they did while the tracker wasn't running — for example, offline work, client meetings away from the desk, or time on a device without the agent. Entries go through a manager approval workflow, so the extra time is accounted for without compromising trust in the data.

## Why Use Manual Time

* **Close gaps in the record** — capture legitimate work that automatic tracking couldn't see.
* **Keep totals accurate** — ensure attendance and productivity reflect real effort.
* **Stay accountable** — every entry is reviewed and approved before it counts.

## Submitting a Manual Time Entry

An employee creates a request with **Add Manual Time**, providing:

* The **date** (past dates only — no future entries) and **start / end time**. Duration is calculated automatically.
* A **time attribution** — Productive, Neutral, or Unproductive (defaults to Productive).
* A **summary** explaining what the time was for.
* An optional **attachment** (a single image) as supporting evidence.
* An optional **manual time type**, if your administrator has configured type options.

Every new entry starts as **Pending** and notifies the employee's manager by email.

## Approval Workflow

Manual-time requests move through three states — **Pending → Approved / Rejected**. From the **My Team** view, a manager reviews pending requests and either approves or rejects them, adding a **remark** in each case:

* **Approve** — the time is accepted and counts toward the employee's attributed hours.
* **Reject** — the request is declined and contributes no hours.

Only entries whose date is fully in the past can be actioned. Employees can delete their own **Pending** entries, but once an entry is approved or rejected it is locked. This mirrors the review flow used for [Timesheets](/reference/work-and-time-management/product/work-and-time-management/timesheets), so managers work with a familiar approve/reject process.

{% hint style="info" %}
Only **approved** manual time counts toward tracked hours and analytics — pending and rejected entries do not.
{% endhint %}

## Reviewing Manual Time

All submitted entries — with their approval status, summary, and any attached evidence — are available in the **Manual Time** report (see [Reports](/reference/work-and-time-management/user-interfaces/portal/universal-tools/reports)) for auditing and record-keeping.


# Workforce Productivity

We360.ai workforce productivity — app tracking, URL monitoring, screen recording, screenshot capture, and productivity analytics.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-window-restore">:window-restore:</i></td><td><strong>App &#x26; URL Tracking</strong></td><td>Application and URL monitoring capabilities.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/app-and-url-tracking">App &amp; URL Tracking</a></td></tr><tr><td><i class="fa-map-marked-alt">:map-marked-alt:</i></td><td><strong>Field Tracking</strong></td><td>Field employee location and activity tracking.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/field-tracking">Field Tracking</a></td></tr><tr><td><i class="fa-lightbulb">:lightbulb:</i></td><td><strong>Insights</strong></td><td>Analytics and insights dashboard.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/insights">Insights</a></td></tr><tr><td><i class="fa-laptop">:laptop:</i></td><td><strong>IT Tracking</strong></td><td>IT asset and system monitoring.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/it-tracking">IT Tracking</a></td></tr><tr><td><i class="fa-ruler">:ruler:</i></td><td><strong>Productivity Rules</strong></td><td>Configuring productivity measurement rules.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/productivity-rules">Productivity Rules</a></td></tr><tr><td><i class="fa-camera">:camera:</i></td><td><strong>Screen Tracking</strong></td><td>Screenshot and screen monitoring features.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/screen-tracking">Screen Tracking</a></td></tr><tr><td><i class="fa-map-pin">:map-pin:</i></td><td><strong>GeoFencing and Controls</strong></td><td>Location-based monitoring and access controls.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/geofencing-and-controls">GeoFencing and Controls</a></td></tr><tr><td><i class="fa-usb">:usb:</i></td><td><strong>USB Detection</strong></td><td>Monitor USB and external device connections.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/usb-detection">USB Detection</a></td></tr><tr><td><i class="fa-gauge-high">:gauge-high:</i></td><td><strong>Employee Scoring &#x26; Scorecards</strong></td><td>A configurable monthly performance score and scorecard.</td><td><a href="/reference/work-and-time-management/product/workforce-productivity/employee-scoring">Employee Scoring &amp; Scorecards</a></td></tr></tbody></table>


# App & URL Tracking

We360.ai app and URL tracking — monitor employee application usage, website visits, and categorize productivity time.

## Overview

We360.ai tracks application and URL usage to provide organizations with clear visibility into how time is being spent across different digital tools. This feature helps teams identify their most utilized platforms and measure focus time accurately.

## Supported Platforms

* **Desktop Agent**: Fully supported on Windows, macOS, and Linux — including **Citrix, RDP, and VDI environments**. The desktop app passively watches the active window title and records the application or domain URL in focus.
* **Chrome Extension**: A dedicated Chrome Extension is available for enhanced browser-level URL tracking and productivity insights.

## How it Works

1. **Focus Capture**: The agent detects which application or website is currently active on the user's screen.
2. **Per-Second Measurement**: It records the duration the application or URL remains in focus with **per-second granularity**, ensuring precise time accounting even for rapid task-switching.
3. **Analytics**: The tracking data is aggregated and displayed on the We360.ai dashboard, allowing administrators and managers to view usage reports and activity percentages per user or team.

## Productivity Classifications

To make the data actionable, administrators can categorize different applications and URLs based on their organization's specific needs. For example, a design tool might be categorized as "Productive" for a design team, while a social media website might be marked as "Unproductive". These classifications power the overall productivity score for each employee.


# Field Tracking

We360.ai field tracking — GPS location monitoring for remote and field employees with real-time visibility.

## Overview

Field Tracking is designed to monitor the location and activity of employees who work outside a traditional office setting. This ensures visibility, safety, and accountability for remote and field-based teams.

## Supported Platforms

* **Mobile App**: Fully supported on iOS and Android devices. Field tracking relies on the mobile application to provide location updates.
* **Desktop Agent (Standard Mode)**: The Standard desktop app also includes built-in location tracking, extending whereabouts visibility beyond mobile-only field teams to desktop endpoints on Windows, macOS, and Linux.

## Capabilities

By utilizing background tracking capabilities on the mobile device, We360.ai can map a user's geographical movement throughout their working shift.

* **Real-time Location:** Administrators and managers can view the real-time whereabouts of their field employees directly via the admin web dashboard.
* **Location History:** Location streams are synced to provide historical pathways and timeline data, allowing managers to review routes taken during a shift.
* **Offline Reliability**: The mobile app is designed to work asynchronously. If a user enters an area with poor or no network connectivity during a field assignment, the location data is safely stored locally on the device. Once an internet connection is restored, the data is automatically synced to the dashboard, ensuring no tracking information is lost.


# Insights

We360.ai insights — workforce analytics dashboard with actionable productivity reports for remote team management.

## Overview

Insights provide a comprehensive, high-level view of your organization's performance. It synthesizes all the underlying tracking data—from application usage to active hours—into actionable reports, enabling managers to make data-driven decisions.

{% hint style="info" %}
**Supported Platforms:** Insights and reporting are primarily accessed and viewed through the We360.ai web administrative portal.
{% endhint %}

We360.ai is not just an employee monitoring tool; it is a workforce intelligence & productivity analytics platform that enables:

* Data-driven performance management
* Predictive HR decision-making
* Operational efficiency
* Cost optimisation
* Workforce wellbeing governance

> The platform converts raw work activity into behavioural intelligence and finally business outcomes.

***

## What Insights Provides

The insights dashboard aggregates data across custom date ranges and teams to deliver:

{% columns %}
{% column %}
**Performance Metrics**

View total active hours, idle spans, and overall productivity benchmarks for individuals and entire groups.
{% endcolumn %}

{% column %}
**Activity Correlations**

Understand how different activities (like application usage and screen time) correlate with overall output.
{% endcolumn %}
{% endcolumns %}

{% columns %}
{% column %}
**Team Comparisons**

Compare productivity trends across different organizational subsets to identify high-performing teams or areas needing support.
{% endcolumn %}

{% column %}
**Exportable Reports**

Generate and export targeted reports outlining organizational adherence and productivity metrics for external review or integration.
{% endcolumn %}
{% endcolumns %}

***

## Insights Coverage

<details>

<summary>Strategic-Level Insights</summary>

**Organisation-Wide Productivity Intelligence**

* *Features used: AI productivity analytics, executive dashboards*
* **Insights:** Productivity comparisons across departments, roles, locations. Identification of high/low-performing teams. Capacity planning inputs.
* **Business Impact:** Better org design, performance-linked budgeting, data-backed leadership decisions.

**Workforce Risk Prediction**

* *Features used: Wellness & Activity*
* **Insights:** Early signals of disengagement, overwork, teams at attrition risk, overtime-driven productivity decline.
* **Business Impact:** Reduced hiring cost, retention strategy planning, proactive HR interventions.

**Digital Transformation Maturity**

* *Features used: App usage, URLs, workflow analytics*
* **Insights:** Which tools are highly used, underutilised, redundant. ROI on SaaS stack.
* **Business Impact:** SaaS cost rationalisation, tool consolidation, automation roadmap.

</details>

<details>

<summary>HR &#x26; People Analytics Insights</summary>

**Employee Performance Intelligence**

* *Features used: Productivity mapping, activity tracking, focus time*
* **Insights:** Productive vs unproductive time, deep work vs shallow work patterns, individual work styles.
* **Use Cases:** Performance reviews based on data, personalised coaching, role–person fitment.

**Workload & Capacity Balancing**

* *Features used: Wellness360, active/idle time*
* **Insights:** Who is overutilised, underutilised, or optimally loaded. Real capacity of teams.
* **Business Impact:** Better resource allocation, reduced burnout, improved delivery timelines.

**Attendance Behaviour Intelligence**

* *Features used: Automated attendance, break trends, shift tracking*
* **Insights:** Late-coming patterns, shift efficiency, break behaviour analytics.
* **Business Impact:** Policy optimisation, hybrid work model design, payroll accuracy.

</details>

<details>

<summary>Operations &#x26; Delivery Insights</summary>

**Process Efficiency Mapping**

* **Insights:** Actual time taken vs planned time, repetitive manual work.
* **Business Impact:** SOP redesign, automation opportunities, faster turnaround time.

**Project Execution Intelligence**

* **Insights:** Realistic project timelines, effort estimation accuracy, delivery risk alerts.
* **Business Impact:** Better client commitments, improved project margins.

**Real-Time Vigilance for Leaders**

* **Insights:** Instant operational visibility, work status without review meetings, real-time performance dips.
* **Business Impact:** Faster decision cycles, reduced manual reporting.

</details>

<details>

<summary>Finance, Compliance &#x26; Security</summary>

**Finance & Cost Optimisation**

* *Cost of Productivity:* Cost per productive hour, payroll vs actual output, team-wise efficiency ROI.
* *SaaS & Tool ROI:* Paid tools not being used, shadow IT detection, license optimisation.
* *Manpower Planning:* Whether to hire or optimise existing capacity, outsource vs in-house decisions.

**Compliance & Security**

* **Insights:** Data misuse risk, policy adherence, device usage compliance.
* **Business Impact:** Stronger audit readiness, reduced insider risk.

</details>

<details>

<summary>Employee Experience &#x26; Culture</summary>

**Work-Life Balance Index**

* **Insights:** After-hours work patterns, burnout hotspots, healthy vs overloaded teams.

**Additional Insights**

* **Engagement Signals:** Culture health measurement and manager effectiveness evaluation derived from focus time and activity patterns.
* **Managerial Effectiveness:** Measure which managers overload teams or deliver high productivity to become a manager scorecard system.
* **Remote & Hybrid Work:** Remote vs office productivity, ideal work models for each function, location-wise performance.

</details>

***

## Stakeholder-Wise Value

Different stakeholders derive unique value from We360.ai insights:

{% tabs %}
{% tab title="CXO" %}

* Org productivity dashboard
* Cost vs output analytics
* Strategic workforce planning
  {% endtab %}

{% tab title="HR" %}

* People analytics
* Attrition prediction
* Performance fairness
  {% endtab %}

{% tab title="Delivery / Ops" %}

* Timeline accuracy
* Resource allocation
* Process optimisation
  {% endtab %}

{% tab title="Finance" %}

* Payroll efficiency
* Cost per output
* Tool ROI
  {% endtab %}

{% tab title="IT & Compliance" %}

* Device governance
* Data security visibility
  {% endtab %}
  {% endtabs %}

***

## The Maturity Curve

{% hint style="success" %}
We360.ai moves an organisation from basic visibility to predictive intelligence: **Attendance Tracking → Productivity Tracking → Workforce Intelligence → Predictive Organisation**
{% endhint %}


# IT Tracking

We360.ai IT tracking — monitor employee devices, hardware assets, and software inventory via the desktop agent.

## Overview

IT Tracking offers generalized asset oversight for organizational infrastructure connected through We360.ai. It focuses on the hardware and software details of devices running the tracking agent.

## Supported Platforms

* **Desktop Agent**: Fully supported on Windows, macOS, and Linux — including **Citrix, RDP, and VDI environments** — to collect system and hardware metadata.
* **Web Dashboard**: Administrators can view the asset reports via the We360.ai web portal.

## Capabilities

We360.ai collects hardware specifications, operating system details, and networking information from the connected devices. This provides organizations with a centralized view of their IT assets.

* **Asset Reporting**: Organizations can easily view installed application versions, operating systems, and connectivity statuses.
* **Health Monitoring**: IT tracking ensures that endpoint agents are healthy, tracking data efficiently, and compliant with organizational hardware standards.


# Productivity Rules

We360.ai productivity rules — configure app and URL tracking classifications for employee productivity monitoring.

## Overview

Productivity Rules govern the categorization of specific applications or URLs to define whether an employee's time spent on a given platform is considered active work. This allows organizations to tailor We360.ai to their specific operational needs.

## Supported Platforms

* **Web Dashboard**: Administrators configure Productivity Rules globally or per team via the We360.ai web portal.
* **Desktop Agent**: The configured rules are actively enforced based on the applications and URLs the Desktop Agent observes.

## Core Mechanisms

1. **Application Categorization**: We360.ai allows administrators to classify software tools and websites into distinct categories, such as "Productive", "Unproductive", or "Neutral".
2. **Flexible Mapping**: Recognizing that different teams use different tools, Productivity Rules can cascade universally across the entire organization or be precisely assigned to specific groups.
3. **Custom Overrides**: A design tool might be categorized as highly productive for the Design Team, but neutral or unproductive for the Finance Team. Administrators have the flexibility to establish completely different rulesets for identical software tools depending on the user's role.


# Screen Tracking

We360.ai screen tracking — automated screenshot monitoring, screen recording, and visual activity auditing for employees.

## Overview

Screen Tracking captures visual representations of the employee's active desktop environment. It serves as both an auditing tool and a core feature of the organizational productivity profile, providing context to the time logged.

## Supported Platforms

* **Desktop Agent**: Captures the screenshots on Windows, macOS, and Linux — including **Citrix, RDP, and VDI environments**.
* **Web Dashboard**: Managers and administrators can review captured screenshots within the user's timeline activity on the We360.ai administration portal.

## Functionality

The We360.ai desktop agent quietly captures the screen at pre-defined intervals across all supported platforms (Windows, macOS, and Linux) and securely uploads them for review. Screen Tracking works identically in both Standard and Stealth (silent) modes.

* **Configurable Captures**: Administrators govern the capture frequency through the compliance settings. The screenshot capability can be explicitly disabled for specific teams or individual users to meet varying privacy requirements.
* **Privacy & Compliance**: Configurable options exist to adjust the screenshot blur level or restrict the ability for managers to download screenshots. This protects sensitive data while ensuring enterprise-level compliance.
* **Timeline Integration**: Extracted screenshots fuel the granular user timeline logs on the front-end, allowing managers to see exactly what an employee was focusing on during specific intervals.


# GeoFencing and Controls

We360.ai geofencing — location-based attendance management, GPS access controls, and field employee tracking boundaries.

## Overview

GeoFencing allows administrators to create virtual geographic boundaries to manage access and track attendance strictly within specific physical locations. This feature is particularly useful for site-based teams, warehouse staff, or field workers who need to report to a specific location.

## Supported Platforms

* **Mobile App**: Fully supported on iOS and Android devices for location validation.
* **Web Dashboard**: Administrators configure and manage GeoFences via the We360.ai web portal.

## How to Manage GeoFences

1. **Configuration**: Administrators can define a GeoFence by setting a central coordinate (location) and a permitted radius around it via the settings on the web dashboard. Multiple locations can be configured for different teams or sites.
2. **Mobile Validation**: When an employee uses the mobile app to Punch In or Punch Out, the system validates their current GPS location against the configured GeoFence boundaries.
3. **Exceptions & Flexibility**: Recognizing that work requirements vary, administrators can enable GeoFence exceptions for specific users or groups. This allows designated employees to bypass the location validation if their role requires them to work outside the standard boundaries.


# USB Detection

We360.ai USB detection — monitor USB and external device connections for data loss prevention and endpoint security.

**USB Detection** gives you visibility into when USB storage devices are connected to or disconnected from monitored computers. It's a lightweight data-loss-prevention (DLP) and endpoint-security signal that helps you spot removable-media usage without deploying separate security tooling.

## What It Monitors

The desktop agent logs **connect** and **disconnect** events for USB **mass-storage devices** (USB drives and external storage). Each record includes:

* The **event type** — connected or disconnected.
* The **device name** — its manufacturer and product name.
* The **timestamp** and the **employee** the event belongs to.

{% hint style="info" %}
USB Detection focuses on **removable storage**. Everyday peripherals such as keyboards and mice are not logged, and the feature records device *connection activity* — it is not a file-transfer scanner. Its purpose is to flag when removable media is in use so you can follow up where your policy requires it.
{% endhint %}

## Enabling USB Detection

USB Detection is off by default and controlled by your organization's monitoring policy. A Super Admin or Admin enables the **USB Detection** toggle under **Settings → Compliance & Security → Compliance**.

{% hint style="warning" %}
Policy changes can take up to about an hour to reach endpoints, so allow some time before expecting events to appear.
{% endhint %}

## Reviewing Activity

USB connect and disconnect events are available in the **USB Detection** report (see [Reports](/reference/work-and-time-management/user-interfaces/portal/universal-tools/reports)) as a per-user event log — timestamp, event type, device name, and user — filterable by date range, user, and team, and exportable to CSV. Viewing it requires a Manager or Owner role.

## Platform Support

USB Detection is provided by the We360.ai **desktop agent** on Windows, macOS, and Linux. See the [Desktop App](/reference/work-and-time-management/user-interfaces/desktop-app) for the full list of agent capabilities.


# Employee Scoring & Scorecards

We360.ai employee scoring & scorecards — a single, configurable monthly performance score that benchmarks each employee against team and company.

**Employee Scoring** turns the metrics you already track into a single, easy-to-read performance number. Each employee gets a monthly **score from 0 to 100**, and an **Employee Scorecard** that benchmarks them against their team and the whole company.

{% hint style="info" %}
Employee Scoring is an early-access (trial) feature. Availability and options may change — contact your account manager to confirm access.
{% endhint %}

## How the Score Works

The score is calculated **per month** from the metrics you choose to include. Each metric is normalized to a 0–100 scale and then combined as a **weighted average**, so you decide what "good" means for your organization. If no metrics are enabled, no score is produced.

Metrics you can enable and weight:

| Metric               | What it reflects                                                              |
| -------------------- | ----------------------------------------------------------------------------- |
| **Work Units**       | Output — from productive hours and/or task story points, or manually uploaded |
| **Productive Hours** | Productive time against a monthly target                                      |
| **Attendance %**     | Attendance against expected working days                                      |
| **Online Hours**     | Total time online                                                             |
| **Idle Penalty**     | Inverted — more idle time lowers the score                                    |
| **Distance Units**   | Travel distance, for field staff                                              |

## Configuring Scoring

A Tenant Owner configures scoring under **Settings → Scoring**. For each metric you set an **Enable** toggle and a **weight** (0–100), with a running total of the enabled weights.

Global options let you tune how the score is calculated, including:

* **Monthly Work-Unit Benchmark** — the output target a full score is measured against.
* **Story-Point Multiplier** and **Default Story Points** — how task points convert into work units (per-project overrides take precedence).
* **Kilometers per Distance Unit** — for field/travel scoring.
* **Extra Goal-Achievement Multiplier** — rewards hours logged above the daily goal (set to 1.0 to disable).
* **Default Effort Metric** — whether effort is measured by Productive, Online, or Active time.
* **Include calculated values in score** — turn off to use only uploaded work units (a Time-&-Materials style score).

{% hint style="warning" %}
Saving a change **recomputes all past months**, so scores update retroactively to reflect the new configuration.
{% endhint %}

## The Employee Scorecard

Each employee's scorecard appears on the **Scorecard** tab of their [User Details](/reference/work-and-time-management/user-interfaces/portal/universal-tools/user-detail) page. It brings the score to life with:

* A comparison of the employee against **team** and **company** averages (radar chart and table).
* **Monthly Attendance** and **Monthly Goal** summaries.
* **Activity** and **Productivity** trend charts.
* **Top Application** and **Wellness** panels, when those modules are enabled.

Scorecards can be exported for sharing in reviews.

## Getting Accurate Scores

For meaningful productivity-based scoring, set a **Company Goal** under **Settings → Productivity → Goals**. Without one, the score falls back to a default daily target, which may not match your expectations.


# Advanced Analytics

We360.ai Advanced Analytics — premium workforce intelligence: business intelligence, capacity planning, technology usage, and workforce risk.

**Advanced Analytics** is We360.ai's premium intelligence layer. Where the standard portal answers *"what happened?"*, Advanced Analytics is built to answer *"what does it mean, and what should we do?"* — turning the same underlying activity, attendance, and productivity data into executive-level insight for planning and risk decisions.

{% hint style="info" %}
Advanced Analytics is available on the **Advanced Analytics** plan. If these modules aren't visible in your portal, contact your account manager to enable them.
{% endhint %}

## Modules

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-chart-line">:chart-line:</i></td><td><strong>Business Intelligence</strong></td><td>Cross-team analytics and trends for leadership decisions.</td><td><a href="/reference/work-and-time-management/product/advanced-analytics/business-intelligence">Business Intelligence</a></td></tr><tr><td><i class="fa-people-group">:people-group:</i></td><td><strong>Capacity Planning</strong></td><td>Balance workload and utilization across the workforce.</td><td><a href="/reference/work-and-time-management/product/advanced-analytics/capacity-planning">Capacity Planning</a></td></tr><tr><td><i class="fa-microchip">:microchip:</i></td><td><strong>Technology Usage</strong></td><td>Understand how software and tools are used across the org.</td><td><a href="/reference/work-and-time-management/product/advanced-analytics/technology-usage">Technology Usage</a></td></tr><tr><td><i class="fa-triangle-exclamation">:triangle-exclamation:</i></td><td><strong>Workforce Risk Intelligence</strong></td><td>Surface people and teams that need attention early.</td><td><a href="/reference/work-and-time-management/product/advanced-analytics/workforce-risk-intelligence">Workforce Risk Intelligence</a></td></tr></tbody></table>


# Business Intelligence

We360.ai Business Intelligence — cross-team workforce analytics and trends for leadership decision-making.

The **Business Intelligence** module gives leaders a consolidated, organization-wide view of workforce performance. Instead of reading individual reports team by team, you get productivity, activity, and attendance signals rolled up and trended over time so you can spot patterns and compare across the business.

## What It's For

* **See the whole organization at once** — compare productivity and activity across teams, departments, and locations from a single dashboard.
* **Track trends, not just snapshots** — follow how key metrics move over weeks and months to separate real shifts from day-to-day noise.
* **Support decisions with data** — bring objective workforce metrics into planning, staffing, and performance conversations.

## Working With the Data

* Filter and group by team, department, or time period to focus on the slice that matters.
* Use trend views to identify sustained improvements or declines rather than reacting to a single day.
* Combine Business Intelligence with the other Advanced Analytics modules — [Capacity Planning](/reference/work-and-time-management/product/advanced-analytics/capacity-planning), [Technology Usage](/reference/work-and-time-management/product/advanced-analytics/technology-usage), and [Workforce Risk Intelligence](/reference/work-and-time-management/product/advanced-analytics/workforce-risk-intelligence) — for a complete picture.

{% hint style="info" %}
Business Intelligence is part of the [Advanced Analytics](/reference/work-and-time-management/product/advanced-analytics) suite and uses the same underlying data as your standard portal reports — no additional tracking is required.
{% endhint %}


# Capacity Planning

We360.ai Capacity Planning — balance workload and utilization across teams and the workforce.

The **Capacity Planning** module helps you understand how work is distributed across your people and teams so you can balance workload, avoid overload, and make better staffing decisions.

## What It's For

* **Spot imbalance early** — identify who is stretched thin and who has spare capacity before it affects delivery or wellbeing.
* **Plan staffing with confidence** — base hiring, reassignment, and project-allocation decisions on actual utilization rather than assumptions.
* **Protect against burnout** — pair utilization signals with the [Workforce Risk Intelligence](/reference/work-and-time-management/product/advanced-analytics/workforce-risk-intelligence) module to catch sustained overwork.

## Working With the Data

* Review utilization across teams and time periods to see where demand consistently exceeds capacity.
* Compare planned versus actual workload to refine future estimates.
* Use the findings to rebalance assignments or justify additional headcount.

{% hint style="info" %}
Capacity Planning is part of the [Advanced Analytics](/reference/work-and-time-management/product/advanced-analytics) suite.
{% endhint %}


# Technology Usage

We360.ai Technology Usage — understand how software and tools are adopted and used across the organization.

The **Technology Usage** module shows how software applications and tools are actually used across your organization. It turns app-usage data into insight about adoption, licensing, and where technology is helping — or hindering — productivity.

## What It's For

* **Rationalize software spend** — see which paid tools are widely used and which sit idle, so you can right-size licenses and renewals.
* **Measure adoption** — track whether newly rolled-out tools are being adopted across teams.
* **Guide tooling decisions** — compare how different teams rely on different applications to inform standardization.

## Working With the Data

* Break usage down by application, team, or time period.
* Identify under-used licensed software as a candidate for reclaiming or removing.
* Combine with [Business Intelligence](/reference/work-and-time-management/product/advanced-analytics/business-intelligence) to relate tool usage to productivity outcomes.

{% hint style="info" %}
Technology Usage is part of the [Advanced Analytics](/reference/work-and-time-management/product/advanced-analytics) suite and builds on the same app & URL tracking used elsewhere in the portal.
{% endhint %}


# Workforce Risk Intelligence

We360.ai Workforce Risk Intelligence — surface people and teams that need attention before problems escalate.

The **Workforce Risk Intelligence** module highlights people and teams that may need attention — combining workforce signals into risk indicators so managers and HR can act early rather than after the fact.

## What It's For

* **Catch problems early** — surface early signals of overwork, disengagement, or unusual patterns before they turn into attrition or burnout.
* **Prioritize where to look** — focus manager and HR attention on the teams and individuals with the highest indicators rather than reviewing everyone equally.
* **Support wellbeing** — complement the [Wellness](/reference/work-and-time-management/product/workforce-productivity/insights) and [Capacity Planning](/reference/work-and-time-management/product/advanced-analytics/capacity-planning) views with a consolidated risk lens.

## Working With the Data

* Review risk indicators across teams to see where attention is most needed.
* Investigate flagged individuals or teams using the standard portal reports for context.
* Use trends over time to confirm whether interventions are working.

{% hint style="warning" %}
Risk indicators are decision-support signals, not verdicts. Always combine them with context and direct conversations before acting.
{% endhint %}

{% hint style="info" %}
Workforce Risk Intelligence is part of the [Advanced Analytics](/reference/work-and-time-management/product/advanced-analytics) suite.
{% endhint %}


# User Interfaces

We360.ai user interfaces — web portal, desktop agent, and mobile app for employee monitoring and workforce analytics.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-desktop">:desktop:</i></td><td><strong>Desktop App</strong></td><td>Desktop application features and usage.</td><td><a href="/reference/work-and-time-management/user-interfaces/desktop-app">Desktop App</a></td></tr><tr><td><i class="fa-mobile-alt">:mobile-alt:</i></td><td><strong>Mobile App</strong></td><td>Mobile application features and usage.</td><td><a href="/reference/work-and-time-management/user-interfaces/mobile-app">Mobile App</a></td></tr><tr><td><i class="fa-globe">:globe:</i></td><td><strong>Portal</strong></td><td>Web portal features and usage.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal">Portal</a></td></tr><tr><td><i class="fa-browser">:browser:</i></td><td><strong>Chrome Extension</strong></td><td>Chrome Extension features and usage</td><td><a href="/reference/work-and-time-management/user-interfaces/chrome-extension">Chrome Extension</a></td></tr></tbody></table>


# Desktop App

We360.ai desktop agent — stealth and standard modes, screen recording, app tracking, and per-second productivity monitoring.

The We360.ai desktop application is responsible for continuous **per-second tracking** of user productivity across **all major desktop platforms (Windows, macOS, and Linux)**, including activity monitoring, screen recording, and input tracking, ensuring accurate work insights with no gaps.

## Operating Modes

The desktop application supports two distinct operational modes:

{% tabs %}
{% tab title="Standard Mode" %}
A visible mode where users can easily interact with the graphical interface to punch in, take breaks, and punch out.
{% endtab %}

{% tab title="Stealth Mode" %}
A fully functional hidden mode that operates silently in the background without user interaction, seamlessly tracking work according to company policies. All tracking features — activity monitoring, screenshots, idle detection, and input tracking — work identically to Standard Mode.
{% endtab %}
{% endtabs %}

## Operating System & Browser Support

The desktop application is built to provide reliable and native tracking across major computing platforms.

{% columns %}
{% column %}
**Supported Operating Systems**

* Microsoft Windows
* macOS
* Linux
  {% endcolumn %}

{% column %}
**Supported Browsers**

Works out-of-the-box without extensions:

* Google Chrome
* Mozilla Firefox
* Brave
* Vivaldi
* Opera
* Chromium-based browsers

A dedicated **Chrome Extension** is also available for enhanced browser-level URL tracking and productivity insights.
{% endcolumn %}
{% endcolumns %}

## Key Features

1. **Activity Monitoring:** Tracks active window titles and the names of applications currently in use at per-second granularity to categorize productive time with precision.
2. **Keyboard & Mouse Tracking:** Fully functional input activity tracking with **sub-second precision** — counts keystrokes and mouse clicks to accurately determine idle versus active time. We360.ai does **not** perform keylogging; individual characters typed are never recorded.
3. **Screen Capture:** Periodically captures screenshots and records video of the user's screen based on the configured tracking policies.
4. **USB Device Monitoring:** Tracks the usage of plugged-in USB devices for additional security and data loss prevention.
5. **Location Tracking:** The Standard App includes built-in location tracking for desktop endpoints.
6. **Citrix, RDP & VDI Support:** Fully supports virtual desktop environments including Citrix, RDP, and VDI sessions.
7. **Offline Support:** Safely queues and stores all tracked activity locally when the computer loses its internet connection. Activity data is automatically synced once the connection is restored, ensuring zero data loss.
8. **Breaks & Attendance Management:** Supports active punching in and out for attendance tracking. Allows users to manage breaks, accurately reflecting active working periods versus downtime.

## Detailed Data Capture

To provide comprehensive productivity metrics, the application captures several specific data points during tracked sessions:

* **Application Usage:** The active window's title, the name of the application (e.g., Google Chrome, Microsoft Word), and potentially the active URL if interacting with a browser.
* **Interaction activity:** The exact duration a user is actively engaging with an application versus idling, captured with sub-second precision. It logs fully functional keyboard and mouse activity — counting keystrokes and mouse clicks without recording actual characters typed (no keylogging).
* **Device Information:** Tracks external hardware interactions, primarily detecting when USBs or external devices are plugged in or used.
* **Visuals:** A screenshot mapping to specific tracked time intervals (only if permitted by organizational policy).

## macOS Permissions

{% hint style="warning" %}
Due to Apple's strict privacy and security controls, macOS users must manually grant specific permissions to the We360.ai desktop application via System Settings > Privacy & Security. Without extending these permissions, the desktop application will be unable to track correctly and may report zero productivity.
{% endhint %}

* **Screen Recording:** Essential for capturing screenshots or video recordings of the user's active screen.
* **Input Monitoring:** Crucial for monitoring keyboard and mouse activity to correctly determine idleness and compute activity scores.
* **Accessibility:** Required for the application to properly read the active application names, window titles, and automate necessary tracking controls across the system.

<details>

<summary>Advanced Tracking Settings</summary>

Organizations can tailor tracking strictness to match privacy and compliance requirements individually:

* **Screenshot Controls:** Administrators can completely disable screenshots, enable them normally, or apply adjustable **Blur Levels** to obscure sensitive text while still validating presence. Users can also be permitted to download and review their captured screenshots.
* **Media Features:** If required, advanced tracking can be configured to capture Video Screen Recordings, Webcam Photos/Videos, and Audio, depending exclusively on compliance needs.
* **Anomalies and Exclusions:** Specific distracting applications or websites can be ignored completely so they do not get factored into productivity data. The app can also detect attempts to bypass tracking (such as utilizing auto-clickers or "keep awake" scripts).
* **External Interfaces:** External Device Detection can be toggled to monitor potentially unauthorized USB storage access.

</details>

<details>

<summary>Stealth Deployment Capabilities</summary>

For organizations utilizing Stealth Mode, the agent requires zero user interaction and features advanced automation for IT rollouts:

* **Auto-Provisioning:** The application can automatically calculate a new user's username or email prefix by reading the computer's Hostname, Machine ID, or MAC Address.
* **Automated Management:** It can instantly provision and create user accounts dynamically within the We360.ai platform upon first launch.
* **Shift Enforcement:** To respect user time, Stealth Mode can be strictly configured to only enable tracking during predefined shift hours, automatically pausing itself when a shift ends.

</details>

## Browser URL Capture & Markers

{% hint style="info" %}
Applies to **desktop app 4.19 and later**. Desktop app versions earlier than 4.19 emit legacy `chrome:` / `<unknown/browser search>` values in these cases.
{% endhint %}

When the agent cannot read a browser's web address (some internal portals, in-browser PDFs, hardened web apps, or browser extensions), it no longer discards the activity or lumps it under the bare browser name. Instead it captures **distinct, individually categorizable entities**:

* **Special browser pages** are kept individually — `chrome://settings`, `about:preferences`, `edge://flags` — instead of collapsing to a bare `chrome:`.
* **Browser extensions** are captured per-extension as `chrome-extension://<extension-id>`.
* **Local files** opened in the browser are captured by file name as `file:///<filename>` (the folder path is intentionally dropped for privacy).
* **Unreadable web pages** that still have a meaningful window title become a **title marker**, `app-marker://<title>`, so time is attributed to the real thing being viewed rather than to "unknown browser search".
* **Genuine noise** — a blank page or an idle new tab — is still recorded as `<unknown/browser search>`.

Each of these values can be categorized as **Productive**, **Unproductive**, or **Neutral** independently in **Settings → Productivity**, exactly like a normal website.

<details>

<summary>Full capture reference (what gets stored)</summary>

<table data-header-hidden="false" data-header-sticky><thead><tr><th>What the user is on</th><th>Stored as</th></tr></thead><tbody><tr><td>A normal website</td><td><code>https://&#x3C;domain>/</code> (e.g. <code>https://github.com/</code>)</td></tr><tr><td>A browser settings/internal page</td><td><code>chrome://settings</code>, <code>about:preferences</code>, <code>edge://flags</code></td></tr><tr><td>A browser extension</td><td><code>chrome-extension://&#x3C;extension-id></code></td></tr><tr><td>A local file opened in the browser</td><td><code>file:///&#x3C;filename></code></td></tr><tr><td>An internal portal / PDF with no readable URL, but a title</td><td><code>app-marker://&#x3C;title></code></td></tr><tr><td>A blank page or idle new tab</td><td><code>&#x3C;unknown/browser search></code></td></tr><tr><td>A local development server</td><td><code>&#x3C;local service></code></td></tr></tbody></table>

For privacy, query strings and deep paths are always removed, full local file paths are reduced to the file name, and normal websites are stored as `https://<domain>/` only.

</details>


# Mobile App

We360.ai mobile app — field employee tracking, GPS attendance, and remote team management on iOS and Android.

We360.ai allows employees to log in, punch in, and track their productivity via their mobile phones by downloading the we360 app from the Play Store (Android) and the App Store (Apple).

This page highlights mobile application features and usage

{% hint style="info" %}
Initial set-up, configuration, and on-boarding of the application must be done via portal
{% endhint %}

{% hint style="info" %}
App requires Location permission access to "Allow all the time" to accurately track Field

<img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-3e41b916cba254b5d30781a5eeef3d44f6b6a1ab%2Fmobile-app-android-location-permission-allow-all-time.jpg?alt=media" alt="Android location permission screen for the We360.ai mobile app with Allow all the time selected" data-size="original">
{% endhint %}

Once access is granted, app can be opened to see this:

<div align="center"><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-01802f254074fb0b004497557911b49b8ec04471%2Fmobile-app-workspace-domain-welcome-screen.jpg?alt=media" alt="We360.ai mobile app welcome screen with the workspace domain field and Let&#x27;s Begin button" width="188"><figcaption></figcaption></figure></div>

This is the first screen. Users/Employees must enter the Workspace (Domain) as configured for the organization, and click `Let's Begin`, which will lead to the authorization page wherein user email and password must be entered. Alternatively, sign-in via Google account is also supported.

<div align="left"><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7673c39b07db322ff4ac724feaaeeb4ba7267683%2Fmobile-app-portal-sign-in-domain-prompt.jpg?alt=media" alt="Portal sign-in page in the mobile browser asking for the organisation&#x27;s We360.ai subdomain" width="188"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e068bc2b932648d61f4a2ac1427793b18cc89a2b%2Fmobile-app-sign-in-email-password-google.jpg?alt=media" alt="We360.ai sign-in form on mobile with email, password, and Google sign-in options" width="188"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-953261430c3ef05ecf5641b09943d9be67b327ec%2Fmobile-app-link-google-email-verification.jpg?alt=media" alt="Link Google prompt asking the user to verify their email before connecting a Google account" width="188"><figcaption><p>To link with Google, email verification is needed</p></figcaption></figure></div>

Once signed in, following confirmation will appear:

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-56182d78e364901909fb85f04484e619c79cfbbc%2Fmobile-app-authentication-successful-confirmation.jpg?alt=media" alt="Authentication Successful confirmation shown after signing in, prompting a return to the app" width="188"><figcaption></figcaption></figure>

Logging in to the user dashboard will open this:

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-5126830a38f9928dd0a1eb904062b50d0f01df62%2Fmobile-app-home-start-working-punch-in.jpg?alt=media" alt="Mobile app Home tab with the shift timer, Start working punch-in button, and attendance summary"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-3b199e90180bb2297010dd00b3f65bf247d41e4f%2Fmobile-app-home-stop-working-punch-out.jpg?alt=media" alt="Mobile app Home tab with a running shift timer and the Stop working punch-out button"><figcaption></figcaption></figure></div>

Press on `Start Working` to punch in. Similarly, once shift is over, click on `Stop Working` to finish.

By pressing `View Logs`, the Punch Logs will be visible highlighting punch in time, punch out time, and duration of hours worked.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-b5453679ac449e88c9e09067fefd1dfb58b0c011%2Fmobile-app-punch-logs-in-out-duration.jpg?alt=media" alt="Punch Logs screen listing punch-in time, punch-out time, and duration for each work session" width="375"><figcaption></figcaption></figure>

At a glance, the Home tab (Center Bottom) shows Attendance.

Bottom Left is the Profile tab, and Bottom Right is the Navigator.

{% hint style="info" %}
Navigator tab has more features available to user accounts tagged as "Admin" or "Super Admin"
{% endhint %}

### Profile

Displays employee information as entered in portal and allows Sign Out.

<div align="left"><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-619b90d36f73be58c77906a45b6a3ee35d3361d8%2Fmobile-app-profile-employee-details-top.jpg?alt=media" alt="Profile tab showing the employee&#x27;s organisation, company domain, team, designation, and joining date" width="188"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-1c5ad969d5509618cdf5b24b5db620cb1635f7c4%2Fmobile-app-profile-sign-out-button.jpg?alt=media" alt="Profile tab scrolled to shift, gender, mobile number, email, and the Sign out button with app version" width="188"><figcaption></figcaption></figure></div>

### Home

This tab shows Attendance, Productivity, Activity, and Overall Wellness at a glance.

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-f07e91a041d840555fd4a1a680bce43c12b7291a%2Fmobile-app-home-attendance-productivity-cards.jpg?alt=media" alt="Home tab with the date strip, team attendance donut chart, and productive percentage bar"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-fc60ca162a4b6071030bd053b415f6209ca6a6fd%2Fmobile-app-home-productive-time-breakdown.jpg?alt=media" alt="Home tab Productive card breaking down productive, unproductive, and neutral time with averages"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-fecf42213ca3b9347eefe6dc25fa15ee03c0bb86%2Fmobile-app-home-activity-overview-card.jpg?alt=media" alt="Home tab Activity Overview card showing active time, idle time, and total online time"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-ecdc86d12b805b577a41286e83c70623cd837b19%2Fmobile-app-home-overall-wellness-card.jpg?alt=media" alt="Home tab Overall Wellness card with underutilized, healthy, and overworked employee counts"><figcaption></figcaption></figure></div>

**Attendance:** Number of days/shifts punched in

**Productivity:** Time on computer spent on apps marked "Productive"

**Activity:** Time on computer spent actively via monitoring keystrokes, mouse movements, etc.

**Wellness:** Suggests whether user is underutilized, properly utilized, or overburdened by tasks based on set parameters.

{% hint style="info" %}
Productivity, Activity, and Wellness are tracked based on computer usage. Phone apps are NOT tracked, except for Location data.
{% endhint %}

### Navigator Tab

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-2535faa23b3f3a0eee2a22322b9d62643dc2aabe%2Fmobile-app-navigator-tab-feature-menu.jpg?alt=media" alt="Navigator tab listing Attendance, Livestream, Activity, Productivity, Wellness, Screenshots, Alerts, and TimeSheet" width="375"><figcaption></figcaption></figure>

This tab allows user to view Attendance, Livestream, Activity, Productivity, Wellness, Screenshots, Alerts, TimeSheet, Projects.

{% hint style="info" %}
Viewing details of other employees requires "Admin" or "Super-Admin" role
{% endhint %}

#### Attendance:

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-04019a4acbb9079bb9fe194ab145e7be3fe8ccf2%2Fmobile-app-attendance-daily-kpi-cards.jpg?alt=media" alt="Attendance screen with daily KPI cards for attendance rate, late arrivals, break time, and working time"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-8315083baba8395f1b8165bb27b16f0fbf4fa65f%2Fmobile-app-attendance-present-absent-donut.jpg?alt=media" alt="Attendance donut chart of present versus absent employees with on-time and late arrival counts"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-6e01554b3bc9638164e087702ffdeaaa41cfc619%2Fmobile-app-attendance-trends-last-7-days.jpg?alt=media" alt="Attendance Trends bar chart for the last 7 days with a View Details button"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-8948e1ec0408a8a73583b914e775c72afd331741%2Fmobile-app-my-attendance-monthly-calendar.jpg?alt=media" alt="My Attendance calendar view marking present and absent days with total punch hours for the month"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d660ed048960f41445e81364c8f95aeb8f6566fd%2Fmobile-app-team-attendance-punch-list.jpg?alt=media" alt="Team Attendance list showing each employee&#x27;s punch-in time or absent status for the selected day"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-1039d7b4d1a87015a6169a0ae8a26524b1fd1179%2Fmobile-app-team-attendance-filter-sheet.jpg?alt=media" alt="Attendance filter sheet to narrow the team list by all, present, or absent users and by team"><figcaption></figcaption></figure></div>

Admin access allows seeing the attendance of entire team, as well as overall attendance of team, late arrivals, working and break times, and 7 days of attendance trends. Downloading the report can be done via portal.

There's also tabs to check individual and team attendance as well as when in punched in and out. A filter allows Admin to quickly see which employees are present and absent, and sort by Team.

#### Activity:

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-261413cc0cfc32d480b7d217950a40f527b1b5bf%2Fmobile-app-activity-detail-user-percentages.jpg?alt=media" alt="Activity Detail table listing each user&#x27;s activity percentage for the selected date"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-45c922d7949f24d1b614d2f25341f23040b64279%2Fmobile-app-activity-overview-active-idle.jpg?alt=media" alt="Activity screen overview with active time, idle time, and total and average online time"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-326159b3d802a3bf072f3cc6f99052e9cbe649af%2Fmobile-app-activity-trend-last-7-days.jpg?alt=media" alt="Activity Trend chart of active versus idle time over the last 7 days with total active time"><figcaption></figcaption></figure></div>

An overview of employee Activity and trends (7 days) can be seen.

#### Productivity:

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-1d2dd11ff2fef48605ca926d8ce2a61c4ea29bb5%2Fmobile-app-productivity-overview-breakdown.jpg?alt=media" alt="Productivity screen showing productive, unproductive, and neutral time with average productive time"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-f7ed7d2a78b50ed54868be41ad6c6131eb665d28%2Fmobile-app-productivity-trend-last-7-days.jpg?alt=media" alt="Productivity Trend chart for the last 7 days with totals for productive, unproductive, and neutral time"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-b65b5acf201e90587da3e279a9da34ec299041d2%2Fmobile-app-productivity-detail-user-percentages.jpg?alt=media" alt="Productivity Detail table listing each user&#x27;s productivity percentage for the selected date"><figcaption></figcaption></figure></div>

As with Attendance, Average team productive time, productivity trends (7 days) and details for each employee can be checked.

#### Wellness:

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-53454e1bee1bb225ce92010d00c40f5e7665d055%2Fmobile-app-wellness-overview-employee-categories.jpg?alt=media" alt="Wellness screen with counts of underutilized, healthy, and overworked employees and a trend chart"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-9cb501b27a8b06b80292e8dc47c72d96932a0ffa%2Fmobile-app-wellness-trend-chart.jpg?alt=media" alt="Wellness Trend chart plotting under-utilized, healthy, and overburdened employees by day"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-773f1936f490751c46dbb3b700b044d08bd5b2d3%2Fmobile-app-wellness-detail-healthy-percentages.jpg?alt=media" alt="Wellness Detail table listing each user&#x27;s healthy percentage for the selected month"><figcaption></figcaption></figure></div>

Similar to Attendance and Productivity, overall team Wellness, and Wellness trends (7 days) and Individual Wellness % can be viewed.

#### Livestream:

Admins can access the operations of what other employees are doing on their computers.

This feature **does not track mobile** phone usage.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-bec13581e47de9a2274a193b19fd93a4b386a23d%2Fmobile-app-livestream-active-app-monitoring.jpg?alt=media" alt="Livestream screen showing which application and window each online employee is currently using" width="375"><figcaption></figcaption></figure>

#### Screenshots

Admins can see what users are doing on their computers and track them via regular screenshots taken at 5 minute intervals. The screenshots also record apps visited in the duration between the screenshots.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-0cb35903fa38567e00519b131231152d8f361fb7%2Fmobile-app-screenshots-user-list.jpg?alt=media" alt="Screenshots screen listing tracked users to open their captured desktop screenshots" width="375"><figcaption></figcaption></figure>

{% hint style="info" %}
Screenshots deleted in the Settings menu of the Web Portal
{% endhint %}

#### Timesheet

TimeSheet is a tool that allows tracking of time outside of punch in/ punch out. The mobile app features `Weekly View` and `History`. There is also an option to `+ Add Time Entry` to manually input hours worked. Select the date, add start time and end time in HH:MM format and click `Add`

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-21521275cab9f9371bd5dc51b9a5b0bbdeb41d3f%2Fmobile-app-timesheet-history-empty-state.jpg?alt=media" alt="TimeSheet History tab with no records available yet"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-843fe787ed50accea463e467721d50fc1a5a756b%2Fmobile-app-timesheet-weekly-view-add-entry.jpg?alt=media" alt="TimeSheet Weekly View listing each day of the current week with the Add Time Entry button"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-8fe55567a54aea2b202508c2a4120e5507c1f76e%2Fmobile-app-timesheet-add-time-entry-form.jpg?alt=media" alt="Add Time Entry sheet to pick a date, describe the work, and set start and end time or duration"><figcaption></figcaption></figure></div>

#### Projects:

Projects can be viewed or added. To add a project, click on `+ New` and fill in the relevant details as shown in the column that appears and click `Add Project`

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e3e5f7e9a181a53e652339962eb0dcd8249f8a5e%2Fmobile-app-projects-list-active-filter.jpg?alt=media" alt="Projects screen listing active projects with search, status filter, My Tasks, and a New button"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-2390ff4dbf254a81cb8c19c23a0e58b37fb91d65%2Fmobile-app-create-project-form.jpg?alt=media" alt="Create Project form with project name, code, description, owner, and status fields"><figcaption></figcaption></figure></div>


# Chrome Extension

This page covers the Chrome Extension for the we360 app

The We360.ai **Chrome Extension** is a lightweight, browser-based tracking client. It is ideal for employees who work primarily inside the browser — or on devices where installing the full desktop agent isn't practical — and can be used **on its own**, without the desktop app.

The extension shares the same tracking policies as the desktop agent, so what it captures (screenshots, screen recording, idle detection, domain blocking) is governed by the **same** organization settings you configure in the portal.

{% hint style="info" %}
The extension and the desktop app are governed by one shared tracking policy. Anything you enable or disable in **Settings → Compliance & Security** and **Settings → Productivity** applies to both.
{% endhint %}

## Signing In

The extension signs in against your organization's workspace, just like the portal and desktop app.

{% stepper %}
{% step %}

### Install the extension

Add the We360.ai extension from the Chrome Web Store (or your organization's managed-extension rollout) and pin it to the toolbar.
{% endstep %}

{% step %}

### Enter your workspace

Click the extension icon and enter your **Workspace** name. This routes you to your organization's sign-in page.
{% endstep %}

{% step %}

### Log in

Enter your **Email** and **Password** (or continue with your organization's single sign-on). Once authenticated, the extension is ready to track.
{% endstep %}
{% endstepper %}

## Key Features

1. **Attendance from the browser:** Punch in, punch out, and manage breaks directly from the extension popup — no separate app required.
2. **Activity tracking:** Records the active tab's website and page title, along with keyboard and mouse activity, to measure active versus idle time. Individual keystrokes are **never** recorded (no keylogging).
3. **Screen capture:** Periodically captures screenshots of the visible tab when screenshots are enabled in your organization's policy.
4. **Screen recording:** Captures screen recordings when recording is enabled in your organization's policy.
5. **Live view:** Supports on-demand live streaming of the employee's screen to authorized managers in the portal.
6. **Idle detection:** Detects inactivity and can automatically punch the employee out after a configured idle period.
7. **Website blocking:** Enforces your organization's blocked-domain list — a restricted site is closed or replaced with a policy notice.
8. **Projects & tasks:** Lets employees select the project or task they are working on so time is attributed correctly.

## When to Use the Extension vs. the Desktop App

{% columns %}
{% column %}

### Chrome Extension

* Best for browser-first roles and quick rollouts.
* No installation of a desktop application required.
* Captures browser activity, attendance, and screen data for the browser.
  {% endcolumn %}

{% column %}

### Desktop App

* Best for full-device visibility across all applications.
* Tracks every desktop application, not just the browser.
* Adds USB monitoring, device/location tracking, and virtual-desktop (Citrix/RDP/VDI) support.
  {% endcolumn %}
  {% endcolumns %}

{% hint style="info" %}
For deep, system-wide monitoring, deploy the [Desktop App](/reference/work-and-time-management/user-interfaces/desktop-app). Many organizations use the extension for browser-heavy teams and the desktop agent everywhere else.
{% endhint %}

{% hint style="info" %}
This extension is an alternative for users to access features without downloading the application onto their computers.

Initializing and configuration must be done via web portal for assigning Admin role, allotting teams, etc.
{% endhint %}

## Getting Started

It's super simple for users to add the we360 chrome extension:

* Click [here ](https://chromewebstore.google.com/detail/we360ai-workforce-product/eainhghihghonimoemjhiimpkfejkgbd)to access the extension on the Chrome Web Store
* Alternatively, head over to the [Chrome Web Store](https://chromewebstore.google.com/) and search for `We360.ai Workforce Productivity Analytics` .

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-6d92b50a925df0d8ec9f41c113e81a827deeb5cd%2Fchrome-extension-web-store-listing.png?alt=media" alt="We360.ai Workforce Productivity Analytics listing on the Chrome Web Store with the Add to Chrome button"><figcaption></figcaption></figure>

* Click on `Add to Chrome`
* This will open up the following pop up box:

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7932fd3247f84fcdbf99dfaa002c84e52299757e%2Fchrome-extension-add-extension-permissions-prompt.png?alt=media" alt="Chrome prompt listing the permissions the We360.ai extension requests, with Add extension and Cancel buttons"><figcaption></figcaption></figure>

* Click on `Add extension`
* This will add the extension, and display this Thank You page.

  <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-c18dcb8d283bebdcf3dace8f728008298c878767%2Fchrome-extension-install-thank-you-page.png?alt=media" alt="Thank you page shown after installing the We360.ai Chrome extension, pointing to the toolbar icon to get started"><figcaption></figcaption></figure>
* Give the extension permissions required:

<div align="center"><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7f0876e7a41b3b16c5f8e92784dbb023cb404869%2Fchrome-extension-site-access-requested.png?alt=media" alt="Chrome Extensions panel showing the We360.ai extension requesting access to the current site"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-bd261814b89141b21b9194345a4ffaeaa5ce3985%2Fchrome-extension-toolbar-options-menu.png?alt=media" alt="Chrome toolbar menu for the We360.ai extension with site data access, manage extension and permissions options"><figcaption></figcaption></figure></div>

* Now you're ready to sign in.

## Signing in

* Enter the Workspace/Domain name assigned to your organization

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-9e52a6e2635b5cc1ab865f0801234f4a5ab8689e%2Fchrome-extension-workspace-domain-sign-in.png?alt=media" alt="We360.ai Chrome extension sign-in screen asking for the organization workspace or domain name"><figcaption></figcaption></figure>

* Enter your email ID and password to sign into your account. Once signed it, you'll see an authentication complete prompt as so:

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-4f1549e3e29b11be0e56cfabcad7638adb9f1254%2Fchrome-extension-authentication-complete.png?alt=media" alt="Authentication complete confirmation shown after signing in to the We360.ai Chrome extension" width="331"><figcaption></figcaption></figure>

### Punch In/Out

Once logged in, the extension will be available to use to punch in, take a break, and punch out.

<div><figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-eed40086b54dc8add61cb3cb83cc940eddf23d39%2Fchrome-extension-attendance-punch-in-button.png?alt=media" alt="Chrome extension Attendance tab showing current working time and the Punch In button"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-ca77fc5128422c0c6125eb41f869849985b5d308%2Fchrome-extension-select-break-type.png?alt=media" alt="Select Break dialog in the Chrome extension listing lunch and tea break options with durations"><figcaption></figcaption></figure> <figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-4e13ac9e1a6111645481d07112bb6e50de1d1432%2Fchrome-extension-punch-out-take-break.png?alt=media" alt="Chrome extension Attendance tab after punching in, with the Take Break link and Punch Out button"><figcaption></figcaption></figure></div>

The `Take Break` option is visible in grey above the Punch Out button.

{% hint style="info" %}
If user is already punched in via another instance of the app (Mobile App or Computer Application), then the following prompt will appear:

<img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-dcb1985fbc16a04276947de712e883cda0e9b936%2Fchrome-extension-already-punched-in-prompt.png?alt=media" alt="Prompt warning that the user is already punched in on another device and asking whether to punch out there" data-size="original">
{% endhint %}

### Tasks/Project

The extension also allows the user to track their tasks with a timer.

In the extension, switch from Attendance to My Task:

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d78cc42f64e4c8c60d7176b64e157cd48bdf40f8%2Fchrome-extension-my-task-select-project.png?alt=media" alt="Chrome extension My Task tab with project and task selectors and a timer ready to track"><figcaption></figcaption></figure>

Then, select the project you're working on, and the task within that project. Users can search for an existing task by name, or also create a New Task on selected project.

{% hint style="info" %}
Projects and Tasks must be defined previously via the web portal.
{% endhint %}

Once selected, you can start the in-built timer and get started on your work.

When changing tasks, you can stop the time tracker.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e51d42665173d11e47944ce09f546866f8ebdbb9%2Fchrome-extension-task-timer-running.png?alt=media" alt="Chrome extension My Task tab tracking a selected task with the timer running and a stop button"><figcaption></figcaption></figure>

{% hint style="info" %}
Clicking on `More Detail >>` will redirect to the task selected, otherwise it opens the Projects tab in the portal.
{% endhint %}

### Other Features

Pressing the button <img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7ce341b267ce7f0aa19e1176e47c20c22f3e4280%2Fimage.png?alt=media" alt="Info button icon" data-size="line"> button allows the options of toggling Auto Punch-In ON/OFF, as well as checking date & time of last sync, and an option to manually sync to current time. The prompt also displays version of extension being used. Make sure to use the latest version for the most updated features & support.

![Chrome extension workspace panel showing the Auto Punch-In toggle, last sync time and extension version](https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-6dd081668c11ebb95ee5cd43ab00614aa3f82e4e%2Fchrome-extension-workspace-auto-punch-in-last-sync.png?alt=media)

The Domain name on top left is a hyperlink that, when clicked, redirects the user to the Projects Dashboard in the web portal.

The <img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7931acbb33f0d6512c2f5dae8aa7d81cd44a0059%2Fchrome-extension-sign-out-icon.png?alt=media" alt="Sign out icon in the We360.ai Chrome extension header, used to log out of the extension" data-size="line"> button logs the user out.


# Portal

We360.ai web portal — admin dashboard for workforce analytics, productivity tracking, and remote team management.

The We360.ai Web Portal is the primary administrative interface for managers and team leaders. It offers a comprehensive view of organizational productivity, project tracking, and employee wellness.

The portal's navigation is divided into distinct thematic "Suites" and a comprehensive Settings center.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-chart-pie">:chart-pie:</i></td><td><strong>Productivity Suite</strong></td><td>Dashboards, real-time monitoring, analytics, and supplemental tracking.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/productivity-suite">Productivity Suite</a></td></tr><tr><td><i class="fa-briefcase">:briefcase:</i></td><td><strong>Project Suite</strong></td><td>Project management, timesheets, and integrated notebook.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/project-suite">Project Suite</a></td></tr><tr><td><i class="fa-user-clock">:user-clock:</i></td><td><strong>HR Suite</strong></td><td>Attendance tracking and leave management.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/hr-suite">HR Suite</a></td></tr><tr><td><i class="fa-wrench">:wrench:</i></td><td><strong>Universal Tools</strong></td><td>Reports, integrations, alerts, and user detail views.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/universal-tools">Universal Tools</a></td></tr><tr><td><i class="fa-gear">:gear:</i></td><td><strong>Settings Center</strong></td><td>Organization, billing, user management, productivity rules, and compliance.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center">Settings Center</a></td></tr></tbody></table>


# Productivity Suite

We360.ai Productivity Suite — employee time tracking analytics, app monitoring, and workforce productivity insights.

The Productivity Suite provides insights into how employees are spending their time and using company resources. It is the core monitoring hub of We360.ai.

## Dashboard

The central hub providing an immediate overview of team performance, active users, and high-level productivity metrics.

## Real Time

Active monitoring of your workforce.

* **Livestream**: Real-time viewing of active employee screens for immediate auditing.
* **Field**: Location and route mapping for remote or field-based employees.

## Analytics

Deep dives into historical data.

* **Timeline**: A visual, chronologically ordered representation of an employee's workday.
* **Activity**: Granular views into input volume (keyboard/mouse activity) to gauge active engagement.
* **Productivity**: Analysis of time spent, categorized by productive, unproductive, or neutral activities based on company rules.
* **Goals**: Target tracking for individuals and teams to align daily activities with broader objectives.
* **Screenshots**: Review periodic screen captures linked to the timeline for enhanced context.
* **Apps & URLs**: Comprehensive reporting on which software tools and websites are being utilized.
* **Wellness**: Metrics and insights dedicated to employee well-being, helping to identify potential burnout.

## Supplemental Tracking

* **Manual Time**: A utility allowing users to log working hours that were not captured automatically.
* **Devices**: Hardware and software inventory tracking for connected endpoint devices.
* **USB Detection**: Logging and alerts for external USB devices connected to monitored endpoints.

***

## In This Section

<table data-view="cards"><thead><tr><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><strong>Dashboard</strong></td><td>Overview of team performance and high-level productivity metrics.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/productivity-suite/dashboard">Dashboard</a></td></tr><tr><td><strong>Real-Time</strong></td><td>Livestream and field monitoring of your workforce.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/productivity-suite/real-time">Real-Time</a></td></tr><tr><td><strong>Analytics</strong></td><td>Timeline, activity, productivity, goals, screenshots, and wellness insights.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/productivity-suite/analytics">Analytics</a></td></tr><tr><td><strong>Supplemental Tracking</strong></td><td>Manual time, devices, and USB detection.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/productivity-suite/supplemental-tracking">Supplemental Tracking</a></td></tr></tbody></table>


# Dashboard

We360.ai dashboard — real-time workforce analytics overview with productivity tracking and team performance metrics.

The **Dashboard** is the first screen you see when logging into the We360.ai portal. Designed specifically to provide an immediate summary of your workforce, the Dashboard synthesizes real-time metrics into actionable insights by pulling data from across the Productivity, HR, and Project suites.

As a manager, the dashboard allows you to answer the critical daily questions: *Who is working today? Are we tracking towards our goals? Who needs assistance?*

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-aa97beddf2b7bbd78119ea101a9cc7d988edadeb%2Fportal-dashboard-default.png?alt=media" alt="We360.ai Dashboard default view"><figcaption><p>The Dashboard provides an at-a-glance summary of workforce performance.</p></figcaption></figure>

## Global Filters & Reporting

Before analyzing the individual widgets, it's important to understand the global filters applied to the dashboard.

* **Date Range Selector**: The entire dashboard (with the exception of the "Today's Attendance" widget) dynamically recalibrates based on the selected date range. The default date range is **Last 7 Days**. You can view yesterday's performance, last week's trends, or a custom monthly view. Note that the data retention period available depends on your license agreement.
* **Organizational Hierarchy Filters**: You can filter the dashboard to display data for the entire organization, drill down into specific departments/teams (e.g., only viewing the "Sales" team), or even isolate a specific user's performance roll-up. The Teams filter supports **hierarchical team selection** with convenient Select All and Clear options.
* **Pin Filter**: The Pin Filter feature lets you save your current filter selections across page navigation, so you don't have to re-apply filters each time you switch between sections.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-84cda33ff72d15f2196feec3b00b0e2d39c64c41%2Fportal-dashboard-am-team.png?alt=media" alt="Dashboard filtered by team"><figcaption><p>Dashboard filtered to display a specific team's performance data.</p></figcaption></figure>

* **Exporting**: The Dashboard view can be exported directly to a consolidated PDF report for executive circulation.

***

## Core Dashboard Widgets

The dashboard consists of **7 main widgets** that aggregate your workforce data into visual charts and lists.

### 1. Today's Attendance

This widget provides an immediate snapshot of the current day's workforce availability.

* **Donut Chart Visualization**: It displays a donut chart with the raw count of employees who are currently marked as "Present" versus those marked "Absent", along with a breakdown of **on-time vs late arrivals**.
* **Static Context**: Note that this specific widget permanently displays *today's* real-time data and is **not** affected by the global date range filter.
* Clicking this widget redirects you immediately to the detailed Attendance logs.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7435c492d6b94b10330d5218eb9d17bfe97241e4%2Fwidget-dashboard-todays-attendance.png?alt=media" alt="Today&#x27;s Attendance donut chart"><figcaption><p>Today's Attendance widget showing present vs absent employee count.</p></figcaption></figure>

### 2. Attendance Trends

While the previous widget shows today's snapshot, the Attendance Trends widget provides a historical view of presence versus absence over your selected date range (e.g., identifying a trend of high absenteeism on Fridays).

* **Multi-graph Visualization**: This widget combines a **grouped bar graph** (present vs absent employee counts on the primary Y axis) with **line graph overlays** for attendance percentage (0--100% on a secondary Y axis) and average working time (in hours on a third Y axis). This layered view lets you correlate headcount trends with time-based metrics in a single chart.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-113be2c35375ebf261d6397600b39643c8f5c136%2Fwidget-dashboard-attendance-trend.png?alt=media" alt="Attendance Trend chart"><figcaption><p>Attendance Trends widget showing present/absent counts over time.</p></figcaption></figure>

### 3. Goals Achievement Outliers

If your organization utilizes the Goals feature (setting targets like "6 hours of productive time daily"), this widget highlights the adherence to those targets.

* It visually separates employees or teams into **top achievers** and those who have **missed goals** within the filtered date range.

### 4. Leaderboards: Activity & Productivity

These modular lists act as the primary operational indicators for managers to identify high performers or instances of workflow blockage.

* **Productivity Outliers (Most/Least Productive Teams)**: Ranks teams based on their highest aggregate percentage of "Productive Time" (time spent on approved applications and URLs) with **progress bars** for visual comparison. Up to three teams are displayed in decreasing order of productivity. If only one team is selected in the Teams filter, only that team is shown. It distinctly highlights the bottom performers to allow managers to intervene and remove operational blockers.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-754b079b6949ee14de813942b7d2b962db39bd95%2Fwidget-dashboard-top3-productive.png?alt=media" alt="Top 3 Productive Teams"><figcaption><p>Productivity leaderboard highlighting the top 3 most productive teams.</p></figcaption></figure>

* **Activity Outliers (Most/Least Active Teams)**: Ranks teams based strictly on their physical input volume (Keystrokes/Mouse clicks per minute), serving as a raw indicator of digital engagement separate from *what* they are doing. Up to three teams are shown, arranged in decreasing order of activity percentage. Also displayed with progress bars.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-502f34facbd6e5ed83ce54e2275cdfb07a379f5c%2Fwidget-dashboard-top3-active.png?alt=media" alt="Top 3 Active Teams"><figcaption><p>Activity leaderboard highlighting the top 3 most active teams.</p></figcaption></figure>

### 5. Trend Analysis Graphs (Activity & Productivity)

These large, overarching line graphs visualize the continuous ebb and flow of your workforce.

* **Activity Trend**: A **line chart** displaying the fluctuating trend of **active vs idle time** (in hours) over the filtered date range, with dates on the X axis. Hovering on the graph displays the active and idle time breakdown for each individual day. This helps you identify the most engaging hours or days of the week.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-b1069f1c1f5b3f704d9658593edf914f9919c50a%2Fwidget-dashboard-activity-trend.png?alt=media" alt="Activity Trend line chart"><figcaption><p>Activity Trend showing active vs idle time over the selected period.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-bf8f6168d6a7e449324b9232b59e32b2801afb61%2Fwidget-dashboard-activity-trend-hover.gif?alt=media" alt="Activity Trend hover interaction"><figcaption><p>Hovering on the Activity Trend reveals the daily active/idle time breakdown.</p></figcaption></figure>

* **Productivity Trend**: A **line chart** providing a visual breakdown of time categorization over the selected date range, with dates on the X axis and time (in hours) on the Y axis. It charts the distinct trend lines for **Productive**, **Unproductive**, and **Neutral** time. Hovering on the graph displays the productive, unproductive, and neutral time detail for each day. This allows you to easily spot anomalies (e.g., a massive spike in "Unproductive" time on a specific date).

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-cd51163c29a70161a9fb90dd1115e404e67a13b1%2Fwidget-dashboard-productivity-trend.png?alt=media" alt="Productivity Trend line chart"><figcaption><p>Productivity Trend charting Productive, Unproductive, and Neutral time.</p></figcaption></figure>


# Real-Time

We360.ai real-time monitoring — live employee screen streaming, field tracking, and active workforce visibility.

The **Real Time** section of the Productivity Suite is dedicated to managers who need immediate, live visibility into active workstreams or field operations.

## Livestream

The Livestream feature provides synchronous, real-time viewing of user desktops currently tracked by the We360.ai Desktop Agent. This feature utilizes WebSocket connections to ensure that as an employee switches applications or stops typing, the portal updates instantly.

* **View Modes**: The Livestream interface can be toggled between two primary visualization modes:
  * **Grid View**: A high-density mosaic displaying a card for each user in the filtered team and user selections. This is ideal for quickly scanning an entire active department. Each card for an **online** user displays: the user's name, email address, current application or URL in use (including the page or tab title), and the time elapsed since the current status started (e.g., "10 minutes ago"). If the user is on break, the card displays "On Break" along with the elapsed break time. **Offline** users are displayed as greyed-out cards with an airplane mode icon.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-953aecb2a20f1784cfc054a5c4674a2016f42093%2Fportal-livestream-grid.png?alt=media" alt="Livestream Grid View"><figcaption><p>Livestream Grid View showing a mosaic of active employee screens.</p></figcaption></figure>

* **List View**: A traditional row-based format where each row corresponds to a filtered user. For online users, each row displays: the user's name, email address, current application or URL with page/tab details, and time elapsed since the current status started. Offline users are shown with an airplane mode icon and the row is greyed out.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-efbec29e6f1253321560e5083239156dc0cd1955%2Fportal-livestream-list.png?alt=media" alt="Livestream List View"><figcaption><p>Livestream List View displaying employee status in a row-based format.</p></figcaption></figure>

{% tabs %}
{% tab title="🟢 Green" %}
All systems and connections are functioning as expected.
{% endtab %}

{% tab title="🟡 Yellow" %}
Potential issue detected — contact the support team.
{% endtab %}

{% tab title="🔴 Red" %}
Connection problem — contact the support team immediately.
{% endtab %}
{% endtabs %}

* **On-Demand Screenshots**: You can view on-demand screenshots for any active user by clicking on their card (Grid View) or row (List View). In Grid View, hovering on a card displays a screenshot icon indicating that a live screenshot can be fetched. This provides real-time insight into each user's work and is a useful tool for evaluating work patterns and ensuring compliance.
* **Activity Indicators**: Instantly see if a user is actively typing, moving their mouse, or if the system has flagged them as "Offline" due to a lack of recent ping data (configurable inactivity threshold).
* **Application Logging**: Below the user's name, the Livestream interface displays the precise name of the application or URL they are *currently* focused on in real time.
* **Instant Warnings**: Depending on compliance settings, if an employee attempts to disable their tracking or if Livestreaming is explicitly disabled for them via privacy settings, an inline notification will alert the manager.

## Field Tracking

Field Tracking is an essential tool for organizations with distributed, remote, or traveling employees utilizing the **We360.ai mobile app** (e.g., Sales Representatives, Field Executives, Service Technicians, Delivery Drivers). The Field module is designed exclusively for **mobile app users only** -- employees use the We360.ai mobile app to punch in and out from the field.

Common use cases include:

* **Geofencing** for office locations
* **Last mile delivery** tracking
* **At-home service delivery** monitoring

{% hint style="warning" %}
The Field module is currently in beta and is available only for mobile devices.
{% endhint %}

* **Employee List & Map**: Admins can see a list of employees with filters. For the first or selected employee, the map displays their **punch-in location** and **current location** (if currently punched in) or their **punch-out location**.
* **Live Locator Map**: A dynamic map (powered by Leaflet/Google Maps) displaying the most recently polled GPS location of active field employees. The map offers two viewing modes:
  * **Filtered View**: Shows only punched-in users with their current locations plotted on the map.
  * **Raw View**: Shows unfiltered location data for all tracked field employees.
* **Route Replay / Travel Paths**: Historical tracking allowing a manager to visualize the travel path a field employee took throughout their shift. Admins can view detailed **travel paths and visit logs** with timestamps for specific checkpoints.
* **Geofence Status**: Information regarding which employees are currently located within defined permissible areas (Geofences) versus those who have drifted out of bounds.
* **Location Tracking Requirement**: GPS/location tracking must remain **enabled on employee devices** for field tracking to function correctly. If location services are disabled, the employee's position cannot be updated.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-215bf4d12eef7781c3f86b6868379368326ea39d%2Fportal-field.png?alt=media" alt="Field Tracking map view"><figcaption><p>Field Tracking showing live GPS locations of field employees on a map.</p></figcaption></figure>


# Analytics

We360.ai analytics — timeline, activity, and productivity tracking with workforce analytics and goal monitoring.

The Analytics hub within the Productivity Suite is where raw tracking data is categorized according to your organizational rules to generate powerful insights.

## Timeline

The **Timeline** acts as the chronological diary of an employee's workday.

<details>

<summary>Timeline Functionality</summary>

* **Daily Representation**: It visually represents continuous blocks of work over a 24-hour horizontal axis.
* **Dual View Modes**: The Timeline can be toggled via a primary switch between two modes:
  * **Activity Mode**: The timeline blocks are colored based purely on input volume (e.g., Active vs. Idle).
  * **Productivity Mode**: The timeline blocks are colored based on the assigned categorization of the software used (e.g., Productive, Unproductive, Neutral).
* **Punch Flags**: Clear visual indicators (colored arrows) show the exact moment of the first "Punch In" and last "Punch Out" of the day.
* **Employee Drawer**: Clicking on any user's timeline opens a detailed side-drawer (`EmployeeTimelineDrawer`) that provides an hour-by-hour breakdown of their precise activities, applications accessed, and power logs.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-f32a474f7cf01aff6cad12a44ca1285a9b2ba03c%2Fwidget-timeline-overview.png?alt=media" alt="Timeline overview with color-coded bars"><figcaption><p>Timeline overview showing employees' workdays as color-coded activity blocks.</p></figcaption></figure>

* **Hourly Detail View**: Clicking on any **1-hour interval** within the timeline opens a detail view showing productivity and activity percentages along with a **minute-by-minute breakdown**. The granularity of the breakdown interval varies from 5 to 30 minutes depending on the screenshot frequency setting configured in Settings. Enterprise-tier customers can configure a higher screenshot frequency.
* **Screenshots**: If enabled, the hour-interval timeline is sub-divided into sections based on the screenshot frequency. For example, if the frequency is set to once every 5 minutes, the hour is divided into 12 sections. Clicking on each section opens the screenshot for that interval along with additional details:
  * **Activity Detail**: Shows the duration of the interval, the number of key presses and mouse clicks recorded.
  * **Application Logs**: Lists the applications accessed during the interval.
  * Admins can **flag** or **download** individual screenshots as needed.
  * If screenshot permission is disabled for a user, clicking on a section reveals only the Application Logs and Activity Detail without a screenshot image.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-4670735d429afbe2cd1bb8a4893609d6b9caf32a%2Fwidget-timeline-detail.png?alt=media" alt="Timeline hourly detail view"><figcaption><p>Timeline detail view showing hourly activity and productivity breakdowns.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-699fe66f1e9b4144fa92a2a8635ce01a53d2d8c5%2Fwidget-timeline-1hr-intervals.gif?alt=media" alt="Timeline 1-hour interval interaction"><figcaption><p>Clicking a 1-hour interval reveals the minute-by-minute breakdown.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d89fb982ab570be0460936f16044b1767f8a243a%2Fwidget-timeline-detail-screenshot.png?alt=media" alt="Timeline screenshot detail"><figcaption><p>Screenshot detail view with application logs and activity metrics.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-c5e87f730c1b4496f2b065fff07dc8bbb4b38c17%2Fportal-timeline.png?alt=media" alt="Timeline view"><figcaption><p>Timeline view showing an employee's workday as color-coded activity blocks.</p></figcaption></figure>

</details>

## Screenshots

The **Screenshots** feature automatically captures screenshots of employees' systems at predefined intervals exclusively during their punched-in hours. Once an employee punches out, screenshots are no longer captured.

<details>

<summary>Screenshots Functionality</summary>

* **Capture Frequency**: The snapshot frequency is adjustable, ranging from 5 minutes to 2 hours. At the minimum interval of 5 minutes, up to 12 snapshots per hour are captured. Screenshot capturing can be disabled for individual employees based on organizational preferences.
* **Screenshot Details**: Each captured screenshot includes a detailed analysis: the application or URL in use, key presses, mouse clicks, and the activity level for the preceding interval.
* **Three Tabs**: The Screenshots feature is organized into three tabs:
  * **All Screenshots**: The primary screenshot dashboard displaying all captured screenshots.
  * **Flagged**: Displays screenshots that have been flagged by any manager or admin.
  * **Flagged by Me**: Shows only the screenshots flagged by the currently logged-in manager or admin.
* **Dashboard Layout**: The interface is split into two sections. The left panel lists employees, allowing you to select a specific user. The right panel displays a grid of screenshot thumbnails for the selected date. Each thumbnail includes a timestamp, activity level indicator, flag button, and download button.
* **Screenshot Detail View**: Clicking any screenshot opens a deeper view showing:
  * Applications and URLs used during the interval, along with their duration.
  * Activity metrics including key presses, mouse clicks, and activity percentage.
  * Zoom functionality for closer examination.
  * Options to download the screenshot or mark it with a flag for future reference.
* **Bulk Download**: You can download all screenshots for a specific date in bulk, or download individual screenshots as needed.

</details>

## Activity (Input Volume)

The **Activity** section moves away from *what* an employee is viewing, and focuses entirely on *how* they are interacting with the device.

<details>

<summary>Activity Metrics</summary>

* **Activity Formula**: Activity % = (Active Time / Online Time) x 100. This metric quantifies how much of an employee's online time is spent with active device input.
* **Input Measurement**: It measures Keystrokes per minute and Mouse clicks/scrolls to establish a baseline of physical engagement.
* **Summary View**: After selecting the team and date range filters, the summary view displays metric cards including the overall activity percentage, the top application and URL used across the organization, and the top app/URL category. Two doughnut graphs are provided: an **Online Time Breakdown** (Active Time vs Idle Time) and an **Activity Breakdown** (grouping users into three brackets: **<50%** active, **51--75%** active, and **76--100%** active). The summary also lists the top 3 most active and top 3 least active teams or users, along with a teamwise activity breakdown bar graph. The summary view can be downloaded as a PDF.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-af9f741a57cef5cb0688b6af26294df0575e1f6c%2Fwidget-activity-metric-cards.png?alt=media" alt="Activity metric cards"><figcaption><p>Activity summary metric cards: Activity %, Top Application, Top URL, and Top Category.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-35ecd06fef449f11d419d5eb4ab3ec9363892747%2Fwidget-activity-online-time-breakdown.gif?alt=media" alt="Online Time Breakdown doughnut"><figcaption><p>Online Time Breakdown doughnut showing Active Time vs Idle Time.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-77af9d2e62d1b2f41c9be295763e65ac74970d6e%2Fwidget-activity-level-breakdown.gif?alt=media" alt="Activity Level Breakdown doughnut"><figcaption><p>Activity Level Breakdown grouping users into activity brackets.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-de0dbf4c2591a4ff378373f31d0b3dadb178e435%2Fwidget-activity-top3-most-active.png?alt=media" alt="Top 3 most active teams"><figcaption><p>Top 3 most active teams ranked by activity percentage.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-3328fcc4edd664809c8cbfbcdcdb764cb39cffb7%2Fwidget-activity-top3-least-active.png?alt=media" alt="Top 3 least active teams"><figcaption><p>Top 3 least active teams for quick identification of low engagement.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d73eee5701b54b09fb811c33ba1972b8d8b2edd9%2Fwidget-activity-teamwise-breakdown.gif?alt=media" alt="Teamwise activity breakdown"><figcaption><p>Teamwise Activity Breakdown comparing active vs idle time per team.</p></figcaption></figure>

* **Detailed View**: The detailed view includes team, user, and date range filters. It displays an **Overall Working Time Trends** graph showing Working Time, Online Time, Offline Time, and Break Time for the selected range. Below that is a **Teamwise Activity Breakdown** graph comparing Active Time and Idle Time per team. A detailed table lists all employees with their Working Time, Online Time, Offline Time, Active Time, Idle Time, Break Time, and Activity Percentage. You can toggle between **total values** and **average values** for the selected period. Both views are available for download as CSV.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-8388333ee331ed3e48370c600cea7827e3012861%2Fwidget-activity-working-time-trends.gif?alt=media" alt="Working Time Trends"><figcaption><p>Overall Working Time Trends graph in the detailed view.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-c127c21467e4854ff612db7930582dd18708b2e5%2Fwidget-activity-detail-table.gif?alt=media" alt="Activity detail table"><figcaption><p>Detailed employee table with activity metrics and toggle for total/average values.</p></figcaption></figure>

* **Team Outliers**: Top and bottom team outliers are displayed with **progress bars** for quick visual comparison.
* **Trend Analysis**: By filtering across a team, managers can spot individuals whose physical input volume has dropped significantly compared to their historical average, which may indicate blockers or disengagement.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-26c57c951019eddcfb7d5f05bde606308036eee2%2Fwidget-activity-trend.gif?alt=media" alt="Activity trend over time"><figcaption><p>Activity trend showing active vs idle time fluctuations over the selected period.</p></figcaption></figure>

</details>

## Productivity

The **Productivity** feature is the categorization engine. Based entirely on the rules configured in the Settings Center (where URLs and Apps are classified), this section provides a breakdown of time spent.

<details>

<summary>Productivity Categorization</summary>

* **Productivity Formula**: Productivity % = (Productive Time / Online Time) x 100. Time is categorized as Productive, Unproductive, or Neutral based on the app/URL category mappings configured in Settings.
* **Productive Time**: Time spent on pre-approved, role-relevant tools.
* **Unproductive Time**: Time spent on categorized non-work-related sites (e.g., social media).
* **Neutral Time**: Time spent in applications not yet classified.
* **Summary View**: The summary view provides four metric cards: overall **Productivity** percentage, the **Top Application** used, the **Top URL** visited, and the **Top Category** contributing to productive time -- all within the selected team(s) and date range. It includes a productivity breakdown pie chart (Productive / Unproductive / Neutral), lists the **Most Productive Teams** (top 3) and **Least Productive Teams** (bottom 3) with their metrics, and a **Teamwise Productivity Breakdown** chart for side-by-side comparison. The summary view can be downloaded as a PDF.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-6cde27f88d723eefa9c85df0ae56f8c9395a2adc%2Fwidget-productivity-metric-cards.png?alt=media" alt="Productivity metric cards"><figcaption><p>Productivity metric cards: Productivity %, Top Application, Top URL, and Top Category.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-53bd798c34b57ca08d96b4181a586a4ae271914e%2Fwidget-productivity-breakdown.gif?alt=media" alt="Productivity breakdown pie chart"><figcaption><p>Productivity Breakdown doughnut showing Productive, Unproductive, and Neutral time.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-f18c6b7ff6376fffdafe996a24d6b62e88f76fed%2Fwidget-productivity-outliers.png?alt=media" alt="Productivity outliers"><figcaption><p>Most and Least Productive Teams with progress bar comparisons.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-61b17292a27bdd9ed355d9d75056fa4d92a95f9e%2Fwidget-productivity-teamwise-breakdown.gif?alt=media" alt="Teamwise Productivity Breakdown"><figcaption><p>Teamwise Productivity Breakdown for side-by-side team comparison.</p></figcaption></figure>

* **Detailed View**: The detailed view offers team, user, and date range filters. It displays a **Working Time Trends** graph breaking down working time into online time and break time, plus an **Overall Productivity Breakdown** graph charting Productive, Unproductive, and Neutral time over the selected period. A detailed employee table lists each employee's working time, online time, productive time, unproductive time, neutral time, break time, and calculated productivity percentage. You can toggle between **total values** and **average values** for the selected period. This view is available for download as CSV.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-044be352c8c93a01fc415992e2feb4f3a240c858%2Fwidget-productivity-working-time-trends.gif?alt=media" alt="Productivity Working Time Trends"><figcaption><p>Working Time Trends in the productivity detailed view.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e9acd7b7e1f5d8ddf2de1a4031f65677d05c48d5%2Fwidget-productivity-trend.gif?alt=media" alt="Productivity trend over time"><figcaption><p>Productivity trend charting Productive, Unproductive, and Neutral time over the period.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-a02f73e3ca365901475302f5986b2182ed0e349e%2Fwidget-productivity-detailed-table.gif?alt=media" alt="Productivity detailed table"><figcaption><p>Detailed employee table with productivity metrics and total/average toggle.</p></figcaption></figure>

* The visual charts help managers understand if the ratio of productive to unproductive time is within acceptable limits for a given role.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-4aa395918bd1206a5fe5e893e5d30acc2041c497%2Fportal-productivity-summary.png?alt=media" alt="Productivity summary"><figcaption><p>Productivity summary breaking down Productive, Unproductive, and Neutral time.</p></figcaption></figure>

</details>

## Goals

**Goals** allow managers to define and track specific, measurable targets.

<details>

<summary>Goal Tracking</summary>

* **Target Definitions**: Goals are set organization-wide for **Active Time** and **Productive Time** targets per day (e.g., "All employees must achieve 6 hours of purely Productive time per 8-hour shift"). Admins configure goals via **Settings > Productivity > Goals tab**.
* **Single or Combined Goals**: You can set either an Active Time goal or a Productive Time goal individually, or set both. When both goals are configured, an employee's goal is considered achieved only when **both** the active time and productive time targets are met. If either target is missed, the overall goal is marked as missed.
* **Maximum Goal Cap**: The maximum hours allowed for a goal depends on the Full Day duration configured in your workplace settings (**Settings > Workplace > Advanced Settings**). For example, if a full day is set to 9 hours, the maximum goal cap is 9 hours.
* **Progress Visibility**: Progress towards these goals is tracked dynamically throughout the day across the dashboard. It is recommended to wait at least one day after setting goals to see analytics reflecting progress.
* **Achievement Status**: Shows the count of employees who have **achieved** vs **missed** their goals within the selected timeframe.
* **Goal Distribution**: Breaks down goal achievement into four brackets: **0-25%**, **25-50%**, **50-75%**, and **>75%**, giving managers a quick view of how goals are distributed across the workforce.
* **Teamwise Goal Comparison**: Compare goal achievement across teams in one view. You can also compare performance against the previous period to identify teams showing improvement and those needing support.
* **Employee List Table**: A detailed table showing individual goal progress for each employee, with columns for **present days**, **goals achieved** (number of days), **online time**, **active time**, **activity vs goal** percentage, **productive time**, and **productivity vs goal** percentage.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-cd0ac47de643ddf7d31cc86f71bb3561e26ece89%2Fportal-goals.png?alt=media" alt="Goals tracking"><figcaption><p>Goals view showing target achievement and missed goals across teams.</p></figcaption></figure>

</details>


# Supplemental Tracking

We360.ai supplemental tracking — device monitoring, employee wellness metrics, and unmonitored time management.

Beyond standard time and application monitoring, the Productivity Suite offers supplemental tools to manage edge cases and hardware context.

## Apps & URLs

A straightforward, exhaustive list of every single application binary and website domain accessed by the team over a given period.

<details>

<summary>Features</summary>

* **Summary and Detailed Tabs**: The Apps & URLs section is organized into two tabs:
  * **Summary Tab**: Provides metric cards showing the top applications used, top URLs accessed, and the top categories for the selected team(s) and date range. It displays a **category utilization chart** showing the complete distribution of time spent across each category (productive, unproductive, or neutral), plus ranked lists of application usage and URL usage in decreasing order. The summary view can be downloaded as a PDF.
  * **Detailed Tab**: Includes team, user, and date range filters. The view is divided into two panels:
    * **Left Panel**: Lists all categories with the total hours of utilization and the number of active users for each category during working hours.
    * **Right Panel**: Clicking any category on the left reveals deeper insights on the right, including an **Application-wise Utilization** chart (with a switcher to view URL usage for the same category) and a **Teamwise Utilization** chart showing how different teams spend time in the selected category. Clicking on any individual application opens three detail tabs: **Logs** (showing project or file activity logs and durations), **Users** (listing all employees and teams that used the application), and **Usage** (a usage graph showing whether the app is classified as productive, unproductive, or neutral across different teams).
* **Shadow IT Discovery**: Quickly identify unauthorized app usage or risky websites.
* **Cumulative Time**: View the total cumulative time spent on a specific domain across the entire organization, helping to justify or cancel software subscriptions.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-2fb8132f6b3dffb0ae76141a932ffb71d2accd98%2Fportal-apps-urls.png?alt=media" alt="Apps and URLs listing"><figcaption><p>Apps &#x26; URLs view showing application and website usage across the organization.</p></figcaption></figure>

</details>

## Wellness (Wellness360)

**Wellness360** analyzes work habits to identify signs of employee fatigue and burnout, ensuring tracking isn't only used for performance, but for employee health.

<details>

<summary>Features</summary>

* **Wellness Categories**: Employees are classified into three wellness states:
  * **Healthy**: Working within expected hours and maintaining a balanced workload.
  * **Overburdened**: Working significantly more than expected hours, indicating potential burnout risk.
  * **Underutilized**: Working significantly less than expected hours, which may indicate disengagement or capacity issues.
* **Summary View**: Displays metric cards showing: the percentage of employees who are Healthy, total Working Time for the selected date (with a comparison to the previous day), the most overburdened employee, and the most underutilized employee. Below the cards, four pie charts provide visual breakdowns: **Overall Wellness** (distribution of Healthy, Overburdened, and Underutilized employees), **Top Healthy** teams with their working hours, **Top Overburdened** teams with their working hours, and **Top Underutilized** teams with their working hours. The summary view uses a single date filter and teams filter, and can be downloaded as a PDF.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7fb79d1932ee4dee7b66822161e3fbaf361f072a%2Fwidget-wellness-metric-cards.png?alt=media" alt="Wellness metric cards"><figcaption><p>Wellness summary metric cards: Healthy %, Working Time, Most Overburdened, and Most Underutilized.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-cad6f9460f499c90be29f06dc4bce6a1763a9072%2Fwidget-wellness-overall.png?alt=media" alt="Overall Wellness donut"><figcaption><p>Overall Wellness donut chart showing Healthy, Overburdened, and Underutilized distribution.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-5d15956498b606b2f4c7c102ca12822b3cfd5f9a%2Fwidget-wellness-top3-healthy.gif?alt=media" alt="Top Healthy teams"><figcaption><p>Top Healthy teams with their working hours breakdown.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-0209549d23cc29de89107a687a2a1e6d5859013b%2Fwidget-wellness-top3-overburdened.png?alt=media" alt="Top Overburdened teams"><figcaption><p>Top Overburdened employees flagged for potential burnout risk.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-cc8be3172799423382c88029689fe6a2dcb3fb03%2Fwidget-wellness-top3-underutilized.png?alt=media" alt="Top Underutilized teams"><figcaption><p>Top Underutilized employees who may need workload rebalancing.</p></figcaption></figure>

* **Team Wise Utilization**: A chart showing the distribution of Healthy, Overburdened, and Underutilized employees **per team**, enabling managers to identify teams with systemic workload imbalances and compare all teams at once.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-f00691c1d8e7c09218e96281c47e17e2b9ad0323%2Fwidget-wellness-teamwise-utilization.png?alt=media" alt="Team Wise Utilization chart"><figcaption><p>Team Wise Utilization comparing wellness distribution across all teams.</p></figcaption></figure>

* **Detailed View**: The detailed view provides team, user, and month filters. It includes a **Wellness Trends** graph displaying the distribution of employees who are Healthy, Overburdened, and Underutilized over time. The detailed employee table lists each employee with the following columns: **Total Present Days**, **Healthy days**, **Overburdened days**, **Underutilized days**, **Health %**, **Overburdened %**, and **Underutilized %**.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-c03b1259dded9b71ad2b1fab4a2fea910df7ac32%2Fwidget-wellness-trends.gif?alt=media" alt="Wellness Trends graph"><figcaption><p>Wellness Trends showing the distribution of wellness states over time.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e355ef08d4f2e20be4cb94da8accab86b36dfc7a%2Fwidget-wellness-detailed-table.gif?alt=media" alt="Wellness detailed table"><figcaption><p>Detailed employee table with wellness metrics per employee.</p></figcaption></figure>

\* \*\*Overwork Flags\*\*: Triggers warnings for employees who consistently work beyond their designated shift hours (e.g., answering emails at midnight). \* \*\*Break Violations\*\*: Highlights users who skip breaks or work continuous stretches without pause, allowing HR to intervene proactively to maintain employee health and compliance with labor laws.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-33dcfc10a940274cf5bd16accc84f92707edf076%2Fportal-wellness.png?alt=media" alt="Wellness360 dashboard"><figcaption><p>Wellness360 identifying overwork patterns and break violations.</p></figcaption></figure>

</details>

## Manual Time

{% hint style="success" %}
**Industry-unique feature:** We360.ai's Manual Time workflow is a capability not found in competing platforms, ensuring no legitimate work goes unrecorded.
{% endhint %}

Sometimes tracking is interrupted, or an employee conducts necessary work away from their monitored device (e.g., an in-person workshop or an extended phone call on a non-monitored, personal line).

<details>

<summary>Features</summary>

* **Request Submissions**: **Manual Time** allows users to retroactively log hours into the system via a formal request form. Entries can only be submitted for **previous dates** (not the current date).
* **Status Flow**: Each manual time entry follows a defined workflow: **Pending -> Approved/Rejected**. Once an entry is approved, it **cannot be edited**. Employees can delete their own entries while they are still in Pending status.
* **Managerial Approval**: These entries are visually distinct from automated tracking and require managerial approval before being added to the final Timesheet or Attendance log. Managers approve entries for employees within their **team hierarchy**. This ensures accuracy without sacrificing accountability.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-084a8cb07c6e1fb24de6ad33121e7c7cef7fb3b3%2Fportal-manualtime.png?alt=media" alt="Manual Time entries list"><figcaption><p>Manual Time log showing submitted time entries and their approval status.</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-75004dffc07a23fc95f2df91e713c9521792c43d%2Fportal-manualtime-modal.png?alt=media" alt="Manual Time request form"><figcaption><p>The Manual Time request form for logging untracked hours.</p></figcaption></figure>

</details>

## Devices & USB Detection

IT Administrators require hardware-level context for the endpoints they are tracking.

<details>

<summary>Features</summary>

* **Device360**: Displays comprehensive metadata about the endpoint device running the agent. The Devices section is organized into three tabs:
  * **PC Tab**: Shows an **online/offline status donut chart**, **platform distribution** (Windows/macOS/Linux), and a detailed device table with columns for MyZen agent version, app type (standard or stealth), OS information, and IP address.
  * **Mobile Tab**: Shows mobile device analytics for employees using the We360.ai mobile app.
  * **Health Status Tab**: Displays device health metrics to help IT teams identify endpoints that may need attention.
* **USB Detection**: A security compliance feature that logs **connect and disconnect events** for USB devices on monitored machines. Important privacy note: USB Detection tracks events only and does **not** track or specify the USB device type (privacy by design). Logged data includes **timestamp, event type, title, user, and email**.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-0c45f3e0da155c132d6a0f734af0672c7e0cf94d%2Fportal-devices.png?alt=media" alt="Device inventory"><figcaption><p>Device360 showing endpoint metadata including OS, hardware IDs, and IP addresses.</p></figcaption></figure>

</details>


# Project Suite

We360.ai Project Suite — project management, task tracking, and timesheet logging for team productivity.

The Project Suite helps teams manage tasks and track time dedicated to specific ongoing initiatives.

## Projects

The core management view for creating and overseeing organizational projects, sub-tasks, and their respective assignees.

## Timesheet

Detailed entries logging hours worked against specific assigned projects or tasks. Provides an overview of billable or trackable hours for project completion.

## Notebook

A built-in utility for taking notes and organizing project-related thoughts directly within the We360.ai portal.

***

## In This Section

<table data-view="cards"><thead><tr><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><strong>Projects</strong></td><td>Create and manage projects, sub-tasks, and assignees.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/project-suite/projects">Projects</a></td></tr><tr><td><strong>Timesheet</strong></td><td>Log and review hours worked against specific projects.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/project-suite/timesheet">Timesheet</a></td></tr><tr><td><strong>Notebook</strong></td><td>Organize project-related notes within the portal.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/project-suite/notebook">Notebook</a></td></tr></tbody></table>


# Projects

We360.ai projects—create, assign, and track team projects with built-in time tracking and budget management.

The central element of the We360.ai Project Suite is the **Projects** dashboard itself, providing a top-down view of all ongoing work and linking time-tracking directly to deliverables.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-f2e7c5144c543a0722d1f58864e65cdc0e1f0e5c%2Fportal-projects.png?alt=media" alt="Projects dashboard showing project list and task management views"><figcaption><p>Projects dashboard with project listing and task management</p></figcaption></figure>

{% hint style="info" %}
This page describes the Project Suite screens and where controls live. For what projects, tasks, statuses, and billing *are* and how they behave, see the [Projects & Tasks reference](https://docs.we360.ai/reference/work-and-time-management/product/work-and-time-management/projects-and-tasks). For step-by-step goals, see [Managing Projects & Time](https://docs.we360.ai/how-to-and-best-practices/managing-projects-and-time).
{% endhint %}

## Dashboard

The project **Dashboard** is the operational landing screen. It combines organization-level project visibility with the signed-in user's own tasks, standups, and timesheet reminders in one place.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-942aacad03f6e15c3be8de2fa8a925c3cdca68fd%2Fproject-dashboard.png?alt=media" alt="Project management dashboard"><figcaption><p>The project management dashboard</p></figcaption></figure>

**KPI summary cards** give a quick read on the user's own workload: total and active projects, active tasks, tasks due today, and hours logged.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-8740782dd1da8c8fe118154be83b85206d467d21%2Fproject-dashboard-kpis.png?alt=media" alt="Personal KPI summary cards"><figcaption><p>Personal KPI summary cards</p></figcaption></figure>

The **Project Overview** area summarizes the active projects the user can access, with visual indicators for scanning several projects at once.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-c216bedc3857e4bf5ae383cadec85c1f93669845%2Fproject-overview.png?alt=media" alt="Project overview across active projects"><figcaption><p>Project overview across active projects</p></figcaption></figure>

## Project Management

At a high level, administrators or project managers define the overarching "Projects."

* **Configuration**: Managers can create new projects, assign a default active status, and dictate which teams or specific individuals are allowed to log time against the project.
* **Custom Fields**: We360.ai supports up to 8 strongly typed "Custom Fields" per project (for example, string, integer, or boolean formats). This lets organizations append specific metadata, such as internal billing codes, priority tags, or external client IDs directly to the project for reporting.
* **Access Control**: Depending on the Role settings, lower-level employees see only the projects explicitly assigned to them, while Tenant Owners maintain a global view.
* **Project Status Filter**: Projects can be filtered by status—**Active** or **Archived**—so managers can keep the dashboard focused on current work while retaining historical project data for reference.

## Project Detail View

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d97d78525670832efbfaa5de68c01386ad5f9617%2Fproject-task-list.png?alt=media" alt="Project detail view with task list"><figcaption><p>A project's detail view and task list</p></figcaption></figure>

Clicking into an individual project opens its detail view, which surfaces the full list of tasks assigned to that project along with cumulative time logged. The task table displays the following columns:

| Column                    | Description                                                           |
| ------------------------- | --------------------------------------------------------------------- |
| **Summary**               | Title of the task (clickable to open details).                        |
| **Status**                | Current progress indicator (for example, TODO, IN PROGRESS, or DONE). |
| **Assignee**              | User responsible for completing the task.                             |
| **Estimate**              | Time estimate to complete the task.                                   |
| **Start Date / Due Date** | Task scheduling details.                                              |
| **Reporter**              | User who created or reported the task.                                |

The table footer displays the total number of tasks within the project, with pagination options for viewing tasks in batches. Search bars allow filtering tasks by summary/keywords or by assigned users. From this view managers can add new tasks, reassign members, and review progress against estimates without leaving the project context.

## Task Management

If a "Project" is the bucket, "Tasks" are the individual drops of work. Large projects are broken down into assignable sub-tasks that act as individual line-items for time tracking.

* **Task Types**: Tasks can be further categorized structurally as an `EPIC` (a large body of work), a standard `TASK`, or a `BUG` (defect resolution).
* **Dual View Modes**: The Task interface can be toggled via a primary switch between two modes:
  * **List Data Table**: A dense, sortable table displaying all tasks, their assignees, due dates, and statuses.
  * **Kanban Board**: A visual drag-and-drop board (for example, To Do → In Progress → Review → Done), so Agile-focused teams can move cards through a workflow pipeline visually.
* **Quick Creation**: The List view features an inline "Quick Add" input field, so managers can add new tasks without opening a separate form for every entry.
* **Add Task Panel**: Creating a new task opens a side panel with structured fields: **Type** (Epic, Task, or Bug), **Summary** (task title, mandatory), **Description** (detailed explanation), **Assignee** (responsible user), and **Start Date / Due Date** (scheduling). Click the Add Task button to save and add the task to the project list.
* **Task Details Drawer**: Clicking any task opens a comprehensive side-drawer detailing the description, assignee history, and a timeline of exactly how many hours have been logged against that specific sub-task. The detail view includes:
  * **Attachments**: Option to upload related files to the task.
  * **Child Issues**: Ability to link or create subtasks within a parent task.
  * **Detail Panel (Sidebar)**: Shows Assignee and Reporter info, time tracking details (Estimate and Time Logged), Start and Due Dates, and Created/Updated timestamps.
  * **Comments**: Collaborate through task-specific discussions.
  * **Status Changes**: Switch between statuses (TODO, IN PROGRESS, or DONE) directly from the detail view.

## My Tasks

**My Tasks** is a personal workspace where users manage their own assigned work: viewing tasks, updating statuses, logging effort, and tracking deadlines across projects.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-ebb4f75df83753efb4a4a009e4a2316a57119159%2Fmy-tasks.png?alt=media" alt="My Tasks workspace"><figcaption><p>The My Tasks workspace</p></figcaption></figure>

Filters narrow the list by status, priority, due date, project, sprint, or tags.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-ecd65508e5e83405a71dac7d64aa1ee273bc91a0%2Fmy-tasks-filters.png?alt=media" alt="Filtering the My Tasks list"><figcaption><p>Filtering the My Tasks list</p></figcaption></figure>

## All Tasks

**All Tasks** widens the view to work across every project the user can access, for monitoring progress, reviewing assignments, and analyzing workload. The same filters apply, with assignee and reviewer added.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e54fbf60082f95c3d7446c23333d253f8fc7b051%2Fall-tasks.png?alt=media" alt="Tasks across all accessible projects"><figcaption><p>Tasks across all accessible projects</p></figcaption></figure>

## Calendar View

Alongside the List and Kanban views, a **Calendar View** places tasks on a timeline for date-based planning. Managers can schedule tasks, adjust timelines, and review upcoming deadlines, and filter the calendar by sprint, status, or assignee. Unscheduled tasks stay visible until a date is added.

## Sprints

Tasks can be grouped into **sprints**—time-boxed cycles with a start and end date. The sprint controls let managers create a sprint, add tasks to it, start it, and complete it; when a sprint is completed, unfinished tasks can carry over to the next one. Task views can be filtered to a single sprint to keep the board focused on the current cycle. For running a sprint end to end, see [Plan and run a sprint](https://docs.we360.ai/how-to-and-best-practices/managing-projects-and-time/plan-and-run-a-sprint).

## Daily Standups

The **Standup** screen gives teams a single place to run a daily check-in without opening each board. From it, the team can review progress across members, add work logs, create or update tasks, change assignees, and add comments. A standup summary can be saved, downloaded as an image or PDF, and shared as a meeting record.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-61e195a3803dbaf015222a88a4724a3cab2f7bd0%2Fproject-standups.png?alt=media" alt="The daily standup screen"><figcaption><p>Running a daily standup from one screen</p></figcaption></figure>

## Access & Roles

Project access is controlled by membership and role. Projects define **Project Owners** and **Project Members**, and **Guests** have view-only access. Permissions can be set at both the organization and project levels.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-05c048e45aa0f731e17c261d83036b746f486134%2Fproject-members.png?alt=media" alt="Managing project members"><figcaption><p>Managing project members</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e002e11dbc466176ada7a026fbe35d5b81c7ee7d%2Fproject-roles.png?alt=media" alt="Role-based access within a project"><figcaption><p>Role-based access within a project</p></figcaption></figure>

## Workflow Automation

The **Workflow** screen lets organizations automate routine project actions such as sprint creation, sprint completion, task movement, and status transitions, keeping process consistent across teams.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7fc93686701afb95ff52001953bb209cedeae1bf%2Fproject-workflows.png?alt=media" alt="Automating project workflows"><figcaption><p>Automating project workflows</p></figcaption></figure>

## Archived Projects

Inactive projects can be archived to hide them from operational views while keeping their tasks and history. A project can also be marked **To Be Deleted** for permanent removal.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-1d89fb0ec4b4652fa76ebed6255efa1feca9c681%2Fproject-archived.png?alt=media" alt="Archived projects remain available for reference"><figcaption><p>Archived projects remain available for reference</p></figcaption></figure>


# Timesheet

We360.ai timesheet — assign employee hours to projects, review budgets, and track billable time automatically.

The **Timesheet** bridges the gap between raw tracked time (from the Productivity Suite) and billable output. While the Desktop Agent automatically records *how long* an employee was at the computer, the Timesheet dictates *what* that time was spent achieving.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-f962e6a91b324b1f65f6370a4893a25b7a9c3931%2Fportal-timesheet.png?alt=media" alt="Timesheet interface showing time allocation to projects"><figcaption><p>Timesheet view for logging and allocating hours to projects</p></figcaption></figure>

## Functionality

<details>

<summary>Logging &#x26; Allocation</summary>

* **Logging Hours**: Employees or managers can assign slices of their tracked time directly to specific Projects and sub-tasks defined in the Projects dashboard.
* **Automated vs. Manual Entry**: Depending on settings, timesheets can either be automatically generated based on the active window titles captured by the tracking agent, or they can require manual input and assignment by the employee at the end of their shift.

</details>

## Standard User Experience

Standard users see two main sections on their Timesheet dashboard:

<details>

<summary>Weekly View</summary>

The Weekly View is where users log their daily work hours. The current week is selected by default, but users can navigate to previous or upcoming weeks.

When filling out a timesheet entry, users provide:

* **What was worked on** -- a short summary describing the task (e.g., "Client meeting," "SEO optimization").
* **Time details** -- three flexible methods:
  * Enter Start Time and End Time; the system calculates Duration automatically.
  * Enter Start Time and Duration; the system fills the End Time automatically.
  * Enter only Duration if exact timings are unknown.
* Multiple entries can be logged in a single day for different tasks.
* **Planned Timesheets**: Users can pre-fill their next week's timesheet in advance if upcoming tasks are already known.

</details>

<details>

<summary>History</summary>

The History section lets users track previously submitted timesheets and check their approval status (Pending, Approved, or Rejected).

</details>

## Submit and Edit Rules

* Users can freely edit timesheet entries **before** submission.
* Once a timesheet is submitted, it is locked and **cannot be edited** by the user.
* To make corrections after submission, a Manager or Admin must **Reopen** the timesheet so the user can revise and resubmit.

## Manager & Admin View

Managers and Admins have two tabs: **My Timesheet** (for their own hours) and **Team's Timesheet** (for reviewing direct reports).

<details>

<summary>Team's Timesheet</summary>

The Team's Timesheet tab is divided into three sections:

* **Pending** -- Submitted timesheets awaiting approval.
* **Approved** -- Finalized timesheets kept for records.
* **Rejected** -- Timesheets sent back with a reason for rejection.

**Available actions** (via the three-dot menu on each row):

* **Approve** -- Accept the timesheet.
* **Reject** -- Send it back with feedback.
* **Reopen** -- Allow the user to edit and resubmit.

**Filters** help locate specific data quickly: filter by User to view a specific employee's timesheets, or by Date Range to access previous weeks.

</details>

<details>

<summary>Review &#x26; Auditing</summary>

* **Timesheet Approval Workflow**: Timesheet entries can be configured to require managerial approval before being finalized for payroll integrations or client invoicing. The full lifecycle — Submit → Pending → Approved/Rejected → Reopen — ensures accountability and accuracy at every stage.
* **Manual Time Workflow**: We360.ai uniquely offers a **Manual Time** workflow where employees can retroactively log untracked hours (e.g., in-person meetings, phone calls on unmonitored devices) via a formal request that requires managerial approval before being added to the timesheet. This ensures no legitimate work time goes unrecorded — a capability not found in competing platforms.
* **Status Tracking**: Managers can quickly filter and view which timesheets are "Pending," "Approved," or "Rejected" (with attached notes detailing why a rejection occurred).
* **Historical Auditing**: Easily look back at past weeks to understand the true time-cost of a delivered project versus the original estimates, enabling more accurate forecasting for future work.

</details>


# Notebook

We360.ai notebook — built-in note-taking tool for documentation within the workforce productivity platform.

Context switching is a major productivity killer. To keep employees focused and within the We360.ai ecosystem, the portal includes a built-in **Notebook** feature designed for rapid documentation.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-076c9b1871374276f794e4de23fced599223e26d%2Fportal-notebook.png?alt=media" alt="Notebook interface with card-based note grid"><figcaption><p>Notebook dashboard with card-based note management</p></figcaption></figure>

## Features

* **Rich Text Editing**: Draft quick thoughts, meeting notes, project specifications, or daily standup logs directly within the portal. The editor utilizes a robust Rich Text editor (Quill.js) allowing for formatting, lists, and embedded content.
* **Card-Based UI**: Notes are displayed in a clean, Pinterest-style grid of cards, making it easy to visually scan for the correct document.
* **Real-time Saving**: The interface supports instant updates, saving changes back to the database as the user types, ensuring data loss is minimized.
* **Organization**: While designed for quick access, notes can be compartmentalized for personal use or shared visibility. (Note: System settings dictate the scope of who can view which notes).


# HR Suite

We360.ai HR Suite — employee attendance management, break tracking, and leave request workflows.

The HR Suite focuses on core workforce management regarding employee presence and time off.

## Attendance

Detailed logs of employee punch-in and punch-out times, total hours worked, and break durations. Supports filtering by date ranges or individual users.

## Leaves

A dedicated section to manage, approve, or review employee leave requests and balances. Users can view their remaining quotas, while managers have oversight over the entire team's absences.

***

## In This Section

<table data-view="cards"><thead><tr><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><strong>Attendance</strong></td><td>Punch-in/out logs, hours worked, and break durations.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/hr-suite/attendance">Attendance</a></td></tr><tr><td><strong>Leaves</strong></td><td>Manage and review leave requests and balances.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/hr-suite/leaves">Leaves</a></td></tr></tbody></table>


# Attendance

We360.ai attendance dashboard — track employee entry, exit, breaks, lateness, and daily attendance metrics.

The **Attendance** dashboard provides HR teams and Managers with a bird's-eye view of employee presence, punctuality, and daily habits. It functions as the definitive ledger of when an employee is actively "at work."

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-005bd22b5f56fb5d9b350b432fa2ec69eed477a3%2Fportal-attendance.png?alt=media" alt="Attendance dashboard with summary metrics and trends"><figcaption><p>Attendance dashboard overview with attendance trends and metrics</p></figcaption></figure>

## Reporting Views

The Attendance section is divided into three distinct reporting tabs, allowing managers to zoom in from high-level trends down to minute-by-minute logs.

<details>

<summary>Summary Tab</summary>

Provides macro-level metrics for the entire organization or selected teams over a date range. With the Teams and Date Range filters, admins have the flexibility to access insights for any team on any date range. By default, the team filter is set to the entire organization and the date range is set to "Last 7 Days."

**Metric Cards**: Four summary cards are displayed at the top:

* **Attendance %**: The overall attendance percentage, with a comparison showing the movement relative to the previous period (e.g., "25% more than the previous 7 days").
* **Late Arrivals %**: The percentage of employees arriving late, with period-over-period comparison.
* **Total Break Time**: Aggregate break time for the selected filters, with comparison to the prior period.
* **Total Working Time**: Aggregate working hours, with comparison to the prior period.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-e1e68529c3f18c0d8ee2d49a4319633ab4284593%2Fwidget-attendance-metric-cards.png?alt=media" alt="Attendance metric cards"><figcaption><p>Summary metric cards showing Attendance %, Late Arrivals, Break Time, and Working Time.</p></figcaption></figure>

**Widgets and Graphs**:

* **Today's Attendance**: This widget always displays today's attendance count and is not affected by the date range filter. Team filters still apply.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-ef7efd2c2e7a25d8413105c315a62bcff62a9f69%2Fwidget-attendance-todays.png?alt=media" alt="Today&#x27;s Attendance donut"><figcaption><p>Today's Attendance widget with present/absent donut chart.</p></figcaption></figure>

* **Attendance Trends**: A bar graph showing the trend of present and absent employee counts over the filtered date range.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-bd3e5ffe70a4097e136af2214d5d4c902f6ec92b%2Fwidget-attendance-trends.gif?alt=media" alt="Attendance Trends bar graph"><figcaption><p>Attendance Trends showing present vs absent counts over time.</p></figcaption></figure>

* **Break Trends**: A line graph displaying the trend of total break time taken by the filtered team over the filtered date range.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-1451f852c077169a93e6a77f0f5cc4dcdc3164c4%2Fwidget-attendance-break-trends.gif?alt=media" alt="Break Trends line graph"><figcaption><p>Break Trends tracking total break time over the selected period.</p></figcaption></figure>

* **Late Arrival Tendency**: A grouped bar graph showing the number of late arrivals versus on-time arrivals within the applied filters.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d5b8b818243f2fa9279b58ff7709ed5ef14f2cd9%2Fwidget-attendance-late-arrival.png?alt=media" alt="Late Arrival Tendency chart"><figcaption><p>Late Arrival Tendency comparing late vs on-time arrivals.</p></figcaption></figure>

* **Export PDF**: The Summary tab includes a PDF export option, generating a formatted cover sheet and executive summary of the attendance health for the period.

{% hint style="info" %}
**How key metrics are calculated**

* **Attendance %** -- For a single date: `Present Employees / Total Employees`. For a date range: the same ratio averaged across all days in the range.
* **Late Arrivals** -- The percentage of present employees who punched in after the start of their shift and outside the configured grace period. For example, if the grace period is 10 minutes, anyone punching in 10+ minutes late is counted. Over a date range this percentage is averaged.
* **Working Time** -- The sum of all successive (punch-out minus punch-in) durations for each employee across the selected period.
* **Break Time** -- Total time employees spend in an active "Break" status (triggered manually or automatically based on configured break policies).
  {% endhint %}

</details>

<details>

<summary>Detailed Tab</summary>

Allows managers to drill down into specific employee performance. Includes team, user, and date range filters.

* **Trend Graph**: Displays attendance trends for the selected filters.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-c0f957ae301a3d6fa0ebdd2a2dd0c73b79f0a057%2Fwidget-attendance-details-trend.gif?alt=media" alt="Detailed attendance trend"><figcaption><p>Attendance trend graph in the Detailed tab.</p></figcaption></figure>

* **Data Table**: Displays a paginated list of employees with their attendance, working time, online time, and break time for the selected date range.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-a600ec9e6143fe41292d490a01b4d7afcf32fbd1%2Fwidget-attendance-details-table.gif?alt=media" alt="Detailed attendance table"><figcaption><p>Employee attendance detail table with working time and break metrics.</p></figcaption></figure>

* **View Calendar**: Each employee row includes a "View Calendar" button. Clicking it opens a modal popup showing the present/absent status for each day of the month. Clicking on any day when the employee was present reveals the detailed presence logs, including in/out timestamps and working time duration.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-4edf65344cc68a15652209342b4f3081fc034665%2Fwidget-attendance-calendar.gif?alt=media" alt="Attendance calendar view"><figcaption><p>Monthly calendar popup showing daily present/absent status.</p></figcaption></figure>

* **Export CSV**: This view enables exporting a granular CSV file for payroll processing.

</details>

<details>

<summary>Datewise Attendance Tab</summary>

A single-date view where admins and managers can see the present/absent statistics for a particular day. Present employees are arranged in a list on the left and absent employees on the right. For each present employee, the in/out timings are displayed.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-2f4b4724234713f899b6574f384e2202d2b00736%2Fwidget-attendance-datewise.gif?alt=media" alt="Datewise Attendance view"><figcaption><p>Datewise Attendance showing present and absent employees for a single date.</p></figcaption></figure>

{% hint style="info" %}
The in/out timings shown are the **first punch-in** and **last punch-out** times for the day. If an employee has punched in/out multiple times during the day, only the earliest in-time and latest out-time are displayed. For employees who have not yet checked out, only the in-time is shown.
{% endhint %}

</details>


# Leaves

We360.ai leaves — employee time-off requests, approval workflows, and absence management for capacity planning.

The **Leaves** module centralizes all Time Off requests, ensuring that both employees and managers have a clear, auditable trail of planned absences to facilitate better capacity planning.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-4e6faa467e9faef119c1ab2d2c41ef0ffa8cbf26%2Fportal-leaves.png?alt=media" alt="Leaves management interface with pending and historical requests"><figcaption><p>Leaves module showing leave requests and approval workflow</p></figcaption></figure>

## The Leave Lifecycle

The portal divides the Leave experience into two primary views centered around the approval workflow.

<details>

<summary>Pending Approval</summary>

When an employee submits a new Leave request (specifying dates, the Leave Type, and an optional summary/reason), it immediately surfaces in this view for managers holding Tenant Manager or Tenant Owner roles.

* **Card UI**: Pending requests are displayed as easily scannable cards.
* **Actionable**: Managers can immediately Approve, Reject (with required remarks), or Edit the request (e.g., adjusting the dates if only a partial leave is granted) directly from the card.
* **Notifications**: Approvals or Rejections trigger automated notifications back to the employee.

</details>

<details>

<summary>All Leave</summary>

A historical and comprehensive data table displaying every leave request ever made within the selected timeframe.

* **Filtering**: Highly configurable filters allow HR to search by a specific Employee Name, Leave Type (e.g., Sick, Casual, Earned), or Status (Approved, Pending, Rejected).
* **Exporting**: Like other critical HR data, this view supports exporting a CSV report detailing the "From," "To," "Duration," "Reason," and "Status" of every request.

</details>

## Applying for Leave

To submit a new leave request, employees click the **Apply Leave** button and fill in the following details:

* **Leave Type** -- select from the configured types (e.g., Sick, Casual, Earned).
* **Date Range** -- the start and end dates of the requested absence.
* **Summary / Reason** -- an optional note explaining the reason for leave.

Once submitted, the request immediately appears in the **Pending Approval** tab for the employee's manager to act on. The employee can track its status from the **All Leave** tab.

## Access Control

The portal enforces strict access controls regarding Leave management. Only users with specific administrative privileges (Tenant Owners/Managers) can approve or reject leaves, whereas standard employees can only submit requests and view the status of their own historical applications.


# Universal Tools

We360.ai Universal Tools — cross-suite workforce analytics reports, alerts, and employee detail views.

Available across different suites, these core reporting functions are always accessible from the main navigation menu.

## Reports

A robust reporting engine capable of generating custom, exportable documents (e.g., Daily Attendance, Group Insights) for external analysis.

## Integrations

Dashboards dedicated to managing connections with external tools and services to seamlessly sync organizational data.

## Alerts

A centralized feed of triggered system notifications and policy violations (e.g., Late Arrivals, Idle times) as defined by administrators.

## User Detail

A personalized view showing an individual user's specific performance profile and metadata.

***

## In This Section

<table data-view="cards"><thead><tr><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><strong>Reports</strong></td><td>Generate custom, exportable reports for external analysis.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/universal-tools/reports">Reports</a></td></tr><tr><td><strong>Integrations</strong></td><td>Manage connections with external tools and services.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/universal-tools/integrations">Integrations</a></td></tr><tr><td><strong>Alerts</strong></td><td>System notifications and policy violation alerts.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/universal-tools/alerts">Alerts</a></td></tr><tr><td><strong>User Details</strong></td><td>Individual user performance profiles and metadata.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/universal-tools/user-detail">User Details</a></td></tr></tbody></table>


# Reports

We360.ai reports — downloadable workforce analytics, productivity tracking exports, and employee monitoring data.

Visual dashboards are excellent for daily management, but deep auditing and cross-platform integrations require raw data. The **Reports** module provides a categorized library of downloadable exports, covering every conceivable metric tracked by the We360.ai Agent.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-818607dee650d288dc0d4557411d2e9153b9fe79%2Fportal-reports.png?alt=media" alt="Reports module showing all available report cards"><figcaption><p>Reports module overview with all available report types</p></figcaption></figure>

## Categories

<details>

<summary>Attendance &#x26; Time</summary>

* **Daily Attendance**: Displays daily shift details, punch times, work duration, and smart attendance remarks like full day, short presence, or absent. The table includes columns for employee name, assigned shift, arrival status (early/late/on-time), in time, out time, departure status (early/late/on-time), working time, and online time. Available as CSV download.
* **Monthly Attendance**: View a complete month's attendance breakdown by day, with total present, absent, and working hours -- filtered by team, user, or time type.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-86cbda41ef38ef3e0e91de3ba0cf2e140f54848f%2Freport-daily-attendance.png?alt=media" alt="Daily Attendance report"><figcaption><p>Daily Attendance Report</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d6048bb5022497ac82a65a4ef1161fdeb9d54451%2Freport-monthly-attendance.png?alt=media" alt="Monthly Attendance report"><figcaption><p>Monthly Attendance Report</p></figcaption></figure>

* **Monthly In-Out**: Track exact punch-in/punch-out times across the month, including absences and weekly offs, for every employee in one clear view.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-c18223a18fa9515eb85ff5c66e572d8ed15b2850%2Freport-monthly-inout.png?alt=media" alt="Monthly In-Out report"><figcaption><p>Monthly In-Out Report</p></figcaption></figure>

* **Break Report**: Get a clear view of when, how often, and how long employees take breaks -- daily or monthly -- so you stay informed and balanced. The report presents break data in a tabular format with columns for break type, start time, end time, and duration. Each column is sortable. Available as CSV download.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-7aeede33232609536f028686d81a281dbcd01de8%2Freport-break-report.png?alt=media" alt="Break Report"><figcaption><p>Break Report</p></figcaption></figure>

* **Cross-Day Attendance**: Designed specifically for night shifts or non-standard work hours that cross midnight boundaries.
* **Timesheet Report**: Export approved project hours and time allocations logged through the Timesheet module.
* **Manual Time Report**: Review every submitted manual time entry along with its approval status, summary, and attached evidence.

</details>

<details>

<summary>Analytics &#x26; Productivity</summary>

* **Productivity Report**: Shows how efficiently employees are working by breaking down their online time into productive, unproductive, neutral, and break durations. The core formula is: **Online Time = Productive Time + Unproductive Time + Neutral Time + Break Time**. Available as CSV download.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-c7dad42d4d820a6a746b0d343f875af41db44a40%2Freport-productivity-report.png?alt=media" alt="Productivity Report"><figcaption><p>Productivity Report</p></figcaption></figure>

* **Apps/URL Report**: Understand where employee time goes -- track which apps and websites are used the most and for how long. Displays a graphical representation of the **top 20 applications and URLs** in descending order of usage, along with a detailed usage table with columns for Type, Details, Percentage, and Duration (each column is sortable). Two checkboxes allow you to filter between Apps usage and URL usage. Note that Apps/URL reports can only be downloaded in **PDF format**.
* **Logs Report (Apps & URL)**: The detailed timestamped logs of application usage and website visits for comprehensive insights into employee activity.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-eb81e1f4b74e0ee23b8990a4dd87d12d73d8cc8b%2Freport-apps-urls-report.png?alt=media" alt="Apps/URLs Report"><figcaption><p>Apps/URLs Report</p></figcaption></figure>

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-0dfa6c25cf13a99e037e1a674dbc31f2e9565564%2Freport-logs-report.png?alt=media" alt="Logs Report"><figcaption><p>Logs Report</p></figcaption></figure>

* **Activity Report**: Track how actively employees are working by monitoring their online, active, and idle time, along with keyboard and mouse activity. The core formula is: **Online Time = Active Time + Idle Time + Break Time**. The report provides an in-depth analysis of each employee's activity, including the number of key presses and mouse clicks. Available as CSV download.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-92d296378680cc9c6605ddf447090219ab4fb270%2Freport-activity-report.png?alt=media" alt="Activity Report"><figcaption><p>Activity Report</p></figcaption></figure>

* **Project Report**: Stay on top of project accountability with a complete view of task ownership, timelines, and time tracked against deliverables.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d8c0d91aef596c245bf49fc0f300ec4147d58af7%2Freport-project-report.png?alt=media" alt="Project Report"><figcaption><p>Project Report</p></figcaption></figure>

* **Teams Insight**: A visual dashboard displayed as a grid of cards, where each card represents a specific team's performance for a single day. Each card shows: **Attendance** (present and absent counts), **Activity** (average activity level), **Working Hours** (total hours worked), and **Top 3 Active Users** within the team. Use the date filter to check insights from previous days. Note: this report is view-only and cannot be downloaded.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-98e2f69556d0f78b70d4da01f165cb2338edc41f%2Freport-teams-insight.png?alt=media" alt="Teams Insight report"><figcaption><p>Teams Insight Report</p></figcaption></figure>

* **Time & Motion**: A focus-quality report that goes beyond total hours to show how work actually flows through the day — how often employees switch context between apps and tasks, how much sustained focus time they get, and where attention is fragmented. Presented on screen for a selected month, with an explicit comparison against the previous month so you can see whether focus is improving or slipping.
* **Summary Report**: A single monthly roll-up that brings attendance, activity, and productivity headlines together in one view, again with a previous-month comparison. Best for a quick month-over-month health check of a team or the organization.
* **Integration (Meeting) Report**: For organizations that connect Microsoft Teams, this report attributes time spent in online meetings so that meeting time is reflected accurately alongside app and productivity data. Requires the Microsoft Teams integration to be configured.

</details>

<details>

<summary>IT &#x26; Security</summary>

* **Device Report**: Detailed inventory of endpoints currently running the We360.ai agent (PC and Mobile), useful for asset management.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-86cb21a206db2f979ce27c1a761c80b0ec26a0ab%2Freport-device-report.png?alt=media" alt="Device Report"><figcaption><p>Device Report</p></figcaption></figure>

* **USB Detection**: Get real-time visibility when any USB device is connected or disconnected on an employee's system.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-dc6f9d84c744ecf611e5b242686ccf7f7805f0be%2Freport-usb-detection.png?alt=media" alt="USB Detection Report"><figcaption><p>USB Detection Report</p></figcaption></figure>

* **Alert Report**: A table organizing all alerts generated for a given day, including the date of the alert, a brief description, the alert type (URL alert, application alert, overtime break alert), who the alert was triggered for, and the trigger time. The Alert Report includes only a **date filter**. Available as CSV download.
* **Audit Logs**: A record of significant administrative actions taken in the portal — configuration and policy changes, user and role updates, and other sensitive operations — for accountability and compliance reviews. Visible to Super Admins.

</details>

## Customization

* **Dynamic Reports**: Beyond the standard list of exports, organizations can build fully customized reports by selecting the exact metrics and information to include. The report builder provides **six filter sections**, each containing checkbox items that become columns in the generated report:

  * **Report Type**: Choose between summary or detailed report, and select the download format. **Cross-day shifts** appears here when your organization works across midnight — see below.
  * **User Information**: Select which user fields to include.
  * **Shift**: Include shift-related data.
  * **Working Time**: Include working time metrics.
  * **Activity**: Include activity-related metrics.
  * **Productivity**: Include productivity-related metrics.

  After configuring the report, clicking the download button prompts you to name the report for easy identification. Dynamic Reports can be downloaded in three formats: **CSV**, **XLS**, or **JSON**.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-61b2c38f21b4043d5b6985e8233c30d4824c0ab3%2Freport-dynamic-report.png?alt=media" alt="Dynamic Report builder"><figcaption><p>Dynamic Report</p></figcaption></figure>

**Cross-day shifts.** Tick this to keep a shift that runs past midnight on a single row, dated by the day it started, instead of splitting it across two dates. It is unticked by default, so a report you do not change behaves exactly as it always has. The option only appears for organizations set up for work across midnight.

Whether you can use it over a date range depends on your setup:

* With [Cross-Day Working Time](/reference/work-and-time-management/user-interfaces/portal/settings-center/workplace#cross-day-working-time) switched on, any date range works.
* Otherwise the shift boundaries are worked out from activity as the report runs, which is only possible **one day at a time**. Pick a single date, or ask an administrator to switch the setting on.
* **Scheduled Reports**: Managers can configure We360.ai to automatically generate and email specific reports (e.g., Weekly Attendance) on a recurring basis, eliminating manual data-pulls.


# Integrations

We360.ai integrations — sync employee monitoring and workforce analytics data with your existing tools and platforms.

We360.ai is designed to act as the single source of truth for workforce analytics, but that data is most powerful when it flows seamlessly into your existing tech stack.

## Integration Dashboard

The **Integrations Dashboard** acts as the command center for monitoring the health and outputs of your connected applications (e.g., mapping data to Workday, syncing with Microsoft Teams, or piping timesheets to Jira).

<details>

<summary>Data Synchronization &#x26; Status</summary>

The primary feature of the dashboard is the **Status Distribution**, which calculates the synchronization health of your workforce.

* It visually categorizes users into specific statuses based on the integrated data (e.g., Red, Green, Overworked, OOO/Absent, Data Missing).
* Managers can toggle the underlying calculation (Active Time vs. Productive Time vs. Online Time) to shift the lens through which employee health is viewed.

</details>

<details>

<summary>Actionable Scenarios</summary>

Rather than just presenting a list of errors, the dashboard highlights specific **Actionable Scenarios** where integrations have run into logical roadblocks.

* **Intelligent Suggestions**: The system identifies discrepancies (e.g., "Employee is marked OOO in Workday but logged 4 hours in We360") and provides targeted suggestions on how to resolve the conflict.
* **Impacted Users**: Hovering over an alert immediately shows exactly which employee IDs are triggering the integration failure, allowing for rapid troubleshooting.

</details>


# Alerts

We360.ai alerts — historical logs of automated employee monitoring notifications and triggered system warnings.

The **Alerts** module acts as the historical ledger for the automated notification system configured in the Settings Center. While the *rules* for alerts are defined elsewhere, this page is where managers review what was actually triggered.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-f0e595cb85b830acb264d6089f24bef79ee6a89a%2Fportal-alerts.png?alt=media" alt="Alerts history showing triggered notifications and events"><figcaption><p>Alerts history log with triggered events and timestamps</p></figcaption></figure>

* **Paginated History**: Displays a continuous feed of all triggered events (e.g., an employee exceeding a threshold for "Unproductive App Usage," or attempting to access a blacklisted URL). The dashboard includes a total alert count and pagination for easy navigation.
* **Alert Details**: Each alert record in the dashboard includes: **Date** of the event, **Alert Description** explaining the trigger reason, **Alert Type** (e.g., Absence, URL, Application, Overtime Break), **Triggered For** (the specific user), and **Triggered Time** when the alert occurred.
* **Timestamps**: Every alert is logged with a precise timestamp, providing an auditable trail for HR or IT security interventions.
* **Email Notifications**: Whenever an alert is triggered, an automated email notification is sent to relevant stakeholders. The email includes the alert reason, user details (name, email, date of event), and additional context such as the last seen time. This ensures managers are informed even when they are not logged into the platform.
* **Exportable**: The entire alert history can be filtered by date and exported as a CSV for external compliance reviews or internal disciplinary tracking.

## Alert Configuration

{% hint style="info" %}
Alert rules are **not** configured on this page. To create or modify alert triggers, navigate to **Settings > Emails & Alerts > Alert Rules**. The Alerts module here is the read-only log of everything those rules have fired.
{% endhint %}

Configurable alert triggers include scenarios such as:

* **Absence Alerts** -- triggered when one or more users are absent during their assigned shift.
* **Inactivity Alerts** -- triggered when a user remains inactive beyond a defined time threshold (e.g., 60 minutes of inactivity).
* **Overtime Break Alerts** -- triggered when an employee exceeds the defined break time limit.
* **URL Alerts** -- triggered when specific URLs (e.g., social or entertainment sites) are accessed.
* **Application Alerts** -- triggered when restricted or monitored applications are opened.
* **Late Arrival** -- employee punches in beyond the allowed grace period.
* **Unproductive App Usage** -- time spent on unproductive applications exceeds a set limit.

Each triggered alert record in the log typically includes: **Employee Name**, **Alert Type**, **Trigger Condition**, **Date & Time**, and the **Team** the employee belongs to.


# User Details

We360.ai user detail — individual employee productivity analytics, activity timeline, and monitoring insights.

While the overarching dashboards provide a macro view of the organization, the **User Details** page is the ultimate micro view. Clicking on an employee's name anywhere within the portal will direct a manager to this comprehensive dossier.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-26d04ca6ec4052e536e59c2f2696dc8425bb1f25%2Fportal-userdetail.png?alt=media" alt="User detail page showing individual employee analytics"><figcaption><p>User detail page with comprehensive individual analytics</p></figcaption></figure>

{% hint style="info" %}
The User Detail page essentially recreates the entire suite of analytical tools, but filters the data exclusively for the selected individual.
{% endhint %}

## Key Analytics Available

{% columns %}
{% column %}
**⏱ Granular Timeline**

Review the specific start, stop, and idle periods of the user's day in chronological order. Easily spot breaks and off-system time.
{% endcolumn %}

{% column %}
**💻 App & URL Usage**

See exactly what software and websites they focused on and for how long. Helps identify the most utilized platforms and productivity alignment.
{% endcolumn %}
{% endcolumns %}

{% columns %}
{% column %}
**📸 Visual Evidence**

*(If enabled by policy)* View the localized timeline of specific screen captures or camera snapshots taken during their session. Supports blurring for privacy.
{% endcolumn %}

{% column %}
**📅 Timesheets & Leaves**

Review their personal project allocations and time-off balances in one unified location, syncing with HRMS integrations if configured.
{% endcolumn %}
{% endcolumns %}

## Available Sub-Tabs

The User Detail page organizes individual analytics across **9 dedicated sub-tabs**:

| Tab              | What it shows                                                                                                                                                                                                                            |
| ---------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Attendance**   | Attendance doughnut chart (present/absent for the date range), monthly attendance calendar visualizing the employee's attendance for the month, and an attendance detail list showing datewise in/out times, working duration, and logs. |
| **Breaks**       | Duration and frequency of breaks taken during each workday.                                                                                                                                                                              |
| **Wellness**     | Wellness doughnut chart, monthly wellness calendar, and a wellness detail list.                                                                                                                                                          |
| **Productivity** | Metric cards for Top Application, Top URL, and Top Category. Productivity breakdown doughnut chart and a productivity detail table.                                                                                                      |
| **Activity**     | Metric cards for Top Application, Top URL, and Top Category. Activity breakdown doughnut chart and an activity detail table.                                                                                                             |
| **Apps & URLs**  | Metric cards for Top Application, Top URL, and Top Category. Category utilization chart, total application usage, total URL usage, and a list of all applications used.                                                                  |
| **Devices**      | OS version, hardware identifiers, and IP address of the user's active endpoints.                                                                                                                                                         |
| **Settings**     | User-specific tracking and policy overrides configured by an admin.                                                                                                                                                                      |
| **Scorecard**    | Monthly performance scorecard with comparative pentagon graph (see below).                                                                                                                                                               |

## Employee Scorecard

The **Scorecard** tab provides a single-page summary of an employee's monthly performance. It is available to admins, managers, and the employee themselves, and can be downloaded as a report.

<details>

<summary>Comparative Analysis (Pentagon Graph)</summary>

The scorecard plots five key performance indicators on a pentagon-shaped radar chart, comparing three overlays:

* **User** -- the individual employee's scores.
* **Team** -- the average scores of the employee's team.
* **Company** -- the organization-wide average.

This lets managers instantly see where an employee excels or falls behind relative to their peers.

</details>

<details>

<summary>Monthly Performance Insights</summary>

Below the pentagon graph, the scorecard breaks performance into six categories:

* **Attendance** -- Total present days, half days, late arrivals, early departures, average working time, and total break time.
* **Productivity** -- Total and average productive, neutral, and unproductive time; most and least productive days.
* **Activity** -- Total and average online, active, and idle time to gauge engagement.
* **Apps & URLs** -- Top applications and websites used, categorized by productivity classification.
* **Goals** -- Monthly goal achievement rate, comparing days goals were met versus missed.
* **Wellness** -- Workload balance indicators showing overburdened or underutilized days.

</details>

<details>

<summary>Supplemental Information</summary>

The user detail view also surfaces:

* **Manual Time Logs:** View and approve manual hours submitted by the user.
* **Device Information:** View the OS version, unique hardware identifiers, and IP address of the user's active endpoint.

</details>


# Settings Center

We360.ai Settings Center — configure employee monitoring policies, productivity rules, and compliance controls.

The Settings center allows administrators to configure every aspect of the platform.

<figure><img src="https://312671257-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FQ3PNLgMbrzO5nP1CwEjg%2Fuploads%2Fgit-blob-d8f0730f7a86696e941a2ec96bb3984a454adf0e%2Fportal-settings.png?alt=media" alt="Settings center main navigation with configuration categories"><figcaption><p>Settings center overview with all configuration categories</p></figcaption></figure>

<details>

<summary>Organization &#x26; Billing</summary>

Manage your overarching company details, global branding (logos, themes), and review billing invoices and subscription tiers. This is also where you update your company name, time zone, and plan details.

</details>

<details>

<summary>User Management</summary>

The core directory for managing access to the portal and tracking agent.

* Add, edit, or remove Users (individually or via bulk import).
* Configure employee Designations and Teams (including bulk team reassignment).
* Manage access control through **Role Settings** -- control which features and reports each role can see.
* Create Custom fields to capture non-standard employee data.
* Edit individual user tracking settings (screenshots, stealth mode, etc.).

</details>

<details>

<summary>Workplace (Attendance Settings)</summary>

Define the rules for how time is managed at the company.

* Create and manage standard working **Shifts** schedules, and assign or change shifts per team.
* Define **Break** policies and trackable **Leave Types**.
* Configure Advanced Settings including Half Days rules, Wellness tracking margins, and Timesheet policies (such as enabling auto-approval or requiring managerial sign-off).

</details>

<details>

<summary>Productivity</summary>

Establish what "productive time" means for your organization.

* **Application Policies**: Determine which specific tools or URLs are classified as productive, unproductive, or neutral. Supports advanced categorization modes (Default, Focus, Drop, DLP-Redaction).
* **Category Mapping**: Group related applications together for easier reporting (e.g., 'Social Media', 'Development Tools').
* **Goal Setting**: Define default daily/weekly productivity targets for Active Time and Productive Time.

</details>

<details>

<summary>Emails &#x26; Alerts</summary>

* **Email Reports**: Subscribe managers and administrators to automated daily or weekly summary emails.
* **Alert Rules**: Define the triggers that generate notifications (e.g., late arrivals, excessive idle time, or accessing blocked websites).

</details>

<details>

<summary>Compliance &#x26; Security</summary>

Protect your organization's digital environment.

* **Domain Blocking**: Restrict website access across teams with smart controls, ensuring focused work and compliance.
* **Compliance Configuration**: Adjust tracking strictness and stealth mode capabilities.
* **Audit Logs Report**: Review administrative actions taken within the portal by other managers for security auditing.

</details>

<details>

<summary>Integrations</summary>

Configure API connections and synchronize data with supported third-party platforms (e.g., HRMS, Project Management tools) from the integration dashboard.

</details>

<details>

<summary>UI Settings</summary>

Customize default fields, data visualization preferences, and portal appearances tailored to the organization's specific needs.

</details>

***

## In This Section

<table data-view="cards"><thead><tr><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><strong>Organization &#x26; Billing</strong></td><td>Company details, branding, and subscription management.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center/organization-billing">Organization &amp; Billing</a></td></tr><tr><td><strong>User Management</strong></td><td>Users, teams, roles, and custom fields.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center/user-management">User Management</a></td></tr><tr><td><strong>Workplace</strong></td><td>Shifts, breaks, leave types, and attendance rules.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center/workplace">Workplace</a></td></tr><tr><td><strong>Productivity</strong></td><td>App policies, category mapping, and goal setting.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center/productivity">Productivity</a></td></tr><tr><td><strong>Emails &#x26; Alerts</strong></td><td>Automated email reports and alert rule configuration.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center/emails-alerts">Emails &amp; Alerts</a></td></tr><tr><td><strong>Compliance &#x26; Security</strong></td><td>Domain blocking, compliance config, and audit logs.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center/compliance-security">Compliance &amp; Security</a></td></tr><tr><td><strong>Integrations</strong></td><td>API connections and third-party platform sync.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center/integrations">Integrations</a></td></tr><tr><td><strong>UI Settings</strong></td><td>Data visualization and portal appearance preferences.</td><td><a href="/reference/work-and-time-management/user-interfaces/portal/settings-center/ui-settings">UI Settings</a></td></tr></tbody></table>


# Organization & Billing

We360.ai organization and billing — manage company profile, employee monitoring subscriptions, and payment history.

The **Organization & Billing** section is solely accessible to Tenant Owners. It serves as the foundational configuration for the company's instance of We360.ai.

## Company Details

Manage the core identity of your workspace:

* **Profile**: Update the legal company name, contact email, primary phone number, and registered address.
* **Branding**: Upload the company logo to customize the portal, making the environment feel native to your employees.

## Billing & Invoices

Managing your SaaS expenditures is straightforward within the billing portal:

* **Subscriptions**: View your current plan (e.g., Basic, Pro, Enterprise), the total count of licensed seats, and your upcoming renewal dates. You can effortlessly add or remove licenses as your workforce scales.
* **Invoices**: A historical ledger of all past payments. You can download PDF invoices for accounting and tax purposes directly from this view.
* **Payment Methods**: Add, remove, or update the credit cards on file for automated renewals.


# User Management

We360.ai user management — administer employee directories, team structures, and monitoring access levels.

Scaling a workforce requires a robust, structured approach to identity management. The **User Management** section is where administrators build the digital replica of their company's org chart.

## Features

<details>

<summary>Directory &#x26; Teams</summary>

* **User Directory**: Invite new employees individually or via bulk CSV upload. Here, you can define their reporting manager, assign them to a team, and set their default workspace policies.
* **Teams & Designations**: Group similar users (e.g., "Engineering", "Sales") into Teams to enable bulk reporting and group-based access filtering. You can also formalize job titles using the Designations feature.
* **Custom Fields**: Every organization is unique. We360.ai allows you to create Custom Fields (e.g., "Employee ID", "T-Shirt Size", "Internal Department Code") to attach specialized metadata to user profiles.

</details>

<details>

<summary>Roles &#x26; Permissions</summary>

Security and data privacy are paramount. **Roles** define exactly what a user can see and do within the portal.

* **Pre-defined Roles**: The system includes standard Roles like *Tenant Owner* (full access), *Tenant Manager* (team-level management), and *Tenant User* (can only view their own data).
* **Role-Based Access Control (RBAC)**: Fine-tune access by granting specific permissions. For example, you can allow a manager to approve Leaves for their team, but deny them access to view Productivity Reports.

</details>

## How-to Guides

<details>

<summary>Adding a Single User</summary>

1. Navigate to **Settings > User Management > Users** tab.
2. Click the **Add User** button at the top right.
3. A sidebar drawer appears with fields for First Name, Last Name, Email, Date of Birth, Date of Joining, Phone, Gender, Role, Designation, and Team. Fields marked with an asterisk (\*) are mandatory.
4. A work email address is required to create the user; without it the account cannot be created.
5. Under the Team dropdown, the **Default** team is pre-selected. You can reassign the user to a custom team later.
6. Click **Submit** to add the user. The user list updates with the new entry showing Name, Email, Team, Role, and Status.

</details>

<details>

<summary>Bulk Import via CSV</summary>

1. In the Users tab, click the kebab menu icon and select **Bulk Import**.
2. A dialog appears with three sections:
   * **Upload CSV file** -- Click **Choose File** and select a `.csv` file (max 100 KB). The parsed data previews in a table.
   * **Download Sample** -- Download a sample CSV to see the required format before preparing your own file.
   * **Fields Description** -- Shows mandatory fields (Email, First Name, Last Name, Role, Team) and non-mandatory fields (Gender, Designation, Date of Birth, Date of Joining, Phone).
3. Click **Validate**. If validation passes, the **Import** button becomes active. Fix any flagged errors in the table or re-upload a corrected file.
4. Click **Import** to create the users.
5. Import history is available in the **Bulk Import Logs** table showing date, status, total, failed, and success record counts.

</details>

<details>

<summary>Editing a User Profile</summary>

Each user row has a kebab menu icon with a **Modify User** option. Clicking it opens a sidebar drawer containing the user's basic details and tracking settings, all of which can be edited.

</details>

<details>

<summary>Activating or Deactivating Users</summary>

Administrators can activate or deactivate users individually or in bulk.

**Bulk method:**

1. Select users via the checkboxes in the user list.
2. Click the **Activate** or **Deactivate** button that appears at the top.

**Individual method:**

1. Click the kebab menu icon next to the target user.
2. Select **Deactivate** (or **Activate**, if the user is currently inactive).

</details>

<details>

<summary>Managing Designations</summary>

1. Navigate to **Settings > User Management > Designations** tab.
2. The tab displays a table of existing designations with Name, Description, and Created At columns.
3. Click **Add Designation** at the top right, fill in the Name and Description, and click **Submit**.
4. To edit, click the **Action** button on any designation row and modify the fields in the popup.

{% hint style="info" %}
Create designations before adding users, since Designation is a mandatory field during user creation.
{% endhint %}

</details>

<details>

<summary>Managing Teams</summary>

The **Teams** section in Settings displays a hierarchical list of teams on the left and team details on the right. Each team has three tabs:

* **Team Info** -- Set the productivity rules policy and shift assignment for the team via dropdown selectors.
* **Members** -- View employees split into "In this Team" and "Not in this Team" lists. Use the plus icon (+) to add members, or the kebab menu to change a member's team or promote them to manager. An employee can belong to only one team, but a team may have multiple managers.
* **Settings** -- Configure team-level tracking parameters (see Tracking Parameters below).

**To create a team:** Click **Add Team**, fill in the Team Name and Description, then confirm.

**To assign or change a team manager:**

1. Open the target team and switch to the **Members** tab.
2. Locate the employee (they must already be in the team).
3. Click the kebab menu next to their name and select **Make Manager**.

</details>

<details>

<summary>Tracking Parameters (Team &#x26; User Level)</summary>

Both team settings and individual user settings expose the same tracking parameters. User-level values default to the team setting but can be overridden per user via **Modify User > Settings**.

| Parameter               | Type     | Description                                                                                     |
| ----------------------- | -------- | ----------------------------------------------------------------------------------------------- |
| Tracking                | Toggle   | Switch off to stop all tracking for the team or user.                                           |
| Capture Screenshots     | Toggle   | Enable periodic screenshot capture.                                                             |
| Screenshot Frequency    | Dropdown | Interval between screenshots (1 min to 2 hours). Only active when Capture Screenshots is on.    |
| Livestream              | Toggle   | Enable real-time screen viewing.                                                                |
| App & URLs              | Toggle   | Track application and URL usage.                                                                |
| Keyboard Mouse          | Toggle   | Track keyboard and mouse activity metrics (no keystroke logging). Requires App & URLs to be on. |
| Idle Timeout Popup      | Dropdown | Duration of inactivity before an idle-check popup appears (1 min to 2 hours).                   |
| Active Threshold        | Dropdown | Duration within which the user is considered active (30 seconds to 3 minutes).                  |
| Auto Punchout Threshold | Dropdown | Duration of inactivity after which the user is automatically punched out (1 min to 2 hours).    |
| Portal Access           | Toggle   | Grant or revoke access to the web portal dashboard.                                             |

</details>


# Workplace

We360.ai workplace settings — configure attendance policies, shift schedules, and time-off rules for employee monitoring.

The **Workplace Settings** module is the policy engine for the HR Suite. It defines the mathematical boundaries of what constitutes "work."

## Core Configurations

<details>

<summary>Shifts &#x26; Breaks</summary>

* **Shift Configuration**: Define standard working hours (e.g., 9:00 AM to 5:00 PM), grace periods for late arrivals, and minimum hours required for a Half-Day or Full-Day attendance mark. You can create multiple overlapping shifts to accommodate round-the-clock operations.
* **Break Policies**: Standardize allowable downtime. Define whether breaks are paid or unpaid, their maximum duration, and what applications (if any) are permitted during a break without triggering a productivity alert.

</details>

<details>

<summary>Leave Types</summary>

Establish the time-off economy for your organization.

* Create distinct leave buckets such as *Casual Leave*, *Sick Leave*, or *Earned Time Off*.
* Define accrual rules, standard annual balances, and whether unused balances can carry over into the next fiscal year.

</details>

<details>

<summary>Advanced Rules</summary>

Toggle system-wide behaviors that deeply alter the tracking experience:

* **Half-Day Logic**: Determine if half-days are calculated based on hours worked, or specific punch-in times.
* **Timesheet Workflows**: Enable or disable managerial approval requirements for submitted timesheets.
* **Wellness Thresholds**: Set limits on continuous working hours before the system prompts the employee to rest, fostering a healthier digital work environment.
* **Auto Punch-Out**: Configure automatic punch-out behavior based on shift end time or a fixed duration, preventing inflated attendance records. Leave this **Disabled** if you need [Cross-Day Working Time](#cross-day-working-time).

</details>

## Cross-Day Working Time

By default, a working day is a calendar day: a shift that starts at 10:00 PM and ends at 6:00 AM is recorded as time on two separate dates. **Cross-Day Working Time** changes that, so the whole shift counts as one working day dated by the day it started.

Turn it on in **Settings → Workplace → Cross-day Working Time**.

| Setting                    | What it does                                                                                                                            | Default      |
| -------------------------- | --------------------------------------------------------------------------------------------------------------------------------------- | ------------ |
| **Cross-day Working Time** | Master switch. When off, every working day ends at midnight, exactly as before.                                                         | Off          |
| **Carryover Limit**        | Hours a working day can run before it closes regardless of activity.                                                                    | 16 hours     |
| **Carryover Grace**        | Extra hours past the carryover limit during which activity still belongs to the previous working day.                                   | 4 hours      |
| **Idle Gap Threshold**     | How long someone has to be inactive for that gap to end the working day, once the carryover limit is reached.                           | 4 hours      |
| **Work-day Reset**         | **Elapsed time** — the limits above always apply. **Calendar date** — never end a working day while it is still on the date it started. | Elapsed time |

A working day therefore ends at whichever comes first: the carryover limit plus the grace window, or the carryover limit followed by an inactive gap at least as long as the idle gap threshold. Someone who works 10:00 PM to 6:00 AM and then signs off stays on one working day; someone who works overnight, sleeps, and starts again the next afternoon gets two.

{% hint style="warning" %}
**Auto Punch-Out must be off.** Cross-day working time and Auto Punch-Out contradict each other — Auto Punch-Out closes the day on a timer, which is exactly what cross-day is meant to avoid. While Auto Punch-Out is set to anything other than **Disabled**, the cross-day switch stays unavailable and the setting has no effect. Turn Auto Punch-Out off first.
{% endhint %}

{% hint style="info" %}
Changing these settings affects how activity is recorded from that point on. It does not re-date activity already recorded, so expect the change to show up going forward rather than in past dates.
{% endhint %}

## How-to Guides

### Shifts

<details>

<summary>Adding a Shift</summary>

1. Navigate to **Settings** and select the **Shifts** tab.
2. Click **Add Shift** at the top right.
3. Fill in the required fields in the popup:
   * **Name** -- A descriptive label (e.g., "Morning Shift", "Night Shift").
   * **Start Time** -- When the shift begins.
   * **End Time** -- When the shift ends.
   * **Grace Period (minutes)** -- Allowed buffer for late arrivals or early departures.
   * **Max Break Time (minutes)** -- Maximum total break duration permitted during the shift.
   * **Weekly Off** -- Select the days employees are not required to work. Tracking is disabled on weekly-off days.
4. Click **Submit**. A confirmation message confirms the shift was saved.

</details>

<details>

<summary>Editing a Shift</summary>

1. Locate the shift in the list and click its pencil icon.
2. Modify any field (name, start/end time, grace period, max break time, weekly off).
3. Click **Submit** to save.

</details>

<details>

<summary>Assigning a Shift to a Team</summary>

1. Navigate to **Settings > Teams**.
2. Select the target team from the list.
3. Under the **Team Info** tab, use the **Shift** dropdown to select the desired shift.
4. The change saves automatically with a confirmation message.

Shifts are assigned at the team level. All members of a team share the same shift schedule.

</details>

### Breaks

<details>

<summary>Adding a Break</summary>

1. Navigate to **Settings** and select the **Breaks** tab.
2. Click **Add Break** at the top right.
3. Enter the **Break Name** and **Max Break Time (minutes)** in the popup. Both are mandatory.
4. Click **Submit**.

</details>

<details>

<summary>Editing a Break</summary>

1. Click the pencil icon next to the break you want to modify.
2. In the popup you can change the break name, max break time, and toggle the break's active status.
3. Click **Submit** to save.

{% hint style="info" %}
Breaks cannot be deleted. To retire a break, toggle its status to **Inactive**. Inactive breaks are no longer available to employees.
{% endhint %}

</details>

### Wellness

<details>

<summary>Setting Healthy Working Hours</summary>

The wellness configuration lets administrators define the ideal daily working-hours range for the organization. This range is used across the platform to classify employees as healthy, overburdened, or underutilized.

1. Navigate to **Settings > Workplace**.
2. Use the dual-handle slider to set the minimum and maximum healthy working hours per day (scale: 0 to 23 hours).
3. Click **Save**.

**Terminology:**

* **Underutilized** -- Employees who work fewer hours than the set minimum.
* **Overburdened** -- Employees who work more hours than the set maximum.
* **Healthy** -- Employees whose daily working hours fall within the defined range.

</details>


# Productivity

We360.ai productivity settings — classify app and URL tracking behavior, set goals, and define productivity thresholds.

The **Productivity Settings** configuration acts as the intelligence layer for We360.ai. Raw tracking data (e.g., active window titles or URLs) is meaningless without context. This section provides that context.

## Application & Domain Policies

The heart of the tracking engine is categorization.

* Define which applications and domains are universally considered **Productive**, **Neutral**, or **Unproductive** across the entire organization.
* **Role-Based Overrides**: We360.ai recognizes that "Productive" means different things to different teams. You can configure overrides so that *Facebook.com* is flagged as "Productive" for the Marketing team, but "Unproductive" for the Engineering department.

## Category Mapping

To streamline the overwhelming amount of software in use today, map individual applications into broader categories (e.g., *GitHub* and *VS Code* map to "Development Tools," while *Slack* and *Teams* map to "Communication"). These categories power the high-level dashboards in the Productivity Suite.

## Goal Setting

We360.ai shifts the focus from simply working *longer* to working *smarter*.

* Establish target productivity percentages (e.g., a goal of 70% productive time per shift).
* Establish activity score baselines that employees should strive to meet, gamifying the effort to remain engaged.

## How-to Guides

### Application Policies

<details>

<summary>Creating an Application Policy</summary>

An application policy defines which categories count as productive, unproductive, or neutral for a specific team context.

1. Navigate to **Settings > Productivity Rules**. The page shows existing policies on the left and category labels on the right. The **Application Policy** and **Mapping** tabs are at the top.
2. Click the **purple plus icon** to add a new policy.
3. Enter the **Application Policy Name** (mandatory) and click **Submit**.
4. Select the newly created policy. On the right, assign each category a label: **Productive**, **Unproductive**, or **Neutral**.

{% hint style="info" %}
Consider naming the policy after the team it will serve (e.g., "Design Team Policy") to simplify assignment later.
{% endhint %}

After creating the policy:

* Assign it to a team (see below).
* Map applications and URLs to categories so the labels take effect.

</details>

<details>

<summary>Editing an Application Policy</summary>

You can make two types of edits:

**Rename the policy:**

1. Click the pencil icon next to the policy name.
2. Change the name in the popup and click **Submit**.

**Reassign category labels:**

1. Select the policy.
2. For each category on the right, switch between the **Productive**, **Unproductive**, and **Neutral** labels as needed.

Changes save immediately.

</details>

<details>

<summary>Assigning a Policy to a Team</summary>

1. Navigate to **Settings > Teams**.
2. Select the target team.
3. Under the **Team Info** tab, open the **Application Policy** dropdown.
4. Select the desired policy. A confirmation message confirms the assignment.

</details>

### Category Mapping

<details>

<summary>Mapping Applications and URLs to Categories</summary>

1. Navigate to **Settings > Productivity Rules** and switch to the **Mapping** tab.
2. The tab lists all applications and URLs observed across your organization. Each entry has a category dropdown.
3. Select the appropriate category for each app or URL.
4. Use the **All / Mapped / Unmapped** filter buttons to focus on entries that still need categorization.

{% hint style="warning" %}
Regularly check the Mapping tab for newly detected applications and URLs. Unmapped entries will not count toward productivity calculations.
{% endhint %}

</details>

<details>

<summary>Can I Create Custom Categories?</summary>

No. Categories are predefined and cannot be created or edited. They serve as fixed groupings (e.g., Social Media, Streaming, Chat & Messaging) that organize applications and URLs by purpose.

</details>


# Emails & Alerts

We360.ai email and alert settings — automate workforce analytics reports and configure employee monitoring notifications.

Managers shouldn't need to constantly live inside the We360.ai portal to stay informed. the **Emails & Alerts** module is designed to proactively push critical data to the people who need it.

<details>

<summary>Automated Email Reports</summary>

* Schedule routine data exports without manual intervention.
* Configure the portal to automatically construct and email Daily, Weekly, or Monthly Attendance and Productivity summaries directly to departmental managers or C-level executives.
* Choose exactly which metrics to include and at what time the email should dispatch.

</details>

<details>

<summary>Alert Rules</summary>

We360.ai acts as an automated supervisor. Instead of combing through logs, you can define **Alert Rules** that trigger instant notifications when specific, predefined conditions are met.

* **Productivity Triggers**: Generate an alert if an employee's Idle Time exceeds a certain threshold, or if they spend more than X minutes on an "Unproductive" application.
* **Attendance Triggers**: Notify managers instantly if an employee clocks in late, punches out early, or if they skip a mandatory shift.
* **Security Triggers**: Receive immediate warnings if an employee attempts to access a blacklisted URL.

</details>

## How-to Guides

### Alert Rules

<details>

<summary>Adding an Alert Rule</summary>

1. Navigate to **Settings** and select the **Alert Rules** tab. The existing rules are displayed in a table.
2. Click **Add Alert Rule** at the top right.
3. Fill in the popup form:
   * **Alert Rule Name** -- A descriptive label.
   * **Description** -- What the alert monitors.
   * **Alert Rule Type** -- Choose **Application**, **URL**, or **Overtime Break**.
   * **Send Email to** -- Select the email recipients for notifications.
4. Depending on the selected type, additional fields appear:
   * **Application** -- Pick target apps from the App Names dropdown.
   * **URL** -- Select target URLs from the URLs dropdown.
   * **Overtime Break** -- Choose the team and break type from their respective dropdowns.
5. Click **Submit**. A confirmation message confirms the rule was created.

</details>

<details>

<summary>Editing an Alert Rule</summary>

1. Click the pencil icon next to the alert rule.
2. Modify any field in the popup.
3. Click **Submit** to save.

</details>

<details>

<summary>Cloning an Alert Rule</summary>

Cloning lets you duplicate an existing rule as a starting point for a new one with minor modifications.

1. Click the clone action button next to the rule you want to duplicate.
2. Adjust the pre-filled fields in the popup as needed.
3. Click **Submit**. The cloned rule appears in the list alongside the original.

</details>


# Compliance & Security

We360.ai compliance and security — audit logs, stealth monitoring controls, URL blocking, and data privacy settings.

Due to the sensitive nature of workforce analytics, maintaining a secure and legally compliant tracking environment is critical. The **Compliance & Security** settings govern how tracking operates on the endpoint device.

## Access & Tracking Configs

<details>

<summary>Agent Configuration</summary>

* **Stealth Mode vs. Standard Mode**: Choose your organization's philosophy. Standard Mode provides employees with a visible Desktop Agent, allowing them to manually pause tracking or view their own stats. Stealth Mode (if legally permitted in your jurisdiction) installs the tracker silently in the background, operating entirely without UI interaction. Both modes deliver the same fully functional per-second tracking capabilities.
* **URL Blocking**: Enforce internet usage policies directly through the portal by creating blacklists of domains that the local agent should actively block access to.

</details>

<details>

<summary>Audit Logs</summary>

Who watches the watchers?

* The **Audit Logs** maintain a permanent, unalterable record of every single administrative action taken within the We360.ai Web Portal.
* If a tenant manager changes a productivity rule, deletes a user, or edits a timesheet, the precise timestamp and the actor's ID are logged here.

</details>

## Compliance Toggles

The compliance section provides organization-wide privacy and security controls:

| Setting                        | Description                                                                                                                                                                 |
| ------------------------------ | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Screenshot Capture**         | Enable or disable screenshot capture across the entire organization. Turning this off prevents any screenshots from being taken, regardless of team or user-level settings. |
| **Screenshots Download**       | When disabled, no portal user can download screenshots, adding a layer of protection against unauthorized distribution of sensitive screen content.                         |
| **Allow We360 Support Access** | Grant the We360.ai support team administrative access to your account for troubleshooting and configuration assistance. This can be revoked at any time.                    |
| **Video Recording**            | Enable or disable session video recording across the organization.                                                                                                          |
| **External USB Detection**     | Enable detection and logging of external USB device connections on monitored endpoints for data loss prevention.                                                            |

### Data Loss Prevention (DLP)

We360.ai includes built-in Data Loss Prevention capabilities to help organizations detect and prevent unauthorized data exfiltration. USB device monitoring, application usage auditing, and screen capture work together to provide comprehensive DLP coverage. Combined with HIPAA compliance, these features make We360.ai suitable for regulated industries including healthcare.

{% hint style="info" %}
These toggles apply organization-wide and override any team-level or user-level tracking configurations where applicable.
{% endhint %}


# Integrations

We360.ai integration settings for connecting HR systems, collaboration and project tools, and the data API.

The **Integrations** settings view manages the *connections* between We360.ai and the external systems your organization already uses. It's the conceptual counterpart to the step-by-step setup guide in the Administration space; for how to configure each connection, see [Administration → Integrations](https://docs.we360.ai/administration/settings-center/integrations).

* **HR & attendance systems**: Keep attendance in sync with your HRMS. Push punch logs to GreytHR, Zoho People, and Keka; and fetch attendance and employee attributes from Keka.
* **Collaboration & project tools**: Reflect Microsoft Teams meeting time in productivity analytics, and sync projects, tasks, and worklogs with Jira.
* **Direct API access**: Generate an access token to pull We360.ai data into your own scripts, dashboards, or reporting tools.
* **Custom integrations**: We360.ai also builds tailored integrations—including additional HRMS systems such as Workday, payroll pipelines, project and task platforms, and case-management systems. Contact the We360.ai team to discuss your requirements.


# UI Settings

We360.ai UI settings — customize portal layout, default views, and visualization preferences for workforce analytics.

The **UI Settings** afford Tenant Owners the ability to tweak the visual and structural defaults of the We360.ai portal for all their users.

* **Default Views**: Force specific visual layouts as the default experience (e.g., standardizing the Timeline view to list formats over graph formats for lower-bandwidth environments).
* **Reporting Defaults**: Select which column headers or custom fields are displayed by default across the various data tables within the app, reducing the need for managers to manually customize their grids upon every login.


# IT Ops

IT ops guides for We360.ai — agent deployment, endpoint management, network security, and infrastructure setup for system admins.

Technical documentation for IT teams deploying and managing <code class="expression">space.vars.company\_name</code> infrastructure.

<table data-view="cards"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-download">:download:</i></td><td><strong>Agent Deployment Hub</strong></td><td>Manual installation, mass deployment, and mobile deployment guides for all platforms.</td><td><a href="/deployment-and-it-ops/deployment/agent-deployment-hub">Agent Deployment Hub</a></td></tr><tr><td><i class="fa-gears">:gears:</i></td><td><strong>Agent Runtime &#x26; Update Reference</strong></td><td>Runtime components, log locations, how auto-update works, and local commands to inspect it.</td><td><a href="/deployment-and-it-ops/deployment/agent-runtime-and-updates">Agent Runtime &amp; Update Reference</a></td></tr><tr><td><i class="fa-building">:building:</i></td><td><strong>Infrastructure Management (On-Premise)</strong></td><td>Complete guide for on-premise infrastructure setup and management.</td><td><a href="/deployment-and-it-ops/deployment/infrastructure-management-on-premise">On-Premise and BYOC</a></td></tr><tr><td><i class="fa-cloud">:cloud:</i></td><td><strong>Infrastructure Management (Cloud)</strong></td><td>Complete guide for cloud infrastructure setup and management.</td><td><a href="/deployment-and-it-ops/deployment/infrastructure-management-cloud">Cloud</a></td></tr><tr><td><i class="fa-plug">:plug:</i></td><td><strong>Integrations</strong></td><td>Portal-managed integrations and OAuth guidance for direct API access.</td><td><a href="/deployment-and-it-ops/integrations-and-api-access/integrations">Integrations</a></td></tr><tr><td><i class="fa-shield">:shield:</i></td><td><strong>Network &#x26; Security Hardening</strong></td><td>Firewall allowlists, AV/EDR exclusions, and security best practices.</td><td><a href="/deployment-and-it-ops/security-and-hardening/network-and-security-hardening">Network &amp; Security Hardening</a></td></tr><tr><td><i class="fa-stethoscope">:stethoscope:</i></td><td><strong>Desktop Doctor</strong></td><td>Diagnostic utility for on-machine triage — network, AV, process, database, and log collection.</td><td><a href="/deployment-and-it-ops/troubleshooting-and-support/desktop-doctor">Desktop Doctor</a></td></tr><tr><td><i class="fa-magnifying-glass">:magnifying-glass:</i></td><td><strong>Tracker Failure Diagnostic Guide</strong></td><td>Identify and resolve the most common causes of agent failure: installation, auth, network, AV, and data capture issues.</td><td><a href="/deployment-and-it-ops/troubleshooting-and-support/tracker-failure-guide">Tracker Failure Diagnostic Guide</a></td></tr></tbody></table>


# Agent Deployment Hub

Deploy the We360.ai MyZen monitoring agent with manual installation, direct download links, MSI and EXE command-line setup, GPO, Intune, MDM, and mobile deployment guides.

Use this hub to deploy the We360.ai MyZen agent across Windows, macOS, Linux, Android, and iOS devices. It covers manual installation, silent deployment, direct download links, and enterprise rollout methods.

<table data-column-title-hidden data-view="cards" data-full-width="false"><thead><tr><th></th><th></th><th></th><th data-hidden data-card-target data-type="content-ref"></th></tr></thead><tbody><tr><td><i class="fa-download">:download:</i></td><td><strong>Download Links</strong></td><td>Links for various installers and utilities</td><td><a href="/deployment-and-it-ops/deployment/agent-deployment-hub/download-links">Download Links &amp; Utilities</a></td></tr><tr><td><i class="fa-hand-pointer">:hand-pointer:</i></td><td><strong>Manual Installation</strong></td><td>Steps for Windows, macOS, and Linux. Stealth and Standard modes. Requirements and uninstall methods.</td><td><a href="/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation">Manual Installation</a></td></tr><tr><td><i class="fa-rocket">:rocket:</i></td><td><strong>Mass Deployment</strong></td><td>MDMs, MSI/GPO, SCCM, and Microsoft Intune configuration. Software updates and mass uninstallation.</td><td><a href="/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment">Mass Deployment</a></td></tr><tr><td><i class="fa-mobile">:mobile:</i></td><td><strong>Mobile Deployment</strong></td><td>Setting up MDM for Android/iOS field tracking.</td><td><a href="/deployment-and-it-ops/deployment/agent-deployment-hub/mobile-deployment">Mobile Deployment</a></td></tr></tbody></table>


# Download Links & Utilities

Download We360.ai MyZen agent installers and utilities for Windows, macOS, Linux, Android, iOS, and Chrome. Get direct download links for employee monitoring software deployment.

All We360.ai agent downloads are available from `https://portal.we360.ai`. Use this page to download MyZen installers and deployment utilities for Windows, macOS, Linux, Android, iOS, and Chrome.

It includes direct download links for EXE, MSI, PKG, DMG, shell, and cleanup tools used in employee monitoring software deployment.

Administrators can open the Download page from the **Download Apps** button in the top bar. For step-by-step setup, use [Manual Installation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation), [Command Line / MSI / EXE](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/command-line-msi), or [Direct Link](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/direct-link).

The following tables list all available We360.ai download links and utilities.

## Desktop Agent Downloads

<table><thead><tr><th width="240.20703125">Platform</th><th width="105.63671875">Type</th><th width="173.82421875">Format</th><th>Direct Download</th></tr></thead><tbody><tr><td><i class="fa-windows">:windows:</i> Windows</td><td>Standard</td><td>EXE</td><td><a href="https://portal.we360.ai/static/installers/MyZenV2-setup.exe">MyZenV2-setup.exe</a></td></tr><tr><td><i class="fa-windows">:windows:</i> Windows</td><td>Standard</td><td>MSI</td><td><a href="https://portal.we360.ai/static/installers/MyZenV2.msi">MyZenV2.msi</a></td></tr><tr><td><i class="fa-windows">:windows:</i> <a data-footnote-ref href="#user-content-fn-1">Windows</a></td><td>Stealth*</td><td>EXE</td><td><a href="https://portal.we360.ai/static/installers/zs-setup.exe">zs-setup.exe</a></td></tr><tr><td><i class="fa-windows">:windows:</i> Windows</td><td>Stealth*</td><td>MSI</td><td><a href="https://portal.we360.ai/static/installers/zs.msi">zs.msi</a></td></tr><tr><td><i class="fa-apple">:apple:</i> macOS (Intel)</td><td>Standard</td><td>PKG</td><td><a href="https://portal.we360.ai/static/installers/MyZenV2-amd64.pkg">MyZenV2-amd64.pkg</a></td></tr><tr><td><i class="fa-apple">:apple:</i> macOS (Intel)</td><td>Standard</td><td>DMG</td><td><a href="https://portal.we360.ai/static/installers/MyZenV2-amd64.dmg">MyZenV2-amd64.dmg</a></td></tr><tr><td><i class="fa-apple">:apple:</i> macOS (Apple Silicon)</td><td>Standard</td><td>PKG</td><td><a href="https://portal.we360.ai/static/installers/MyZenV2-arm64.pkg">MyZenV2-arm64.pkg</a></td></tr><tr><td><i class="fa-apple">:apple:</i>macOS (Apple Silicon)</td><td>Standard</td><td>DMG</td><td><a href="https://portal.we360.ai/static/installers/MyZenV2-arm64.dmg">MyZenV2-arm64.dmg</a></td></tr><tr><td><i class="fa-apple">:apple:</i>macOS (Intel)</td><td>Stealth*</td><td>PKG</td><td><a href="https://portal.we360.ai/static/installers/zs-amd64.pkg">zs-amd64.pkg</a></td></tr><tr><td><i class="fa-apple">:apple:</i>macOS (Apple Silicon)</td><td>Stealth*</td><td>PKG</td><td><a href="https://portal.we360.ai/static/installers/zs-arm64.pkg">zs-arm64.pkg</a></td></tr><tr><td><i class="fa-ubuntu">:ubuntu:</i> Ubuntu (64-bit Intel)</td><td>Stealth*</td><td><a data-footnote-ref href="#user-content-fn-2">SH</a></td><td><a href="https://portal.we360.ai/static/installers/zs-amd64.sh">zs-amd64.sh</a></td></tr></tbody></table>

{% hint style="info" %}

* Stealth downloads are restricted to users with **Tenant Owner** permissions. Standard EXE downloads are available to all authenticated users.
  {% endhint %}

{% hint style="danger" %}
Stealth installer are not meant to be used as is. They are lacking the installer license key and the unique key can be determined from an older version of installer or stealth key downloaded from the portal.

* SHELL and EXE, PKG files need to be renamed to the \<stealth\_license\_key>.\<extension>
  {% endhint %}

## Mobile App Downloads

| Platform | Link                                                                                       |
| -------- | ------------------------------------------------------------------------------------------ |
| Android  | [Google Play Store](https://play.google.com/store/apps/details?id=com.zenstack.we360.ai)   |
| iOS      | [Apple App Store](https://apps.apple.com/in/app/we360-ai-workforce-analytics/id6455370600) |

## Browser Extension Download

| Browser | Link                                                                                                                    |
| ------- | ----------------------------------------------------------------------------------------------------------------------- |
| Chrome  | [Chrome Web Store](https://chromewebstore.google.com/detail/we360ai-workforce-product/eainhghihghonimoemjhiimpkfejkgbd) |

## Deployment and Cleanup Utilities

Use these utilities for scripted installation, deep cleanup, macOS uninstall, and Windows installation troubleshooting.

| Utility                                     | Platform              | Architecture | Direct Download                                                                       |
| ------------------------------------------- | --------------------- | ------------ | ------------------------------------------------------------------------------------- |
| **macOS Uninstall (pkg)**                   | macOS                 | Universal    | [zen-uninstall.pkg](https://portal.we360.ai/static/installers/zen-uninstall.pkg)      |
| **Zen Cleanup Utility**                     | Windows               | amd64        | [zen\_cleanup.exe](https://portal.we360.ai/static/utils/windows/zen_cleanup.exe)      |
| **Zen Cleanup Utility**                     | macOS (Intel)         | amd64        | [zen\_cleanup](https://portal.we360.ai/static/utils/mac_amd64/zen_cleanup)            |
| **Zen Cleanup Utility**                     | macOS (Apple Silicon) | arm64        | [zen\_cleanup](https://portal.we360.ai/static/utils/mac_arm64/zen_cleanup)            |
| **Zen Cleanup Utility**                     | Linux                 | amd64        | [zen\_cleanup](https://portal.we360.ai/static/utils/linux_amd64/zen_cleanup)          |
| **Zen Cleanup Utility**                     | Linux                 | arm64        | [zen\_cleanup](https://portal.we360.ai/static/utils/linux_arm64/zen_cleanup)          |
| **Zen Online Installer (zs\_manager)**      | Windows               | amd64/arm64  | [zs\_manager.exe](https://portal.we360.ai/static/utils/windows/zs_manager.exe)        |
| **Powershell Stealth Install Script (PS1)** | Windows               | amd64/arm64  | [MyZenInstall.ps1](https://portal.we360.ai/static/scripts/MyZenInstall.ps1)           |
| **Installation Debugger**                   | Windows               | amd64/arm64  | [test-msi.ps1](https://portal.we360.ai/static/scripts/test-msi.ps1)                   |
| **macOS Stealth Install Script (Shell)**    | macOS (All)           | amd64/arm64  | [zs-macos.sh](https://portal.we360.ai/static/scripts/zs-macos.sh)                     |
| **macOS Uninstall Script (Shell)**          | macOS (All)           | amd64/arm64  | [zs-uninstall-macos.sh](https://portal.we360.ai/static/scripts/zs-uninstall-macos.sh) |

**Zen Online Installer (zs\_manager) -** A web-installer utility: resolves the correct agent installer for the machine's tenant, downloads it, and installs it silently (`/updater-standard` or `/updater-stealth`, with a `--dry-run` mode). Work in progress — intended for support and IT tooling, not end users. See [Agent Runtime & Update Reference](/deployment-and-it-ops/deployment/agent-runtime-and-updates#zs_manager-online-installer-utility-windows).

**Zen Cleanup -** Completely removes all MyZen traces from a system, including registry entries, launch agents/daemons, processes, and application files. Use only when you want a full removal of everything related to MyZen.

{% hint style="warning" %}
The **Zen Cleanup Utility** performs a deep clean and removes all MyZen-related files, processes, and configuration. Only use it if you intend to completely remove MyZen from the system. It cannot be undone.
{% endhint %}

## Desktop Doctor Downloads

Desktop Doctor is a diagnostic utility for troubleshooting agent issues. Run it on any affected machine to check network connectivity, AV interference, agent status, and collect logs for support. See [Desktop Doctor](/deployment-and-it-ops/troubleshooting-and-support/desktop-doctor) for usage instructions.

| Platform              | Download                                                                                                                  |
| --------------------- | ------------------------------------------------------------------------------------------------------------------------- |
| Windows               | [Desktop-Doctor.exe](https://portal.we360.ai/static/desktop-doctor/windows-gui/Desktop-Doctor.exe)                        |
| macOS (Apple Silicon) | [Desktop-Doctor.app.zip](https://portal.we360.ai/static/desktop-doctor/darwin-gui/darwin-arm64/Desktop-Doctor.app.zip)    |
| macOS (Intel)         | [Desktop-Doctor.app.zip](https://portal.we360.ai/static/desktop-doctor/darwin-gui/darwin-amd64/Desktop-Doctor.app.zip)    |
| Linux (x86\_64)       | [Desktop-Doctor-x86\_64.AppImage](https://portal.we360.ai/static/desktop-doctor/linux-gui/Desktop-Doctor-x86_64.AppImage) |

***

## Important Notes for Stealth Installer Downloads

{% hint style="danger" %}
**Never rename stealth installer files.** The stealth installer filename is encoded with your organization's license key. Renaming the file or allowing extra characters to be appended (e.g. `(1)` or `(2)` from duplicate downloads) will cause the installation to fail or invalidate the license. Always use the file exactly as downloaded.
{% endhint %}

* Stealth installers should not be shared directly with employees, as they may extract the embedded license key or misuse the installer.
* For stealth deployments, prefer administrator-controlled methods: GPO, Intune, MDM, or command-line installation.

[^1]: The installer needs to be renamed to work on a fresh system

[^2]: (Save the file if not downloaded automatically)


# Installation & Update Architecture

This page explains **how the desktop agent installs and updates itself** on Windows and macOS — what runs, in what order, where files land, and how updates are triggered and applied. It is a reference for IT/security teams who need to understand the moving parts behind the step-by-step deployment guides.

There are two flavours of the agent:

* **Standard** (`MyZenV2`) — visible, interactive app.
* **Stealth** (`zs`) — headless. A background **service monitor** (`svcmonitor`) supervises the tracker, applies admin commands, and performs updates.

Both flavours share the same Go tooling and the same per-tenant key configuration (`zs.json`, the tenant id + key the installer is bound to).

***

## Windows — installation

### Primary path: self-contained installer (`zs-setup.exe`)

The recommended installer is a single self-contained executable with the entire application payload embedded inside it, so it installs **fully offline** with no download step.

1. **Resolve the tenant key config.** The installer determines which tenant it belongs to from (in order) an `installer-sources.json` beside it, an installer text marker, the executable's own (encoded) filename, or an existing `C:\Windows\System32\zs.json`.
2. **Elevate to administrator** (UAC prompt if not already elevated).
3. **Write the key config** to the canonical path `C:\Windows\System32\zs.json` so the agent and service always read the current tenant binding (this happens on update/repair too, replacing a stale config).
4. **Extract & validate the payload**, with a short settle delay so antivirus can inspect files before they're used.
5. **Place files atomically with rollback** (stage `.new`, move current to `.old`, rename into place; restore on failure) — resilient to AV locks/quarantine.
6. **Register and start the Windows service** (`svcmonitor`) with crash-recovery, write install registry keys, and add outbound firewall rules.

### Legacy path: MSI (Advanced Installer)

An MSI (`zs.msi` / `MyZenV2.msi`) is still produced for enterprise deployment via Group Policy / SCCM / Intune. It lays down the same file layout and service. New deployments should prefer the self-contained `zs-setup.exe` for offline/air-gapped scenarios. (The `configure_user.exe` helper is **no longer shipped** in either path — onboarding now runs in-process in the app.)

### Windows services

| Service                                      | Role                                                                                                                                                |
| -------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------- |
| **svcmonitor** (`C:\Windows\svcmonitor.exe`) | Supervises the tracker, polls the server for admin commands, performs updates, ships logs on request. Auto-start, with `sc failure` crash recovery. |
| **svcrunner** (`C:\Windows\svcrunner.exe`)   | Companion that keeps svcmonitor alive across sessions/crashes.                                                                                      |

***

## macOS — installation

The agent ships as a signed, **notarized** `.pkg`, built per architecture (`amd64` and `arm64` — no universal binary, intentionally). Gatekeeper acceptance, stapling, and signature integrity are verified at build time.

The package installs the app bundle and runs a **postinstall** script that:

1. Stops any existing app/processes.
2. Resolves and writes the tenant key config to `/Library/Preferences/zs.json` (stealth uses a `keyconfig_check` helper that reads the tenant from the package's own name).
3. Renders **launchd** job definitions from templates and bootstraps them for the system and logged-in GUI users.

### launchd jobs

| Job                        | Flavour  | Type                   | Purpose                                          |
| -------------------------- | -------- | ---------------------- | ------------------------------------------------ |
| `ai.we360.MyZenV2`         | Standard | LaunchAgent (per user) | Starts the interactive app at login              |
| `ai.we360.MyZenV2-updater` | Standard | LaunchDaemon (system)  | Hourly update check                              |
| `ai.zs.zs`                 | Stealth  | LaunchAgent/Daemon     | Starts/keeps `svcmonitor` running                |
| `ai.zs.zs-updater`         | Stealth  | LaunchDaemon (system)  | Runs `svcmonitor updater` to check/apply updates |

***

## File locations

|                              | Windows                                                           | macOS                                                                  |
| ---------------------------- | ----------------------------------------------------------------- | ---------------------------------------------------------------------- |
| **Stealth app**              | `C:\Program Files\zs\zs\`                                         | `/usr/local/zs/zs.app`                                                 |
| **Standard app**             | `C:\Program Files\…` (MSI)                                        | `/Applications/MyZenV2.app`                                            |
| **Service binaries**         | `C:\Windows\svcmonitor.exe`, `svcrunner.exe`                      | inside the app bundle (`…/Contents/MacOS/svcmonitor`), run via launchd |
| **Tenant key config**        | `C:\Windows\System32\zs.json` (fallback `…\zs\zs\keyconfig.json`) | `/Library/Preferences/zs.json` (fallback `/etc/zs.json`)               |
| **Version file**             | `…\zs\zs\version.txt`                                             | `…/Contents/MacOS/version.txt`                                         |
| **Per-user config (tokens)** | `%APPDATA%\ai.zs\zs.ini`                                          | `~/.config/ai.zs/zs.ini`                                               |
| **App data / logs**          | `%APPDATA%\ai.zs\zs\`                                             | `~/Library/Application Support/ai.zs/zs`                               |

> A custom key-config path can be supplied via the `ZS_KEY_CONFIG` environment variable (used by always-on mode); it overrides the platform default path.

***

## Updates

Updates are **server-led and per-tenant**, with a build-time fallback URL. The agent never auto-downgrades by accident.

### How an update is decided

1. **Resolve the installer URL** for this tenant: `GET https://origin.in.we360.ai/discover/v1/tenant/<id>/download-urls/` (cached in-process). If unavailable, fall back to the per-brand build-time base URL.
2. **Check the auto-update gate** (`auto_update` per tenant). If disabled, the updater no-ops.
3. **Compare versions** with a strict semver gate — an update installs only when the published version is **higher** than the installed one. (Intentional rollbacks require publishing a new build with the older bits.)
4. **Verify integrity** — the download's MD5 is checked against the published `.version` sidecar; a mismatch aborts the install.

### How an update is applied

* **Windows:** `svcmonitor` re-runs the self-contained `zs-setup.exe` (downloaded for this tenant), which stops the service, performs the same atomic file swap as a fresh install, and recreates/starts the service. MSI assets are applied via `msiexec /i … /qn /norestart`.
* **macOS:** the `*-updater` launchd job runs the updater, which downloads the per-arch `.pkg` and installs it system-wide via `/usr/sbin/installer -pkg … -target /`. The stealth updater encodes the tenant key config into the package path so postinstall can re-bind the tenant.

### Cadence & triggers

* **Standard (macOS):** hourly via the updater LaunchDaemon.
* **Stealth (both OS):** `svcmonitor` checks on a timer (only while a user session is active) and also honours an on-demand **`UPDATE`** admin command delivered through the service-state channel.
* **Skip markers:** developer/opt-out markers on disk cause the updater to no-op (used for dev machines and temporary holds).

***

## Related

* Step-by-step install guides: **Manual Installation** (Windows/macOS, standard/stealth).
* Mass deployment: **Mass Deployment** (GPO, Intune, MDM, command-line MSI).
* Network behaviour & endpoints: **Network & Security Hardening → Stealth App — Server Communication (v4.13+)**.


# Manual Installation

Manual installation guides for the We360.ai MyZen agent on Windows and macOS, including Standard and Stealth setup for employee monitoring software deployment.

Use these guides to manually install the We360.ai MyZen desktop agent on individual Windows, macOS, and Linux devices. Choose the setup guide that matches your operating system and deployment mode.

## Deployment Modes

| Mode         | Visibility                                              | Use Case                                                     |
| ------------ | ------------------------------------------------------- | ------------------------------------------------------------ |
| **Standard** | Visible to the employee (system tray icon, punch-in UI) | Transparent monitoring with employee self-service            |
| **Stealth**  | Hidden from the employee                                | Discrete monitoring where employee awareness is not required |

## Windows

| Guide                                                                                                                    | Audience             |
| ------------------------------------------------------------------------------------------------------------------------ | -------------------- |
| [Standard Installation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/windows-standard)     | Admins and employees |
| [Stealth Installation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/windows-stealth)       | Admins only          |
| [Uninstallation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/windows-uninstallation)      | Admins only          |
| [Installation Validation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/windows-validation) | Admins only          |
| [FAQ](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/windows-faq)                            | Admins and employees |

## macOS

| Guide                                                                                                                  | Audience             |
| ---------------------------------------------------------------------------------------------------------------------- | -------------------- |
| [Standard Installation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/macos-standard)     | Admins and employees |
| [Stealth Installation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/macos-stealth)       | Admins only          |
| [Uninstallation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/macos-uninstallation)      | Admins only          |
| [Installation Validation](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/macos-validation) | Admins only          |
| [FAQ](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/macos-faq)                            | Admins and employees |

## Linux

| Guide                                                                                                                   | Audience    |
| ----------------------------------------------------------------------------------------------------------------------- | ----------- |
| [Installation (Stealth)](/deployment-and-it-ops/deployment/agent-deployment-hub/manual-installation/linux-installation) | Admins only |


# Windows Standard Installation

Install We360.ai MyZen Standard agent on Windows — employee monitoring software installation guide with setup steps.

## Prerequisites

| Requirement      | Detail                                                                                                                                                                                                                                           |
| ---------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| **OS**           | Windows 10 or later (Windows 8 is end-of-life; Windows 10+ is recommended)                                                                                                                                                                       |
| **Hardware**     | Minimum: any x86-64 machine. Recommended: 8 GB RAM, SSD                                                                                                                                                                                          |
| **Admin rights** | Not required for Standard mode                                                                                                                                                                                                                   |
| **Antivirus**    | Add an exception for the MyZen process and install directory if a third-party AV or Windows Firewall is active (see [AV and EDR Exclusions](/deployment-and-it-ops/security-and-hardening/network-and-security-hardening/av-and-edr-exclusions)) |

## Download the Installer

1. Log in to the We360.ai web portal.
2. Click the **Download Apps** button in the top bar.
3. In the **Windows** section, click **Standard** to download `MyZenV2-setup.exe`.

> **Tip:** Employees can also download Standard mode themselves after logging in with the credentials provided in their welcome email.

## Install

1. Open the `MyZenV2-setup.exe` file from your Downloads folder (do **not** rename the file).
2. If a Windows SmartScreen prompt appears, click **Yes** to allow the installation.
3. The installer runs silently and closes automatically when finished.
4. The MyZen app window appears. Enter your **Workspace** name and click **Sign in**.
5. Enter your **Email** and **Password** on the sign-in page.
6. Return to the MyZen desktop app via the taskbar icon and click **Punch In** to begin tracking.

### Post-Installation Notes

* After signing in, the employee must punch in before closing or minimising the window. MyZen continues running in the system tray.
* Employees must **Punch Out** before they can log out.

## Automatic Updates

MyZen updates itself automatically in the background. No manual intervention is required.

## Install Locations (Reference)

| Item                  | Path                                            |
| --------------------- | ----------------------------------------------- |
| Application directory | `C:\Program Files\Zenstack\MyZenV2\`            |
| Version file          | `C:\Program Files\Zenstack\MyZenV2\version.txt` |


# Windows Stealth Installation

Install We360.ai MyZen Stealth agent on Windows — silent employee monitoring setup with background service deployment.

## Prerequisites

| Requirement      | Detail                                                               |
| ---------------- | -------------------------------------------------------------------- |
| **OS**           | Windows 10 or later                                                  |
| **Admin rights** | **Required** for Stealth mode                                        |
| **Antivirus**    | Add an exception for the MyZen stealth process and install directory |

{% hint style="danger" %}
**Never rename the stealth installer file.** The encoded filename contains your organization's license key and configuration. Renaming it or allowing extra characters to be appended (e.g. `(1)` from duplicate downloads) will cause the installation to fail. Use the file exactly as downloaded.
{% endhint %}

## Download the Installer

1. Log in to the We360.ai web portal as an administrator.
2. Click the **Download Apps** button in the top bar.
3. In the **Windows** section, click **Stealth** to download the installer (filename is a Base64-encoded string ending in `.exe`).

## Install

1. Locate the setup file (e.g. `<encoded-name>.exe`) in your Downloads folder and double-click it.
2. A Windows SmartScreen dialog appears. Click **More info**.
3. Click **Run anyway** to continue.
4. A UAC prompt appears. Click **Yes** to confirm and start installation.
5. The installer runs silently. No application window opens because MyZen is in stealth mode.

### Post-Installation Notes

* Stealth mode does not show a visible application or system tray icon to the employee.
* Consider clearing browser download history on the target machine if confidentiality is required.

## Install Locations (Reference)

| Item                  | Path                                 |
| --------------------- | ------------------------------------ |
| Application directory | `C:\Program Files\zs\zs\`            |
| Version file          | `C:\Program Files\zs\zs\version.txt` |
| Process name          | `MyZenV2s.exe`                       |
| Background service    | `zsrvc`                              |
| Watchdog service      | `C:\Windows\svcmonitor.exe`          |
| Service host process  | `C:\Windows\svcrunner.exe`           |

{% hint style="info" %}
Both `svcmonitor` and `svcrunner` run as **Local System**. `svcmonitor` is a watchdog that automatically restarts the agent if terminated. `svcrunner` is the Windows service host.
{% endhint %}


# Windows Uninstallation

Uninstall We360.ai MyZen agent from Windows — Control Panel, command line, and Stealth mode removal instructions.

## Standard Uninstallation (GUI)

1. Open **Control Panel**.
2. Navigate to **Programs and Features** (or search for "Uninstall a program").
3. Locate **MyZenV2** in the list and click it.
4. Click **Uninstall** in the top menu bar.
5. Confirm by clicking **Yes** on the prompt.
6. Select **Remove all components** and click **Next**.
7. Click **Uninstall**.
8. Click **Finish** when the process completes.

## Silent Uninstallation (Command Line)

To silently uninstall via the MSI installer, run the following in an elevated Command Prompt or PowerShell:

```powershell
MSIEXEC /x <installer-filename>.msi /QN
```

Replace `<installer-filename>.msi` with the exact MSI filename used during installation. Do not rename the file.

> Quiet-mode flags accepted by MSIEXEC: `-Quiet`, `/Quiet`, `-Q`, `/Q`, `/QN`.

## Zen Cleanup Utility

If the standard uninstallation does not fully remove all MyZen components, or if you want to completely erase every trace of MyZen from the system, use the **Zen Cleanup Utility**.

{% hint style="warning" %}
Only use the Zen Cleanup Utility if you want to **completely remove everything** related to MyZen from the system. This includes all application files, registry entries, scheduled tasks, and services. This action cannot be undone.
{% endhint %}

The utility is available from the same download location as the agent installers. See [Download Links & Utilities](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links) for details.


# Windows Installation Validation

Verify We360.ai MyZen agent installation on Windows — check processes, services, and validate endpoint monitoring is active.

## Automated Verification Script (Stealth)

For scripted / bulk validation of a **stealth** install, use `zs-postverify.ps1`. It is brand-agnostic (it discovers the install directory rather than hardcoding it, so it works whichever branded build is installed) and checks everything a manual pass would, in one run:

* The `svcmonitor` service exists **and** is `Running` — with an initial wait plus two retries (\~30s apart), since the service can take a moment to reach `Running` right after install.
* `svcrunner` is registered as `svcmonitor`'s recovery (failure) action — it is **not** a service of its own, so Windows starts it when `svcmonitor` fails. Whether it happens to be running is advisory only.
* Service binaries `C:\Windows\svcmonitor.exe` and `C:\Windows\svcrunner.exe`.
* The `MyZenV2s.exe` agent and its companions (`zen_cli.exe`, `cleanup_mgr.exe`, `version.txt`, `ffmpeg`).
* The tenant keyconfig (`C:\Windows\System32\zs.json`, or the in-tree fallback).
* The Visual C++ runtime files and minimum version.
* Whether the agent process is currently running.

Each check prints `[ PASS ]` / `[ FAIL ]` / `[ WARN ]` (WARN is advisory and never fails the run). The script **exits `0`** when all required checks pass, **`1`** otherwise — suitable for use as a post-install gate in RMM / MDM tooling. Add `-Json` for a machine-readable summary.

{% hint style="info" %}
The agent is 64-bit, so its files live in the real `C:\Windows\System32`. If your RMM / MDM tool runs the script from **32-bit** PowerShell, Windows silently redirects `System32` to `SysWOW64` — the script resolves the real path itself, so it reports correctly either way. No action needed on your side.
{% endhint %}

Save the script below as `zs-postverify.ps1` and run it from an **elevated** PowerShell prompt:

```powershell
powershell -ExecutionPolicy Bypass -File .\zs-postverify.ps1
```

To skip the initial wait for a quick manual check (e.g. long after install):

```powershell
powershell -ExecutionPolicy Bypass -File .\zs-postverify.ps1 -SvcMonitorInitialWaitSeconds 0 -SvcMonitorRetries 0
```

<details>

<summary>zs-postverify.ps1</summary>

```powershell
<#
.SYNOPSIS
    Post-install verification for the We360 / ZS stealth desktop agent on Windows.

.DESCRIPTION
    Verifies that a completed stealth ("zs") install is present and healthy.
    Brand-agnostic: it does NOT assume a particular branded
    install directory -- the shared, fixed pieces (the svcmonitor / svcrunner
    services under C:\Windows, the MyZenV2s.exe agent, the VC runtime, the
    keyconfig) are what an install is judged by, and the brand only changes the
    Program Files subdirectory, which is discovered rather than hardcoded.

    Every check prints [ PASS ] / [ FAIL ] / [ WARN ] / [ INFO ]. WARN checks
    are advisory (state that is legitimately variable, e.g. svcrunner can be
    Stopped by design once it has started the agent) and never fail the run.
    The script exits 0 when all required checks pass, 1 otherwise.

.PARAMETER Json
    Emit a machine-readable JSON summary to stdout instead of the human report.

.PARAMETER MinVcRuntimeVersion
    Minimum acceptable VC++ runtime version (msvcp140.dll). Defaults to the
    version the agent is built against.

.EXAMPLE
    powershell -ExecutionPolicy Bypass -File .\zs-postverify.ps1

.EXAMPLE
    powershell -ExecutionPolicy Bypass -File .\zs-postverify.ps1 -Json

.NOTES
    Run elevated (as Administrator) for complete results -- service state and the
    ProgramData install tree are not fully readable to a standard user.
#>

[CmdletBinding()]
param(
    [switch]$Json,
    [string]$MinVcRuntimeVersion = "14.42.34438",

    # svcmonitor can take a moment to reach Running right after install (AV
    # settle, service auto-start). We wait once, then re-check on an interval.
    [int]$SvcMonitorInitialWaitSeconds = 30,
    [int]$SvcMonitorRetryIntervalSeconds = 30,
    [int]$SvcMonitorRetries = 2
)

Set-StrictMode -Version Latest
$ErrorActionPreference = "Stop"

# ---------------------------------------------------------------------------
# Canonical, brand-agnostic install facts (mirrors pkg/apps/stealth/settings
# and pkg/system/os_windows.go in the desktop-app repo).
# ---------------------------------------------------------------------------
$SvcMonitorName   = "svcmonitor"
$SvcRunnerName    = "svcrunner"
$SvcMonitorBinary = "C:\Windows\svcmonitor.exe"
$SvcRunnerBinary  = "C:\Windows\svcrunner.exe"

# The stealth agent binary. Same file name across brands -- only its parent
# directory under "C:\Program Files\<brand>\zs" differs, so we discover it.
$AgentExeName     = "MyZenV2s.exe"

# Companion files expected alongside the agent in the install directory.
$CompanionFiles   = @("zen_cli.exe", "cleanup_mgr.exe", "version.txt")

# Under a 32-bit host process (plenty of RMM/MDM agents spawn 32-bit
# PowerShell) the WOW64 file-system redirector silently maps C:\Windows\System32
# to C:\Windows\SysWOW64, where the 64-bit agent's DLLs and config do not live.
# "Sysnative" is the redirector's escape hatch back to the real System32.
$System32 = if (-not [Environment]::Is64BitProcess -and
                [Environment]::Is64BitOperatingSystem) {
    "C:\Windows\Sysnative"
} else {
    "C:\Windows\System32"
}

# Keyconfig (tenant config) -- primary path plus the in-tree fallback.
$KeyConfigPrimary = Join-Path $System32 "zs.json"

# VC++ redistributable runtime the C++ agent links against.
$VcRuntimeFiles   = @((Join-Path $System32 "vcruntime140_1.dll"),
                      (Join-Path $System32 "msvcp140.dll"))
$VcVersionFile    = Join-Path $System32 "msvcp140.dll"

# ---------------------------------------------------------------------------
# Result plumbing
# ---------------------------------------------------------------------------
$script:Results = New-Object System.Collections.Generic.List[object]

function Add-Result {
    param(
        [ValidateSet("PASS", "FAIL", "WARN", "INFO")][string]$Status,
        [string]$Name,
        [string]$Detail
    )
    $script:Results.Add([pscustomobject]@{
        Status = $Status
        Name   = $Name
        Detail = $Detail
    })
    if (-not $Json) {
        $color = switch ($Status) {
            "PASS" { "Green" }
            "FAIL" { "Red" }
            "WARN" { "Yellow" }
            default { "Cyan" }
        }
        Write-Host ("[ {0,-4} ] " -f $Status) -ForegroundColor $color -NoNewline
        Write-Host ("{0,-34} {1}" -f $Name, $Detail)
    }
}

function Test-IsAdmin {
    try {
        $id = [Security.Principal.WindowsIdentity]::GetCurrent()
        return ([Security.Principal.WindowsPrincipal]$id).IsInRole(
            [Security.Principal.WindowsBuiltInRole]::Administrator)
    } catch { return $false }
}

# ---------------------------------------------------------------------------
# Checks
# ---------------------------------------------------------------------------
if (-not $Json) {
    Write-Host ""
    Write-Host "ZS stealth install verification" -ForegroundColor White
    Write-Host "===============================" -ForegroundColor White
    Write-Host ("Host: {0}   Time: {1}" -f $env:COMPUTERNAME, (Get-Date -Format "yyyy-MM-dd HH:mm:ss"))
    Write-Host ""
}

# 0. Elevation (advisory -- some checks degrade without it)
if (Test-IsAdmin) {
    Add-Result PASS "Elevation" "running as Administrator"
} else {
    Add-Result WARN "Elevation" "not elevated; service/ProgramData results may be incomplete"
}

# 1. svcmonitor service -- must exist AND be running. Give it time to come up:
#    an initial wait, then re-check every interval up to $SvcMonitorRetries.
function Get-SvcMonitor { Get-Service -Name $SvcMonitorName -ErrorAction SilentlyContinue }

if (-not $Json -and $SvcMonitorInitialWaitSeconds -gt 0) {
    Write-Host ("[ INFO ] Waiting {0}s for {1} to settle..." -f $SvcMonitorInitialWaitSeconds, $SvcMonitorName) -ForegroundColor Cyan
}
if ($SvcMonitorInitialWaitSeconds -gt 0) { Start-Sleep -Seconds $SvcMonitorInitialWaitSeconds }

$svcMon = Get-SvcMonitor
$attempt = 0
while (($null -eq $svcMon -or $svcMon.Status -ne "Running") -and $attempt -lt $SvcMonitorRetries) {
    $attempt++
    if (-not $Json) {
        $seen = if ($null -eq $svcMon) { "not installed" } else { $svcMon.Status }
        Write-Host ("[ INFO ] {0} {1}; retry {2}/{3} in {4}s..." -f `
            $SvcMonitorName, $seen, $attempt, $SvcMonitorRetries, $SvcMonitorRetryIntervalSeconds) -ForegroundColor Cyan
    }
    Start-Sleep -Seconds $SvcMonitorRetryIntervalSeconds
    $svcMon = Get-SvcMonitor
}

if ($null -eq $svcMon) {
    Add-Result FAIL "Service: $SvcMonitorName" ("not installed (after {0} retries)" -f $SvcMonitorRetries)
} elseif ($svcMon.Status -eq "Running") {
    $suffix = if ($attempt -gt 0) { " (after retry $attempt)" } else { "" }
    Add-Result PASS "Service: $SvcMonitorName" ("installed and Running{0}" -f $suffix)
} else {
    Add-Result FAIL "Service: $SvcMonitorName" ("installed but {0} (expected Running, after {1} retries)" -f $svcMon.Status, $SvcMonitorRetries)
}

# 2. svcrunner is NOT a service of its own. It is registered as svcmonitor's
#    recovery (failure-action) command, so Windows launches it when svcmonitor
#    fails. What must be true is that svcmonitor's FailureCommand points at it.
$failCmd = (Get-ItemProperty -LiteralPath "HKLM:\SYSTEM\CurrentControlSet\Services\$SvcMonitorName" `
                -Name FailureCommand -ErrorAction SilentlyContinue).FailureCommand
if ($failCmd -and $failCmd -match [regex]::Escape($SvcRunnerName)) {
    Add-Result PASS "Recovery: $SvcRunnerName" "registered as $SvcMonitorName failure action"
} else {
    Add-Result FAIL "Recovery: $SvcRunnerName" ("not registered as $SvcMonitorName failure action (FailureCommand = '{0}')" -f $failCmd)
}

#    Whether it is currently running is advisory: it is started on demand and
#    exits once it has done its work.
$runProc = Get-Process -Name $SvcRunnerName -ErrorAction SilentlyContinue
if ($runProc) {
    Add-Result PASS "Process: $SvcRunnerName" ("running (PID {0})" -f ($runProc | Select-Object -First 1).Id)
} else {
    Add-Result WARN "Process: $SvcRunnerName" "not currently running (starts on demand)"
}

# 3. Service binaries on disk (fixed paths, shared across brands).
foreach ($bin in @($SvcMonitorBinary, $SvcRunnerBinary)) {
    if (Test-Path -LiteralPath $bin) {
        Add-Result PASS "File: $(Split-Path $bin -Leaf)" $bin
    } else {
        Add-Result FAIL "File: $(Split-Path $bin -Leaf)" "missing: $bin"
    }
}

# 4. Locate the agent (MyZenV2s.exe) without assuming the brand directory.
#    Prefer the canonical "<brand>\zs" layout, then fall back to a scan.
$agentPath = $null
$programDirs = @("C:\Program Files", "C:\Program Files (x86)") |
    Where-Object { Test-Path -LiteralPath $_ }

foreach ($root in $programDirs) {
    $candidate = Get-ChildItem -LiteralPath $root -Directory -ErrorAction SilentlyContinue |
        ForEach-Object { Join-Path $_.FullName "zs\$AgentExeName" } |
        Where-Object { Test-Path -LiteralPath $_ } |
        Select-Object -First 1
    if ($candidate) { $agentPath = $candidate; break }
}
if (-not $agentPath) {
    foreach ($root in $programDirs) {
        $hit = Get-ChildItem -LiteralPath $root -Recurse -Filter $AgentExeName `
                   -ErrorAction SilentlyContinue -File -Depth 4 | Select-Object -First 1
        if ($hit) { $agentPath = $hit.FullName; break }
    }
}

$installDir = $null
if ($agentPath) {
    $installDir = Split-Path -Parent $agentPath
    Add-Result PASS "File: $AgentExeName" $agentPath
} else {
    Add-Result FAIL "File: $AgentExeName" "not found under Program Files"
}

# 5. Companion files in the install directory.
if ($installDir) {
    foreach ($f in $CompanionFiles) {
        $p = Join-Path $installDir $f
        if (Test-Path -LiteralPath $p) {
            $extra = ""
            if ($f -eq "version.txt") {
                try { $extra = "= " + ((Get-Content -LiteralPath $p -Raw).Trim()) } catch {}
            }
            Add-Result PASS "File: $f" ("{0} {1}" -f $p, $extra).Trim()
        } else {
            # version.txt absence is advisory; the binaries are required.
            if ($f -eq "version.txt") {
                Add-Result WARN "File: $f" "missing (agent may not have written it yet)"
            } else {
                Add-Result FAIL "File: $f" "missing: $p"
            }
        }
    }

    # ffmpeg is the screen-recording backend; usually bundled in the install dir.
    $ffmpeg = Get-ChildItem -LiteralPath $installDir -Filter "ffmpeg*.exe" `
                  -ErrorAction SilentlyContinue -File | Select-Object -First 1
    if ($ffmpeg) {
        Add-Result PASS "File: ffmpeg" $ffmpeg.FullName
    } else {
        Add-Result WARN "File: ffmpeg" "not found in install dir (recording backend)"
    }
} else {
    Add-Result WARN "Companion files" "skipped -- install directory unknown"
}

# 6. Keyconfig / tenant config.
$keyConfigFallback = if ($installDir) { Join-Path $installDir "keyconfig.json" } else { $null }
$keyConfigFound = $null
if (Test-Path -LiteralPath $KeyConfigPrimary) {
    $keyConfigFound = $KeyConfigPrimary
} elseif ($keyConfigFallback -and (Test-Path -LiteralPath $keyConfigFallback)) {
    $keyConfigFound = $keyConfigFallback
}
if ($keyConfigFound) {
    $tenant = ""
    try {
        $cfg = Get-Content -LiteralPath $keyConfigFound -Raw | ConvertFrom-Json
        if ($cfg.PSObject.Properties.Name -contains "tenant_id" -and $cfg.tenant_id) {
            $tenant = "tenant_id=$($cfg.tenant_id)"
        }
        Add-Result PASS "Keyconfig" ("{0} {1}" -f $keyConfigFound, $tenant).Trim()
    } catch {
        Add-Result FAIL "Keyconfig" "$keyConfigFound present but not valid JSON"
    }
} else {
    Add-Result FAIL "Keyconfig" "not found (checked $KeyConfigPrimary and install dir)"
}

# 7. VC++ runtime files + version floor.
$vcFilesOk = $true
foreach ($f in $VcRuntimeFiles) {
    if (-not (Test-Path -LiteralPath $f)) {
        $vcFilesOk = $false
        Add-Result FAIL "VC runtime" "missing: $f"
    }
}
if ($vcFilesOk) {
    try {
        $vcVer = (Get-Item -LiteralPath $VcVersionFile).VersionInfo.ProductVersion
        if (-not $vcVer) { $vcVer = (Get-Item -LiteralPath $VcVersionFile).VersionInfo.FileVersion }
        $verClean = ($vcVer -split '[^0-9\.]')[0]
        if ($verClean -and ([version]$verClean -ge [version]$MinVcRuntimeVersion)) {
            Add-Result PASS "VC runtime" "$verClean (>= $MinVcRuntimeVersion)"
        } else {
            Add-Result FAIL "VC runtime" "$verClean (< required $MinVcRuntimeVersion)"
        }
    } catch {
        Add-Result WARN "VC runtime" "files present but version unreadable"
    }
}

# 8. Agent process running (advisory -- svcmonitor will (re)start it, and it may
#    be mid-restart at the moment of check).
$proc = Get-Process -Name ([IO.Path]::GetFileNameWithoutExtension($AgentExeName)) `
            -ErrorAction SilentlyContinue
if ($proc) {
    Add-Result PASS "Process: $AgentExeName" ("running (PID {0})" -f ($proc | Select-Object -First 1).Id)
} else {
    Add-Result WARN "Process: $AgentExeName" "not currently running (svcmonitor should start it)"
}

# ---------------------------------------------------------------------------
# Summary
# ---------------------------------------------------------------------------
$fail = @($script:Results | Where-Object { $_.Status -eq "FAIL" }).Count
$warn = @($script:Results | Where-Object { $_.Status -eq "WARN" }).Count
$pass = @($script:Results | Where-Object { $_.Status -eq "PASS" }).Count
$ok   = ($fail -eq 0)

if ($Json) {
    [pscustomobject]@{
        ok         = $ok
        pass       = $pass
        warn       = $warn
        fail       = $fail
        installDir = $installDir
        agentPath  = $agentPath
        keyConfig  = $keyConfigFound
        checks     = $script:Results
    } | ConvertTo-Json -Depth 5
} else {
    Write-Host ""
    Write-Host ("Summary: {0} passed, {1} warnings, {2} failed" -f $pass, $warn, $fail) `
        -ForegroundColor $(if ($ok) { "Green" } else { "Red" })
    if ($ok) {
        Write-Host "RESULT: Install verified." -ForegroundColor Green
    } else {
        Write-Host "RESULT: Install verification FAILED." -ForegroundColor Red
    }
    Write-Host ""
}

exit $(if ($ok) { 0 } else { 1 })
```

</details>

## Check Running Status

### Standard Mode

1. Open **Task Manager**.
2. Search for `MyZenV2` in the process list.
3. If multiple instances appear, right-click each and select **Go to details**.
4. Verify the **User name** column matches the currently logged-in user.

### Stealth Mode

1. Open **Task Manager**.
2. Search for `MyZenV2s` in the process list. Alternatively search for `zs` in the process list.
3. Right-click and select **Go to details**. Verify the **User name** matches the current user.
4. Additionally, confirm that the `svcmonitor` process is running.

## Check Application Version

The **installer version** is the authoritative version indicator. The version shown in the MyZen app window may differ.

### Standard Mode

**Option 1:** Read the contents of:

```
C:\Program Files\Zenstack\MyZenV2\version.txt
```

**Option 2:** Navigate to `C:\Program Files\Zenstack\MyZenV2\updater.exe`, right-click, select **Properties**, then the **Details** tab. Note the version number.

### Stealth Mode

**Option 1:** Read the contents of:

```
C:\Program Files\zs\zs\version.txt
```

**Option 2:** Navigate to `C:\Program Files\zs\zs\updater.exe`, right-click, select **Properties**, then the **Details** tab. Note the version number.

> **Tip:** Check the **Download Apps** page in the We360.ai portal for the latest available version number to compare against.


# Windows FAQ

Windows installation FAQ for We360.ai MyZen agent — admin rights, troubleshooting, and common deployment issues resolved.

**How do I install MyZen on Windows?** Download the Windows installer (`MyZenV2-setup.exe`) from the We360.ai admin portal, run it, and follow the on-screen instructions. Do **not** rename the file.

**Is admin privilege required for Windows installation?** No, Standard mode does not require admin privileges. Stealth mode **does** require administrator rights.

**How can I verify if MyZen is installed correctly in Standard mode?** Check if `MyZenV2.exe` exists in the default install directory: `C:\Program Files\Zenstack\MyZenV2\`.

**How can I verify if MyZen is installed correctly in Stealth mode?** Check if `MyZenV2s.exe` exists in `C:\Program Files\zs\zs\`. Also verify the `zsrvc` service is running in Task Manager.

**Where can I find the download links?** Visit [we360.ai/downloads](https://we360.ai/downloads), or download from the We360.ai admin portal via the profile menu.

**I just signed up but cannot access my workspace. What should I do?** Verify your email by clicking the link sent to your inbox. The workspace is created after verification.

**I have not received the email verification link.** Check your spam folder. If it is not there, request a new verification email from your account settings.

**How do I update MyZen after installation?** MyZen automatically updates itself. No manual action is needed.

**How often are updates released?** Updates are released regularly to improve functionality and security. They are applied automatically.

**Do I need separate licenses for Standard and Stealth modes?** No. Any license can be used for either Standard or Stealth deployment.

**Is documentation available for the application features?** Yes. Refer to the We360.ai help portal for detailed articles on reporting, monitoring, and analytics.


# macOS Standard Installation

Install We360.ai MyZen Standard agent on macOS — step-by-step employee monitoring software setup with permissions guide.

## Prerequisites

| Requirement       | Detail                                                     |
| ----------------- | ---------------------------------------------------------- |
| **OS**            | macOS 13 (Ventura) or later                                |
| **Hardware**      | Minimum: any supported Mac. Recommended: 8 GB RAM, SSD     |
| **Apple Silicon** | Rosetta must be installed if prompted (Apple Silicon Macs) |
| **Antivirus**     | Add an exception for MyZen if a third-party AV is active   |

## Download the Installer

1. Log in to the We360.ai web portal.
2. Click the **Download Apps** button in the top bar.
3. In the **Mac** section, click **Standard** to download `MyZenV2.pkg`.

## Install (PKG Installer)

1. Double-click `MyZenV2.pkg` in your Downloads folder.
2. macOS may block the installer. If prompted with a security warning, click **OK**, then open **System Settings > Privacy & Security**.
3. Scroll to the **Security** section. You will see: *"MyZenV2 was blocked from use because it is not from an identified developer."* Click **Open Anyway**.
4. Click **Open** on the confirmation dialog.
5. The MyZenV2 Installer window appears. Click **Continue**.
6. Select the destination disk and click **Continue**.
7. Click **Install**, then enter your macOS credentials and click **Install Software**.
8. When "The installation was successful" appears, click **Close**.
9. Optionally keep or discard the PKG file when prompted.

## Grant Required Permissions

After installation, macOS will prompt for permissions. These are mandatory for data collection.

1. **Accessibility:** A prompt to enable Accessibility access appears. Click **Open System Settings**, locate **MyZenV2**, and toggle it **ON**. Authenticate if prompted.
2. **Screen Recording:** A prompt for screen and audio recording appears. Click **Open System Settings**, locate **MyZenV2**, and toggle it **ON**. After granting this permission, you must **log out and log back in** (or restart MyZen) for it to take effect.
3. **Browser URL Reading:** When you open a browser for the first time after installation, MyZen will prompt for permission to read browser URLs. This permission cannot be granted beforehand and is not skippable -- you must approve it when prompted.
4. Click **Quit & Reopen** when prompted to restart MyZen with the new permissions.

## Sign In

1. The MyZen app opens. Enter your **Workspace** name and click **Sign in**.
2. Enter your **Email** and **Password**.
3. Click **Punch In** to begin tracking.

### Post-Installation Notes

* The app will not automatically start until the user logs out and back in (or restarts).
* MyZen updates itself automatically.

## Install Locations (Reference)

| Item           | Path                                                    |
| -------------- | ------------------------------------------------------- |
| Application    | `/Applications/MyZenV2.app`                             |
| Version file   | `/Applications/MyZenV2.app/Contents/MacOS/version.txt`  |
| Launch agent   | `/Library/LaunchAgents/ai.we360.MyZenV2.plist`          |
| Updater daemon | `/Library/LaunchDaemons/ai.we360.MyZenV2-updater.plist` |


# macOS Stealth Installation

Install We360.ai MyZen Stealth agent on macOS — discrete employee monitoring software setup with silent background operation.

## Prerequisites

| Requirement       | Detail                                |
| ----------------- | ------------------------------------- |
| **OS**            | macOS 13 (Ventura) or later           |
| **Admin rights**  | **Required** for Stealth mode         |
| **Apple Silicon** | Rosetta must be installed if prompted |

{% hint style="danger" %}
**Never rename the stealth installer file.** The encoded filename contains your organization's license key and configuration. Renaming it or allowing extra characters to be appended (e.g. `(1)` from duplicate downloads) will cause the installation to fail. Use the file exactly as downloaded.

For scripted or MDM installs where the filename cannot be preserved, see [Stealth License Key Insertion Methods](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/macos-mdm#stealth-license-key-insertion-methods) for alternative ways to supply the license key (environment variable, config file).
{% endhint %}

## Download the Installer

1. Log in to the We360.ai web portal as an administrator.
2. Click the **Download Apps** button in the top bar.
3. In the **Mac** section, click **Stealth** to download the installer (filename is a Base64-encoded string ending in `.pkg`).

## Install

1. Locate the `<encoded-name>.pkg` file in your Downloads folder and double-click it.
2. If macOS displays *"macOS cannot verify that this app is free from malware"*, click **OK**.
3. Open **System Settings > Privacy & Security**. Scroll to **Security** and find the blocked installer message. Click **Open Anyway**.
4. Enter your macOS credentials when prompted.
5. Click **Open** on the confirmation dialog.
6. The installer window appears. Click **Continue**.
7. If prompted with *"Installer would like to access files in your Downloads folder"*, click **OK**.
8. Select the destination disk and click **Continue**.
9. Click **Install**, then enter credentials and click **Install Software**.
10. When "The installation was successful" appears, click **Close**.
11. Optionally keep or discard the PKG file when prompted.

### Permissions

In stealth mode, macOS permission prompts will still appear for the logged-in user:

* **Accessibility** -- prompted on first run. Must be approved in System Settings.
* **Screen Recording** -- prompted on first run. Must be approved manually (cannot be pre-granted by any MDM). After granting, a **logout/login or app restart** is required for the permission to take effect.
* **Browser URL Reading** -- prompted when a browser is first used. This permission is not skippable and cannot be granted beforehand without PPPC.

### Post-Installation Notes

* Stealth mode does not display a visible application or dock icon.
* The app will not automatically start until a lock/unlock cycle is performed. A restart is recommended.
* When **uninstalling** on macOS, a **system restart** is required.
* Consider clearing browser download history on the target machine if confidentiality is required.

## Install Locations (Reference)

| Item           | Path                                              |
| -------------- | ------------------------------------------------- |
| Application    | `/usr/local/zs/zs.app`                            |
| Version file   | `/usr/local/zs/zs.app/Contents/MacOS/version.txt` |
| Launch agent   | `/Library/LaunchAgents/ai.zs.zs.plist`            |
| Updater daemon | `/Library/LaunchDaemons/ai.zs.zs-updater.plist`   |
| Process name   | `zs`                                              |


# macOS Uninstallation

Uninstall We360.ai MyZen agent from macOS — GUI and terminal removal for Standard and Stealth monitoring modes.

## GUI Uninstallation (Standard Mode)

1. Open **Finder** and navigate to the **Applications** folder.
2. Locate **MyZenV2**.
3. Right-click and select **Move to Bin**.

> If you see *"The item 'MyZenV2' can't be moved to the Bin because it's open"*, quit MyZen first (right-click the dock icon or use Activity Monitor), then repeat step 3.

## Complete Uninstallation (Standard and Stealth)

For a thorough removal of all MyZen components (both Standard and Stealth), run the following in Terminal. This removes the application, launch agents, daemons, preferences, and support files.

```bash
# Stop services
sudo launchctl bootout system /Library/LaunchDaemons/ai.we360.MyZenV2-updater.plist 2>/dev/null
sudo launchctl bootout system /Library/LaunchDaemons/ai.zs.zs-updater.plist 2>/dev/null

# Remove launch plists
sudo rm -f /Library/LaunchDaemons/ai.we360.*.plist
sudo rm -f /Library/LaunchDaemons/ai.zs.*.plist
sudo rm -f /Library/LaunchAgents/ai.we360.*.plist
sudo rm -f /Library/LaunchAgents/ai.zs.*.plist

# Remove applications
sudo rm -rf /Applications/MyZenV2.app
sudo rm -rf /usr/local/zs

# Remove user data
rm -rf ~/Library/Application\ Support/MyZenV2
rm -rf ~/Library/Application\ Support/zs
rm -f ~/Library/Preferences/com.zenstack.MyZenV2.plist
rm -f ~/Library/Preferences/ai.zs.zs.plist

# Kill remaining processes
sudo pkill MyZenV2 2>/dev/null
sudo pkill zs 2>/dev/null
```

> This script is derived from the uninstall routine shipped with the agent. For the full version, contact We360.ai support.

{% hint style="info" %}
A **system restart is required** on macOS after uninstalling MyZen to fully release all system hooks and services.
{% endhint %}

## Zen Cleanup Utility

If the manual uninstallation does not fully remove all MyZen components, or if you want to completely erase every trace of MyZen from the system, use the **Zen Cleanup Utility**.

{% hint style="warning" %}
Only use the Zen Cleanup Utility if you want to **completely remove everything** related to MyZen from the system. This includes all application files, launch agents, daemons, preferences, and support directories. This action cannot be undone.
{% endhint %}

The utility is available from the same download location as the agent installers. See [Download Links & Utilities](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links) for details.


# macOS Installation Validation

Verify We360.ai MyZen agent installation on macOS — check running status and validate endpoint monitoring is active.

## Check Running Status

### Standard Mode

> **Note:** The app will not automatically start until the user logs out and logs back in.

1. Open **Activity Monitor**.
2. Search for `MyZenV2`.
3. Verify the **User** matches the current user.
4. If the processed are listed, the agent is running.

### Stealth Mode

> **Note:** The app will not automatically start until a lock/unlock cycle is performed. A restart is recommended.

1. Open **Activity Monitor**.
2. Search for `zs`. Also search for `svcmonitor`
3. Verify the **User** matches the current user.
4. If the processes are listed, the agent is running.

## Check Application Version

The **installer version** is the authoritative version indicator. The version displayed in the MyZen app window may differ. Check the Download Apps page in the portal for the latest version.

### Standard Mode

Read the version file:

```bash
cat /Applications/MyZenV2.app/Contents/MacOS/version.txt
```

Alternatively: right-click `MyZenV2.app` in Finder, select **Show Package Contents**, and navigate to `Contents/MacOS/version.txt`.

### Stealth Mode

Read the version file:

```bash
cat /usr/local/zs/zs.app/Contents/MacOS/version.txt
```

> **Tip:** Compare the installed version against the latest version shown on the **Download Apps** page in the We360.ai portal.


# macOS FAQ

macOS installation FAQ for We360.ai MyZen agent — permissions, troubleshooting, and common setup issues resolved.

**How do I install MyZen in Standard mode on Mac?** Download the PKG installer (`MyZenV2.pkg`) from the We360.ai admin portal, double-click to run it, and follow the on-screen instructions. Grant all requested permissions during installation.

**What permissions are needed during Mac installation?** MyZen requires the following macOS permissions to function correctly:

* **Privacy & Security > Security:** Allow the app to open from an unidentified developer.
* **Privacy & Security > Accessibility:** Enable access for MyZenV2.
* **Privacy & Security > Screen Recording:** Enable access for MyZenV2.

**I am experiencing intermittent data issues on Mac. What should I do?** Verify that all three permissions above are granted. Missing permissions are the most common cause of data gaps.

**Do I need Rosetta for Apple Silicon Macs?** If prompted during installation, install Rosetta before proceeding. MyZen requires Rosetta on Apple Silicon hardware.

**Where can I find the download links?** Visit [we360.ai/downloads](https://we360.ai/downloads), or download from the We360.ai admin portal via the profile menu.

**I just signed up but cannot access my workspace.** Verify your email by clicking the link sent to your inbox. The workspace is created after verification.

**I have not received the email verification link.** Check your spam folder. If it is not there, request a new verification email from your account settings.

**How do I update MyZen after installation?** MyZen automatically updates itself. No manual action is needed.

**How often are updates released?** Updates are released regularly and are applied automatically.

**Do I need separate licenses for Standard and Stealth modes?** No. Any license can be used for either Standard or Stealth deployment.


# Linux Installation

Install the We360.ai MyZen agent on Linux (Ubuntu) — Stealth-mode employee monitoring software installation guide.

On Linux, the We360.ai agent is deployed in **Stealth mode** using a shell installer. It runs silently in the background with no user interface, following your organization's tracking policies.

{% hint style="info" %}
Standard (visible) mode is available on Windows and macOS. On Linux, the agent is distributed as a headless Stealth installer intended for IT-managed rollouts.
{% endhint %}

## Prerequisites

| Requirement       | Detail                                                                                                                                                                                            |
| ----------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Distribution**  | Ubuntu (64-bit / x86‑64). Other Debian-based distributions may work but Ubuntu is the supported target.                                                                                           |
| **Privileges**    | Root / `sudo` access is required to install the background service.                                                                                                                               |
| **Antivirus/EDR** | Add an exception for the agent if endpoint protection is active (see [AV and EDR Exclusions](/deployment-and-it-ops/security-and-hardening/network-and-security-hardening/av-and-edr-exclusions)) |
| **Network**       | Outbound HTTPS/WSS on TCP 443 to the We360.ai endpoints (see [The "Allowlist" Guide](/deployment-and-it-ops/security-and-hardening/network-and-security-hardening/allowlist-guide))               |

## Download the Installer

1. Log in to the We360.ai web portal, or use the [Download Links & Utilities](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links) page.
2. Download the Linux Stealth installer: `zs-amd64.sh`.

{% hint style="warning" %}
Before running it, **rename the installer to your Stealth license key**, keeping the `.sh` extension — for example `A1B2C3D4.sh`. The installer reads the tenant binding from its own filename, so do not run it under the generic `zs-amd64.sh` name.
{% endhint %}

## Install

Open a terminal in the folder containing the renamed installer and run:

{% code title="Terminal" %}

```bash
chmod +x <stealth_license_key>.sh
sudo ./<stealth_license_key>.sh
```

{% endcode %}

The script installs the agent and registers a background service that starts automatically and survives reboots. No further interaction is required — there is no window or tray icon in Stealth mode.

## Validate the Installation

Because Stealth mode is invisible on the device, confirm success from the **server side**:

1. Wait a few minutes after installation.
2. In the We360.ai portal, open the **Devices** view (or the user's detail page).
3. Confirm the Linux device appears and is reporting recent activity.

If no data arrives, review the [Tracker Failure Diagnostic Guide](/deployment-and-it-ops/troubleshooting-and-support/tracker-failure-guide) and verify network reachability and AV/EDR exclusions.

## Offline / Firewalled Environments

If the device cannot reach the discovery endpoint, IT can pre-provision service discovery with a protected `zs-origin.json` manifest at `/etc/`. See [Pre-Provisioned Origin Data](/deployment-and-it-ops/security-and-hardening/network-and-security-hardening/pre-provisioned-origin-data).

## Uninstall

Use the **Zen Cleanup Utility** for Linux to fully remove the agent. Download it from [Download Links & Utilities](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links) (`zen_cleanup`, available for `amd64` and `arm64`), then run it with `sudo`.


# Mass Deployment

Mass deploy We360.ai agent via GPO, Intune, MDM, SCCM, and MSI — scalable employee monitoring software rollout for enterprises.

This section covers methods for deploying MyZen across many machines without direct physical access. Choose the method that fits your infrastructure.

## Deployment Methods

| Method                              | Platform       | Stealth Support | Guide                                                                                                            |
| ----------------------------------- | -------------- | --------------- | ---------------------------------------------------------------------------------------------------------------- |
| Command Line (MSI)                  | Windows        | Yes             | [Command Line / MSI](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/command-line-msi)    |
| Active Directory Group Policy       | Windows        | Yes             | [AD GPO Deployment](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/active-directory-gpo) |
| Microsoft Intune (Windows)          | Windows        | Yes             | [Intune Deployment](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/microsoft-intune)     |
| Microsoft Intune (macOS)            | macOS          | Yes             | [macOS MDM Deployment](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/macos-mdm)         |
| MDM Tools (JAMF, Addigy, etc.)      | macOS          | Partial         | [macOS MDM Deployment](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/macos-mdm)         |
| Direct Link (Employee Self-Install) | Windows, macOS | No              | [Direct Link](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/direct-link)                |

## Key Notes

* **Do not rename installer files.** The filename contains encoded organization configuration. Renaming prevents proper installation.
* **Stealth mode on macOS via MDM:** MDM tools can install the agent but cannot automatically grant Accessibility and Screen Recording permissions. The end user must approve these manually.
* **Automatic updates:** Once installed, MyZen updates itself. No post-deployment update action is needed.


# Command Line / MSI / EXE

Silent MSI deployment of We360.ai agent on Windows — MSIEXEC command-line install for mass employee monitoring rollout.

Our Windows installers come as both MSI and EXE packages . They can be deployed silently using `MSIEXEC` from an elevated Command Prompt, PowerShell, or any RMM tool with remote command-line access.

{% hint style="warning" %}
The MSI installer is absolutely not recommended unless you have no other choice. We recommend using the EXE installer to ensure that our app starts immediately after install and that the updates and installtions work properly (which has been found to be buggy with MSI setups)
{% endhint %}

## Prerequisites

* The installer file downloaded from the We360.ai portal (Stealth version recommended for silent deployment).
* An elevated (Run as Administrator) command prompt or PowerShell session on the target machine.

{% hint style="danger" %}
**Do not rename the stealth installer file.** The **stealth** installer filename is tied to your organization's license. Renaming it, or allowing extra characters to be appended (e.g. `(1)` or `(2)` from duplicate downloads), will cause the installation to fail.
{% endhint %}

## Silent Install

#### EXE

```powershell
> "C:\path\to\<installer-filename>.exe" /exenoui /qn
```

Replace `C:\path\to\<installer-filename>.exe` with the actual path and filename of your organization's EXE.

#### MSI

```powershell
MSIEXEC /i "C:\path\to\<installer-filename>.msi" /QN
```

Replace `C:\path\to\<installer-filename>.msi` with the actual path and filename of your organization's MSI.

## Silent Uninstall (MSI only)

```powershell
MSIEXEC /x "C:\path\to\<installer-filename>.msi" /QN
```

## Silent Uninstall (All Apps and Config)

* Download the zen-cleanup utility from here [Download Links & Utilities](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links#utilities)
* Run the exe file via terminal with Administrator permissions.

## Install with Logging (for Troubleshooting)

If an installation fails, re-run with verbose logging enabled:

```
"C:\path\to\<installer-filename>.exe" /exenoui /qn /l*v %TEMP%\myzen-install.log
```

```powershell
MSIEXEC /i "C:\path\to\<installer-filename>.msi" /QN /l*v %TEMP%\myzen-install.log
```

Attach the generated log file (`%TEMP%\myzen-install.log`) when creating a support ticket.

## Usage with RMM / PSExec

These commands work with any tool that provides remote command-line access:

* **RMM tools** with remote shell (e.g. ConnectWise, Datto, NinjaRMM)
* **PSExec** for remote execution across the network
* **SCCM** task sequences

The command runs silently with no on-screen feedback. RMM tools may provide their own success/failure reporting.


# Active Directory GPO

Deploy We360.ai agent via Active Directory GPO — mass Windows endpoint deployment using Group Policy for employee monitoring.

Machines bound to an Active Directory domain can have the MyZen agents installed via Group Policy, allowing administrators to deploy across their entire network without touching individual machines.

## Step 1: Create a Distribution Point

1. Log on to the domain server as an Administrator.
2. Create a **shared network folder** (this will hold the MSI package).
3. Set share permissions to allow read access for the computers/groups that need the agent.
4. Copy the MyZen MSI file into this shared folder.
   * Download the **MSI** file from the We360.ai admin portal for silent deployment.

{% hint style="danger" %}
**Do not rename the stealth installer file.** The **stealth** installer filename is tied to your organization's license. Renaming it, or allowing extra characters to be appended (e.g. `(1)` or `(2)` from duplicate downloads), will cause the installation to fail.
{% endhint %}

## Step 2: Create a Group Policy Object

1. Open **Active Directory Users and Computers** (Start > Programs > Administrative Tools).
2. Right-click your domain name and select **Properties**.
3. Select the **Group Policy** tab and click **New**.
4. Name the policy (e.g. `We360 Agent`).
5. Click **Properties**, select the **Security** tab.
6. Enable the **Apply Group Policy** checkbox only for the groups to which this policy should apply.
7. Click **OK**.

## Step 3.1: MSI - Assign the MSI Package

The agent should be assigned on a **per-machine** basis so it installs silently at machine startup.

1. Open **Active Directory Users and Computers**.
2. Right-click your domain name and select **Properties**.
3. Go to the **Group Policy** tab, select the GPO you created, and click **Edit**.
4. Expand **Computer Configuration > Software Settings**.
5. Right-click **Software Installation**, select **New > Package**.
6. In the Open dialog, enter the **full UNC path** to the MSI in the shared folder (e.g. `\\server\share\<installer>.msi`).
7. Click **Open**.
8. Select **Assigned** and click **OK**.
   * Alternatively, select **Published** to make the app available for all users under the AD UNC.
9. Close the Group Policy snap-in and exit Active Directory Users and Computers.

## Step 3.2: Via Powershell

* Please download the EXE installer from the portal
* Please download the powershell install helper script from [here](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links#utilities).
* Please replace the `$DownloadUrl` variable in the script with the correct exe URL from [here](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links#desktop-agents).
* If installing **stealth** app, please rename the `$InstallerName` variable to your downloaded exe name (along with .exe) part.
* Add this powershell script in startup scripts. You can also run this script directly via Group Policy.

{% hint style="info" %}
For debugging failed installations etc, please see [Command Line / MSI / EXE](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/command-line-msi)for more details
{% endhint %}

## What Happens Next

* When a client computer **starts or restarts**, Active Directory synchronises and the assigned package installs automatically.
* The installation is silent; no user interaction is required.
* MyZen will begin operating in Stealth mode (if the Stealth MSI was used) after the next user login. For instant start, please use the powershell script path or EXE installer via other MDM tools / manually.


# Microsoft Intune (Windows)

Deploy We360.ai agent via Microsoft Intune — Endpoint Manager setup for mass Windows employee monitoring software deployment.

{% hint style="info" %}
This page covers the **Windows** MSI agent. To deploy the **macOS** agent via Intune (PKG app, PPPC and background-items profiles), see [macOS MDM Deployment → Microsoft Intune (macOS)](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/macos-mdm).
{% endhint %}

To deploy the MyZen Windows agent via Microsoft Intune, the MSI file must first be converted to the `.intunewin` format using the Microsoft Win32 Content Prep Tool.

## Prerequisites

* The MyZen Windows MSI installer downloaded from the We360.ai admin portal.
* The [Microsoft Win32 Content Prep Tool](https://github.com/Microsoft/Microsoft-Win32-Content-Prep-Tool) (`IntuneWinAppUtil.exe`).
* Access to Microsoft Endpoint Manager (Intune).
* The installer file must **not** be renamed or have extra characters appended to the filename. The stealth installer filename is tied to your organization's license.

{% hint style="danger" %}
**Do not rename the stealth installer file.** The **stealth** installer filename is tied to your organization's license. Renaming it, or allowing extra characters to be appended (e.g. `(1)` or `(2)` from duplicate downloads), will cause the installation to fail.
{% endhint %}

## Step 1: Convert the MSI to .intunewin Format

Run the Win32 Content Prep Tool from a Command Prompt or PowerShell:

```powershell
IntuneWinAppUtil.exe -c <folder-containing-msi> -s <msi-filename> -o <output-folder> -q
```

| Flag | Description                                      |
| ---- | ------------------------------------------------ |
| `-c` | Folder containing the MSI file                   |
| `-s` | The MSI filename (not including the folder path) |
| `-o` | Output folder for the `.intunewin` file          |
| `-q` | Quiet mode                                       |

### Example

```powershell
IntuneWinAppUtil.exe -c C:\Users\admin\Downloads\ -s zs.msi -o .\intune -q
```

> For full command-line parameter documentation, see the README in the [Microsoft Win32 Content Prep Tool GitHub repository](https://github.com/Microsoft/Microsoft-Win32-Content-Prep-Tool).

## Step 2: Upload to Intune

1. Open **Microsoft Endpoint Manager** (endpoint.microsoft.com).
2. Navigate to **Apps > All apps > Add**.
3. Select **Windows app (Win32)** as the app type.
4. Upload the `.intunewin` file generated in Step 1.
5. Configure the install command:

   ```
   MSIEXEC /i <msi-filename>.msi /QN
   ```
6. Configure the uninstall command:

   ```
   MSIEXEC /x <msi-filename>.msi /QN
   ```
7. Set detection rules (e.g. check for the existence of `MyZenV2.exe` or `MyZenV2s.exe` in Program Files).
8. Assign the app to the appropriate device groups.


# macOS MDM Deployment

Deploy We360.ai macOS agent via MDM — Jamf, Mosyle, Kandji, Hexnode, Addigy, SimpleMDM, ManageEngine, and Microsoft Intune setup for mass endpoint monitoring.

The MyZen macOS installer is distributed as a standard `.pkg` file, which can be deployed through any MDM that supports macOS package distribution. This guide covers deployment steps, PPPC configuration profiles, and background items management for each supported MDM platform.

## App & Team Identifiers

{% hint style="info" %}
**Apple Developer Team ID:** `5KPT5U8WVR` (Zenstack Private Limited)

**Bundle Identifiers:**
{% endhint %}

| Variant  | Bundle ID          | Install Path                |
| -------- | ------------------ | --------------------------- |
| Standard | `ai.we360.MyZenV2` | `/Applications/MyZenV2.app` |
| Stealth  | `ai.zs.zs`         | `/usr/local/zs/zs.app`      |

{% hint style="info" %}
**Code Requirement (Stealth):**

{% code overflow="wrap" fullWidth="true" %}

```
identifier "ai.zs.zs" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = "5KPT5U8WVR"
```

{% endcode %}

To extract the code requirement yourself, run on a Mac with the app installed:

```bash
codesign -dr - /usr/local/zs/zs.app    # Stealth
codesign -dr - /Applications/MyZenV2.app # Standard
```

{% endhint %}

## Important Points for Stealth App Install

{% hint style="danger" %}
**Do not rename the stealth installer file.** The **stealth** installer filename is tied to your organization's license. Renaming it, or allowing extra characters to be appended (e.g. `(1)` or `(2)` from duplicate downloads), will cause the installation to fail.
{% endhint %}

{% hint style="info" %}
If you're having issues with the Stealth App installation, with install please check the /tmp/zs-postinstall.log . If the **PACKAGE\_PATH** variable in the first few lines does not match the package file name as downloaded from portal, you will require a pre-install script to run on the machine before the package can be installed, as our unique package name contains your tenant/org's license details.

The following preinstall script should work:

```
#!/bin/sh
basename "<pkg_file_name>" .pkg | base64 --decode | tee /Library/Preferences/zs.json
```

> If your MDM does not support pre-install scripts, please contact our support team for a custom installer. (Not all custom installer requests may be approved)
> {% endhint %}

## Stealth License Key Insertion Methods

The stealth agent needs your organization's license key at install time. There are four supported ways to provide it — pick the one your deployment tool can deliver:

| Method                        | How                                                                                                                                                                                                                                                | When to use                                                                                                   |
| ----------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------- |
| **PKG filename** (default)    | Install the PKG with its original portal filename: `<license-key>.pkg`. The installer reads its own filename.                                                                                                                                      | Portal downloads and any MDM that preserves the PKG filename.                                                 |
| **Environment variable**      | Run the installer with `ZS_KEY_CONFIG_BASE64_ENCODED` set to the license key (the same Base64 string as the installer filename, without `.pkg`). This takes the **highest precedence** — it wins over any filename or stale config on the machine. | Scripted installs where the PKG is downloaded under a generic name (Intune shell scripts, custom automation). |
| **Config file drop**          | Place the stealth config at `/Library/Preferences/zs.json` **before** installing (decode the license key: `echo "<license-key>" \| base64 --decode > /Library/Preferences/zs.json`).                                                               | MDMs that rename uploads but support pre-install scripts.                                                     |
| **Config file path variable** | Set `ZS_KEY_CONFIG=<path>` to point at a stealth config JSON stored at a custom location.                                                                                                                                                          | Advanced/custom provisioning only.                                                                            |

```bash
# Environment-variable method — no rename needed:
sudo ZS_KEY_CONFIG_BASE64_ENCODED='<license-key>' installer -pkg /tmp/zs-installer.pkg -target /
```

{% hint style="info" %}
`<license-key>` is always the Base64-encoded string that forms your stealth installer's filename as downloaded from the We360.ai portal (everything before `.pkg`). The environment-variable methods require a recent agent installer (v4.15 or later).
{% endhint %}

{% hint style="info" %}
**Restart may be required after MDM install.** When installing via MDM, by default our installer tries to start the apps immediately via `launchctl`. This should not fail unless there's some MDM or OS level controls blocking this.\
A **logout/login** or **system restart** may be required to circumvent such scenarios.
{% endhint %}

## macOS Permissions

MyZen requires several macOS privacy permissions. How they are granted depends on whether you use an MDM with PPPC support.

**With MDM (PPPC profile):**

* **Accessibility** — can be pre-approved via a PPPC configuration profile.
* **Browser URL Reading (AppleEvents/Automation)** — can be pre-approved via PPPC per browser. If not granted via PPPC, the user will be prompted to allow browser URL access the first time a browser is used.
* **Screen Recording** **(Optional)** — **cannot** be approved via any MDM. Apple does not allow Screen Recording to be granted programmatically. The end user must approve this manually.

**Without MDM:**

* All permissions will prompt the user at first use.

{% hint style="info" %}
**After granting Screen Recording permission**, the user must perform a **logout/login** or **restart the MyZen/zs app** for the permission to take effect.
{% endhint %}

## Configuration Profiles

Three `.mobileconfig` profiles are provided for MDM deployment. Deploy these **before** installing the agent PKG.

| Profile                     | Filename                                                                                                                                                | Purpose                                                                                                                     |
| --------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------- |
| PPPC (Privacy Preferences)  | [`zs-pppc.mobileconfig`](https://github.com/zenstack-we360/documentation/tree/main/it-ops/.gitbook/assets/zs-pppc.mobileconfig)                         | Pre-approves Accessibility, simplifies Screen Recording prompt, and grants browser Automation (AppleEvents) for URL reading |
| Background Items            | [`zs-background-items.mobileconfig`](https://github.com/zenstack-we360/documentation/tree/main/it-ops/.gitbook/assets/zs-background-items.mobileconfig) | Suppresses "Background Items Added" notification and prevents users from disabling ZS services (macOS 13+)                  |
| Screen Capture (standalone) | [`zs-screen-capture.mobileconfig`](https://github.com/zenstack-we360/documentation/tree/main/it-ops/.gitbook/assets/zs-screen-capture.mobileconfig)     | Standalone Screen Recording PPPC entry — use if you deploy screen capture permissions separately                            |

{% file src="/files/F4wj3GekG0pLPIyijl85" %}
PPPC profile — Accessibility and browser AppleEvents (URL reading)
{% endfile %}

{% file src="/files/vQWSnrWOCoVtSsKUhgVl" %}
Background Items profile — suppresses the macOS 13+ "Background Items Added" notification
{% endfile %}

{% file src="/files/PNdI6tJPySYtfgGLQ5Bh" %}
Screen Capture profile — standalone Screen Recording PPPC entry
{% endfile %}

{% hint style="warning" %}
**PPPC profiles must be delivered via MDM.** Manually installed `.mobileconfig` files (double-clicked by users) **cannot** grant TCC permissions — macOS may ignore TCC payloads from user-installed profiles for security reasons.
{% endhint %}

### Background Items (macOS 13+)

Starting with macOS 13 Ventura, macOS shows a "Background Items Added" notification when an application installs LaunchAgents or LaunchDaemons. Users can disable these from **System Settings > General > Login Items & Extensions**. The background items profile prevents this.

**Managed background items for MyZen:**

| Mode     | Launch Agent Label | Updater Daemon Label       |
| -------- | ------------------ | -------------------------- |
| Standard | `ai.we360.MyZenV2` | `ai.we360.MyZenV2-updater` |
| Stealth  | `ai.zs.zs`         | `ai.zs.zs-updater`         |

The provided profile uses a `TeamIdentifier` rule (`5KPT5U8WVR`) which covers all current and future LaunchAgents/Daemons signed by Zenstack.

### Install Locations

MDM administrators may need these paths for configuration profiles, detection rules, or post-install scripts.

<table data-header-hidden="false" data-header-sticky><thead><tr><th>Item</th><th>Standard App Path</th><th>Stealth App Path</th></tr></thead><tbody><tr><td>Application</td><td><code>/Applications/MyZenV2.app</code></td><td><code>/usr/local/zs/zs.app</code></td></tr><tr><td>Launch Agent</td><td><code>/Library/LaunchAgents/ai.we360.MyZenV2.plist</code></td><td><code>/Library/LaunchAgents/ai.zs.zs.plist</code></td></tr><tr><td>Updater Daemon</td><td><code>/Library/LaunchDaemons/ai.we360.MyZenV2-updater.plist</code></td><td><code>/Library/LaunchDaemons/ai.zs.zs-updater.plist</code></td></tr><tr><td>Config file</td><td><code>-</code></td><td><code>/Library/Preferences/zs.json</code></td></tr><tr><td>Install logs</td><td><code>/tmp/MyZenV2-*.log</code></td><td><code>/tmp/zs-*.log</code></td></tr></tbody></table>

## General Deployment Sequence

Regardless of which MDM you use, follow this order:

1. **Deploy the PPPC profile** (`zs-pppc.mobileconfig`) to target devices.
2. **Deploy the Background Items profile** (`zs-background-items.mobileconfig`) to target devices.
3. **Upload and deploy** the MyZen `.pkg` installer.
4. **Instruct end users** to grant Screen Recording permission when prompted, then logout/login.
5. **Verify** the agent appears online in the We360.ai dashboard.

> **Note:** The PKG is signed by Zenstack Private Limited (Team ID `5KPT5U8WVR`). You may need to add this to your allowed developers list.

***

## MDM Platform Guides

<details>

<summary>Jamf Pro</summary>

**PKG Upload & Deployment**

1. Log in to **Jamf Pro** (`your-instance.jamfcloud.com`).
2. Navigate to **Settings > Computer Management > Packages**.
3. Click **New** to create a new package entry.
4. Upload the MyZen `.pkg` file.
5. Set a **Display Name** (e.g., "MyZenV2 Stealth").
6. Click **Save**.
7. Navigate to **Computers > Policies** and click **New**.
8. Configure the **General** payload:
   * **Display Name:** e.g., "Deploy MyZenV2"
   * **Trigger:** Recurring Check-in (or Enrollment Complete for new devices)
   * **Execution Frequency:** Once per computer
9. Click the **Packages** payload and click **Configure**.
10. Select the uploaded PKG and set the **Action** to **Install**.
11. Click the **Scope** tab and add target computers or smart/static groups.
12. Click **Save**.

**PPPC Profile Deployment**

**Option A — Built-in PPPC builder:**

1. Navigate to **Computers > Configuration Profiles**.
2. Click **New**.
3. Set a **Name** (e.g., "ZS App Permissions").
4. In the left sidebar, click **Privacy Preferences Policy Control**.
5. Click **Add** (+).
6. Fill in the fields:
   * **Identifier:** `ai.zs.zs`
   * **Identifier Type:** Bundle ID
   * **Code Requirement:** paste from `codesign -dr -` output
   * **Static Code:** No
7. Under **App or Service**, click **Add**:
   * Select **Accessibility** and set to **Allow**.
8. Repeat for additional permissions (AppleEvents for each browser).
9. Scope to target computers and **Save**.

**Option B — Upload pre-built profile:**

1. Navigate to **Computers > Configuration Profiles > Upload**.
2. Upload `zs-pppc.mobileconfig`.
3. Scope to target computers and **Save**.

**Background Items**

1. Navigate to **Computers > Configuration Profiles > New**.
2. Upload `zs-background-items.mobileconfig` (or use **Managed Background Items** payload in Jamf Pro 10.44+).
3. Scope and **Save**.

**Verification**

1. Navigate to **Computers > Search Inventory** and select a target device.
2. Go to the **Configuration Profiles** tab — confirm both PPPC and Background Items profiles are installed.
3. Go to the **Applications** tab — confirm MyZenV2 or zs.app is listed.
4. Ask the end user to **logout/login** or **restart**.
5. Verify the endpoint appears online in the **We360.ai dashboard** at `portal.we360.ai`.

{% hint style="info" %}
Jamf Pro preserves the original PKG filename during distribution. Stealth deployments work without issues.
{% endhint %}

</details>

<details>

<summary>Jamf Now</summary>

**PKG Upload & Deployment**

1. Log in to **Jamf Now** (`your-instance.jamfnow.com`).
2. In the left sidebar, click **Apps**.
3. Click **Add an App** and select the **Upload Your App** tab.
4. Drag and drop the MyZen `.pkg` file, or click **browse** to select it.
5. Jamf Now will process the file and show a **Review Your App** dialog.
6. Verify the **App Name** (e.g., "zs") and the **Bundle ID** are correct.
7. Click **Done** to finish the upload.
8. Navigate to **Blueprints** and select the target Blueprint.
9. Go to the **Apps** section and add the uploaded app.
10. Click **Save Blueprint**.
11. Devices assigned to this Blueprint will receive the app at next check-in.

**PPPC Profile Deployment**

1. Navigate to **Blueprints** > target Blueprint.
2. Go to the **Custom Profiles** section.
3. Click **Upload** and select `zs-pppc.mobileconfig`.
4. Click **Save Blueprint**.

{% hint style="danger" %}
**Jamf Now does not have a built-in PPPC profile builder.** You must upload a pre-built `.mobileconfig` file. The profiles provided in this guide are ready to use.
{% endhint %}

{% hint style="warning" %}
**Filename renaming concern:** Jamf Now may rename the uploaded PKG to `app.pkg` during distribution. This breaks MyZen's **stealth** licensing (which is encoded in the filename). Please request a **custom stealth installer** from our team. If unavailable, request our team for **stealth config zs.json** file, which has to be placed in `/Library/Preferences/zs.json`
{% endhint %}

**Background Items**

Upload `zs-background-items.mobileconfig` via the **Custom Profiles** section (same process as PPPC).

**Verification**

1. Navigate to **Blueprints** and select the target Blueprint.
2. Check the **Devices** section — confirm the device appears and app is installed.
3. Ask the end user to **logout/login** or **restart**.
4. Verify the endpoint appears online in the **We360.ai dashboard** at `portal.we360.ai`.

**Limitations**

* Custom Apps and Custom Profiles require the **Jamf Now Plus** plan.
* No Smart Groups or conditional logic — only static Blueprint assignments.
* Limited troubleshooting and logging compared to Jamf Pro.

</details>

<details>

<summary>Addigy</summary>

**PKG Upload & Deployment**

1. Log in to **Addigy** (`app.addigy.com`).
2. Navigate to **Catalog > Software**.
3. Click **New** to create a new software item.
4. Upload the MyZen `.pkg` file.
5. Addigy auto-generates an `_install.sh` script. Review it — typically no changes are needed.
6. Optionally configure a **Condition** to control when the install runs (e.g., only if the app is not already installed).
7. Click **Save**.
8. Navigate to **Policies** and select the target Policy.
9. Add the software item to the Policy's **Catalog**.
10. Devices in that Policy will receive the software.

**PPPC Profile Deployment**

**Option A — Built-in profile builder:**

1. Navigate to **Catalog > MDM Profiles**.
2. Click **New** to create a new profile.
3. Select **Privacy Preferences Policy Control** payload.
4. Configure the fields as described in the Identifiers section above.
5. Click **Save** and add to target Policy.

**Option B — Upload custom profile:**

1. Navigate to **Catalog > MDM Profiles > Custom Profile**.
2. Upload `zs-pppc.mobileconfig`.
3. Add to target Policy.

**Background Items**

Navigate to **Catalog > MDM Profiles** and use the **Service Management - Managed Background Items** payload, or upload `zs-background-items.mobileconfig` as a custom profile.

{% hint style="info" %}
Addigy uses an agent-based architecture for software installs and MDM for profiles. Profile deployment may be slightly slower than software deployment. Addigy preserves the original PKG filename.
{% endhint %}

</details>

<details>

<summary>Mosyle Business</summary>

**PKG Upload & Deployment**

1. Log in to **Mosyle Business** (`business.mosyle.com`).
2. Navigate to **Management** (bottom navigation).
3. Select **Install App**.
4. Click **Add new profile** (top-right).
5. Choose **macOS** as the platform.
6. Select **Enterprise App** (not App Store).
7. Choose **Upload a PKG file** as the source.
8. Upload the MyZen `.pkg` file.
9. Configure:
   * **Installation type:** "Install and keep" or "Install once"
   * **Assignment:** Scope to specific users, devices, or groups.
10. Click **Save**.

**PPPC Profile Deployment**

**Option A — Built-in builder:**

1. Navigate to **Management**.
2. Select **Privacy & Security > Privacy Preferences**.
3. Click **Add new profile**.
4. Configure with the identifiers and code requirements above.
5. Scope and **Save**.

**Option B — Custom profile upload:**

1. Navigate to **Management > Custom MDM Profiles**.
2. Upload `zs-pppc.mobileconfig`.
3. Scope and **Save**.

**Background Items**

Use the **Managed Background Items** profile under the macOS 13+ management section, or upload `zs-background-items.mobileconfig` as a custom profile.

{% hint style="warning" %}
MyZen is a custom app — use the **Enterprise App** path, not "Auto Apps." Ensure the Package Identifier matches exactly to avoid reinstallation loops.
{% endhint %}

</details>

<details>

<summary>Kandji</summary>

**PKG Upload & Deployment**

1. Log in to **Kandji** (`your-tenant.kandji.io`).
2. Navigate to **Library**.
3. Click **Add New** and select **Custom App**.
4. Upload the MyZen `.pkg` file.
5. Configure:
   * **Install Type:** "Install once per device" or "Continuously enforce"
   * **Audit Script (optional):**

     ```bash
     #!/bin/bash
     if [ -d "/usr/local/zs/zs.app" ]; then
       exit 0  # Installed
     else
       exit 1  # Not installed, trigger reinstall
     fi
     ```
6. Click **Save**.
7. Navigate to **Blueprints** and add the Custom App to the target Blueprint.

**PPPC Profile Deployment**

**Option A — Native PPPC builder:**

1. Navigate to **Library**.
2. Click **Add New** and select **Privacy Preferences**.
3. Configure with identifiers and code requirements above.
4. Toggle Accessibility to **Allow**.
5. Click **Save** and add to target Blueprint.

**Option B — Custom profile upload:**

1. Navigate to **Library > Add New > Custom Profile**.
2. Upload `zs-pppc.mobileconfig`.
3. Add to target Blueprint.

**Background Items**

Use the dedicated **Managed Background Items** library item. Kandji provides a UI to configure rules by label, bundle ID, or team ID. Add Team ID `5KPT5U8WVR`.

{% hint style="info" %}
Kandji's "Continuously enforce" mode will reinstall the app if the audit script fails — useful for ensuring the agent stays installed. Kandji preserves the original PKG filename.
{% endhint %}

</details>

<details>

<summary>Hexnode UEM</summary>

**PKG Upload & Deployment**

1. Log in to **Hexnode UEM** (`your-instance.hexnodemdm.com`).
2. Navigate to **Apps > +Add Apps > Enterprise App**.
3. Select **macOS** as the platform.
4. Upload the MyZen `.pkg` file.
5. Provide a **Name** and optional description.
6. Click **Add**.
7. Navigate to **Policies > New Policy** (or edit an existing one).
8. Go to **macOS > App Management > Mandatory Apps**.
9. Select the uploaded app.
10. Navigate to **Policy Targets** and assign to device groups.
11. Click **Save**.

**PPPC Profile Deployment**

1. Navigate to **Policies > New Policy** (or edit existing).
2. Go to **macOS > Security > Privacy Preferences**.
3. Click **Configure**.
4. Add a new app entry:
   * **Bundle Identifier:** `ai.zs.zs`
   * **Code Requirement:** paste from `codesign -dr -` output
   * **Permissions:** Toggle Accessibility to **Grant**.
5. Assign the policy to target devices/groups.
6. Click **Save**.

**Background Items**

Use **Policies > macOS > Security > Managed Background Items** (Hexnode 7.8+).

{% hint style="info" %}
Hexnode preserves the original PKG filename. PPPC profiles require the MDM channel (not the agent channel).
{% endhint %}

</details>

<details>

<summary>SimpleMDM</summary>

**PKG Upload & Deployment**

1. Log in to **SimpleMDM** (`a.simplemdm.com`).
2. Navigate to **Apps** in the left sidebar.
3. Click **Add App** and choose **Custom App** (Enterprise App).
4. Upload the MyZen `.pkg` file.
5. Configure:
   * **Name:** e.g., "MyZenV2"
   * **Deploy automatically:** Toggle on if desired.
6. Click **Save**.
7. Navigate to **Device Groups** and assign the app.

**PPPC Profile Deployment**

**Option A — Native PPPC builder:**

1. Navigate to **Profiles** in the left sidebar.
2. Click **Create Profile**.
3. Select **Privacy Preferences** payload.
4. Configure with identifiers and code requirements above.
5. Click **Save** and assign to a Device Group.

**Option B — Custom profile upload:**

1. Navigate to **Profiles > Create Profile > Custom**.
2. Upload `zs-pppc.mobileconfig`.
3. Assign to a Device Group.

**Background Items**

Use **Profiles > Create Profile > Managed Background Items**, or upload `zs-background-items.mobileconfig` as a custom profile.

{% hint style="info" %}
SimpleMDM preserves the original PKG filename. No Smart Groups — only static Device Group assignments.
{% endhint %}

</details>

<details>

<summary>ManageEngine Endpoint Central</summary>

ManageEngine Endpoint Central (formerly Desktop Central) is part of the Zoho ManageEngine suite and supports macOS MDM enrollment, app deployment, and configuration profiles.

**Step 1 — Enroll macOS Devices**

Before deploying apps or profiles, devices must be MDM-enrolled:

1. Log in to **ManageEngine Endpoint Central** (cloud: `endpointcentral.manageengine.com`, or your on-premise URL).
2. Navigate to **MDM > Enrollment > Apple Enrollment**.
3. Ensure your **Apple Push Notification (APNs)** certificate is valid and uploaded.
4. Choose an enrollment method:
   * **Open Enrollment Link** — share a URL with users to self-enroll.
   * **Apple Business Manager (ABM)** — for zero-touch automated enrollment.
   * **Email Invitation** — send enrollment invitations to users.
5. Enrolled devices will appear under **MDM > Inventory > Devices**.

**Step 2 — Deploy PPPC Profile (Before PKG)**

**Option A — Built-in macOS PPPC Policy (recommended):**

ManageEngine Endpoint Central has a native **macOS PPPC Policy** builder under its configuration management:

1. Navigate to **Configuration > macOS PPPC Policy**.
2. Click **Create Collection** (or **Add Configuration**).
3. Fill in:
   * **Collection Name:** e.g., "zen-apps-access-grants" (internal reference)
   * **Description:** "Allow permissions of Accessibility and per browser grants"
   * **Category:** macOS PPPC Policy
   * **Platform:** Mac
4. Under the first app entry, configure the **ZS agent**:
   * **Identifier:** `ai.zs.zs`
   * **Code sign requirement:** `identifier "ai.zs.zs" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = "5KPT5U8WVR"`
   * **Static code validation:** No
   * **Allowed permissions:** Accessibility
   * **Other permissions:** User Controlled
5. Add **browser entries** for AppleEvents (URL reading). Click **Add** for each browser:
   * **Google Chrome:**
     * Identifier: `com.google.Chrome`
     * Code sign requirement: `identifier "com.google.Chrome" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = EQHXZ8M8AV`
     * Static code validation: No
   * **Safari:**
     * Identifier: `com.apple.Safari`
     * Code sign requirement: `identifier "com.apple.Safari" and anchor apple`
     * Static code validation: No
6. Click **Save**.
7. Navigate to **Targets** and select the target scope (Remote Office, custom groups, or individual devices).
8. Click **Deploy** / **Associate**.
9. Check the **Execution Status** — devices should show "Succeeded" after next check-in.

**Option B — Custom profile upload:**

1. Navigate to **Configuration > Profiles & Policies > macOS**.
2. Click **Create Profile** and select **Custom Configuration**.
3. Upload `zs-pppc.mobileconfig`.
4. Click **Save** and associate with target groups/devices.

**Step 3 — Deploy Background Items Profile**

1. Navigate to **MDM > Configuration > Profiles & Policies**.
2. Click **Create Profile** and select **macOS**.
3. Name: e.g., "ZS Background Items".
4. Select **Custom Configuration** as the payload type.
5. Upload `zs-background-items.mobileconfig`.
6. Click **Save**.
7. Associate with the same target groups/devices as the PPPC profile.

**Step 4 — Upload and Deploy the PKG**

{% hint style="danger" %}
**ManageEngine renames uploaded PKG files internally.** The stealth installer's filename contains the encoded license key, so a rename breaks installation. You **must** use a custom installation command that renames the file back to the original before running `installer`. See the installation command below.
{% endhint %}

1. Navigate to **Software Deployment > Packages > Add Package**.
2. Select **Mac** as the platform.
3. Fill in:
   * **Application Name:** e.g., "zs-mac" (internal reference only)
   * **Version:** Current version (e.g., "4.x")
   * **Vendor:** `ai.zs`
   * **Package License Type:** Commercial
   * **Path Type:** "This computer (used across multiple remote offices)"
4. Upload **two files**:
   * The MyZen `.pkg` installer (e.g., `zs.pkg`)
   * The uninstallation script (`remove_myzenv2_Version3.sh`) — download this from the We360.ai admin portal
5. Set the **Installation Command** to rename the file back to its original name before installing:

   ```bash
   mv "./zs.pkg" "./<CUSTOM_INSTALLER_PREFIX>.pkg" && installer -pkg "./<CUSTOM_INSTALLER_PREFIX>.pkg" -target "/"
   ```

   Replace `<CUSTOM_INSTALLER_PREFIX>` with the **exact original filename** of your stealth PKG (without the `.pkg` extension). This is the filename as downloaded from the We360.ai portal.
6. Set the **Uninstallation Command** to:

   ```bash
   /bin/sh remove_myzenv2_Version3.sh
   ```
7. Click **Save**.
8. Navigate to **Software Deployment > Deploy** and create a new deployment configuration.
9. Select the package and target the same groups/devices as your profiles.
10. Deploy.

{% file src="/files/FiA6hwqTgyo7JMJ48Jwn" %}
ManageEngine Endpoint Central — Package configuration reference (PDF)
{% endfile %}

{% file src="/files/HF2nwFjOnS8z8Qv9yYlf" %}
ManageEngine Endpoint Central — PPPC policy configuration reference (PDF)
{% endfile %}

**Step 5 — Verify Deployment**

1. Navigate to **MDM > Inventory > Devices** and select a target device.
2. Check the **Profiles** tab — both PPPC and Background Items profiles should show as **Installed**.
3. Check the **Apps** tab — the MyZen app should show as **Installed**.
4. Ask the end user to **logout/login** or **restart** for the agent to start.
5. Verify the endpoint appears online in the **We360.ai dashboard** at `portal.we360.ai`.

{% hint style="info" %}
**Cloud vs. on-premise:** ManageEngine Endpoint Central supports both cloud and on-premise deployments. The navigation paths above apply to both. Ensure your instance has the **macOS MDM module** enabled (it is a separately licensed module in some editions).
{% endhint %}

{% hint style="warning" %}
**APNs certificate renewal:** Your Apple Push Notification certificate must be renewed annually. If it expires, MDM communication with all macOS/iOS devices will break. Set a calendar reminder 30 days before expiration. Navigate to **MDM > Enrollment > Apple Enrollment > APNs Certificate** to check the expiry date.
{% endhint %}

</details>

<details>

<summary>Microsoft Intune (macOS)</summary>

Intune manages macOS through a combination of the **MDM channel** (configuration profiles) and the **Microsoft Intune management agent for macOS** (PKG app installs and shell scripts). Both are needed for a complete MyZen deployment.

{% hint style="info" %}
For the **Windows** agent via Intune (MSI → `.intunewin`), see [Microsoft Intune (Windows)](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/microsoft-intune).
{% endhint %}

**Prerequisites**

* macOS devices enrolled in Intune (Apple Business Manager / Automated Device Enrollment, or Company Portal enrollment).
* A valid **Apple Push Notification (APNs)** certificate in **Tenant administration > Connectors and tokens > Apple MDM Push certificate** (renew annually).
* The **Microsoft Intune management agent for macOS** version 2308.006 or later. It installs automatically the first time a macOS PKG app or shell script policy is assigned to the device.
* The MyZen `.pkg` is well under Intune's 8 GB app size limit.

**Step 1 — Deploy the PPPC Profile (before the PKG)**

**Option A — Upload the pre-built profile (recommended):**

1. Sign in to the **Microsoft Intune admin center** (`intune.microsoft.com`).
2. Navigate to **Devices > macOS > Configuration** and click **Create > New Policy**.
3. Set **Profile type** to **Templates**, select **Custom**, and click **Create**.
4. **Name:** e.g., "ZS App Permissions (PPPC)".
5. On the **Configuration settings** page:
   * **Deployment channel:** **Device channel** — TCC/PPPC payloads must be delivered on the device channel.
   * **Configuration profile file:** upload [`zs-pppc.mobileconfig`](https://github.com/zenstack-we360/documentation/tree/main/it-ops/.gitbook/assets/zs-pppc.mobileconfig).
6. Assign to the target **device groups** and click **Create**.

**Option B — Build it in the Settings Catalog:**

1. Navigate to **Devices > macOS > Configuration > Create > New Policy**.
2. Set **Profile type** to **Settings catalog** and click **Create**.
3. Click **Add settings** and search for **Privacy Preferences Policy Control**, then expand **Services**.
4. Add **Accessibility** and configure the ZS agent entry:
   * **Identifier:** `ai.zs.zs` (Stealth) or `ai.we360.MyZenV2` (Standard)
   * **Identifier Type:** Bundle ID
   * **Code Requirement:** paste the code requirement from the top of this page
   * **Static Code:** false
   * **Allowed:** true
5. Add **AppleEvents** entries for each browser you need URL reading from. Each entry needs both a *source* (the ZS agent identifier and code requirement) and a *receiver* (the browser bundle ID and its code requirement) — see [Supported Browsers for AppleEvents](#supported-browsers-for-appleevents-url-reading) below.
6. Assign to the target device groups and click **Create**.

{% hint style="warning" %}
**PPPC failures are silent.** Intune will report the profile as successfully applied even when macOS discards an entry because the code requirement doesn't match the app's signature. If Accessibility is still prompting the user after the profile lands, re-extract the code requirement with `codesign -dr -` on an installed endpoint and compare it character-for-character. The AppleEvents entries in the Settings Catalog are fiddly to build by hand — prefer Option A.
{% endhint %}

**Step 2 — Deploy the Background Items Profile**

**Option A — Settings catalog (native):**

1. Navigate to **Devices > macOS > Configuration > Create > New Policy > Settings catalog**.
2. Click **Add settings** and search for **Service Management - Managed Login Items**.
3. Add a rule:
   * **Rule Type:** Team Identifier
   * **Rule Value:** `5KPT5U8WVR`
   * **Team Identifier:** `5KPT5U8WVR` (Intune requires this field even though Apple treats it as optional)
4. Assign to the same device groups and click **Create**.

**Option B — Custom profile:** upload [`zs-background-items.mobileconfig`](https://github.com/zenstack-we360/documentation/tree/main/it-ops/.gitbook/assets/zs-background-items.mobileconfig) using the same **Templates > Custom** flow as Step 1 (Device channel).

**Step 3 — Upload and Deploy the PKG**

1. Navigate to **Apps > All apps > Create**.
2. Under **Select app type**, choose the **macOS** platform and select **macOS app (PKG)** — the *unmanaged* PKG type. Click **Select**.
3. Click **Select app package file** and upload the MyZen `.pkg`. Click **OK**.
4. Fill in **Name**, **Description**, and **Publisher** (Zenstack Private Limited), then click **Next**.
5. **Program** (optional) — you may supply a pre-install script to skip devices that already have the agent:

   ```bash
   #!/bin/bash
   # Exit non-zero to block the install (Intune retries at next check-in)
   if [ -d "/usr/local/zs/zs.app" ]; then
     exit 1   # already installed
   fi
   exit 0
   ```
6. **Requirements** — set the **Minimum Operating System** to the lowest macOS version you support.
7. **Detection rules:**
   * **Ignore app version:** **Yes** (the agent self-updates, so version matching would cause reinstall loops).
   * **Included apps:** add the bundle ID and build number of the app the PKG installs:

     | Variant  | Bundle ID          | Build number source                                                                |
     | -------- | ------------------ | ---------------------------------------------------------------------------------- |
     | Standard | `ai.we360.MyZenV2` | `defaults read /Applications/MyZenV2.app/Contents/Info CFBundleShortVersionString` |
     | Stealth  | `ai.zs.zs`         | `defaults read /usr/local/zs/zs.app/Contents/Info CFBundleShortVersionString`      |
8. Assign the app as **Required** to the target device groups.
9. **Review + create**.

{% hint style="info" %}
**Why the "macOS app (PKG)" type and not "Line-of-business app" (`.intunemac`)?** The unmanaged PKG app type is the only one that supports packages which install outside `/Applications/`, packages containing scripts, and component/non-flat packages. The Stealth build installs to `/usr/local/zs/`, so it requires this app type. The DMG app type does not apply — MyZen ships as a PKG.
{% endhint %}

{% hint style="warning" %}
**Stealth installer filename:** the Stealth PKG's filename encodes your organization's license. Intune stores and delivers the package from its own content cache, and — unlike ManageEngine — there is **no install command you can override** to rename the file back before `installer` runs. Verify on a pilot device that the Stealth agent enrolls into the correct tenant. If it does not, deploy via the **shell script method** below (recommended), or place your stealth config at `/Library/Preferences/zs.json` with a platform script (Step 5) that runs before the app assignment lands.
{% endhint %}

**Alternative to Step 3 — Deploy the Stealth PKG via Intune Shell Script (recommended for Stealth)**

Instead of uploading the PKG as an app, deploy it with an Intune **macOS shell script**. The script downloads the correct architecture's PKG directly from the We360.ai portal and inserts your license key itself, so Intune's content cache and filename handling never come into play.

1. Navigate to **Devices > macOS > Shell scripts** and click **Add**.
2. Paste (or upload as `.sh`) the script below, after replacing `<license-key>` with your organization's stealth license key — the Base64-encoded filename of your stealth PKG as downloaded from the portal, **without** the `.pkg` extension:

   ```bash
   #!/bin/bash
   set -e

   # REQUIRED: your stealth license key — the Base64-encoded installer
   # filename from the We360.ai portal, without the .pkg extension.
   LICENSE_KEY="<license-key>"

   if [ -z "$LICENSE_KEY" ] || [ "$LICENSE_KEY" = "<license-key>" ]; then
       echo "ERROR: LICENSE_KEY is not set. Paste your stealth license key." >&2
       exit 1
   fi

   ARCH="$(uname -m)"
   if [ "$ARCH" = "arm64" ]; then
       PKG_URL="https://portal.we360.ai/static/installers/zs-arm64.pkg"
   else
       PKG_URL="https://portal.we360.ai/static/installers/zs-amd64.pkg"
   fi

   DOWNLOAD_PATH="/tmp/zs-installer.pkg"
   PKG_PATH="/tmp/${LICENSE_KEY}.pkg"

   echo "Detected architecture: $ARCH"

   echo "Downloading installer..."
   if ! curl -fsSL "$PKG_URL" -o "$DOWNLOAD_PATH"; then
       echo "ERROR: Download failed" >&2
       exit 1
   fi

   echo "Renaming installer to insert license key..."
   mv "$DOWNLOAD_PATH" "$PKG_PATH"

   echo "Installing..."
   # ZS_KEY_CONFIG_BASE64_ENCODED doubles up the license insertion (v4.15+
   # agents); the renamed PKG filename covers older installers.
   if ! ZS_KEY_CONFIG_BASE64_ENCODED="$LICENSE_KEY" installer -pkg "$PKG_PATH" -target /; then
       echo "ERROR: Installation failed" >&2
       rm -f "$PKG_PATH"
       exit 1
   fi

   rm -f "$PKG_PATH"
   echo "Install completed successfully"
   exit 0
   ```
3. Configure the script settings:
   * **Run script as signed-in user:** **No** (must run as root).
   * **Hide script notifications on devices:** **Yes**.
   * **Script frequency:** Not configured (run once).
   * **Max number of times to retry if script fails:** 3 times.
4. Assign to the target device groups.

{% hint style="info" %}
The script inserts the license key **twice** for safety: it renames the PKG to `<license-key>.pkg` (the mechanism every agent version understands) and also exports `ZS_KEY_CONFIG_BASE64_ENCODED` (highest-precedence method on v4.15+ agents). See [Stealth License Key Insertion Methods](#stealth-license-key-insertion-methods).

Because a shell-script install bypasses Intune's app model, there is no Intune install/detection reporting — treat the **We360.ai dashboard** as the source of truth, which is already the recommendation for Stealth (see the reporting note above).
{% endhint %}

{% hint style="warning" %}
**Install reporting for Stealth:** Intune detects installs by looking for the bundle IDs listed under **Included apps**. Because the Stealth app lives outside `/Applications/`, install status in Intune may stay **Pending** or report a failure even when the agent installed correctly. Treat the **We360.ai dashboard** as the source of truth for Stealth rollouts, not the Intune app report.
{% endhint %}

**Step 4 — Screen Recording (Optional, User Action)**

Screen Recording cannot be granted by Intune or any other MDM. If your plan uses screenshots, instruct users to approve the prompt and then **logout/login**.

**Step 5 — Shell Scripts (config drop and uninstall)**

Intune has **no Uninstall assignment type for macOS PKG apps**. Removal is done with a shell script:

1. Navigate to **Devices > macOS > Shell scripts** and click **Add**.
2. Upload `remove_myzenv2_Version3.sh` (download it from the We360.ai admin portal).
3. Set **Run script as signed-in user:** **No** (run as root).
4. **Script frequency:** Not configured (run once).
5. Assign to the group of devices you want the agent removed from.

The same mechanism is used to drop `/Library/Preferences/zs.json` if you were supplied a stealth config file.

**Step 6 — Verify Deployment**

1. Navigate to **Devices > macOS > macOS devices**, select a target device, and open **Device configuration** — both the PPPC and Background Items profiles should show **Succeeded**.
2. Open **Managed Apps** — the MyZen app should show **Installed** (see the Stealth reporting caveat above).
3. On the endpoint, confirm the agent is present:

   ```bash
   ls -d /usr/local/zs/zs.app          # Stealth
   ls -d /Applications/MyZenV2.app     # Standard
   launchctl list | grep -i "zs\|MyZen"
   ```
4. Ask the end user to **logout/login** or **restart**.
5. Verify the endpoint appears online in the **We360.ai dashboard** at `portal.we360.ai`.

{% hint style="info" %}
**Agent logs on the endpoint** for troubleshooting Intune-side install failures: `/Library/Logs/Microsoft/Intune/` (management agent), plus MyZen's own install logs at `/tmp/zs-*.log` (Stealth) or `/tmp/MyZenV2-*.log` (Standard).
{% endhint %}

</details>

***

## Platform Comparison

| Feature                          | Jamf Pro | Jamf Now           | Addigy | Mosyle | Kandji | Hexnode | SimpleMDM | ManageEngine       | Intune                 |
| -------------------------------- | -------- | ------------------ | ------ | ------ | ------ | ------- | --------- | ------------------ | ---------------------- |
| PKG upload                       | Yes      | Yes (Plus)         | Yes    | Yes    | Yes    | Yes     | Yes       | Yes                | Yes (macOS app PKG)    |
| Preserves PKG filename           | Yes      | Verify             | Yes    | Yes    | Yes    | Yes     | Yes       | Yes                | Verify                 |
| Native PPPC builder              | Yes      | No                 | Yes    | Yes    | Yes    | Yes     | Yes       | Yes                | Yes (Settings catalog) |
| Custom .mobileconfig upload      | Yes      | Yes (Plus)         | Yes    | Yes    | Yes    | Yes     | Yes       | Yes                | Yes                    |
| Background Items Management      | Yes      | Via custom profile | Yes    | Yes    | Yes    | Yes     | Yes       | Via custom profile | Yes (Settings catalog) |
| Smart Groups / conditional logic | Yes      | No                 | Yes    | Yes    | Yes    | Yes     | No        | Yes                | Yes (dynamic groups)   |
| Uninstall via app assignment     | Yes      | Yes                | Yes    | Yes    | Yes    | Yes     | Yes       | Yes                | No (shell script)      |

***

## Supported Browsers for AppleEvents (URL Reading)

The PPPC profile (`zs-pppc.mobileconfig`) includes AppleEvents entries for the following browsers. This allows MyZen to read the active browser URL without triggering an Automation permission prompt for the user.

```
==================================================
       Browser Bundle ID & Codesign Report
==================================================

App:        Google Chrome
Bundle ID:  com.google.Chrome
Team ID:    EQHXZ8M8AV

App:        Safari
Bundle ID:  com.apple.Safari
Signing:    Apple system-signed

App:        Microsoft Edge
Bundle ID:  com.microsoft.edgemac
Team ID:    UBF8T346G9

App:        Firefox
Bundle ID:  org.mozilla.firefox
Team ID:    43AQ936H96

App:        Brave Browser
Bundle ID:  com.brave.Browser
Team ID:    KL8N8XSYF4

App:        Arc
Bundle ID:  company.thebrowser.Browser
Team ID:    S6N382Y83G

App:        Vivaldi
Bundle ID:  com.vivaldi.Vivaldi
Team ID:    4XF3XNRN6Y

App:        Opera / Opera GX
Bundle ID:  com.operasoftware.Opera / com.operasoftware.OperaGX
Signing:    Certificate leaf hash

App:        DuckDuckGo
Bundle ID:  com.duckduckgo.macos.browser
Team ID:    HKE973VLUW

App:        Chromium
Bundle ID:  org.chromium.Chromium
Signing:    Developer ID (no Team ID constraint)

App:        Orion (Kagi)
Bundle ID:  com.kagi.kagimacOS
Team ID:    TFVG979488

App:        Dia
Bundle ID:  company.thebrowser.dia
Team ID:    S6N382Y83G

App:        Aloha
Bundle ID:  com.alohabrowser.alohabrowser
Team ID:    DBVBNXAA55

==================================================
```

{% hint style="info" %}
If a browser used in your organization is not listed above, you can add an additional `AppleEvents` entry to the PPPC profile using the browser's bundle ID and code requirement. Run `codesign -dr - /Applications/BrowserName.app` to obtain the values.
{% endhint %}

***

## PPPC Profile Contents

Below is the full content of the `zs-pppc.mobileconfig` file for reference:

<details>

<summary>zs-pppc.mobileconfig (click to expand)</summary>

```xml
<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE plist PUBLIC "-//Apple//DTD PLIST 1.0//EN" "http://www.apple.com/DTDs/PropertyList-1.0.dtd">
<plist version="1.0">
<dict>
    <key>PayloadContent</key>
    <array>
        <dict>
            <key>PayloadDescription</key>
            <string>Configures Privacy Preferences for the ZS agent and supported browsers.</string>
            <key>PayloadDisplayName</key>
            <string>ZS Privacy Preferences</string>
            <key>PayloadIdentifier</key>
            <string>ai.zs.pppc</string>
            <key>PayloadOrganization</key>
            <string>Zenstack Private Limited</string>
            <key>PayloadType</key>
            <string>com.apple.TCC.configuration-profile-policy</string>
            <key>PayloadUUID</key>
            <string>A1B2C3D4-E5F6-7890-ABCD-EF1234567890</string>
            <key>PayloadVersion</key>
            <integer>1</integer>
            <key>Services</key>
            <dict>
                <key>Accessibility</key>
                <array>
                    <dict>
                        <key>Authorization</key>
                        <string>Allow</string>
                        <key>Identifier</key>
                        <string>ai.zs.zs</string>
                        <key>IdentifierType</key>
                        <string>bundleID</string>
                        <key>CodeRequirement</key>
                        <string>identifier "ai.zs.zs" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = "5KPT5U8WVR"</string>
                    </dict>
                </array>
                <key>ScreenCapture</key>
                <array>
                    <dict>
                        <key>Authorization</key>
                        <string>AllowStandardUserToSetSystemService</string>
                        <key>Identifier</key>
                        <string>ai.zs.zs</string>
                        <key>IdentifierType</key>
                        <string>bundleID</string>
                        <key>CodeRequirement</key>
                        <string>identifier "ai.zs.zs" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = "5KPT5U8WVR"</string>
                    </dict>
                </array>
                <key>AppleEvents</key>
                <array>
                    <!-- Entries for Chrome, Safari, Edge, Firefox, Brave, Arc, Vivaldi, Opera, DuckDuckGo, Chromium, Orion, Dia, Aloha -->
                    <!-- See the full file for all browser entries -->
                </array>
            </dict>
        </dict>
    </array>
    <key>PayloadDisplayName</key>
    <string>ZS — Privacy Preferences</string>
    <key>PayloadIdentifier</key>
    <string>ai.zs.profile.pppc</string>
    <key>PayloadOrganization</key>
    <string>Zenstack Private Limited</string>
    <key>PayloadScope</key>
    <string>System</string>
    <key>PayloadType</key>
    <string>Configuration</string>
    <key>PayloadUUID</key>
    <string>F1E2D3C4-B5A6-9870-FEDC-BA0987654321</string>
    <key>PayloadVersion</key>
    <integer>1</integer>
</dict>
</plist>
```

</details>

<details>

<summary>zs-background-items.mobileconfig (click to expand)</summary>

```xml
<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE plist PUBLIC "-//Apple//DTD PLIST 1.0//EN" "http://www.apple.com/DTDs/PropertyList-1.0.dtd">
<plist version="1.0">
<dict>
    <key>PayloadContent</key>
    <array>
        <dict>
            <key>PayloadType</key>
            <string>com.apple.servicemanagement</string>
            <key>PayloadVersion</key>
            <integer>1</integer>
            <key>PayloadIdentifier</key>
            <string>ai.zs.servicemanagement</string>
            <key>PayloadUUID</key>
            <string>B2C3D4E5-F6A7-8901-BCDE-F12345678901</string>
            <key>PayloadDisplayName</key>
            <string>ZS — Managed Background Items</string>
            <key>Rules</key>
            <array>
                <dict>
                    <key>RuleType</key>
                    <string>TeamIdentifier</string>
                    <key>RuleValue</key>
                    <string>5KPT5U8WVR</string>
                    <key>Comment</key>
                    <string>Allow all ZS app background items</string>
                </dict>
            </array>
        </dict>
    </array>
    <key>PayloadDisplayName</key>
    <string>ZS — Background Items Management</string>
    <key>PayloadIdentifier</key>
    <string>ai.zs.profile.servicemanagement</string>
    <key>PayloadOrganization</key>
    <string>Zenstack Private Limited</string>
    <key>PayloadScope</key>
    <string>System</string>
    <key>PayloadType</key>
    <string>Configuration</string>
    <key>PayloadUUID</key>
    <string>C3D4E5F6-A7B8-9012-CDEF-123456789012</string>
    <key>PayloadVersion</key>
    <integer>1</integer>
</dict>
</plist>
```

</details>

<details>

<summary>zs-screen-capture.mobileconfig (click to expand)</summary>

```xml
<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE plist PUBLIC "-//Apple//DTD PLIST 1.0//EN" "http://www.apple.com/DTDs/PropertyList-1.0.dtd">
<plist version="1.0">
<dict>
    <key>PayloadContent</key>
    <array>
        <dict>
            <key>PayloadDescription</key>
            <string>Screen Capture PPPC entry for the ZS agent.</string>
            <key>PayloadDisplayName</key>
            <string>ZS — Screen Recording Permission</string>
            <key>PayloadIdentifier</key>
            <string>ai.zs.pppc.screencapture</string>
            <key>PayloadOrganization</key>
            <string>Zenstack Private Limited</string>
            <key>PayloadType</key>
            <string>com.apple.TCC.configuration-profile-policy</string>
            <key>PayloadUUID</key>
            <string>D4E5F6A7-B8C9-0123-DEFA-234567890123</string>
            <key>PayloadVersion</key>
            <integer>1</integer>
            <key>Services</key>
            <dict>
                <key>ScreenCapture</key>
                <array>
                    <dict>
                        <key>Authorization</key>
                        <string>AllowStandardUserToSetSystemService</string>
                        <key>Identifier</key>
                        <string>ai.zs.zs</string>
                        <key>IdentifierType</key>
                        <string>bundleID</string>
                        <key>CodeRequirement</key>
                        <string>identifier "ai.zs.zs" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = "5KPT5U8WVR"</string>
                    </dict>
                </array>
            </dict>
        </dict>
    </array>
    <key>PayloadDisplayName</key>
    <string>ZS — Screen Recording</string>
    <key>PayloadIdentifier</key>
    <string>ai.zs.profile.pppc.screencapture</string>
    <key>PayloadOrganization</key>
    <string>Zenstack Private Limited</string>
    <key>PayloadScope</key>
    <string>System</string>
    <key>PayloadType</key>
    <string>Configuration</string>
    <key>PayloadUUID</key>
    <string>E5F6A7B8-C9D0-1234-EFAB-345678901234</string>
    <key>PayloadVersion</key>
    <integer>1</integer>
</dict>
</plist>
```

</details>


# Direct Link

Let employees install the We360.ai MyZen agent from a direct download link in the admin portal. Covers self-install setup for Windows and macOS employee monitoring software deployment.

Use this method when employees need to download and install the We360.ai MyZen agent themselves from the We360.ai portal. It is the simplest deployment option when physical access, remote access, or device management tools are not available.

## When to Use This Method

* Devices are not on a shared network or VPN (preventing GPO/remote deployment).
* You want employees to install the agent themselves.
* No MDM or RMM infrastructure is available.

This direct download method supports both **Standard** and **Stealth** installers for Windows and macOS.

{% hint style="warning" %}
**Stealth installer security:** The stealth installer should ideally not be shared with employees directly, as they may misuse it or extract the embedded license key from within the installer. If stealth deployment is required, prefer an administrator-controlled method (GPO, MDM, or command-line).
{% endhint %}

{% hint style="danger" %}
**Do not rename the stealth installer file.** The **stealth** installer filename is tied to your organization's license. Renaming it, or allowing extra characters to be appended (e.g. `(1)` or `(2)` from duplicate downloads), will cause the installation to fail.
{% endhint %}

## How It Works

1. After employees are added in the We360.ai portal, they receive a **welcome email** with login credentials.
2. Employees log in to the We360.ai portal using those credentials.
3. They click the **download icon** in the top-right corner to reach the Download page.
4. They select their operating system (Windows or Mac) and click **Standard**. For stealth install, the installer has to be shared by the tenant administrator.
5. They open the downloaded file and follow the installation prompts.

## Administrator Steps

1. Add employees in the We360.ai portal (they receive welcome emails automatically).
2. Optionally send additional instructions pointing employees to the download page.
3. Monitor installation status via the admin dashboard.

| Platform | Standard | Stealth            |
| -------- | -------- | ------------------ |
| Windows  | Yes      | Yes (with caution) |
| macOS    | Yes      | Yes (with caution) |


# Mobile Deployment

Deploy We360.ai mobile agent on Android and iOS via MDM for employee field tracking and monitoring.

Setting up MDM for Android/iOS field tracking.

*Content coming soon...*


# Agent Runtime & Update Reference

Reference for the desktop agent's runtime components, log and data locations, the auto-update system, and local commands IT admins can run to inspect or troubleshoot updates on a machine.

This page is a machine-level reference for the desktop agent: which processes run, where they log, how auto-update works end to end, and the commands you can run locally to verify all of it. It is primarily written for **Windows Standard** installs, with Stealth and macOS notes where they differ.

If you are diagnosing a broken agent rather than inspecting a healthy one, start with [Desktop Doctor](/deployment-and-it-ops/troubleshooting-and-support/desktop-doctor) and the [Tracker Failure Diagnostic Guide](/deployment-and-it-ops/troubleshooting-and-support/tracker-failure-guide).

***

## Runtime components

### Windows — Standard

Install directory: `C:\Program Files\Zenstack\MyZenV2`

| Component              | Path                                                     | Role                                                                                     |
| ---------------------- | -------------------------------------------------------- | ---------------------------------------------------------------------------------------- |
| `MyZenV2.exe`          | `C:\Program Files\Zenstack\MyZenV2\MyZenV2.exe`          | Main tray application (tracking, screenshots, punch in/out UI). Runs per logged-in user. |
| `zen_cli.exe`          | `C:\Program Files\Zenstack\MyZenV2\zen_cli.exe`          | Command-line helper used for install-time checks and diagnostics.                        |
| `install_notifier.exe` | `C:\Program Files\Zenstack\MyZenV2\install_notifier.exe` | Notifies logged-in users after an update installs.                                       |
| `ffmpeg.exe`           | `C:\Program Files\Zenstack\MyZenV2\ffmpeg.exe`           | Screen-recording encoder, launched on demand by the main app.                            |
| `version.txt`          | `C:\Program Files\Zenstack\MyZenV2\version.txt`          | The locally installed version.                                                           |

{% hint style="info" %}
**Windows Standard has no on-machine auto-updater today** — there is no resident updater process and no scheduled task. Machines are updated by deploying the new MSI through your normal software-distribution channel (Intune, GPO, SCCM, or a manual reinstall); the MSI upgrades in place and preserves configuration. A native auto-updater (mirroring the macOS launchd updater) is planned for an upcoming release. macOS Standard and Stealth (both platforms) do auto-update — see below.
{% endhint %}

### Windows — Stealth

Install directory: `C:\Program Files\zs`. The supervisors live outside the install directory:

| Component             | Path                        | Role                                                                                                                                                                  |
| --------------------- | --------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `svcmonitor.exe`      | `C:\Windows\svcmonitor.exe` | Windows service / watchdog. Runs the update check loop **inline** (there is no separate updater task for stealth), supervises the agent, and applies domain blocking. |
| `svcrunner.exe`       | `C:\Windows\svcrunner.exe`  | Secondary watchdog that keeps `svcmonitor` and the agent alive.                                                                                                       |
| `MyZenV2.exe` (agent) | under `C:\Program Files\zs` | The tracking agent, run headless per user session.                                                                                                                    |

### macOS — Standard

| Component         | Path                                                                                                              |
| ----------------- | ----------------------------------------------------------------------------------------------------------------- |
| Main app          | `/Applications/MyZenV2.app`                                                                                       |
| Installed version | `/Applications/MyZenV2.app/Contents/MacOS/version.txt`                                                            |
| Updater           | `updater` binary inside the app bundle, scheduled by the `standard-updater` launchd plist (same 12-hour cadence). |

***

## Log and data locations (Windows)

| What                               | Location                                                                                                                                                                                                                                                                                                 |
| ---------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Main app logs (Standard)           | `%APPDATA%\ai.we360\MyZen\logs\log_YYYY-MM-DD.log`                                                                                                                                                                                                                                                       |
| Local activity database (Standard) | `%APPDATA%\ai.we360\MyZen\zs.db`                                                                                                                                                                                                                                                                         |
| App configuration (Standard)       | `%APPDATA%\ai.we360\MyZen.ini`                                                                                                                                                                                                                                                                           |
| Go helper / updater logs           | `zen-<component>-YYYY-MM-DD.log` in the process's temp directory — `%TEMP%` for per-user processes, `C:\Windows\Temp` (or `C:\ProgramData\Temp` if that is not writable) for `SYSTEM` processes such as `zs_manager.exe` and `svcmonitor.exe`. Example: `C:\Windows\Temp\zen-zs_manager-2026-07-14.log`. |
| Stealth service logs               | `C:\Windows\Temp\zen-svcmonitor-YYYY-MM-DD.log` — each service start logs one grep-friendly `Updater diagnostics:` line containing the resolved installer URL, remote version, and installed version.                                                                                                    |

{% hint style="info" %}
**Enable verbose debug logging:** create an empty file named `.zs-debug` in `%TEMP%` or in the user's home directory. On the next start, the Go components switch to debug-level logging and force file logging on. Delete the file to return to normal.
{% endhint %}

On macOS, the equivalent app data directory is `~/Library/Application Support/ai.we360/MyZen/` (logs in `logs/`, database `zs.db`), and Go component logs go to the system temp directory with the same `zen-<component>-<date>.log` naming.

***

## How auto-update works

Auto-update currently applies to **macOS Standard** (the launchd-scheduled `updater` binary inside the app bundle) and **Stealth** (the update loop inside `svcmonitor`). Windows Standard is updated by redeploying the MSI — see the commands below. Every auto-update run walks the same pipeline:

1. **Resolve the tenant** from the local configuration.
2. **Auto-update policy gate.** The updater asks the We360 origin server whether this device/tenant allows auto-update:
   * A **device-level** setting (per machine) is checked first, then the **tenant manifest**'s auto-update flag.
   * If no tenant is configured yet (fresh install), updates are **allowed** so unconfigured machines don't strand on stale builds.
   * If a tenant *is* configured but the policy cannot be fetched, updates are **skipped** — the updater never installs without an authoritative "yes".
3. **Resolve the installer URL.** Server-first: `GET /discover/v1/tenant/{id}/update-urls/` on the origin server returns the per-tenant installer URLs by brand / OS / architecture / asset type. If the endpoint is unreachable or has no matching asset, the updater falls back to the CDN base URL baked into the binary at build time plus the canonical filename (`MyZenV2.msi` on Windows, `MyZenV2-<arch>.pkg` on macOS).
4. **Fetch the version manifest.** Every published installer has a JSON sidecar at `<installer-url>.version` containing `version`, `build_version`, `commit`, `built_at`, `md5`, brand, OS, and arch. Any network error, non-2xx response, or implausible version string skips the tick — the updater never installs from a junk response.
5. **Version gate.** The update proceeds only when the remote version is **strictly newer** than the local `version.txt` (semver comparison). This blocks accidental downgrades; a rollback requires publishing a higher-versioned build.
6. **Download, verify, install.** The installer is downloaded, its MD5 is verified against the manifest, and it is installed silently (`SYSTEM` context on Windows, so no UAC prompt). Users are then notified via `install_notifier`.

### Local override markers

Three sentinel files under `C:\ProgramData` (or `/tmp` and `/etc` on Unix) let you veto updates on a specific machine — useful for pinning a machine during troubleshooting or QA:

| File                              | Effect                                        |
| --------------------------------- | --------------------------------------------- |
| `C:\ProgramData\zs-do-not-update` | Skip all update installs on this machine.     |
| `C:\ProgramData\zs-dev-mode`      | Same skip, intended for development machines. |
| `C:\ProgramData\zs-updater-abort` | Aborts an in-flight update.                   |

Create them as empty files; delete them to re-enable updates.

***

## Local commands — checking the update system on a machine

All commands below are for Windows Standard, run from an **elevated** PowerShell or Command Prompt unless noted.

### 1. What version is installed?

```powershell
type "C:\Program Files\Zenstack\MyZenV2\version.txt"
```

### 2. What version is published?

Fetch the `.version` sidecar next to the published installer:

```powershell
curl.exe https://portal.we360.ai/static/installers/MyZenV2.msi.version
```

You should get a small JSON document with `version`, `md5`, `built_at`, etc. If you get HTML instead, the URL is wrong or being intercepted by a proxy — see [Network & Security Hardening](/deployment-and-it-ops/security-and-hardening/network-and-security-hardening). Tenants with a custom installer base URL should substitute their own base path.

### 3. Update the machine

Download the current MSI (see [Download Links & Utilities](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links)) and install it over the existing version — it upgrades in place and preserves configuration:

```powershell
msiexec /i MyZenV2.msi /qn
```

For fleet-wide updates use your normal channel: [Intune](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/microsoft-intune), [GPO](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/active-directory-gpo), or [command line](/deployment-and-it-ops/deployment/agent-deployment-hub/mass-deployment/command-line-msi).

### 4. Stealth machines

Stealth has no standalone updater or scheduled task — `svcmonitor.exe` runs the same pipeline internally. To check it, grep the service log for the diagnostics line:

```powershell
findstr /C:"Updater diagnostics" C:\Windows\Temp\zen-svcmonitor-*.log
```

The line includes `effective_base_url`, `installer_url`, `installed_version`, `remote_version`, and `is_remote_newer` — a complete snapshot of what the updater would do on its next tick.

***

## zs\_manager — online installer utility (Windows)

`zs_manager.exe` is a **web-installer wrapper**: a small self-contained utility that resolves the correct installer for the machine's tenant, downloads it, and runs it silently. It is a support/IT tool — it is **not** part of the agent install, not a resident process, and not the mechanism by which deployed agents update. It is still **work in progress**, so treat its behavior as subject to change.

The same binary also powers the renamed **standalone web installers** (e.g. `myzen-standalone.exe` for a standard install, or a stealth installer named after the license key) — those are distributed separately and behave as one-shot online installers; the `zs_manager.exe` download here is the raw utility with the mode switches below.

Download: [zs\_manager.exe](https://portal.we360.ai/static/utils/windows/zs_manager.exe) (also listed on [Download Links & Utilities](/deployment-and-it-ops/deployment/agent-deployment-hub/download-links)).

Run it elevated. Modes:

| Command                            | What it does                                                                                                                                                                                                                                                                                                                                  |
| ---------------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `zs_manager.exe /updater-standard` | Install/repair the **Standard** agent: checks the tenant's auto-update policy, resolves the installer URL, downloads, installs silently. Add `/patch-only` to refuse a full reinstall when the existing installation looks valid.                                                                                                             |
| `zs_manager.exe /updater-stealth`  | Same flow for the **Stealth** agent (requires an onboarded machine with a valid key configuration).                                                                                                                                                                                                                                           |
| `... --dry-run`                    | Append to either mode to print a `[DRY-RUN]` report **without changing the machine**: system info, the live update context from the origin server (`AutoUpdateEnabled`, `InstallerBaseUrl`), and the exact installer URL a real run would download. This is the quickest way to check what the update system sees for a given machine/tenant. |

Logs go to `zen-zs_manager-YYYY-MM-DD.log` in the temp directory (`C:\Windows\Temp` when run elevated).

For testing, the `WE360_INSTALL_BASE_URL` environment variable overrides the built-in CDN fallback URL so the flow can be pointed at a staging or local HTTP server serving `MyZenV2.msi` + `MyZenV2.msi.version`. Per-tenant URLs returned by the origin server still take precedence over the override.

***

## macOS quick reference

| Task              | Command                                                                                |
| ----------------- | -------------------------------------------------------------------------------------- |
| Installed version | `cat /Applications/MyZenV2.app/Contents/MacOS/version.txt`                             |
| Updater config    | `/Applications/MyZenV2.app/Contents/MacOS/updater --show-config`                       |
| Dry-run           | `sudo /Applications/MyZenV2.app/Contents/MacOS/updater --dry-run`                      |
| Update schedule   | `launchctl print system \| grep -i updater` (loaded from the `standard-updater` plist) |
| Skip markers      | `/tmp/zs-do-not-update`, `/etc/zs-dev-mode`                                            |


# On-Premise and BYOC

VM and Kubernetes deployment requirements for on-premise and BYOC installations.

We offer two main variants of on-premise/bring-your-own-cloud deployments:

### **Deployment Types**

* VM (services are run in Docker Containers)
  * Single VM installations work for 300-2000 users.
  * We can separate the Databases onto separate VMs/Managed Solutions for easier backups.
* Kubernetes with Managed Databases
  * This is a scalable and highly available deployment for 1000+ users.

***

### **VM Based Deployment Requirements (300-2000 Users)**

* **Linux VM with:**
  * 16 Cores and 64 GB of RAM
  * 512 GB SSD (resizable)
    * If the infrastructure does not support dynamic disk expansion, please provision a larger initial volume.
    * Disk backups/replication should be enabled.
  * Ubuntu Server LTS (24.04) OS
    * Username should be ubuntu or we360user.
  * Sufficient Network Bandwidth
* **External Storage for Screenshots and Backups (Elastic)**
  * External S3-compatible Object Storage (preferred)

    *or*
  * NFS like distributed file system

    * Durability and corruption issues may surface

    *or*
  * Additional attached disks
    * Please note that automated backup workflows are not compatible with locally attached disks.
* **Network Access**
  * SSH Access for deployment and maintenance
  * Outbound access for:
    * Fetching configuration,
    * Licensing details and
    * Updates
* **Managed/External Databases (Optional)**
  * Managed PostgreSQL Database (Optional, but recommended)
  * Clickhouse Database (Optional)

### **Kubernetes Requirements (1000+ Users)**

* Kubernetes Cluster (1.30+) with appropriate networking and load balancing.
* Kubernetes Worker Nodes:
  * 3-6 nodes of size 8 cores and 32GB RAM (worker node sizing/numbers will be based on user count)
  * Ensure worker nodes have a minimum of 100GB available for image caching and ephemeral storage.
* A storage provisioner (CSI Driver) that can provision at least 100 GB of disk space (SSD preferred)
* We require two databases to be installed separately, either on VMs or as Managed Services.
  * PostgreSQL Database
  * Clickhouse Database

***

### **Database Requirements**

* Managed PostgreSQL 16/17/18 Database with 2 Cores, 8GB RAM and a 256 GB SSD.
  * Please ensure that all VMs/Containers on the private network can connect to the database by making appropriate changes to `pg_hba.conf`.
    * This is typically managed via the provider's security group, server parameters or firewall settings for Cloud Managed DBs.
  * The server must be able support 300 connections.
  * Please ensure you have backups and WAL replication/PITR enabled.
* Clickhouse Database with 2 Cores, 8 GB RAM and a 400 GB SSD.
  * Please ensure that you have disk snapshots enabled.

#### **Additional Notes:**

* We can share Images for Clickhouse upon request.

### **Network Requirements**

#### **Outbound Access**

* All Outbound Internet access must open during deployment.
* Following outbound access must be open always:
  * To our licensing server at <code class="expression">space.vars.company\_licensing\_server\_url</code> both from the on-prem infrastructure and from client machines. No customer data is sent to this service except for licensing and tenant configuration.
  * Container registries:
    * docker.io
    * gcr.io
    * quay.io
    * \*.azurecr.io
    * docker.elastic.co
    * \*.amazonaws.com
    * registry.gitlab.com
    * container-registry.we360.ai
  * Python package hosts:
    * pypi.org
    * pypi.python.org
    * pythonhosted.org
    * files.pythonhosted.org
  * Ubuntu and Debian repository servers (along with the cloud provided mirrors) on HTTP and HTTPS:
    * security.debian.org
    * deb.debian.org
    * ftp.debian.org
    * archive.ubuntu.com
  * Azure Blob Storage, AWS S3 and Google Cloud Storage (to download our configuration files and installation scripts).
  * raw\.githubusercontent.com (to download configuration files).

#### **Internal Access**

* All internal access must be open i.e. all VMs must be able to communicate with each other on all ports with TCP, UDP and ICMP. Please make appropriate changes to the Security Groups, Cloud/Data Centre Firewalls and Linux Server Firewalls (iptables, ufw, systemd etc.).

#### **Inbound Access**

* Ports 80 and 443 must be open for Inbound Traffic for HTTP(S)/Websocket/TCP.
* In case of a single node deployment, inbound SSH must be allowed.

***

### **IPs, DNS and Certificates**

* Domains and certificates for API and Auth servers.
  * These domain names must resolve to the correct Load Balancer/VM both in the private network of the VM/Cluster and on the client machines.
  * Suggested domains are as follows:
    * `api.<your_base_subdomain>` and\
      `auth.<your_base_subdomain>`
    * `api-we360.<your_base_subdomain>` and\
      `auth-we360.<your_base_subdomain>`
* Depending on the exact architecture, two additional domains and their SSL certificates might be required.

#### **IP Addresses**

We will require 1-2 public IP addresses.

***

### **Email Server**

* To enable email functionality for your on-premises deployment, we require access to an SMTP server. Share its:
  * From Display Name and From Email Address
  * Authentication Credentials - Username and password or API key
  * Server details (Hostname/IP Address, Port Number)
  * Encryption Method - TLS/STARTTLS/SSL
* Recommended SMTP Service Providers:
  * Zeptomail by Zoho
  * Amazon Simple Email Service (SES)
  * Mailgun

### **Monitoring and Alerts**

* Disk Usage Alert (80% threshold) - Configure monitoring to trigger alerts when any disk partition reaches 80% capacity.
* External Storage Usage Alert
* CPU Usage (Optional)
* Memory Usage (Optional)

### **Storage Estimates**

* Screenshots Data captured per user per month (at 5 minute frequency, assuming 8 working hours): 1 GB
* Screen Recording Data captured per user per month (assuming 8 working hours): 15GB


# LDAP / Kerberos Login (SSO)

Directory-based sign-in (LDAP / Active Directory) and optional silent Kerberos SSO for on-premise deployments — and the information we need from you to set it up.

On-premise deployments can authenticate users against your existing directory instead of separate We360 credentials. Two modes are supported:

* **Directory login** — users sign in with their existing directory (LDAP / Active Directory) username and password.
* **Silent SSO (Kerberos)** — on domain-joined Windows machines, users are logged in automatically from their existing Windows session, with no username/password prompt.

Both are optional and are configured per deployment.

{% hint style="info" %}
**We360 performs the configuration.** You do not need to set up anything in the application. We only need some details about your directory environment, listed below. The Kerberos (silent SSO) mode is optional — set it up only if you want zero-prompt login.
{% endhint %}

## Information we need from you

To enable this, we ask your IT / directory administrator for the following. The downloadable form at the bottom of this page has a fill-in table for each item.

1. **Directory server** — type (Active Directory / other LDAP), version, host name(s), port, and whether the connection uses LDAPS/TLS (plus the CA certificate if it is issued by a private CA).
2. **Service (bind) account** — a dedicated **read-only** account we use to look up users: its distinguished name (DN) and password.
3. **Directory structure** — the base DN and the specific container(s)/OU where the users who should log in are located, and whether all of them or only a subset (e.g. a group) get access.
4. **User attributes** — which fields hold the login username, email, and name, and a stable unique identifier.
5. **Kerberos / SSO** *(optional)* — the Kerberos realm, KDC (domain controller) host names, confirmation that machines are domain-joined, and a service account + SPN + **keytab** your AD administrator generates for the login service.
6. **Network & environment** — connectivity from the We360 server to the directory (and KDC), DNS resolution, and clock synchronization.
7. **Test accounts** *(optional)* — one or two non-critical accounts so we can validate login before rollout.

{% hint style="warning" %}
**Handle secrets securely.** Passwords, certificates, keytab files, and test credentials must be shared through a secure channel that your We360 contact provides — never by email or inside the form document.
{% endhint %}

## Requirements form

Download, complete the **"Your value"** column, and return the form to your We360 contact. Items marked **(secure)** are sent separately via the secure channel.

{% file src="/files/Wvl1XcJ6WE8aRwoNiCMl" %}
We360 — Directory Integration (LDAP / Active Directory) Information Request
{% endfile %}


# LDAP / Kerberos SSO - Runbook

Internal engineering runbook for standing up AD/LDAP + Kerberos (SPNEGO) silent SSO for the standard desktop app end-to-end, with the non-obvious gotchas that break it. Companion to the client-facing

End-to-end configuration for silent AD login: a domain-joined Windows client runs the standard app, which auto-discovers the tenant from a pre-provisioned `zs-origin.json`, opens the browser to Keycloak, the browser negotiates Kerberos (SPNEGO) with no prompt, and core-service JIT-provisions the user on first login.

> Reproducible local rig (Samba AD DC + Keycloak federation + Windows join scripts) lives in `java-apps/.deployment/ad-kerberos/`. This page is the "why", the correct settings, and the failure modes.

## The chain (what must line up)

```
domain-joined Windows client (domain-user session → Kerberos TGT)
   │  reads C:\Windows\System32\zs-origin.json  → tenant + apiKeycloakUrl + realm
   │  browser (Chrome/Edge) with SPNEGO allowlist for the Keycloak host
   ▼
Keycloak (developer/tenant realm)
   │  LDAP user federation (LDAPS) + Kerberos, editMode = UNSYNCED
   │  SPN HTTP/<keycloak-host> + AES keytab
   ▼
core-service  (JIT provisioning: /api/v2/onboarding/ensure-federated-identity)
   │  tenant StandardConfig.autoCreateUsers = true
   ▼
We360 Identity created; identity_id claim written back to Keycloak
```

## Keycloak federation — the settings that matter

| Setting       | Value                                                                                    | Why                                                                                                                                                                            |
| ------------- | ---------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| Connection    | `ldaps://<dc>:636`                                                                       | Samba blocks cleartext simple binds; **do not** set `ldap server require strong auth = no`.                                                                                    |
| TLS cert      | Must carry an **IP SAN** if Keycloak dials the DC by IP                                  | Java LDAPS verifies the host; a DNS-only SAN fails on an IP dial.                                                                                                              |
| Truststore    | DC CA in Keycloak `conf/truststores/`                                                    | Loaded at startup only — **restart Keycloak** after adding.                                                                                                                    |
| **editMode**  | **`UNSYNCED`** (not `READ_ONLY`)                                                         | READ\_ONLY makes the imported user's federated storage non-writable, so the `identity_id` attribute can't be stored → JIT fails with *"Federated storage is not writable"*.    |
| importEnabled | `true`                                                                                   | The `identity_id` attribute lives on the imported (local) copy.                                                                                                                |
| Mappers       | username→`sAMAccountName`, email→`mail`, **first name→`givenName`**, last name→`sn`      | The API-created federation is easy to leave **missing the first-name mapper**; then `firstName` is null and JIT fails validation *"First name and last name cannot be empty"*. |
| Kerberos      | `allowKerberosAuthentication=true`, `serverPrincipal=HTTP/<host>@REALM`, `keyTab=<path>` | `<host>` MUST equal the host in the manifest's `apiKeycloakUrl` (see below).                                                                                                   |

## Kerberos SPN / keytab — must match the manifest host and be AES

* The browser derives the SPN from the URL it opens: `apiKeycloakUrl` host → `HTTP/<that-host>`. The AD SPN, the exported keytab, and Keycloak's `serverPrincipal` must **all** use that exact host. A mismatch = Keycloak can't decrypt the ticket → silent fallback to the username/password form.
* **Use AES, not RC4.** Set `msDS-SupportedEncryptionTypes = 24` (AES128+AES256) on the service account, then re-export the keytab. JDK 17+/21 (Keycloak) **rejects RC4** with *"Encryption type RC4 with HMAC is not supported/enabled"*, which also falls back to the form. Verify the keytab: `ktutil -k <file> list` should show `aes256-cts-hmac-sha1-96` / `aes128-…`, not `arcfour-hmac`.
* After changing enctype, purge the client's cached ticket (`klist purge` in the domain-user session) so it fetches a fresh AES service ticket.

## The Windows client

1. **Domain-joined** and the interactive desktop session must be a **domain user** (e.g. `DOMAIN\einstein`) — a *local* account has **no Kerberos TGT**, so SPNEGO cannot happen regardless of everything else. Check with `klist` in that session.
2. **Browser SPNEGO allowlist (whitelist the Keycloak host).** By default Chrome and Edge do **not** perform Kerberos/Negotiate for any site — they do **not** honour the IE "Local Intranet" zone for this. You must explicitly allowlist the Keycloak host via the **`AuthServerAllowlist`** policy. The host you list MUST be the host in the manifest's `apiKeycloakUrl` — the same host the SPN/keytab use (e.g. `api.local.we360.ai`). Listing the wrong host = no Negotiate = password prompt.

   **What to allowlist.** A comma-separated list of hosts; wildcards are allowed, so a whole domain works — e.g. `api.local.we360.ai` or `*.we360.ai`. Do **not** include a scheme or port (`https://`, `:8080`) — host only.

   **Deploy via Group Policy (fleet).** Import the Chrome/Edge ADMX templates, then set:

   * Chrome: *Computer Configuration → Administrative Templates → Google → Google Chrome → HTTP authentication → **Authentication server allowlist*** = `<host or *.domain>`
   * Edge: *… → Microsoft Edge → **Authentication server allowlist*** = `<host or *.domain>`

   **Or set the registry directly** (per-machine, `/reg:64` on ARM64/64-bit Windows):

   ```
   reg add HKLM\SOFTWARE\Policies\Google\Chrome  /v AuthServerAllowlist /t REG_SZ /d "*.we360.ai" /f /reg:64
   reg add HKLM\SOFTWARE\Policies\Microsoft\Edge  /v AuthServerAllowlist /t REG_SZ /d "*.we360.ai" /f /reg:64
   ```

   Set the policy for **every** browser the app may open — the standard app launches the OS **default browser**, which is often Edge. **Fully quit and relaunch** the browser (kill all `chrome.exe` / `msedge.exe`) so it reloads the policy — a browser that was already running will ignore a freshly-set allowlist.

   `AuthNegotiateDelegateAllowlist` (same key) is **only** needed if the Keycloak host must delegate the user's ticket onward (constrained delegation); plain SSO does not need it — leave it unset unless you have that requirement.

   **Firefox** (if used) doesn't read these policies — set `network.negotiate-auth.trusted-uris = <host or .domain>` (via `about:config` or a policy) instead.

   **Reading the symptom:**

   * **Basic-auth popup** (browser's own username/password box) → host not allowlisted (or browser not restarted). Fix the allowlist.
   * **Proper Keycloak login form** → Negotiate *was* attempted but Keycloak rejected the ticket (server-side GSS: RC4 vs AES, or SPN/host mismatch — see above).
3. Post-domain-join, the network profile switches to **Domain** — if OpenSSH (or any management) was firewalled to Private/Public only, it goes dark. Widen the rule to `-Profile Any` if you manage the box remotely.

## `zs-origin.json` (pre-provisioned discovery)

* Content is exactly the origin by-base-domain response — open in a browser: `https://origin.in.we360.ai/discover/tenant_by_base_domain/?baseDomain=<baseDomain>` and save the JSON verbatim. See *Pre-Provisioned Origin Data* for schema/trust.
* Windows path: `C:\Windows\System32\zs-origin.json`.
* **WOW64 caveat (ARM64 Windows).** The app reads the **real** System32 (it's a 64-bit/ARM64 process). A **32-bit** shell (e.g. x86 PowerShell over OpenSSH) writing to `C:\Windows\System32` is silently redirected to `SysWOW64` — and a read-back in the same 32-bit shell also hits SysWOW64, so it *looks* placed but the app never sees it. Write via `C:\Windows\Sysnative\zs-origin.json` (or a native-arch shell) and verify from an ARM64/x64 process.

## JIT provisioning (core-service)

* Gated by the tenant's `StandardConfig.autoCreateUsers` (`core_master.tenant_settings.standard.auto_create_users`). Off → `ensure-federated-identity` returns FORBIDDEN.
* On first login the endpoint creates the identity and writes `identity_id` back to Keycloak; the client refreshes its token to pick up the claim. When the identity already exists the endpoint is a **fast no-op** — it must not re-touch Keycloak.
* AD user needs: `sAMAccountName` (username), `mail` (email, e.g. `user@realm`), **`givenName` + `sn`** (first/last — required), `userPrincipalName`.

## Troubleshooting — symptom → cause → fix

| Symptom                                      | Cause                                                      | Fix                                                                           |
| -------------------------------------------- | ---------------------------------------------------------- | ----------------------------------------------------------------------------- |
| Browser shows **basic-auth popup**           | Host not in the browser's SPNEGO allowlist                 | Set Chrome/Edge `AuthServerAllowlist`; restart browser                        |
| Browser shows **Keycloak form** (not silent) | SPNEGO reached Keycloak but GSS failed                     | Check keytab: RC4 (→ set AES) or SPN/host mismatch with `apiKeycloakUrl`      |
| Keycloak log: *RC4 with HMAC not supported*  | Service ticket is RC4; JDK rejects it                      | `msDS-SupportedEncryptionTypes=24`, re-export keytab, `klist purge` on client |
| Prompt even with policy set                  | Interactive session is a **local** user (no TGT)           | Sign in as a **domain** user; verify `klist`                                  |
| App **hangs after login**                    | `ensure-federated-identity` erroring/slow                  | Check core-service log (see below); usually one of the next three rows        |
| *First name and last name cannot be empty*   | Missing first-name mapper / no `givenName`                 | Add `givenName→firstName` mapper; set `givenName`+`sn` in AD                  |
| *Federated storage is not writable*          | editMode = `READ_ONLY`                                     | Set editMode = **UNSYNCED**, re-sync                                          |
| *User exists with same email* (409)          | KC user lookup by username, but federated username ≠ email | Fixed in core-service (`searchByEmail`); rebuild required                     |
| `zs-origin.json` "not found" by app          | Written to SysWOW64 via a 32-bit shell                     | Write to `C:\Windows\Sysnative\...`; verify from ARM64 process                |

## Getting core-service logs locally

core-service defaults to stdout-only JSON. For local debugging, enable the file appender with `-Dcore.logToFile=true` (path via `-Dcore.logFile=…`). `./dev.sh api` sets this automatically and writes `tmp/logs/core-service-app.log`; for an IDE run, add the flag to the run configuration's VM options.


# Cloud

Complete guide for cloud infrastructure setup and management.

Complete guide for cloud infrastructure setup and management.

*Content coming soon...*


---

[Next Page](/llms-full.txt/1)